

LBFH
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
educationexploitationhash-analysis+9
725 years ago
naimkowshik/lbfhAbout All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
 alkimcoskun/yordam-kutuphane-otomasyonunda-coklu-html-enjeksiyonu
CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…
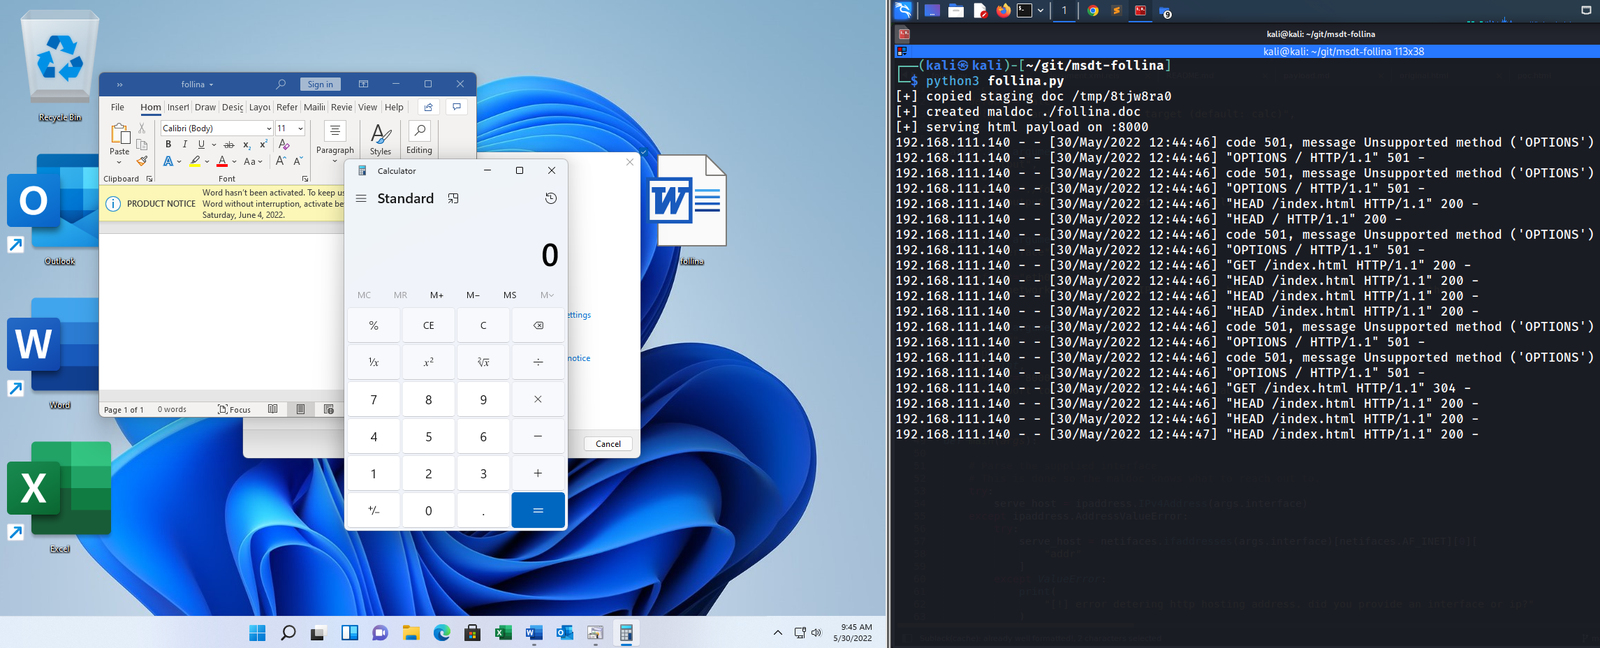 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 ajansha/cve-2025-55903
Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 prodigiousmind/cve-2023-41425
WonderCMS Authenticated RCE - CVE-2023-41425
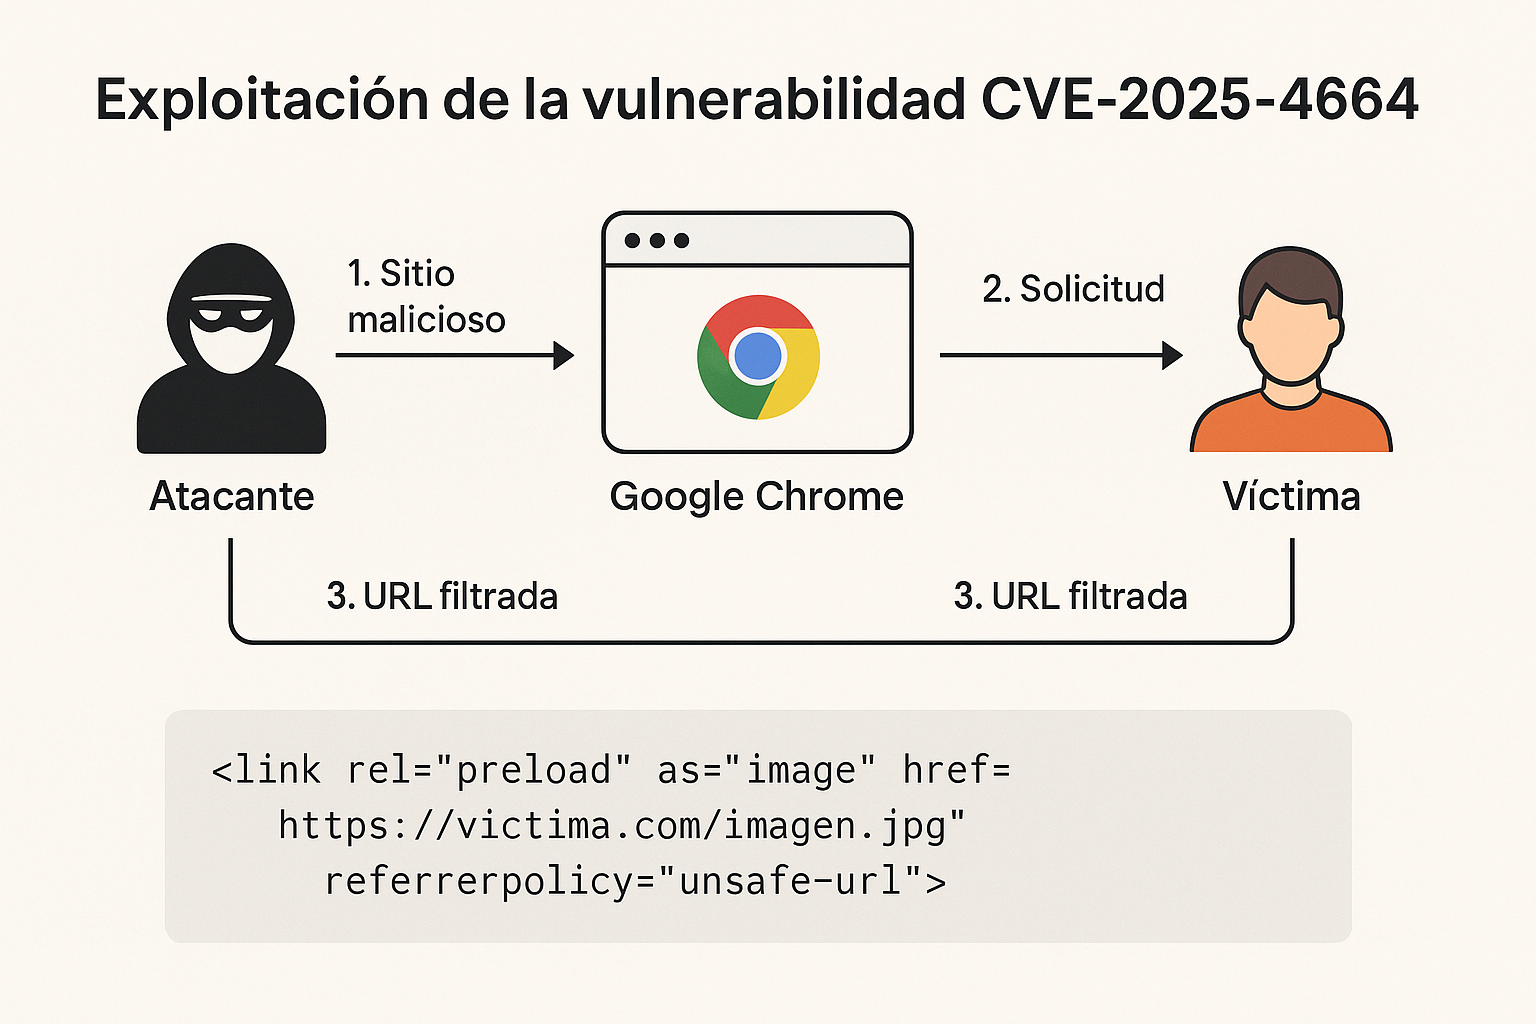 speinador/cve-2025-4664
Educational demo of CVE-2025-4664, a Chrome Loader vulnerability enabling cross-origin data leakage via referrer-policy manipulation. Includes a…
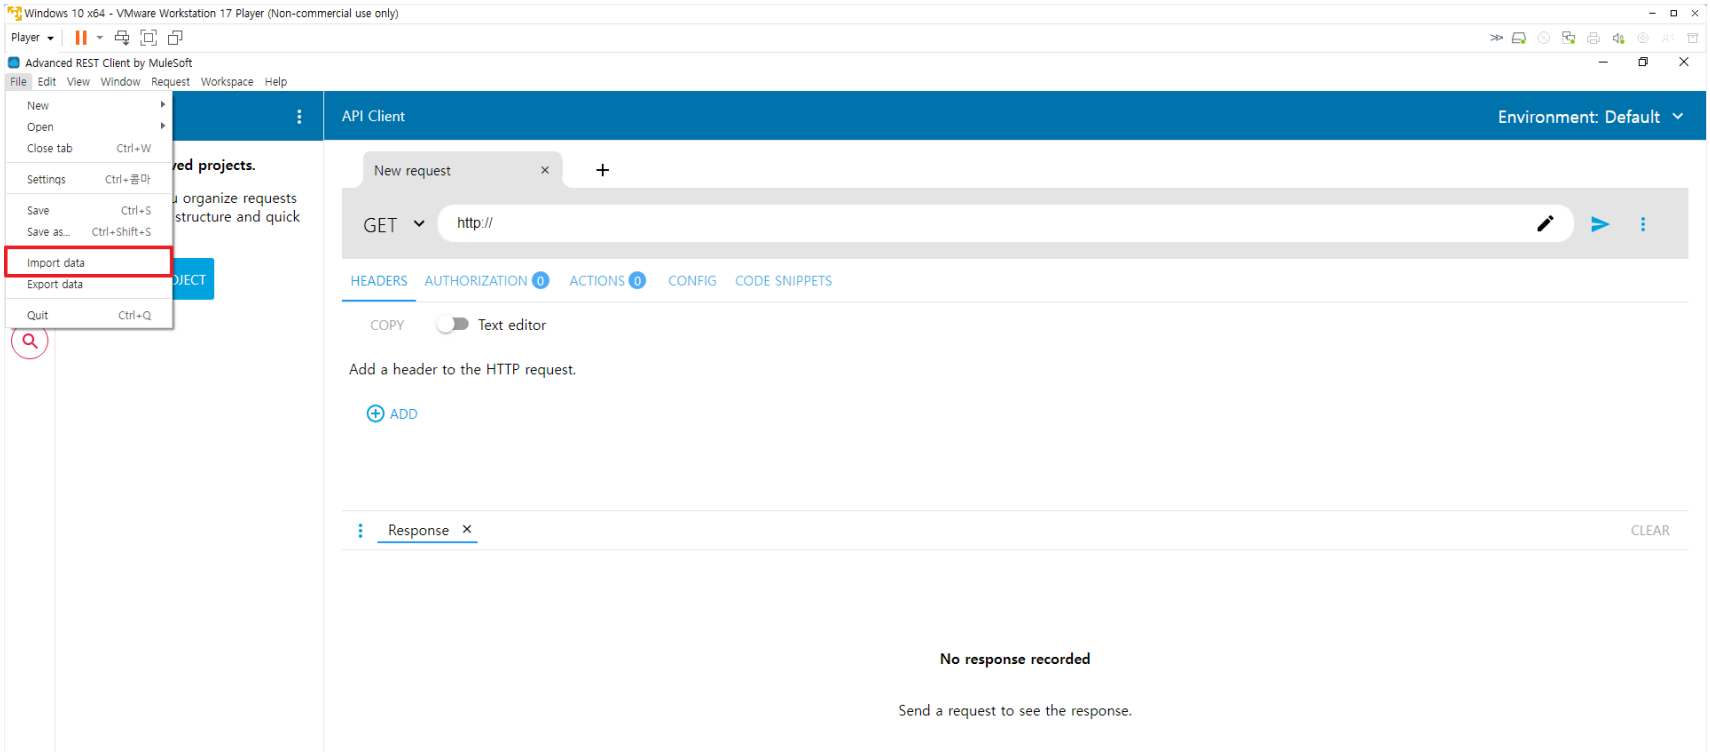 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
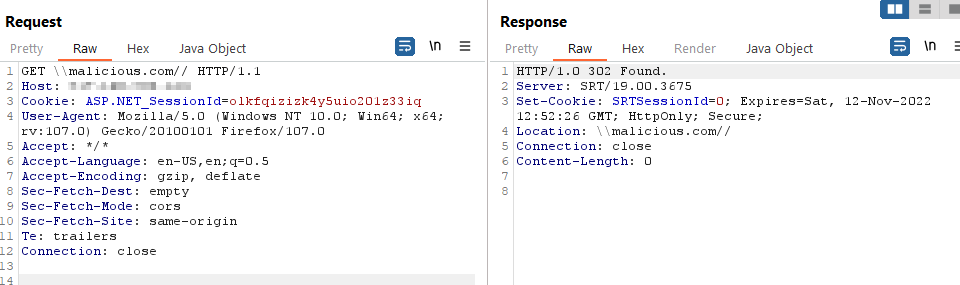 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…