
CVE-2025-40778
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
dns-analysiseducationexploitation+3
6
nehkark/cve-2025-40778Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…

 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 mrbrutti/cartero
Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…
 george0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-
Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
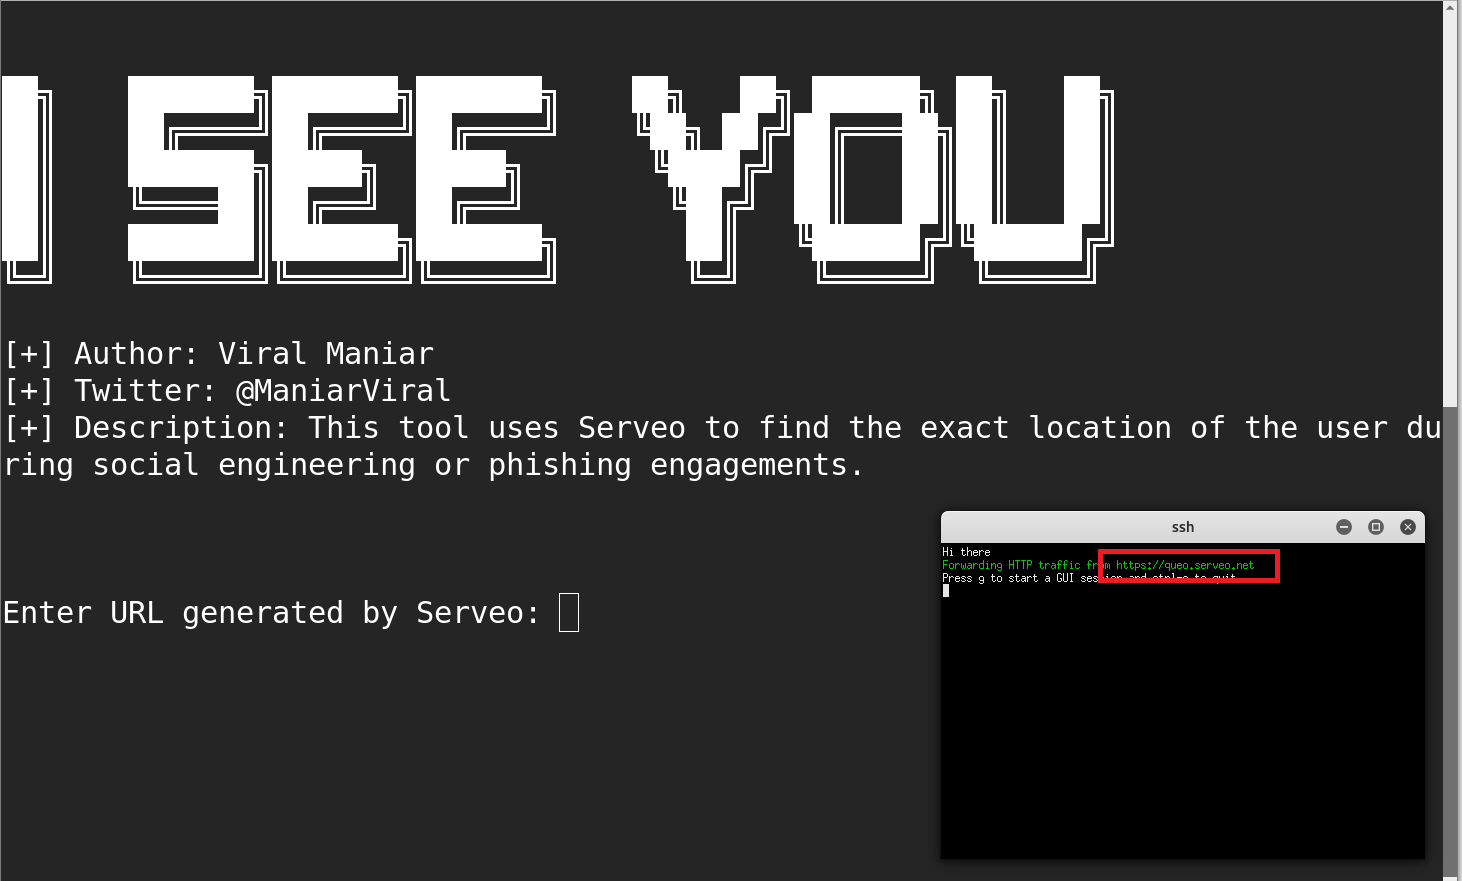 viralmaniar/i-see-you
ISeeYou is a Bash and Javascript tool to find the exact location of the users during social engineering or phishing engagements. Using exact location…
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
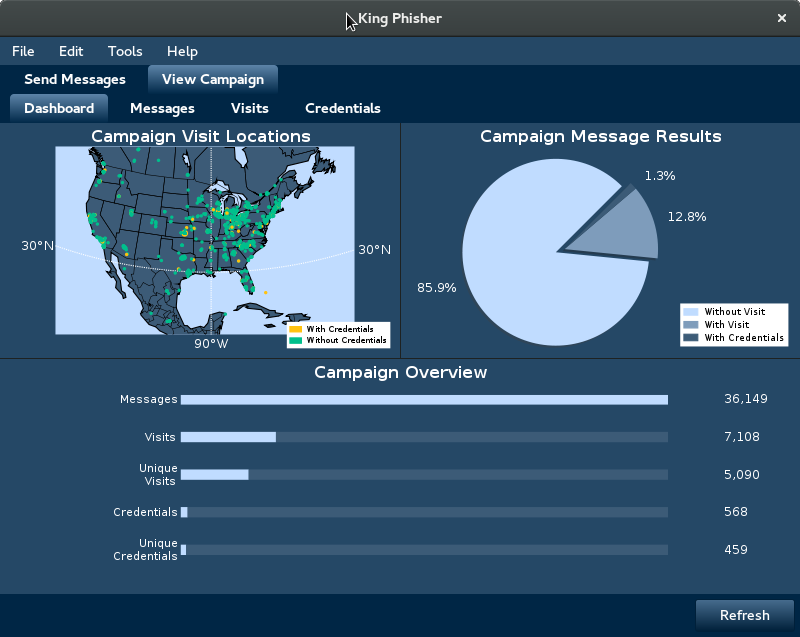 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
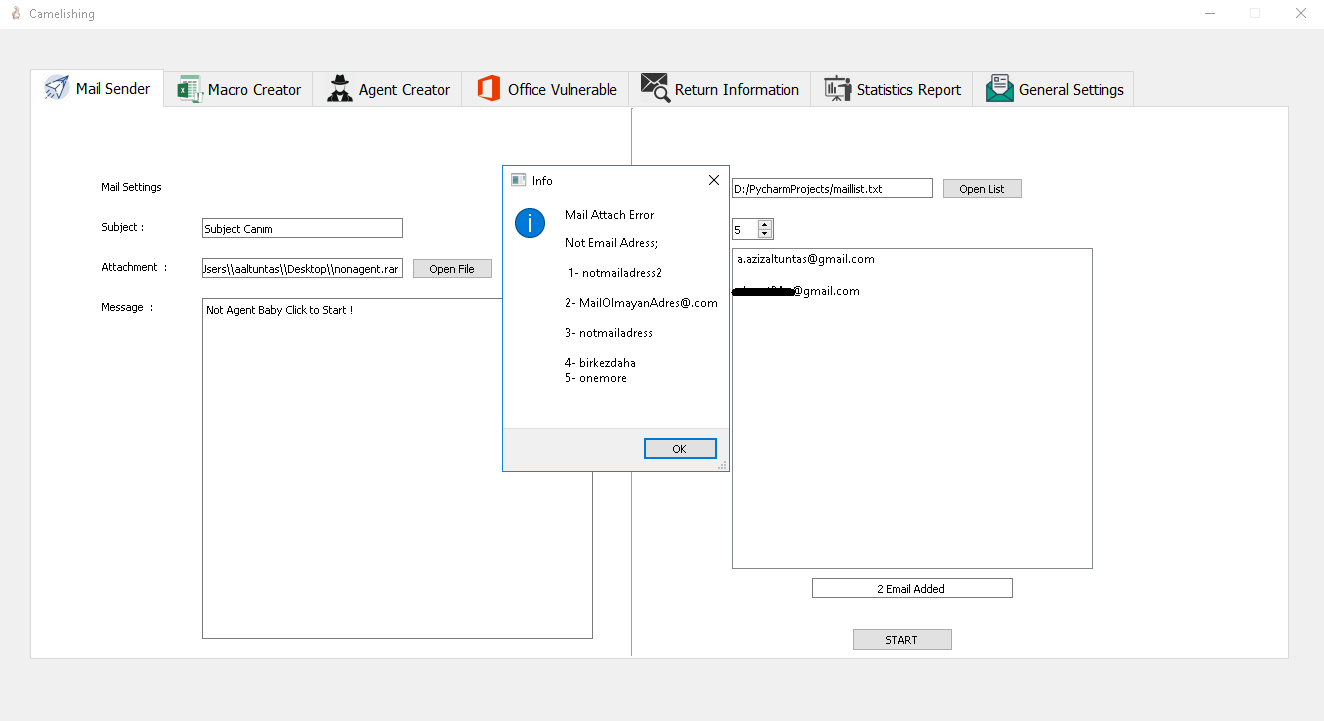 azizaltuntas/camelishing
Social Engineering Tool
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…