Yordam-Kutuphane-Otomasyonunda-Coklu-HTML-Enjeksiyonu

CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…

CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…

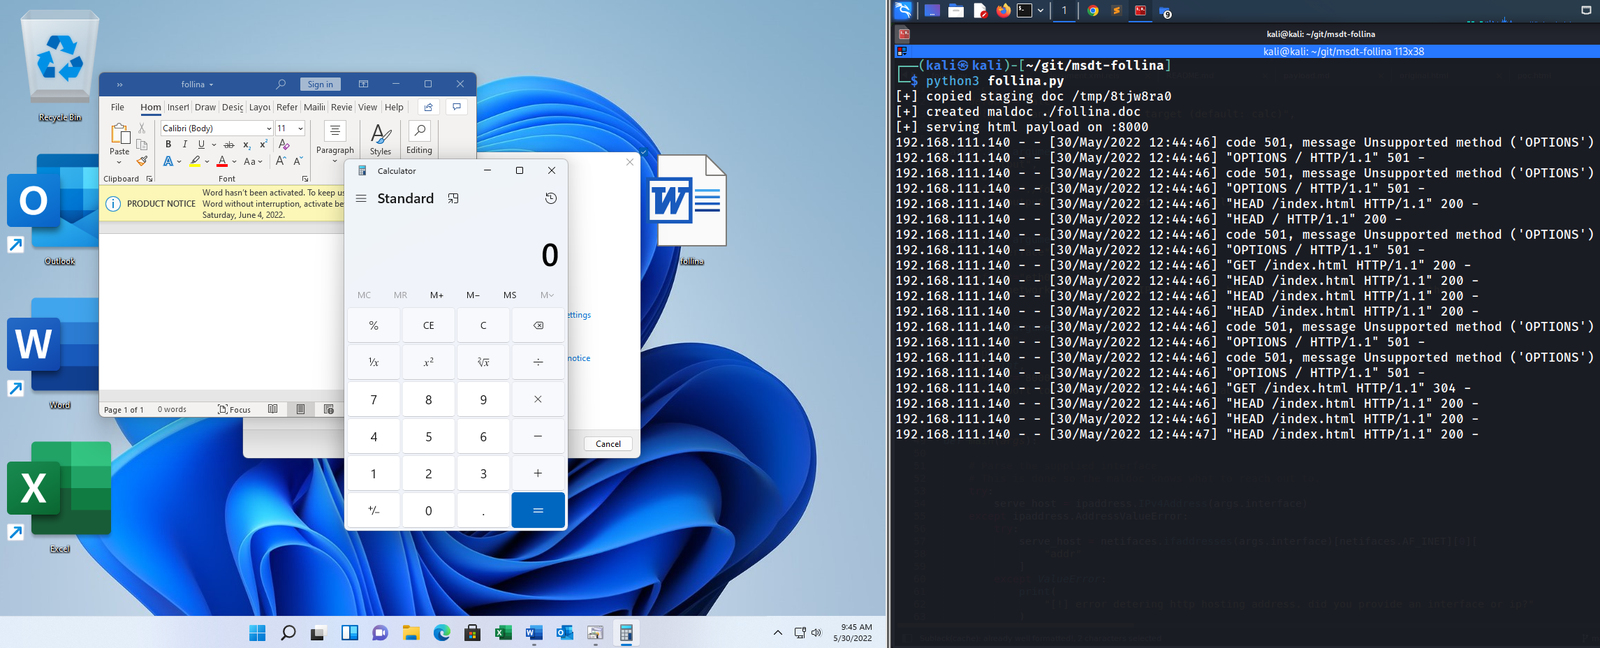
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…

Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…

Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…

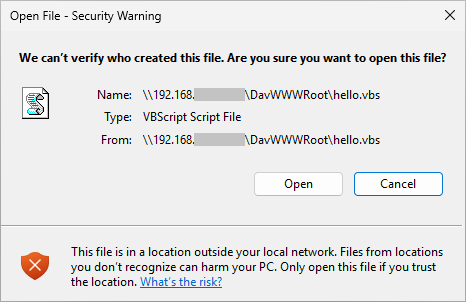
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…

Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.

Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…

PoC for the "Windows Notepad RCE"

WonderCMS Authenticated RCE - CVE-2023-41425

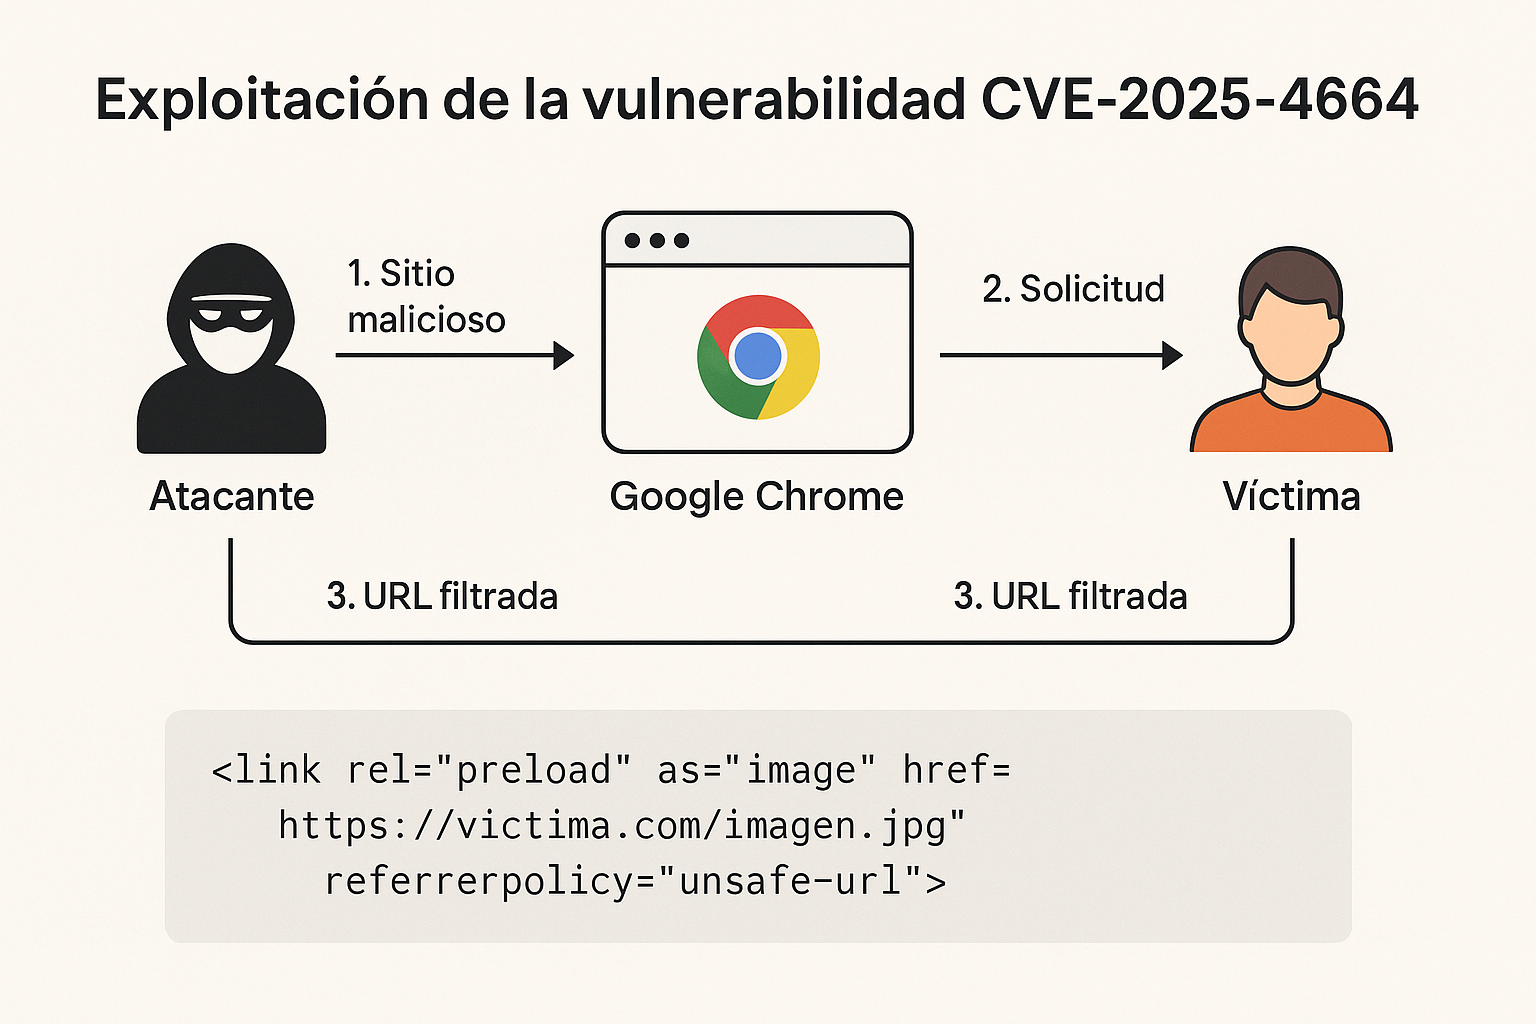
Educational demo of CVE-2025-4664, a Chrome Loader vulnerability enabling cross-origin data leakage via referrer-policy manipulation. Includes a…

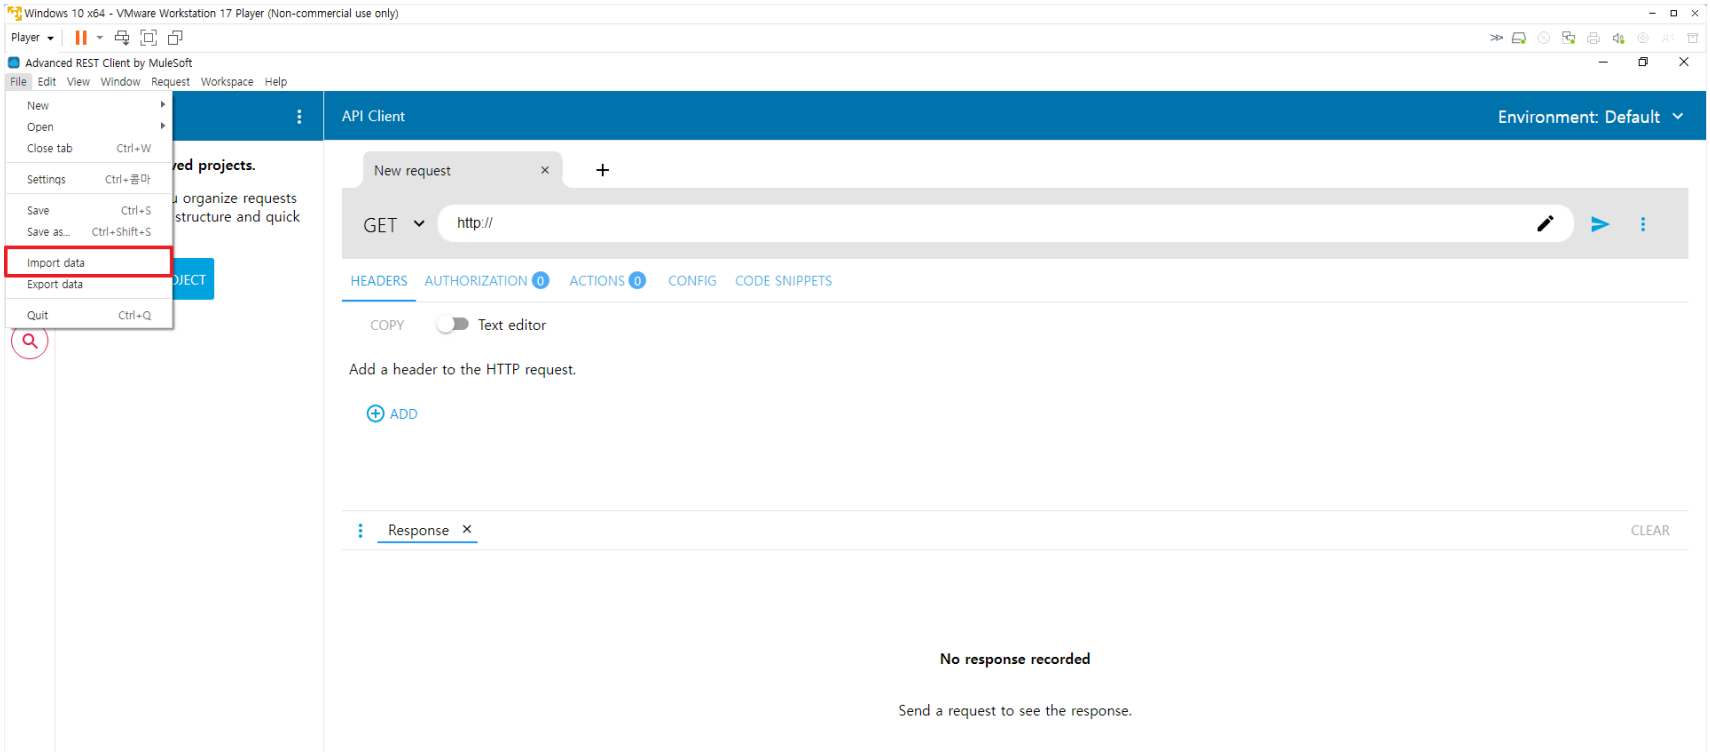
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit

Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…

Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…

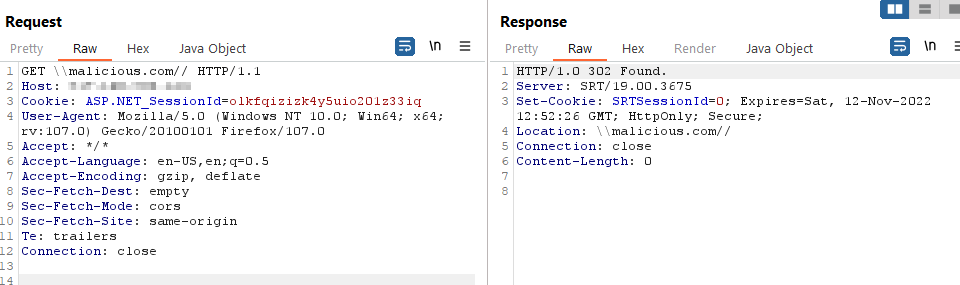
Public disclosure of TitanFTP 19.X Open Redirection vulnerability