
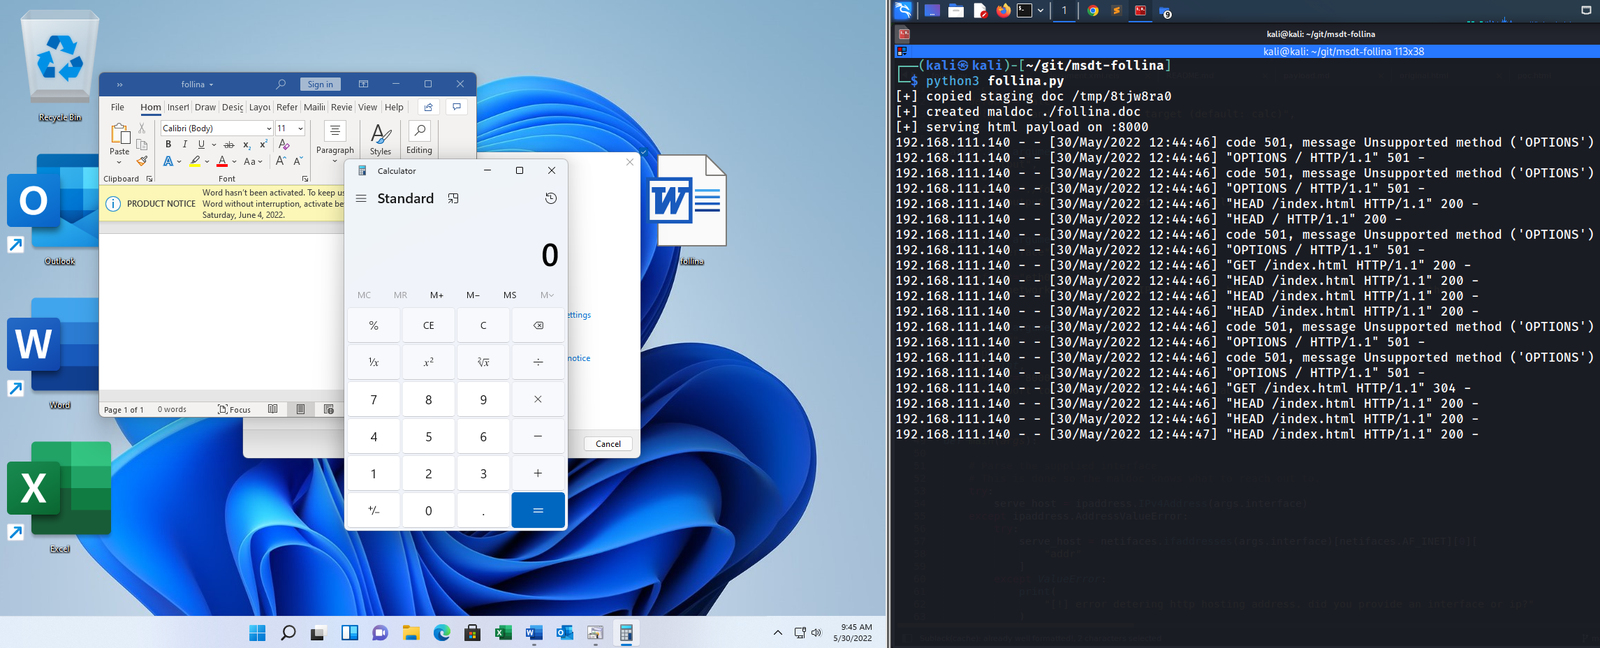
msdt-follina
 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
command-and-controlexploitationpayload-development+2
1.6k
johnhammond/msdt-follinaGenerates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 tangent65536/cve-2026-20841
PoC for the "Windows Notepad RCE"
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 prodigiousmind/cve-2023-41425
WonderCMS Authenticated RCE - CVE-2023-41425
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 tarantula-team/cve-2019-12949
CVE-2019-12949
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
 kaleth4/cve-2022-30190
Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
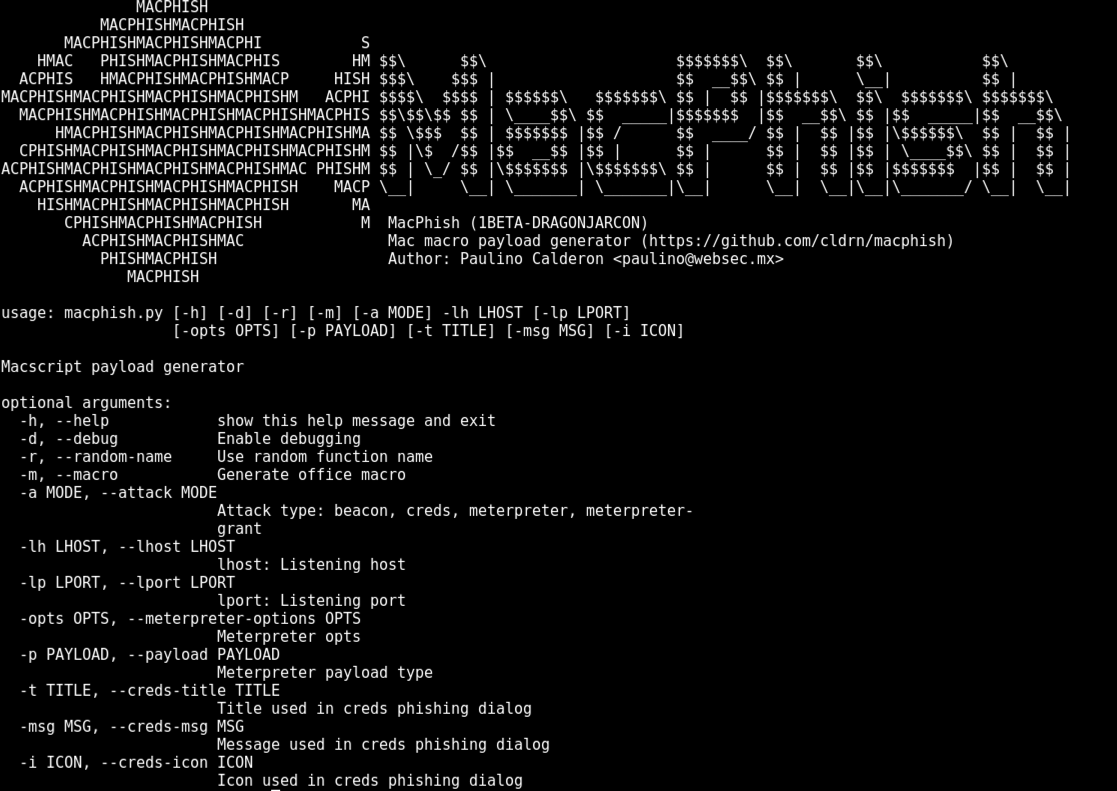 cldrn/macphish
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.
 azizaltuntas/camelishing
Social Engineering Tool

 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…