

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
10 results
bettercap preview

bettercap

GitHubbettercap/bettercap

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.2k
6 days ago
CVE-2019-13496 preview

CVE-2019-13496

GitHubfurqankhan1/cve-2019-13496

Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
authenticationids-ips-evasionpenetration-testing+3
26 years ago
HTB-Mailing-A-Complete-Walkthrough preview

HTB-Mailing-A-Complete-Walkthrough

GitHubthemursalin/htb-mailing-a-complete-walkthrough

If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…

ctfeducationexploitation+8
7 months ago
cve-2023-23397-purple-team preview

cve-2023-23397-purple-team

GitHubpraneethnaidu1910-cmd/cve-2023-23397-purple-team

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
educationemail-securityexploitation+3
2 months ago
CVE-2022-25257 preview

CVE-2022-25257

GitHubpolling-repo-continua/cve-2022-25257

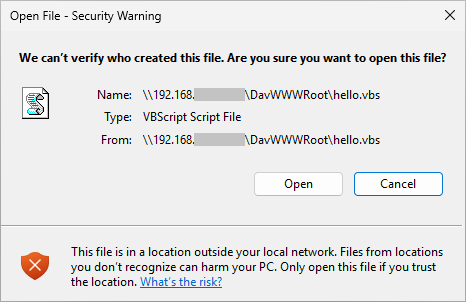
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
exploitationphishingsocial-engineering+2
4 years ago
CVE-2026-20841 preview

CVE-2026-20841

GitHubtangent65536/cve-2026-20841

PoC for the "Windows Notepad RCE"
exploitationpayload-generationphishing
28 months ago
XSScope preview

XSScope

GitHubkleiton0x00/xsscope

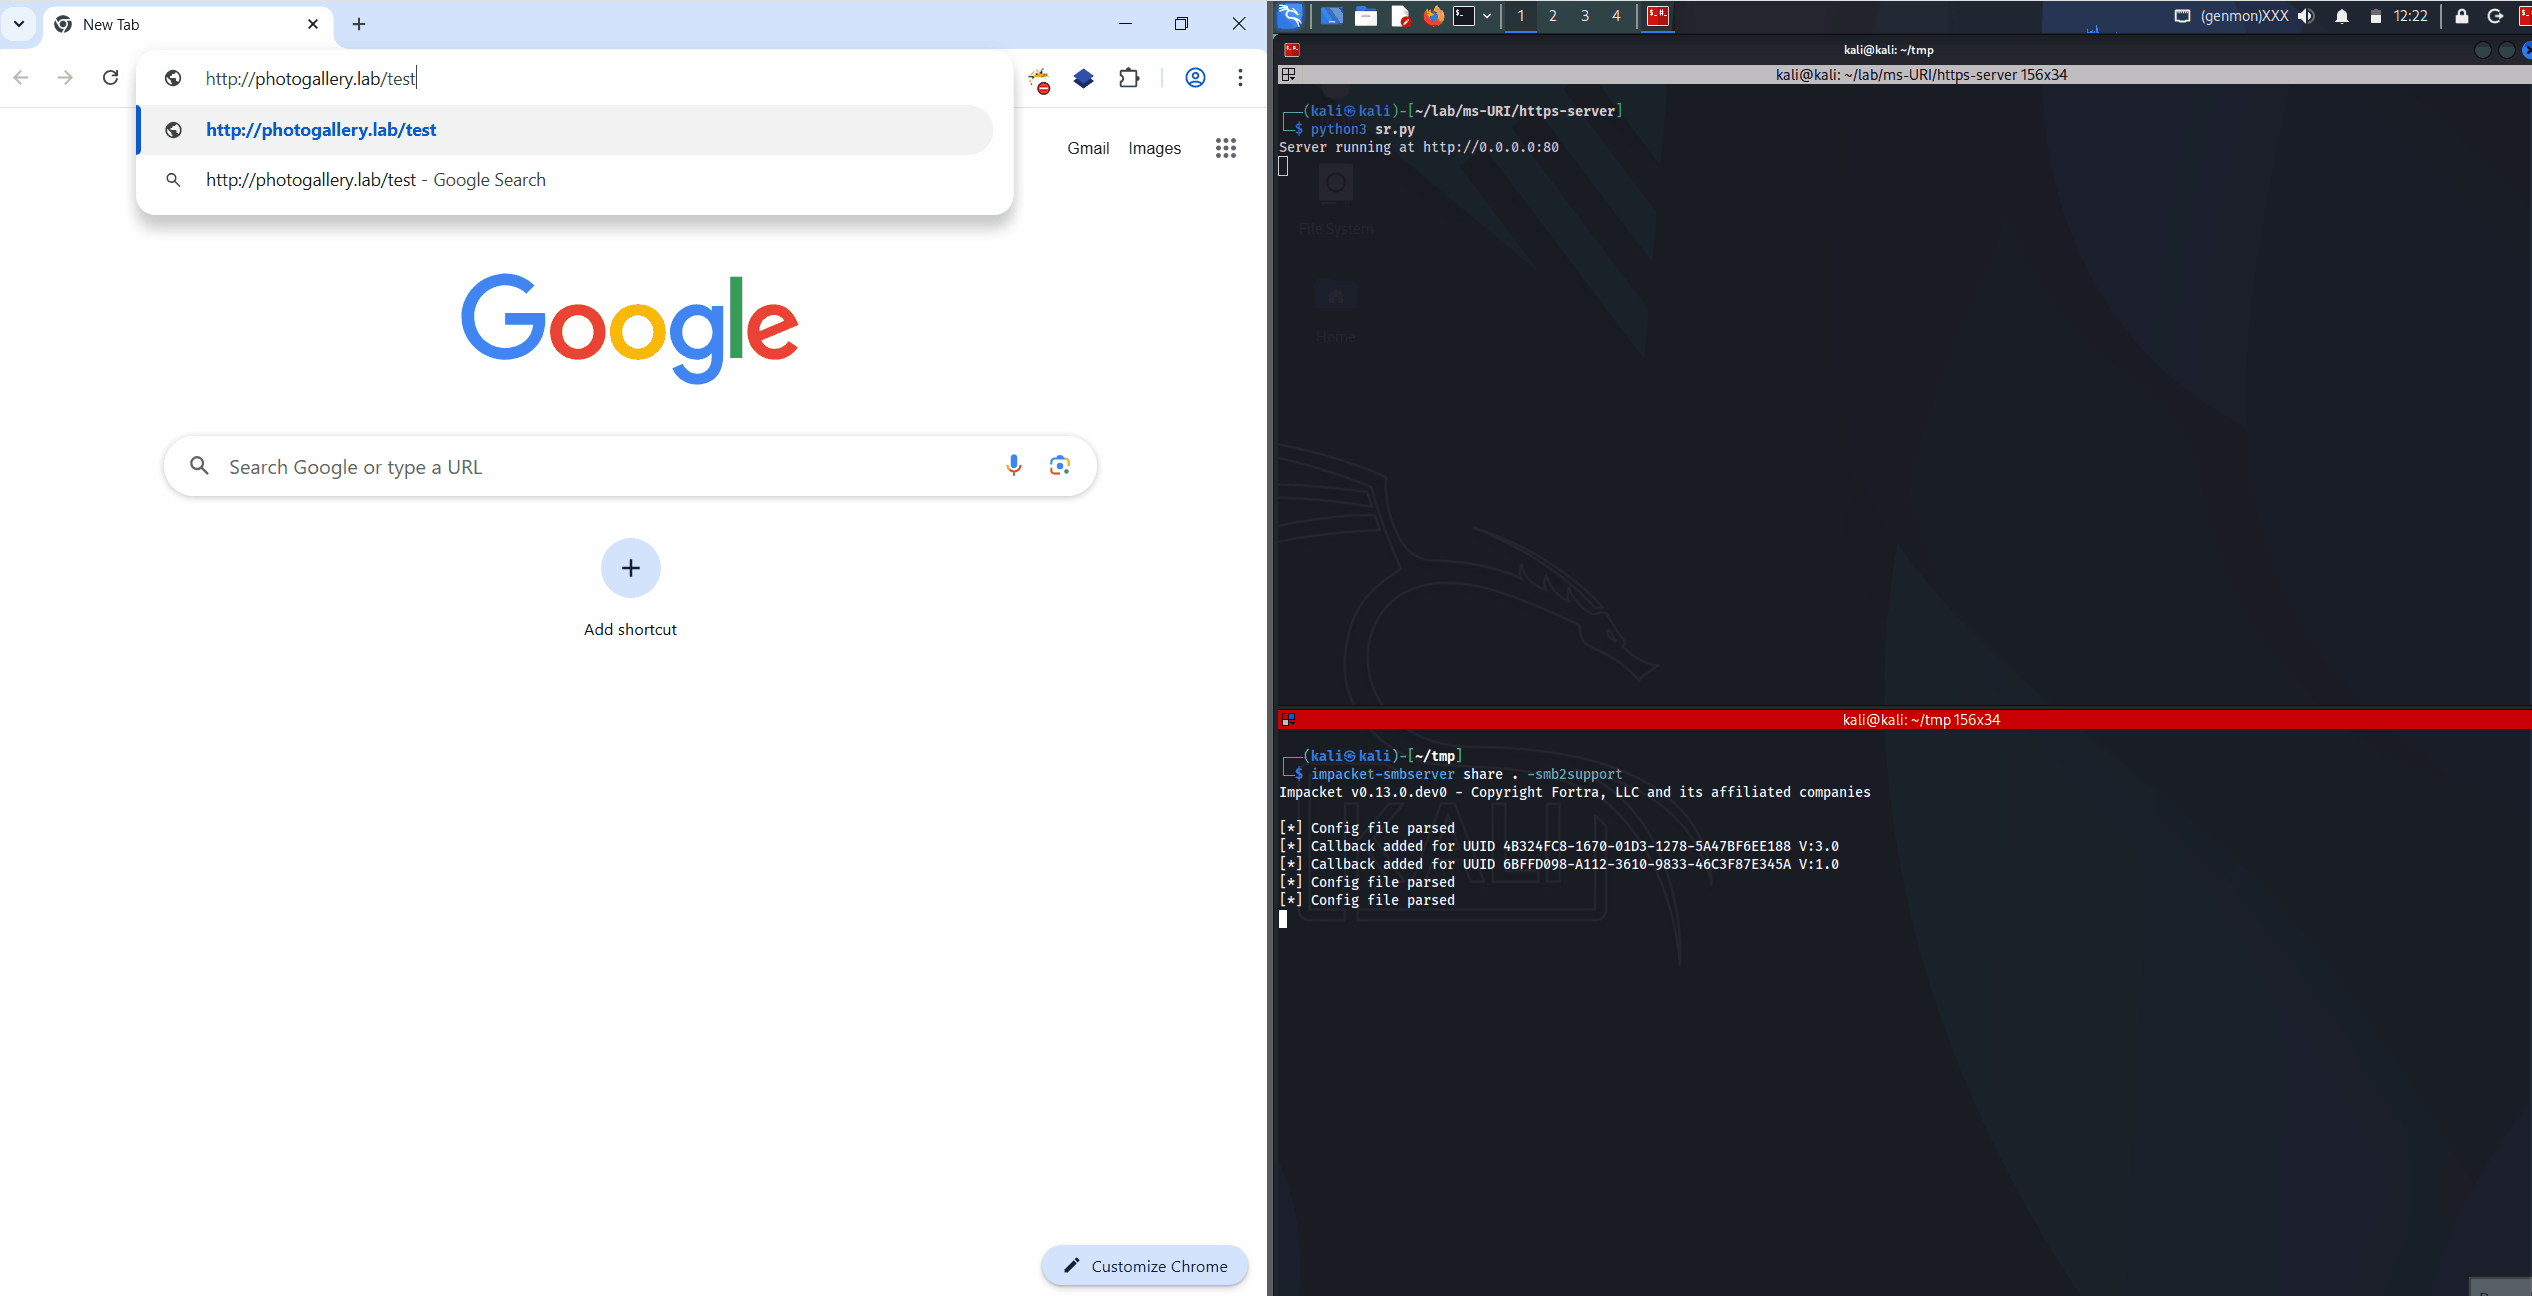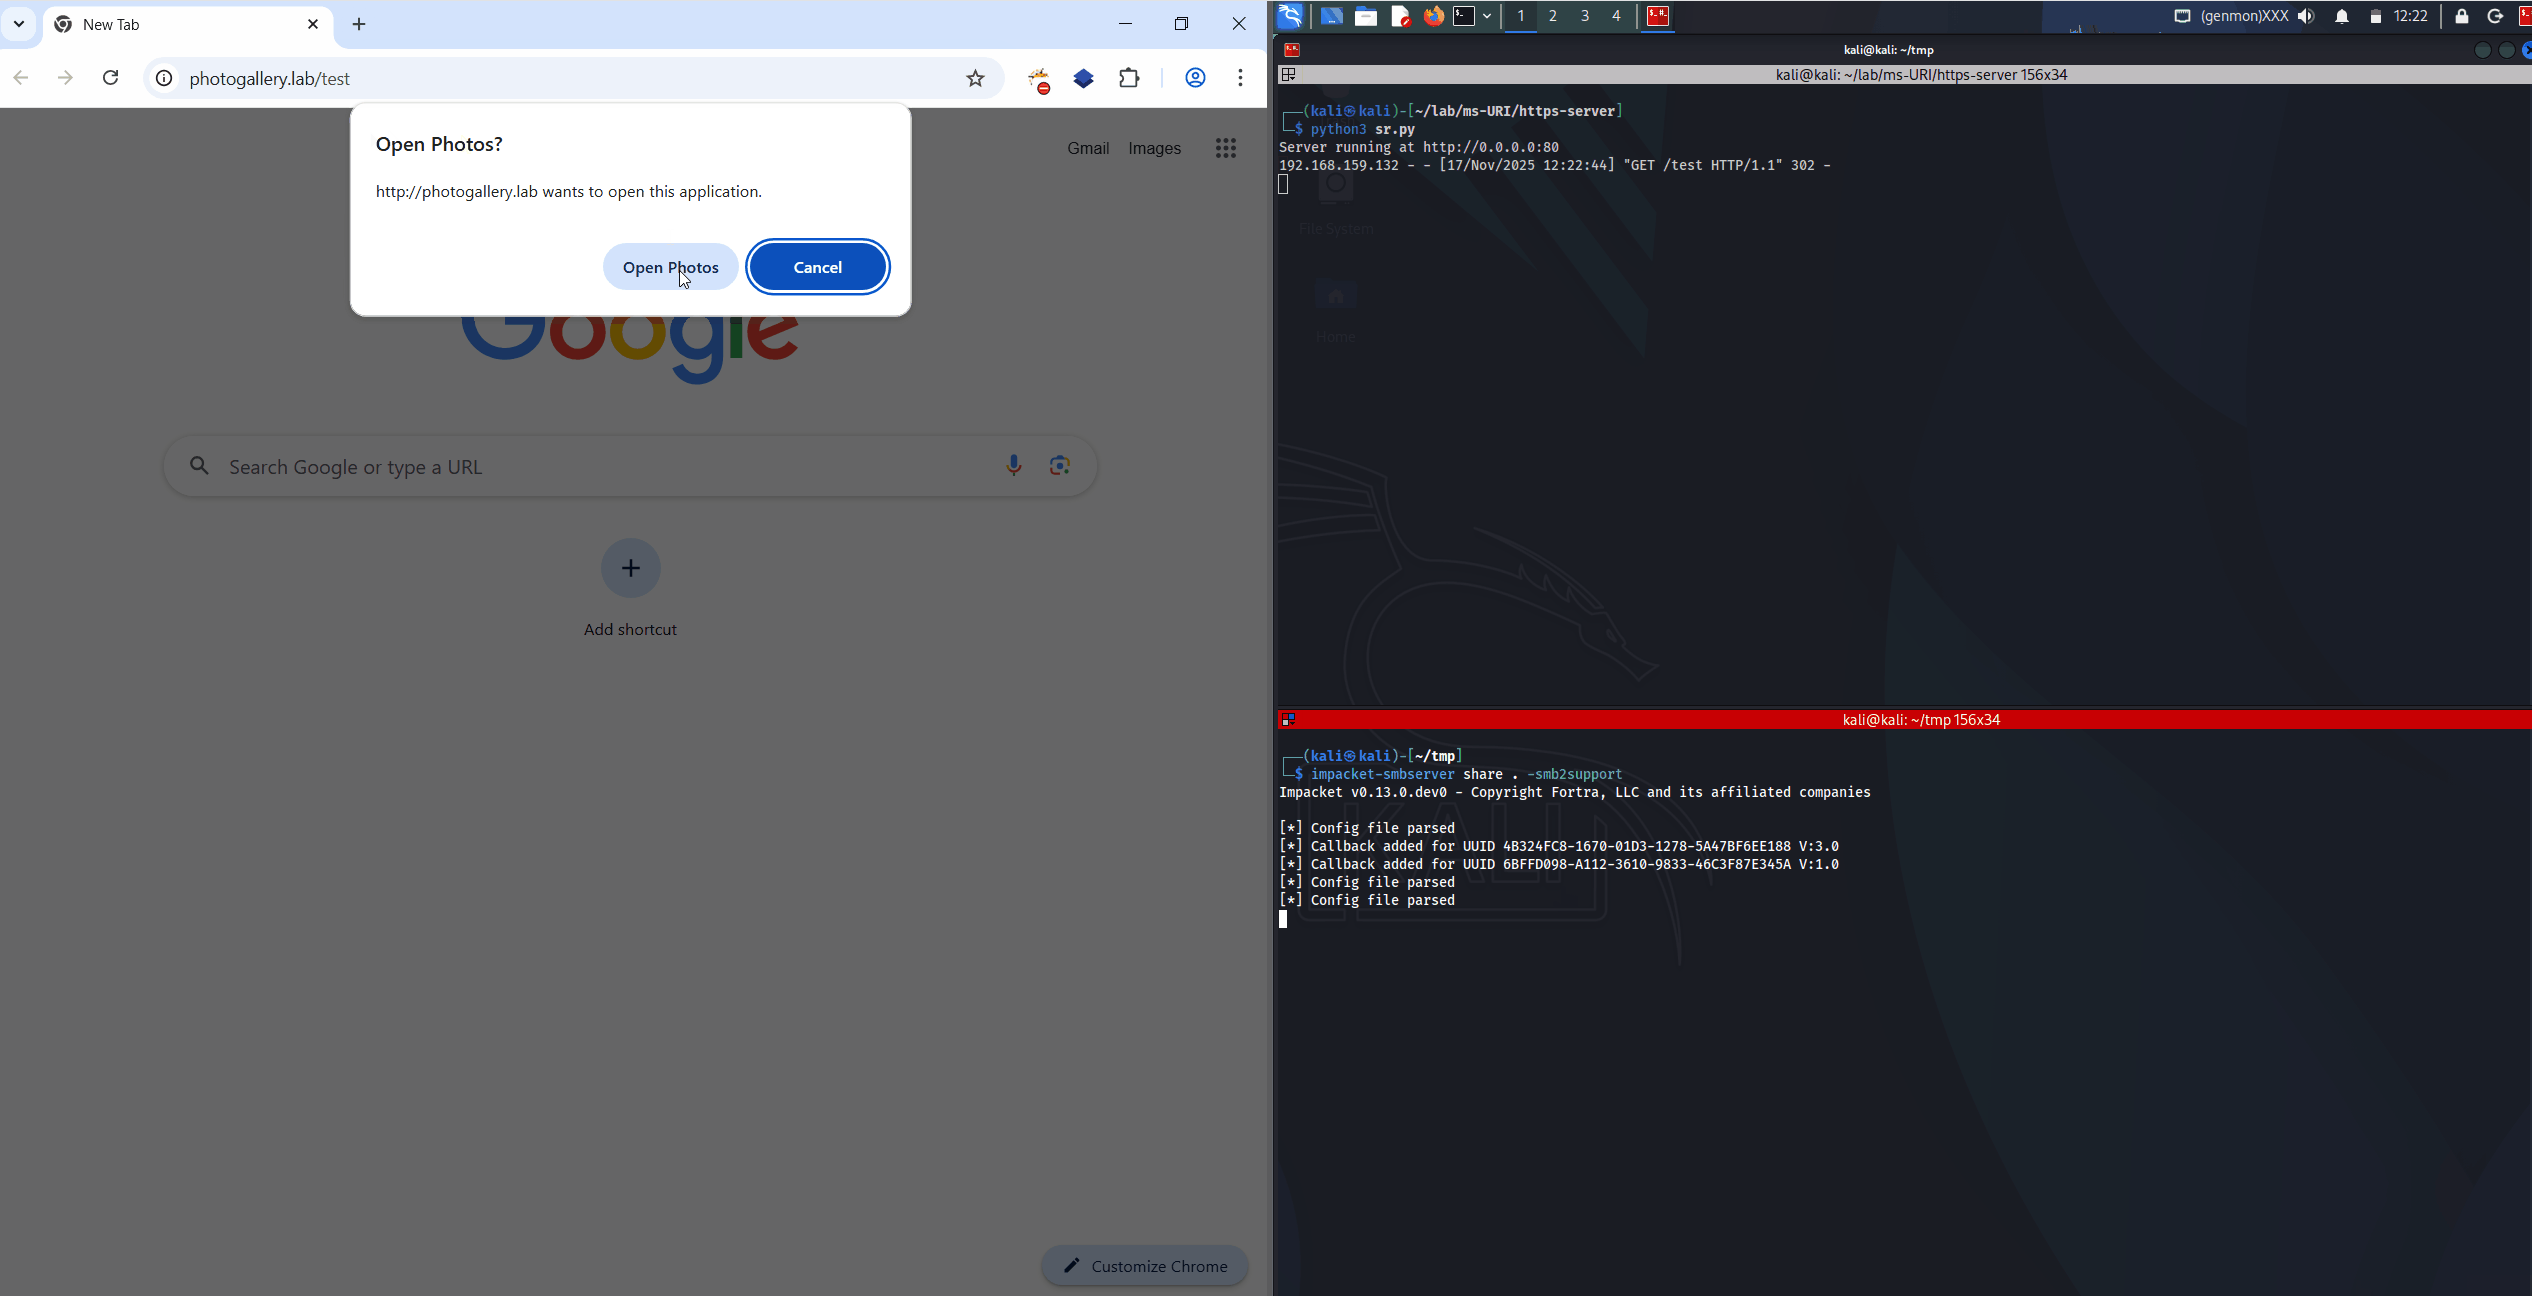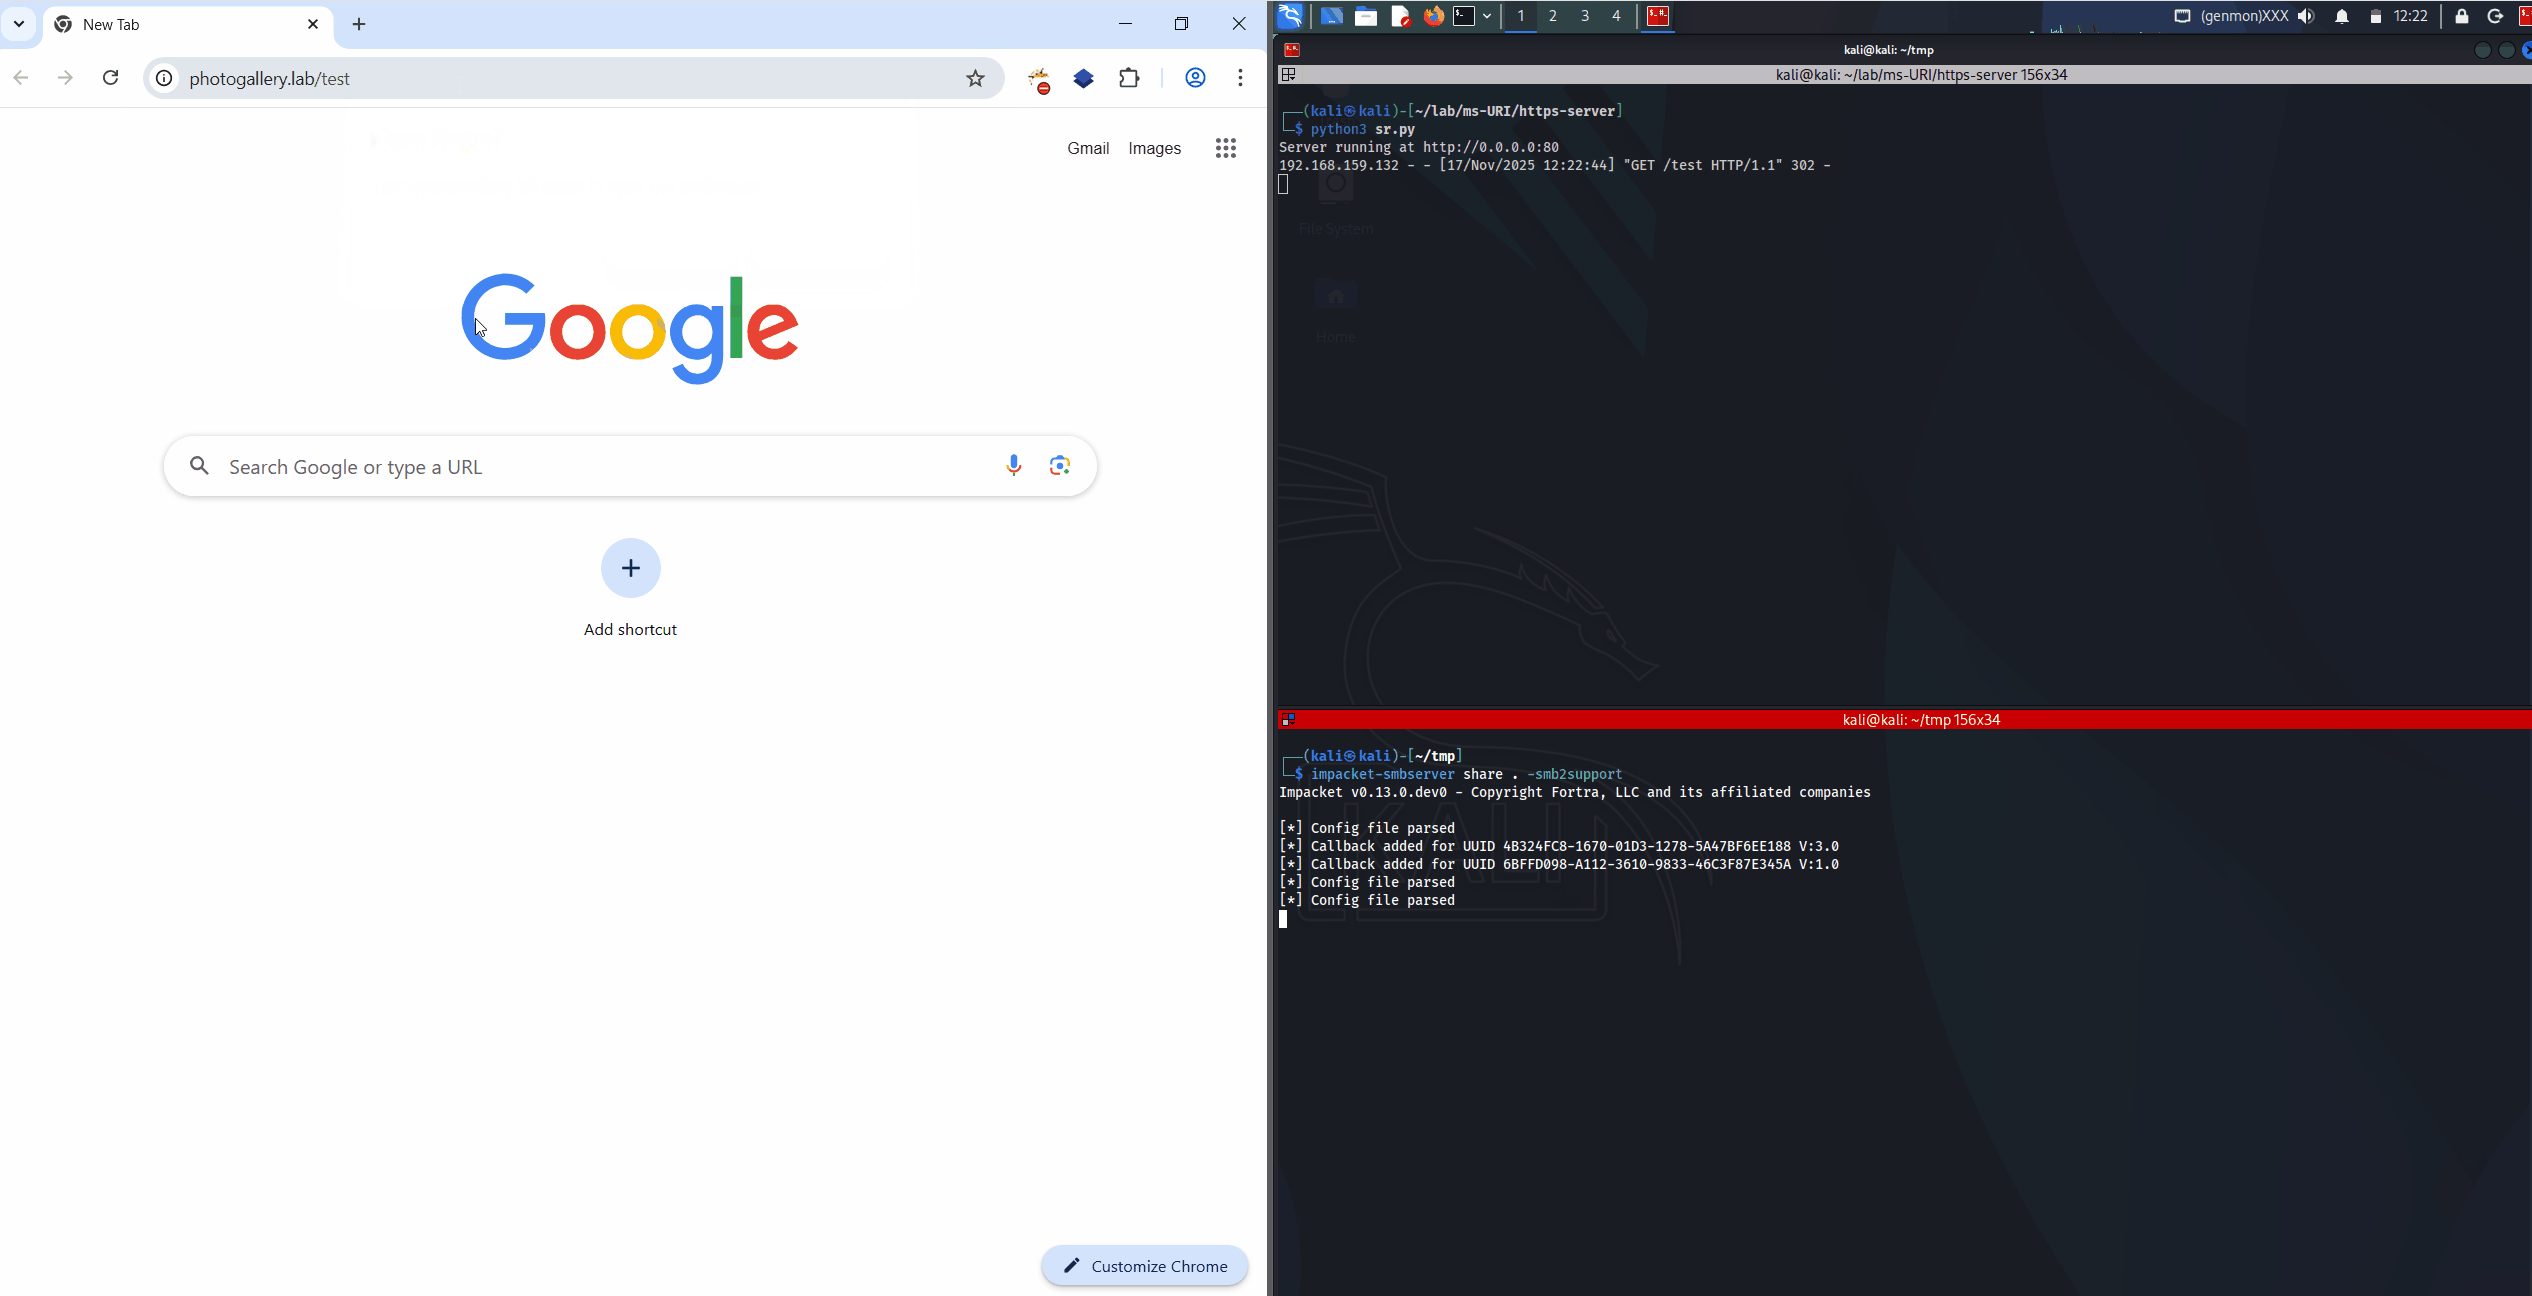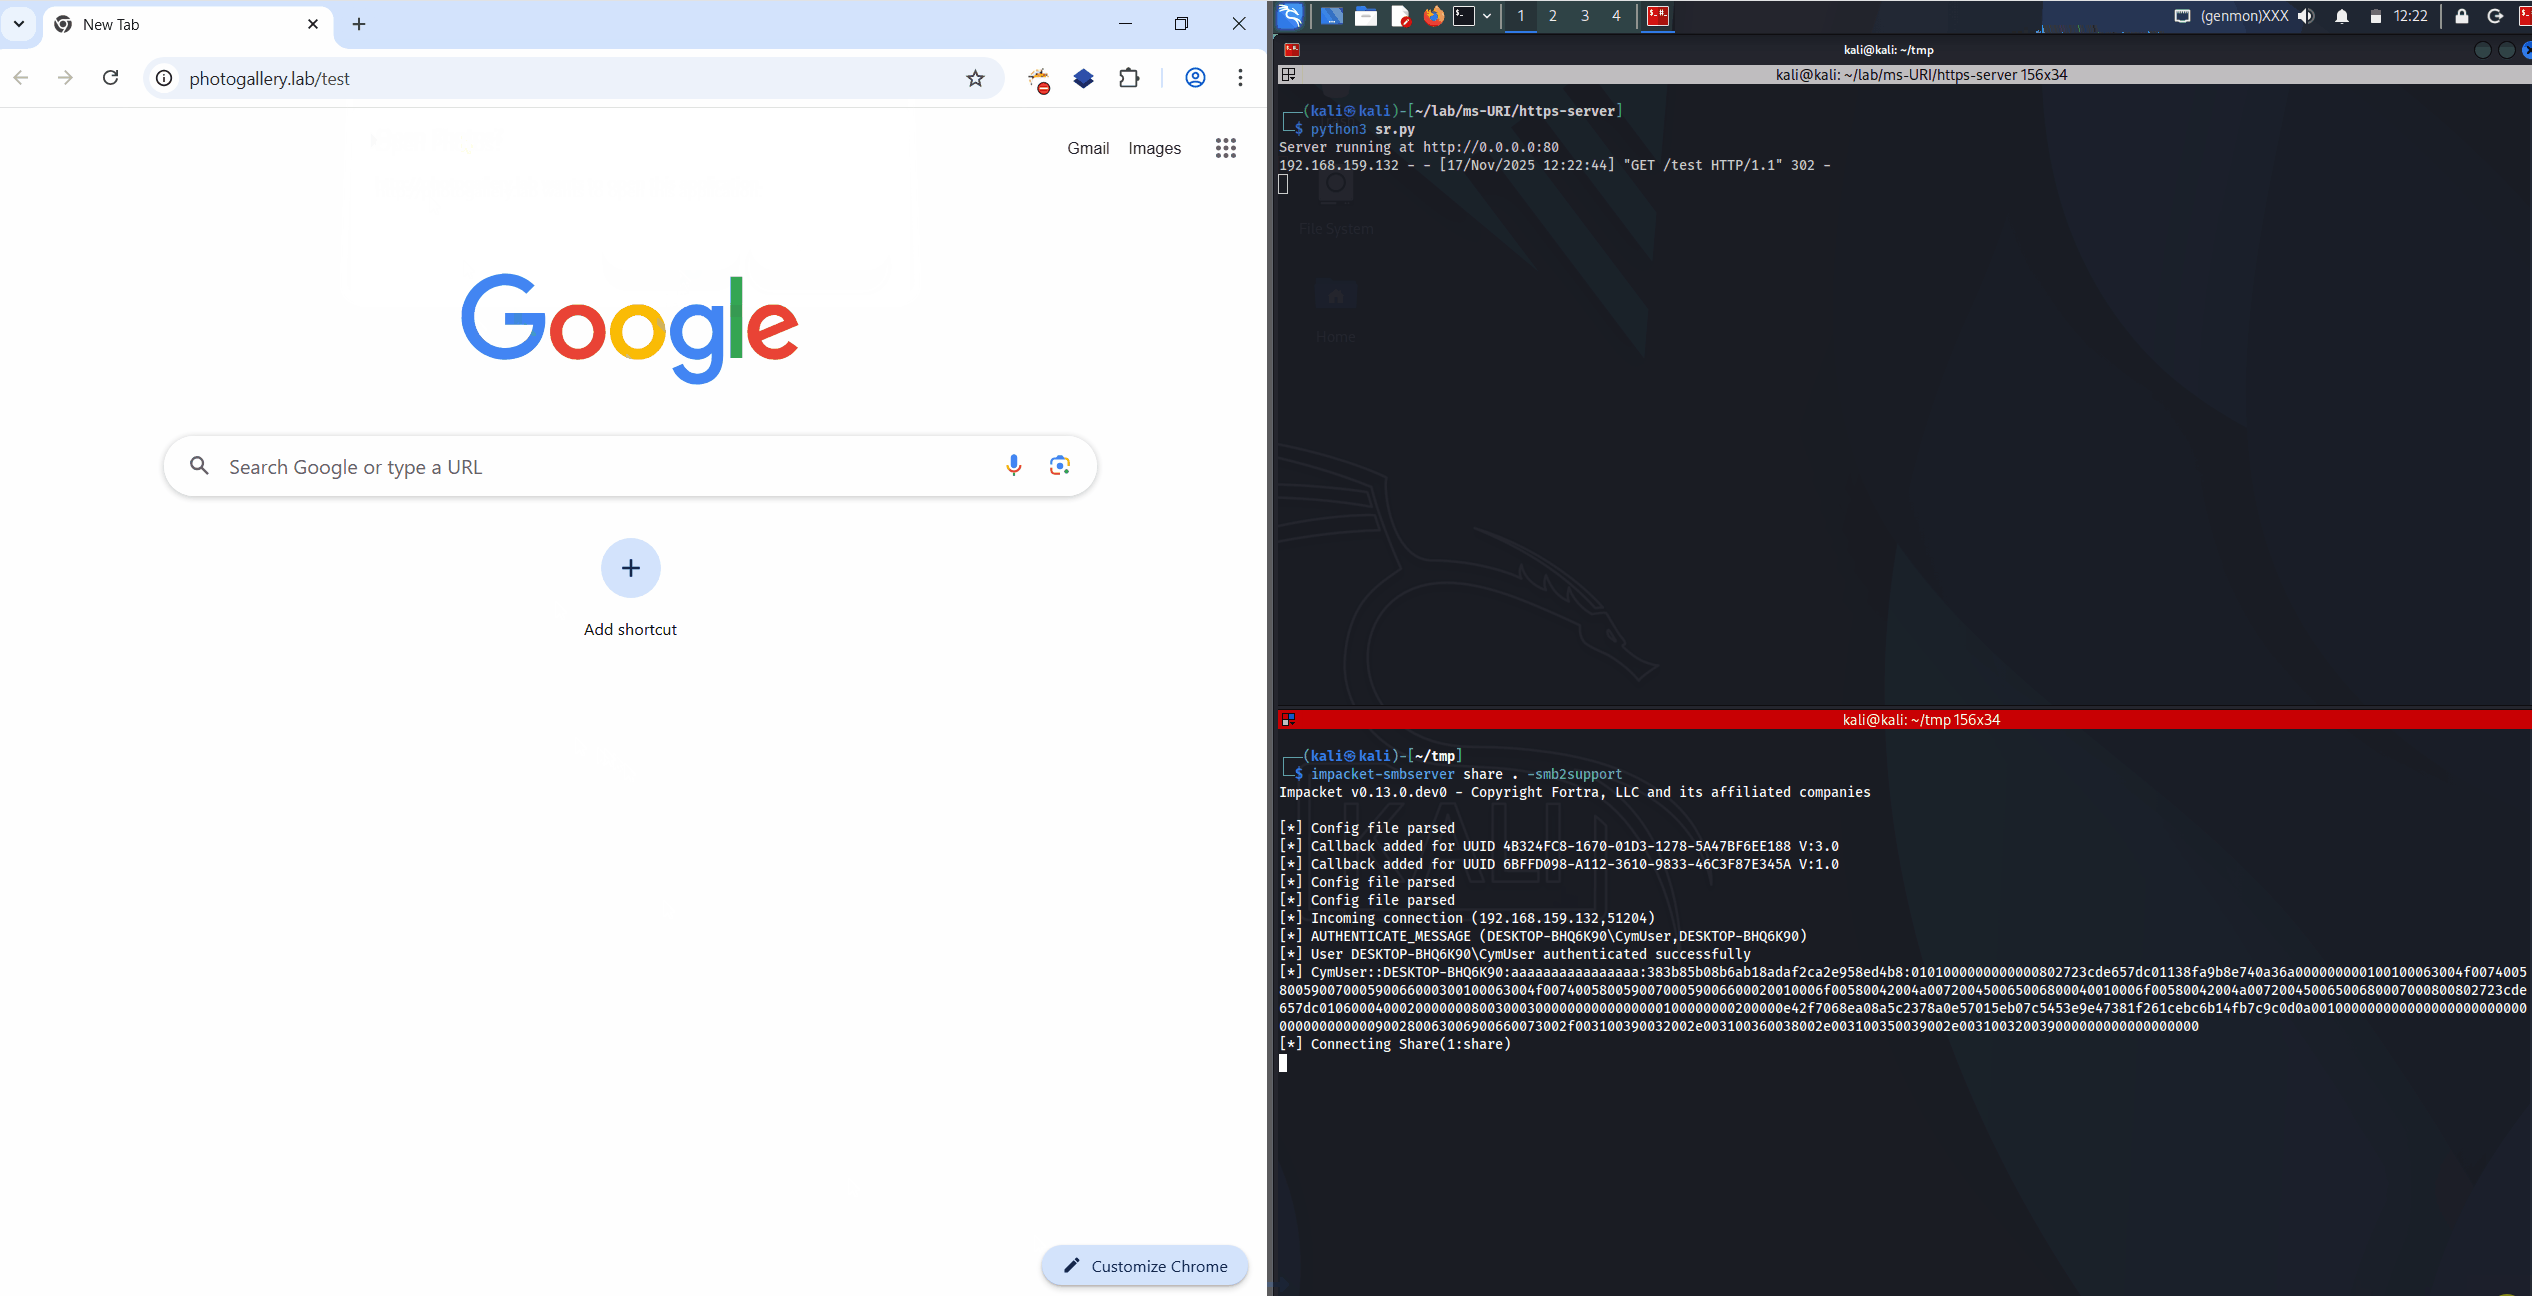
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
command-and-controlexploitationinformation-gathering+5
3134 years ago
ms-photos_NTLM_Leak preview

ms-photos_NTLM_Leak

GitHubrubenformation/ms-photos_ntlm_leak

New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click

educationexploitationlateral-movement+4
20811 months ago
threatripper preview

threatripper

GitLabmevislobo2006/threatripper

Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…

api-securitydefensive-toolseducation+4
128 days ago
LBFH preview

LBFH

GitHubnaimkowshik/lbfh

About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers

educationexploitationhash-analysis+9
725 years ago
