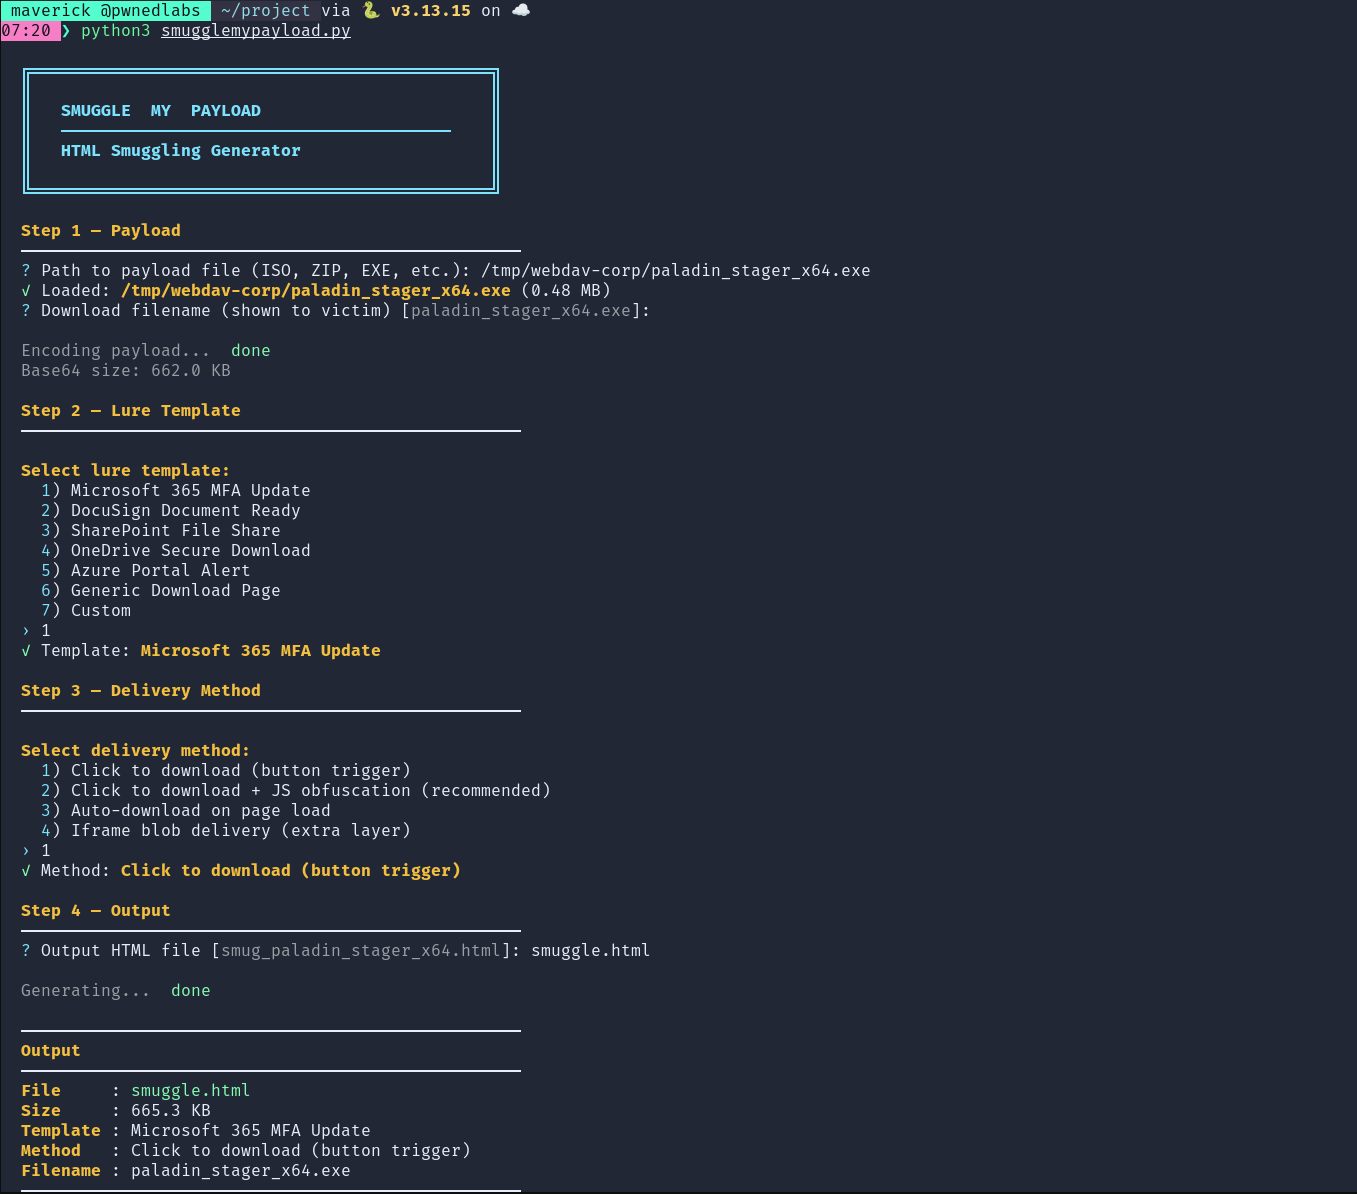

SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…


Information Protection & OSINT resources | 一个关于数字隐私搜集、保护、清理集一体的方案,外加开源信息收集(OSINT)对抗

A Phishing Dropper designed to Pentest.

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…

Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.

Automated man-in-the-middle attack tool.

Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…

Find phishing kits which use your brand/organization's files and image.

This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…

POC Files for CVE-2019-17497


CVE-2025-33053 Proof Of Concept (PoC)

Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…

The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…