SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…

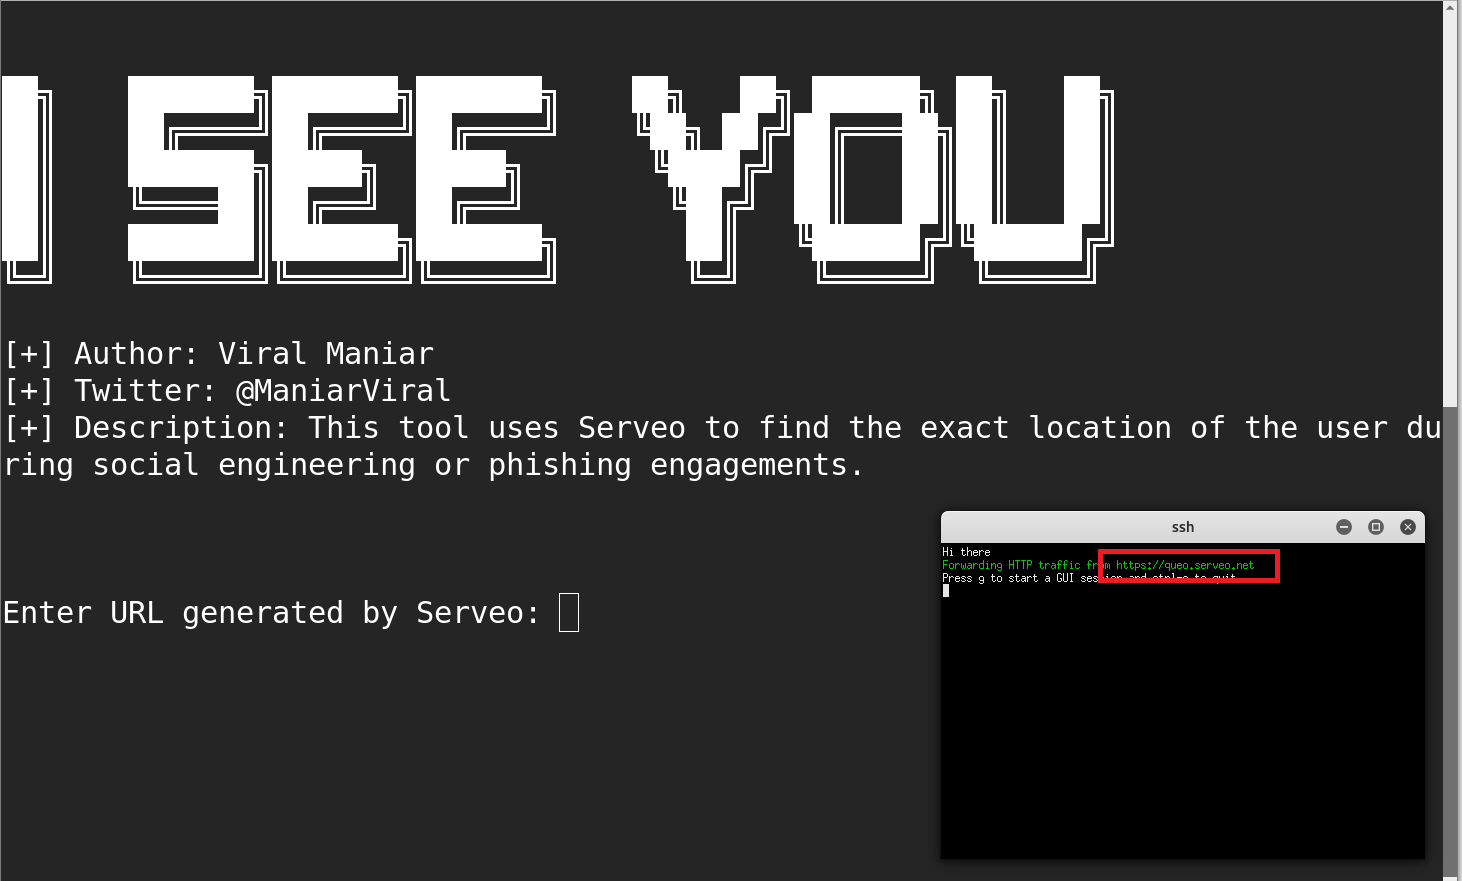
ISeeYou is a Bash and Javascript tool to find the exact location of the users during social engineering or phishing engagements. Using exact location…

Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…

CVE-2024-57428: PHPJabbers Cinema Booking System v2.0 suffers from stored XSS, enabling persistent JavaScript injection for phishing and malware…

SVG Analysis and generation tools for commonly seen SVG attachment phishing

Spam Scanner is a Node.js anti-spam, email filtering, and phishing prevention tool and service. Built for @ladjs, @forwardemail, @cabinjs, @breejs,…

Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…

Serverless AITM Simulation Framework for Entra ID and M365

Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…

In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…

Proof-of-concept for CVE-2020-16270, an XSS vulnerability in OLIMPOKS under 3.3.39, demonstrating remote injection of malicious JavaScript to steal…

The plugin does not sanitise the HTML allowed in the Bio of users, allowing them to use malicious JavaScript code, which will be executed when anyone…

Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…

The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…