
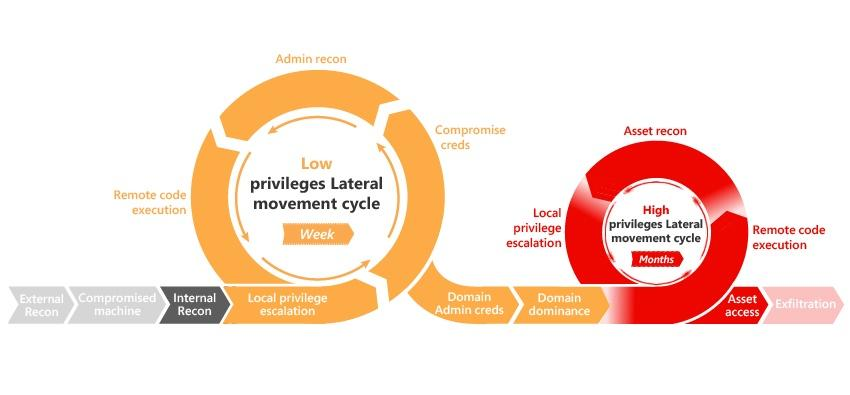
AD-Attack-Defense
 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
curated-resourcesdefensive-toolseducation+7
infosecn1nja/ad-attack-defenseAttack and defend active directory using modern post exploitation adversary tradecraft activity
 redcode-labs/bashark
Bash post exploitation toolkit
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
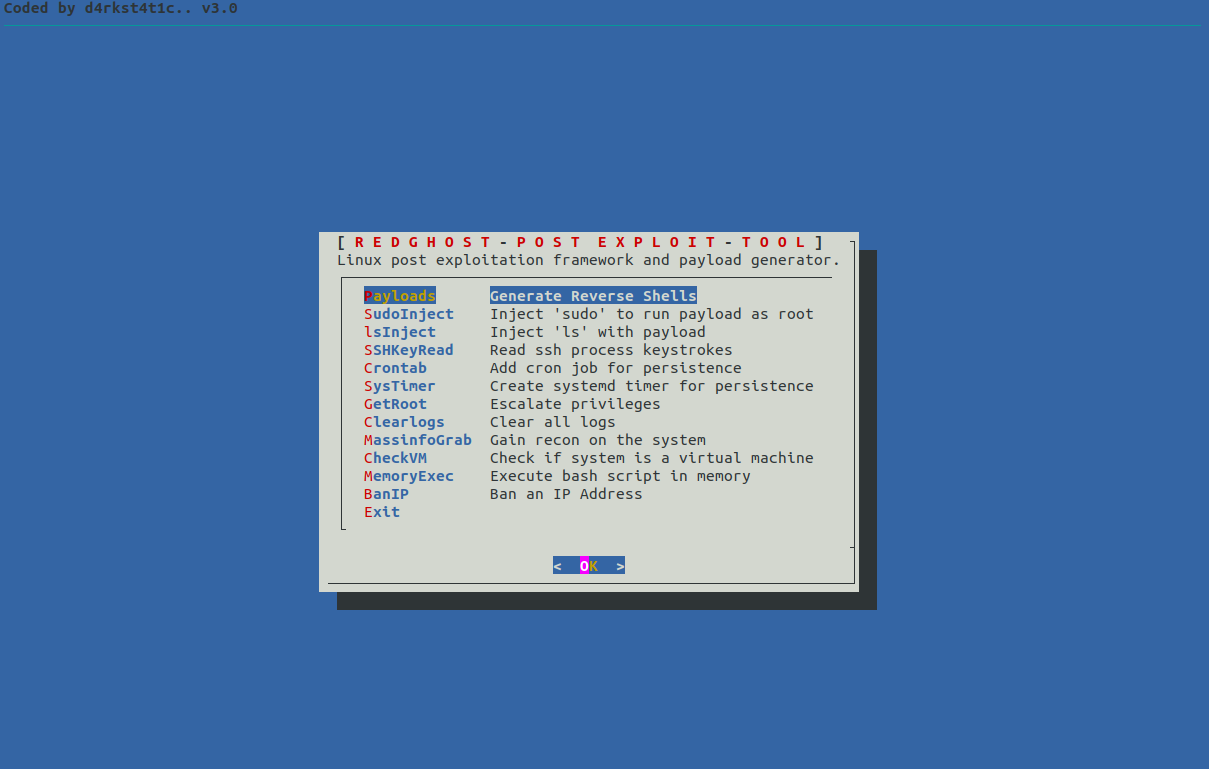 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
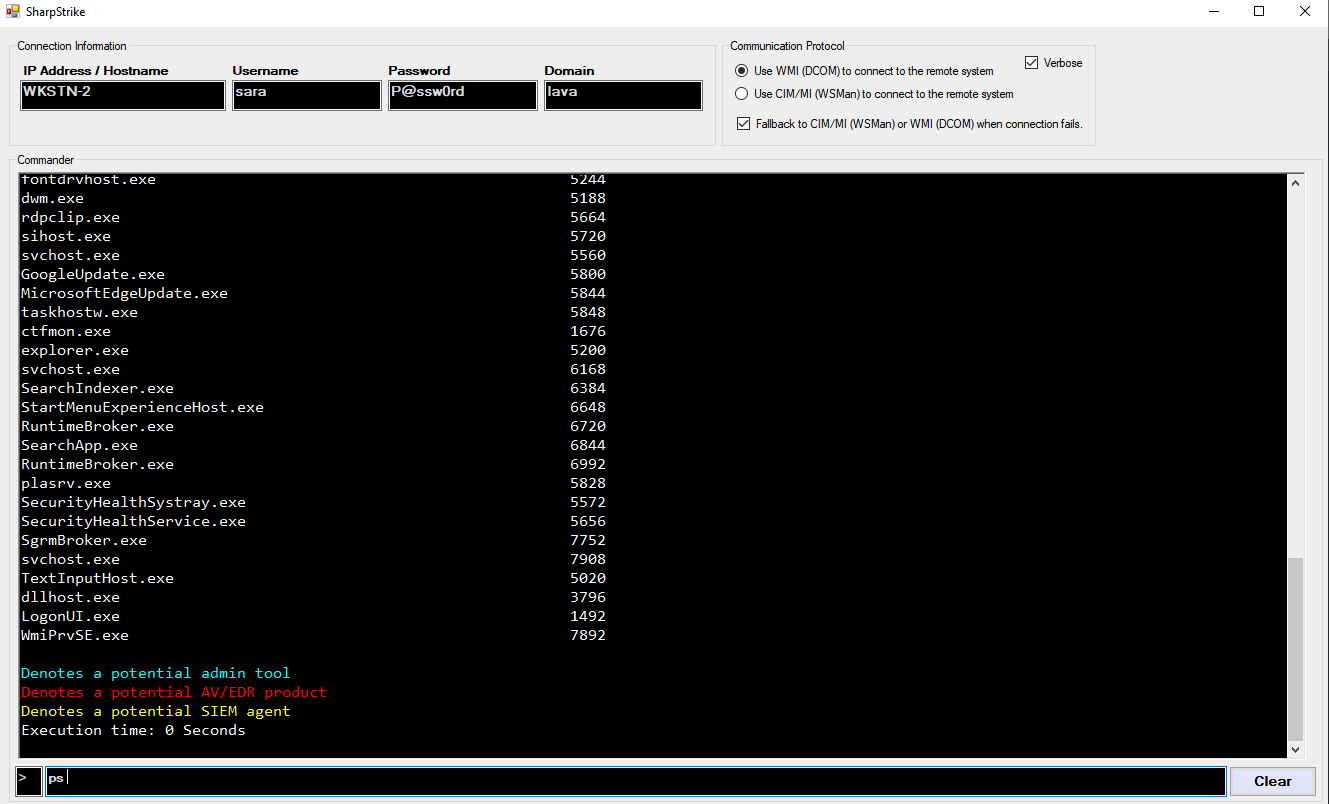 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
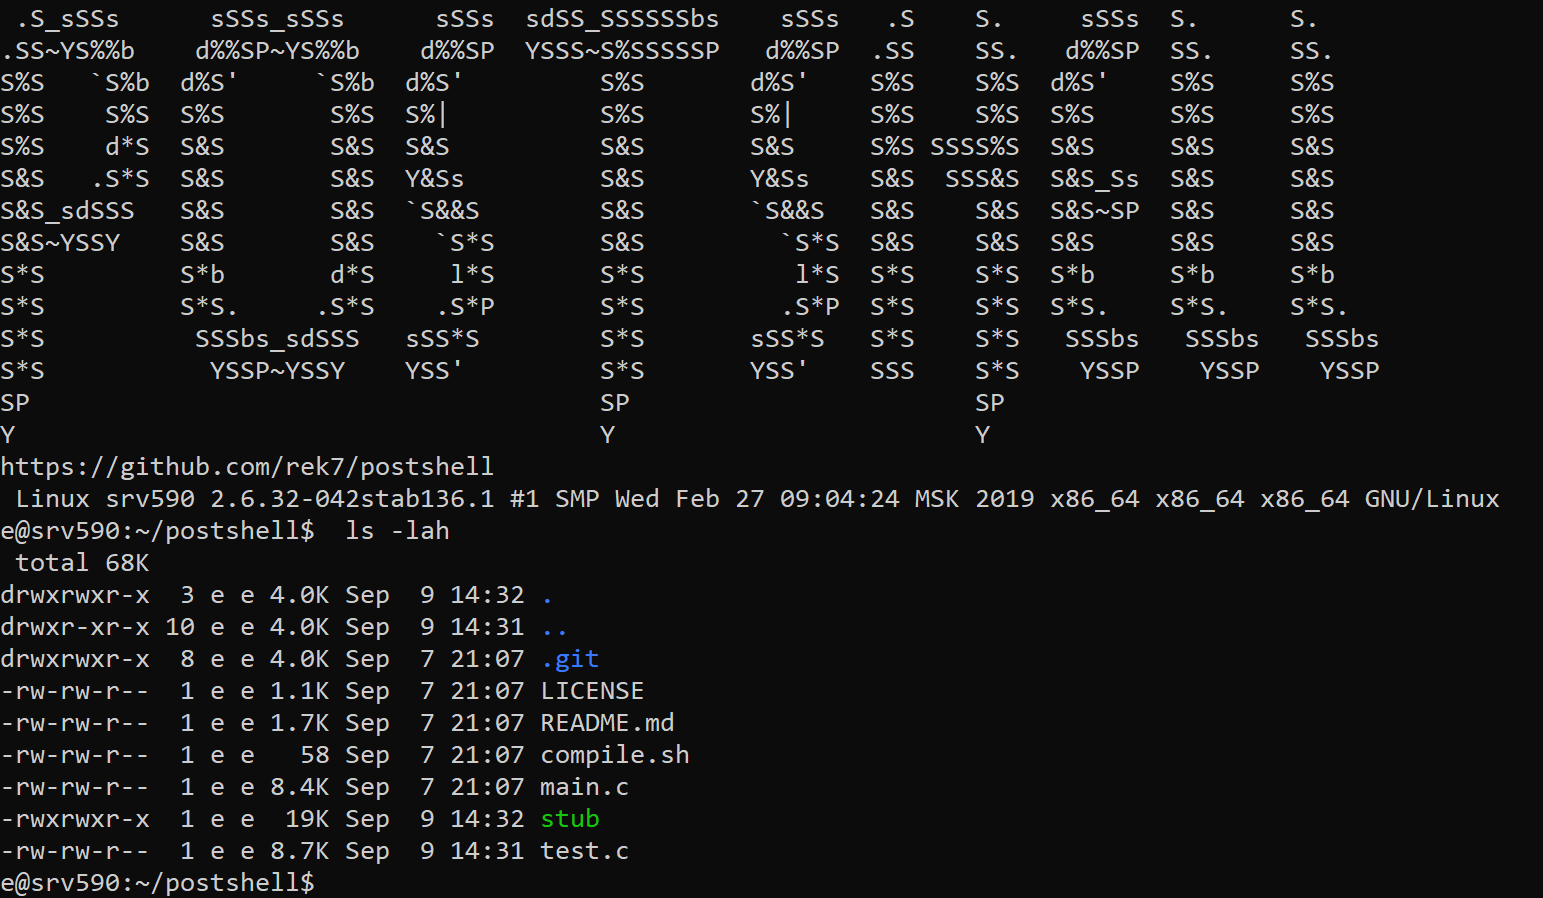 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 yo-yo-yo-jbo/macos_sandbox
Blog post exploring macOS App Sandbox, entitlements via codesign, and sandbox escape techniques using launchd, LaunchAgents, and quarantine…
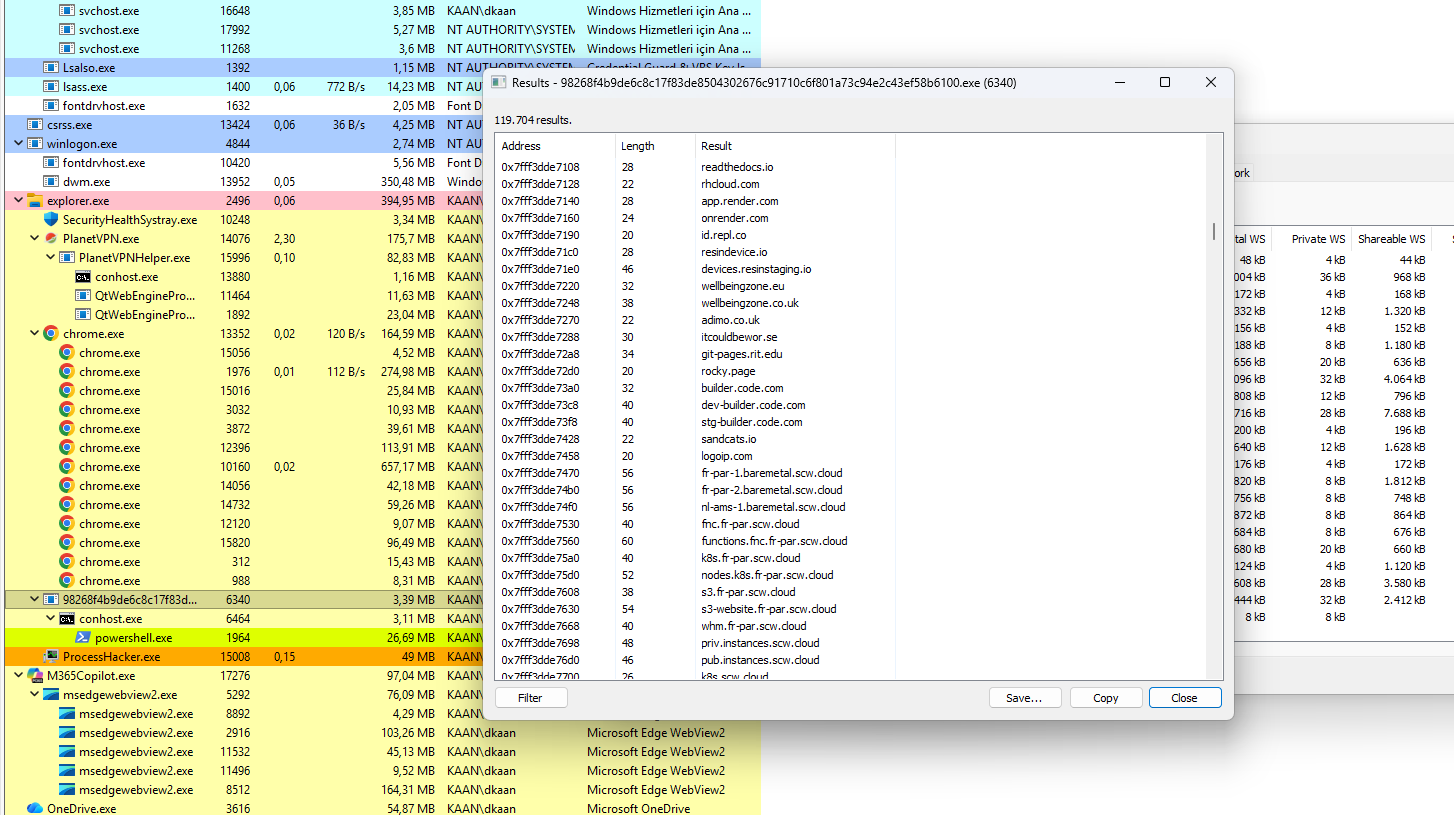 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra — taken past the base PoC to show how a common…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
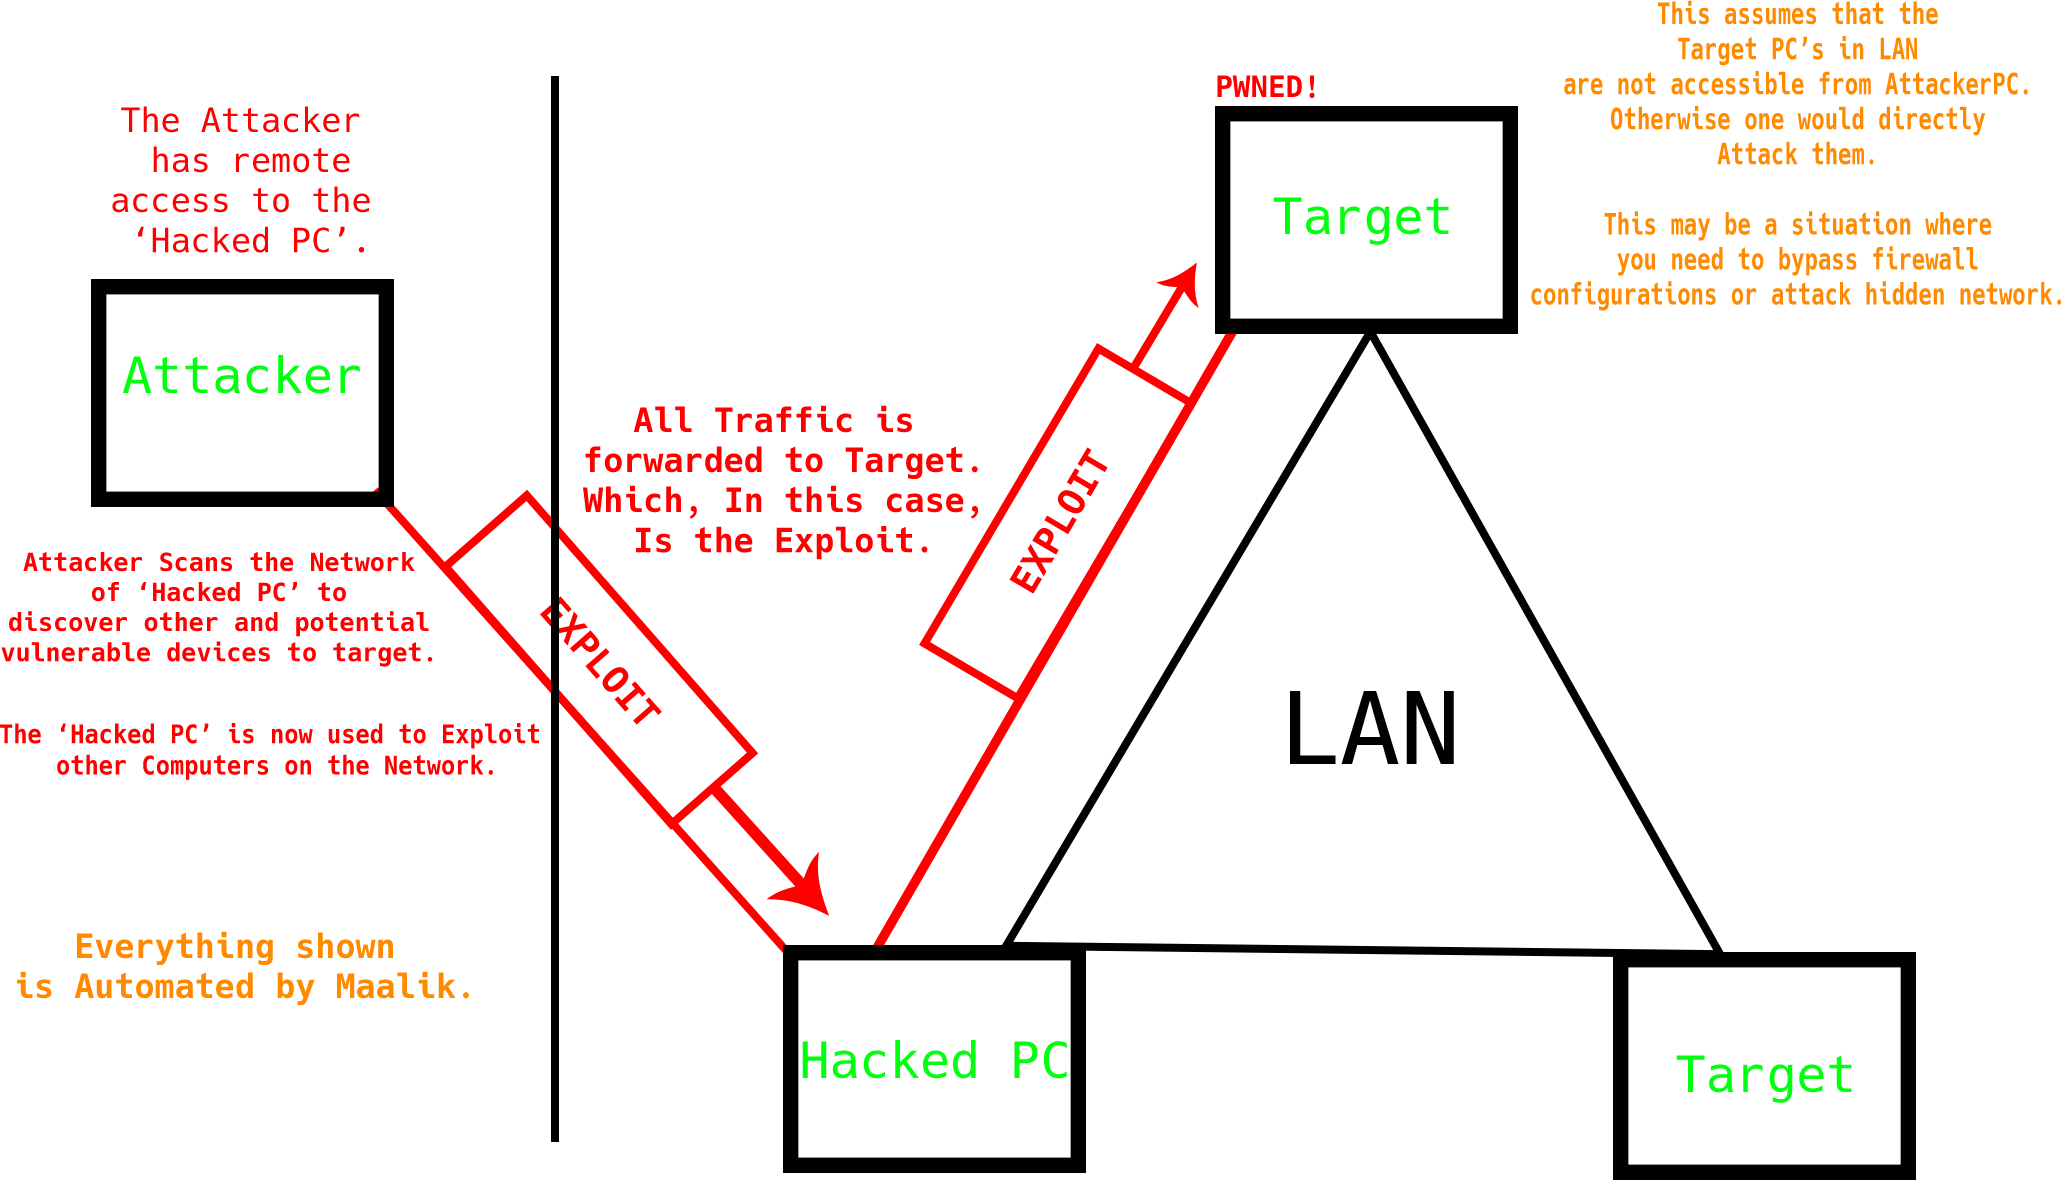 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 fr0gger/awesome_malware_techniques
This is a repository of resource about Malware techniques