
shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…

Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…

Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

Adversary Emulation Framework

BlackLotus UEFI Windows Bootkit

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…

Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…

Curated reference of Windows persistence mechanisms across registry, scheduled tasks, services, and more, designed to improve protection and…

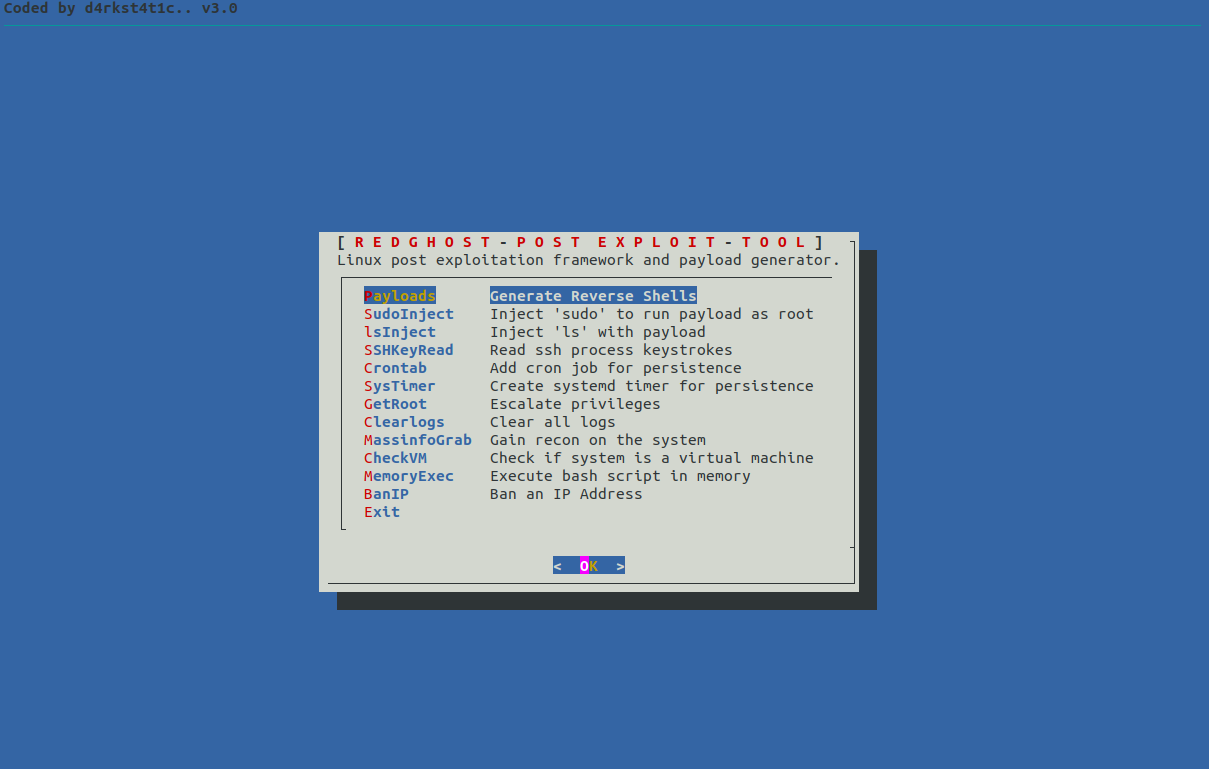
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.

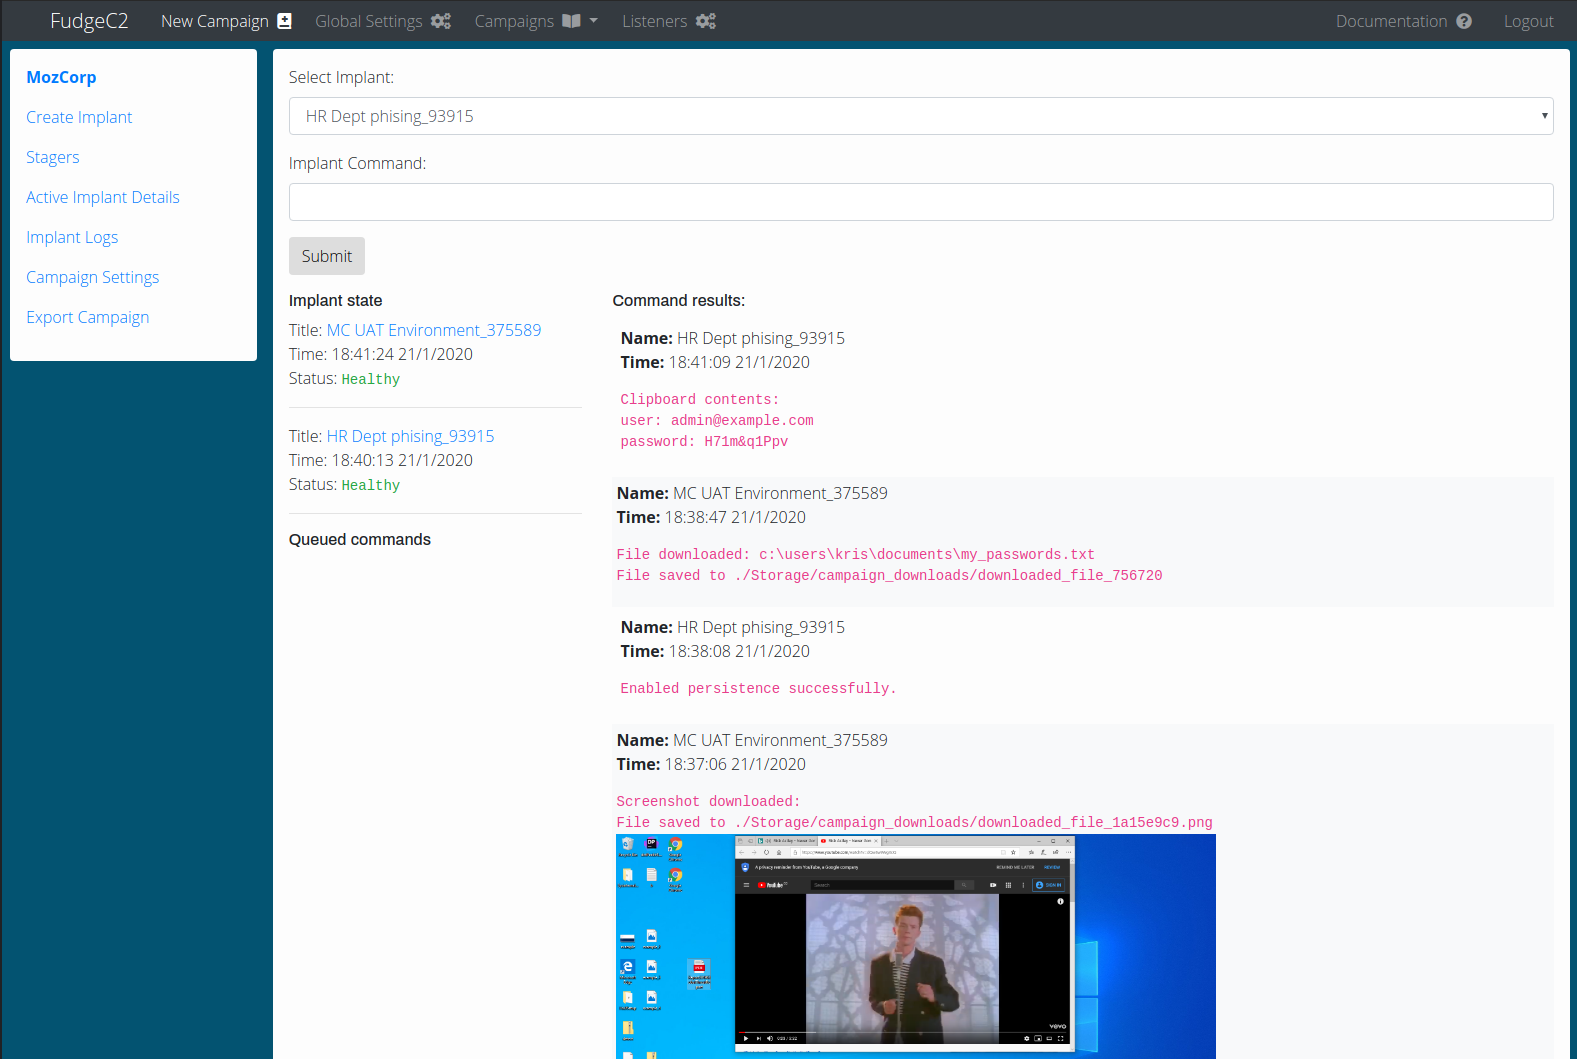
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.

C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…

CLI tool for applying and removing macOS persistence mechanisms, designed for threat emulation and red team operations. Supports 17 techniques…

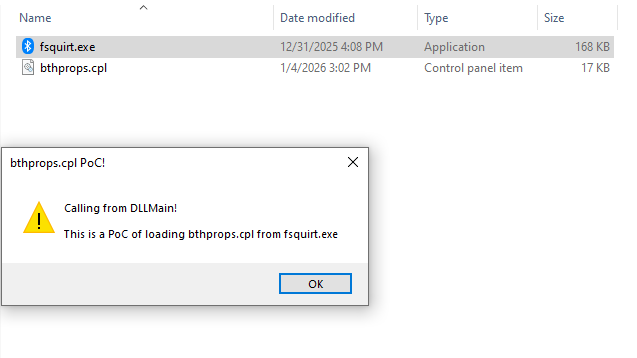
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin

Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…

🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.

A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

RefleXXion is a utility designed to aid in bypassing user-mode hooks utilised by AV/EPP/EDR etc. In order to bypass the user-mode hooks, it first…

Attack and defend active directory using modern post exploitation adversary tradecraft activity