honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

A simple remote tool in C#.

Creates invisible Windows accounts with administrative privileges via direct SAM manipulation and RID hijacking, bypassing standard user management…

Simple (relatively) things allowing you to dig a bit deeper than usual.

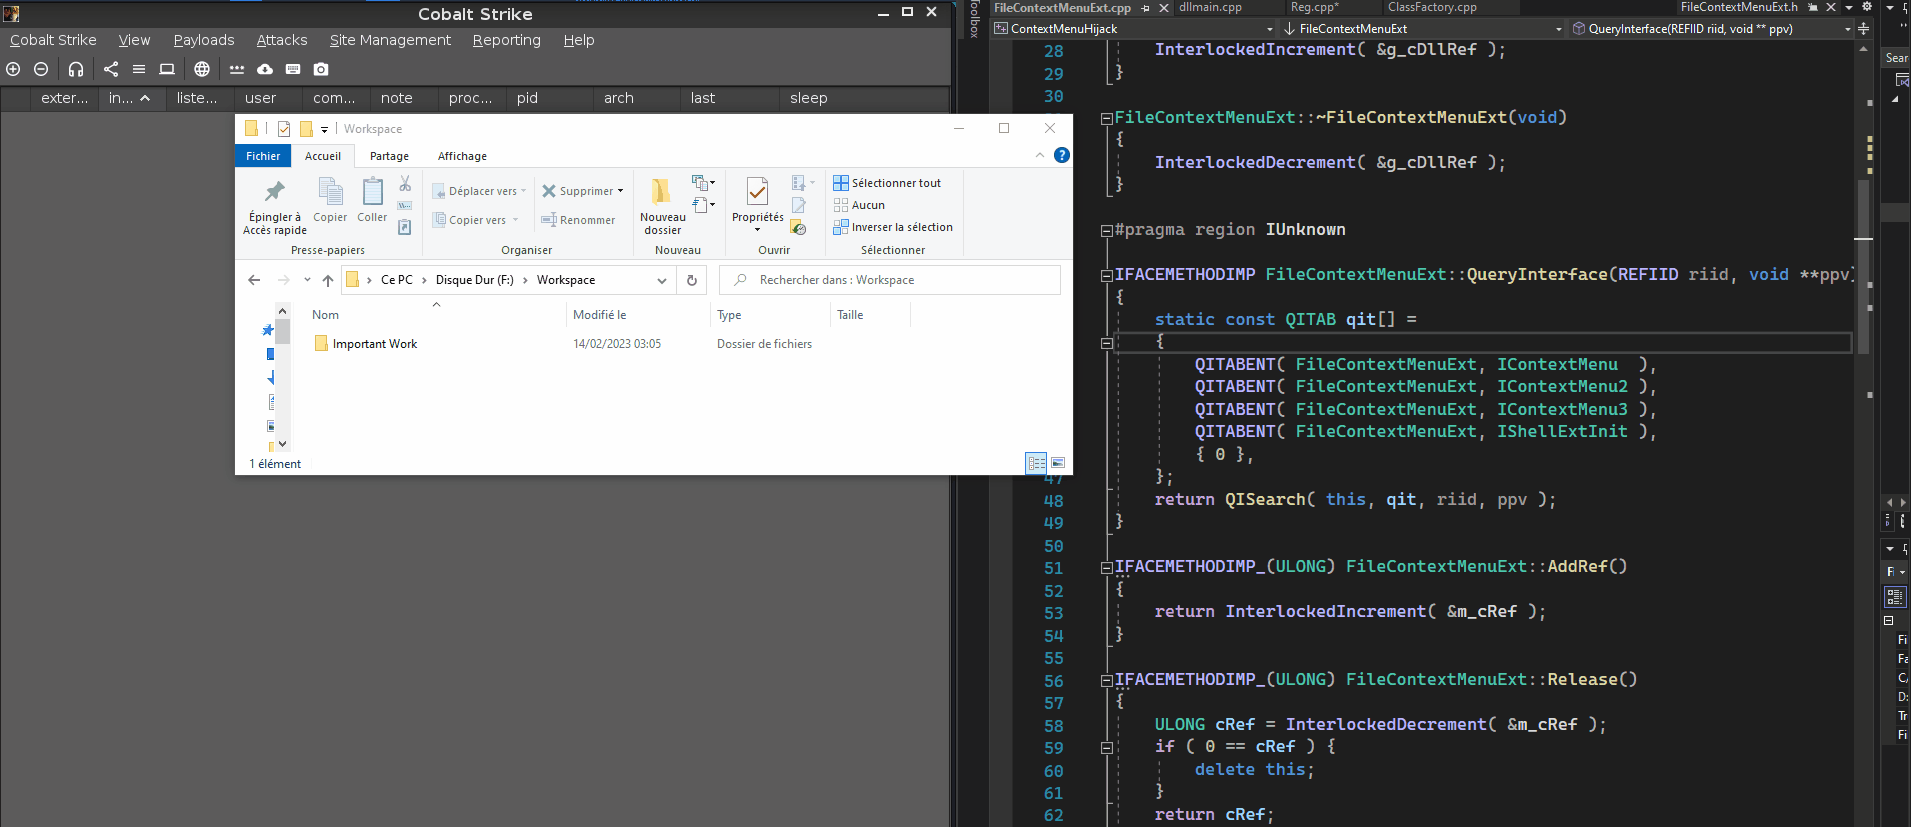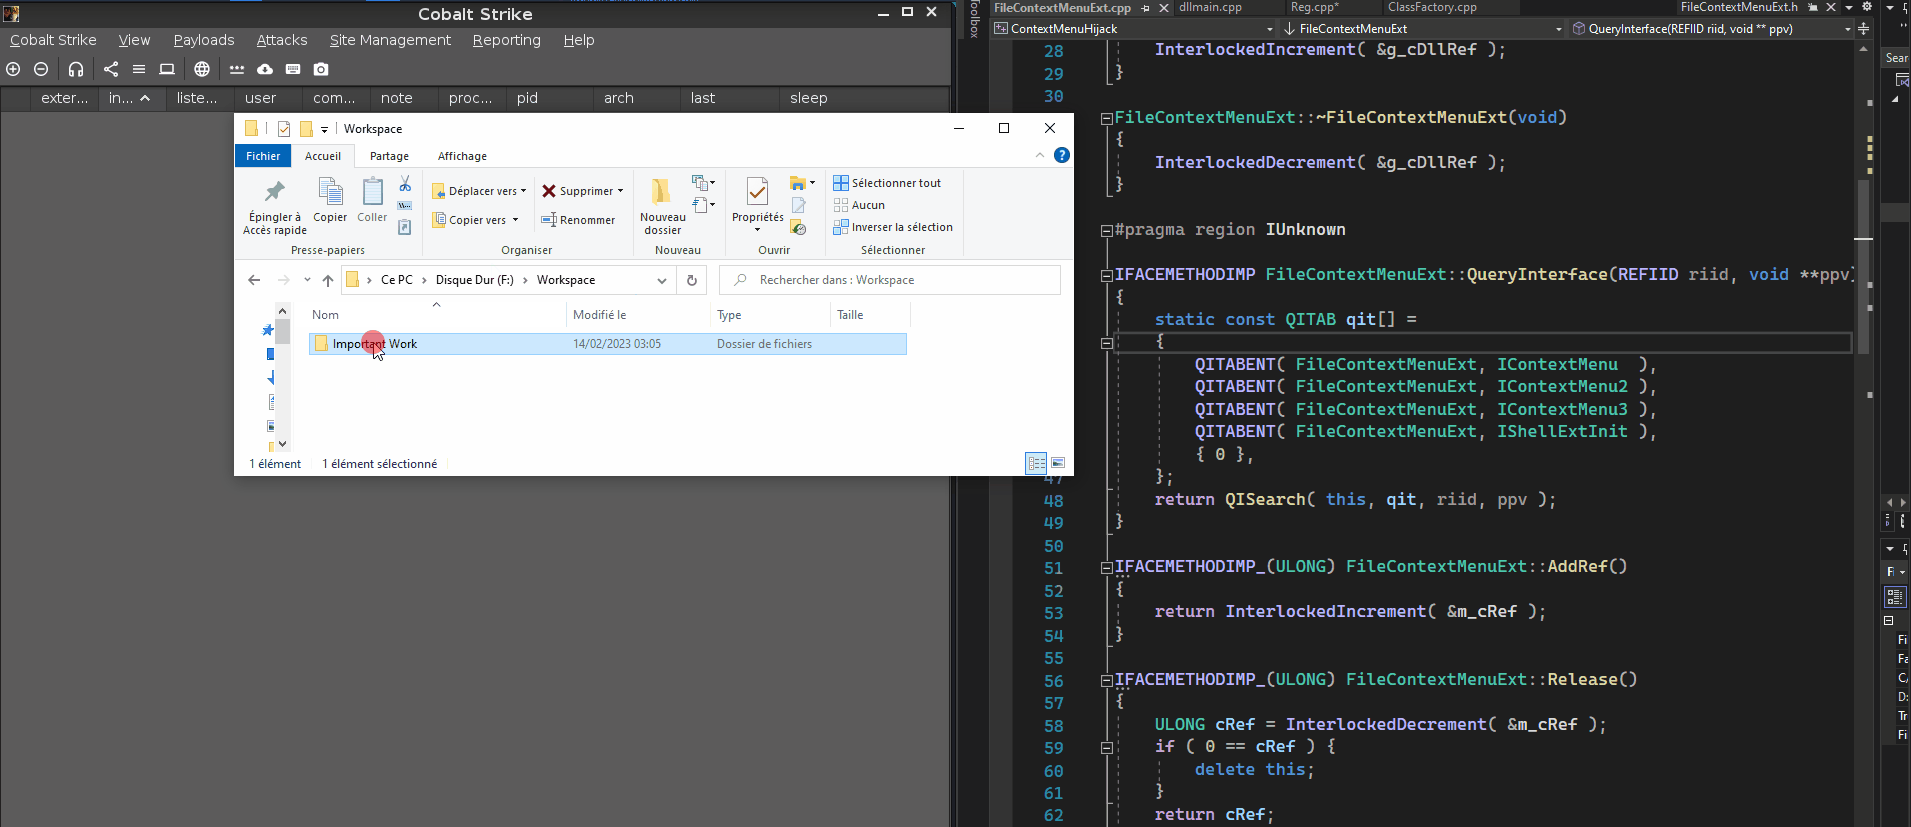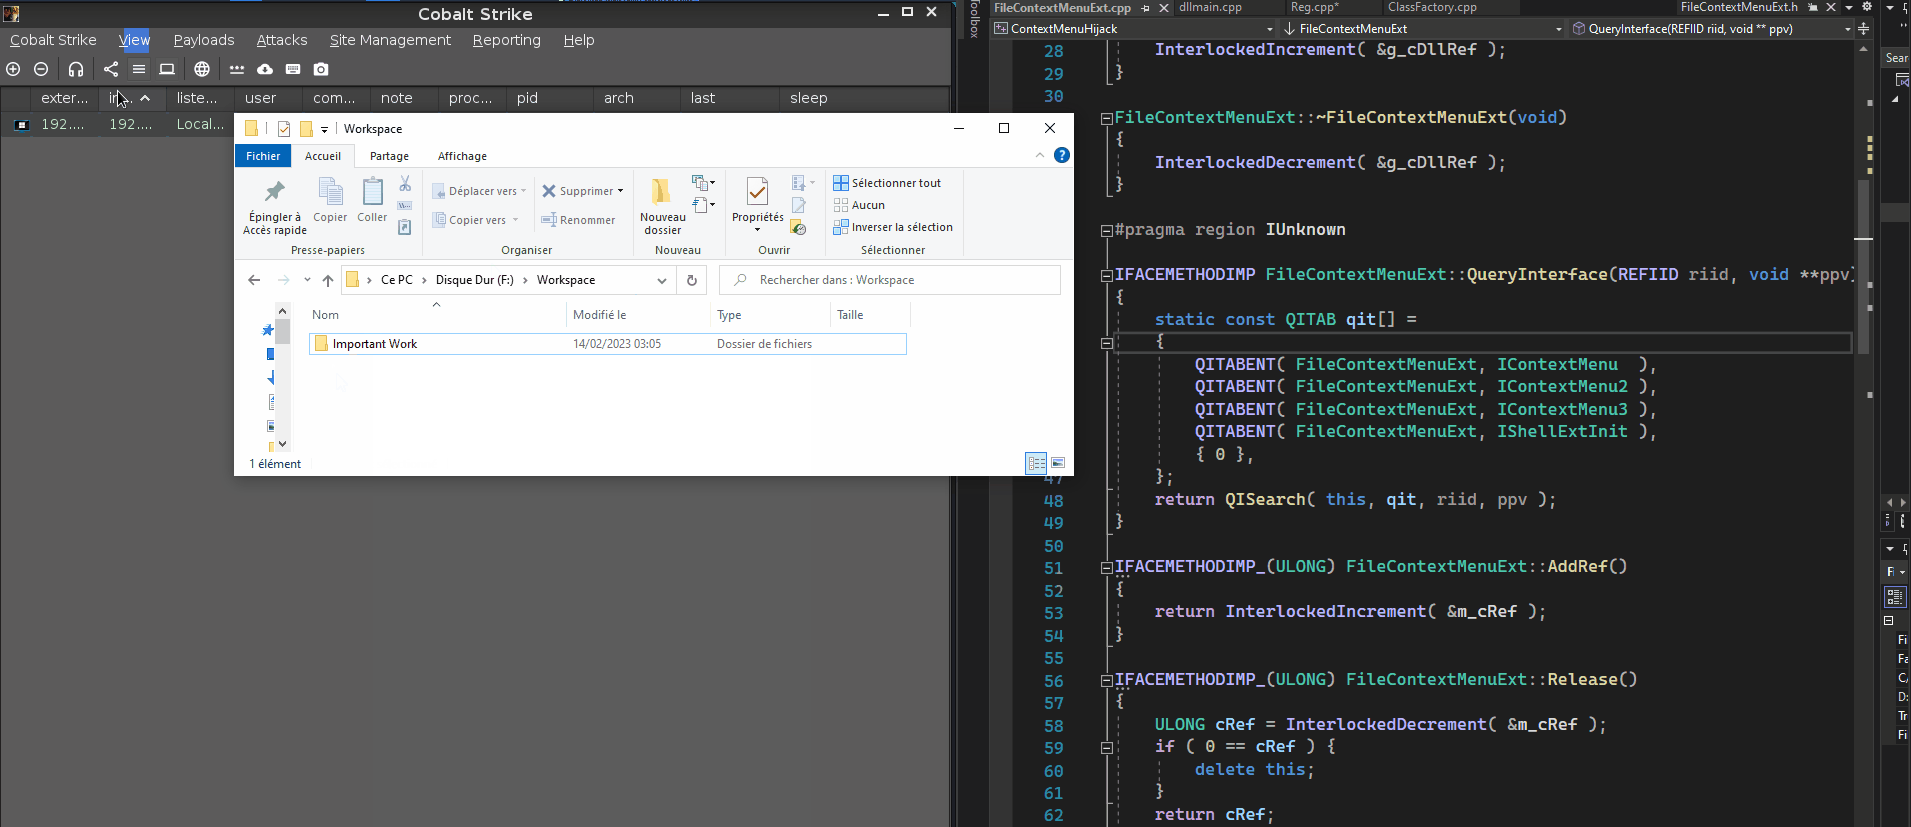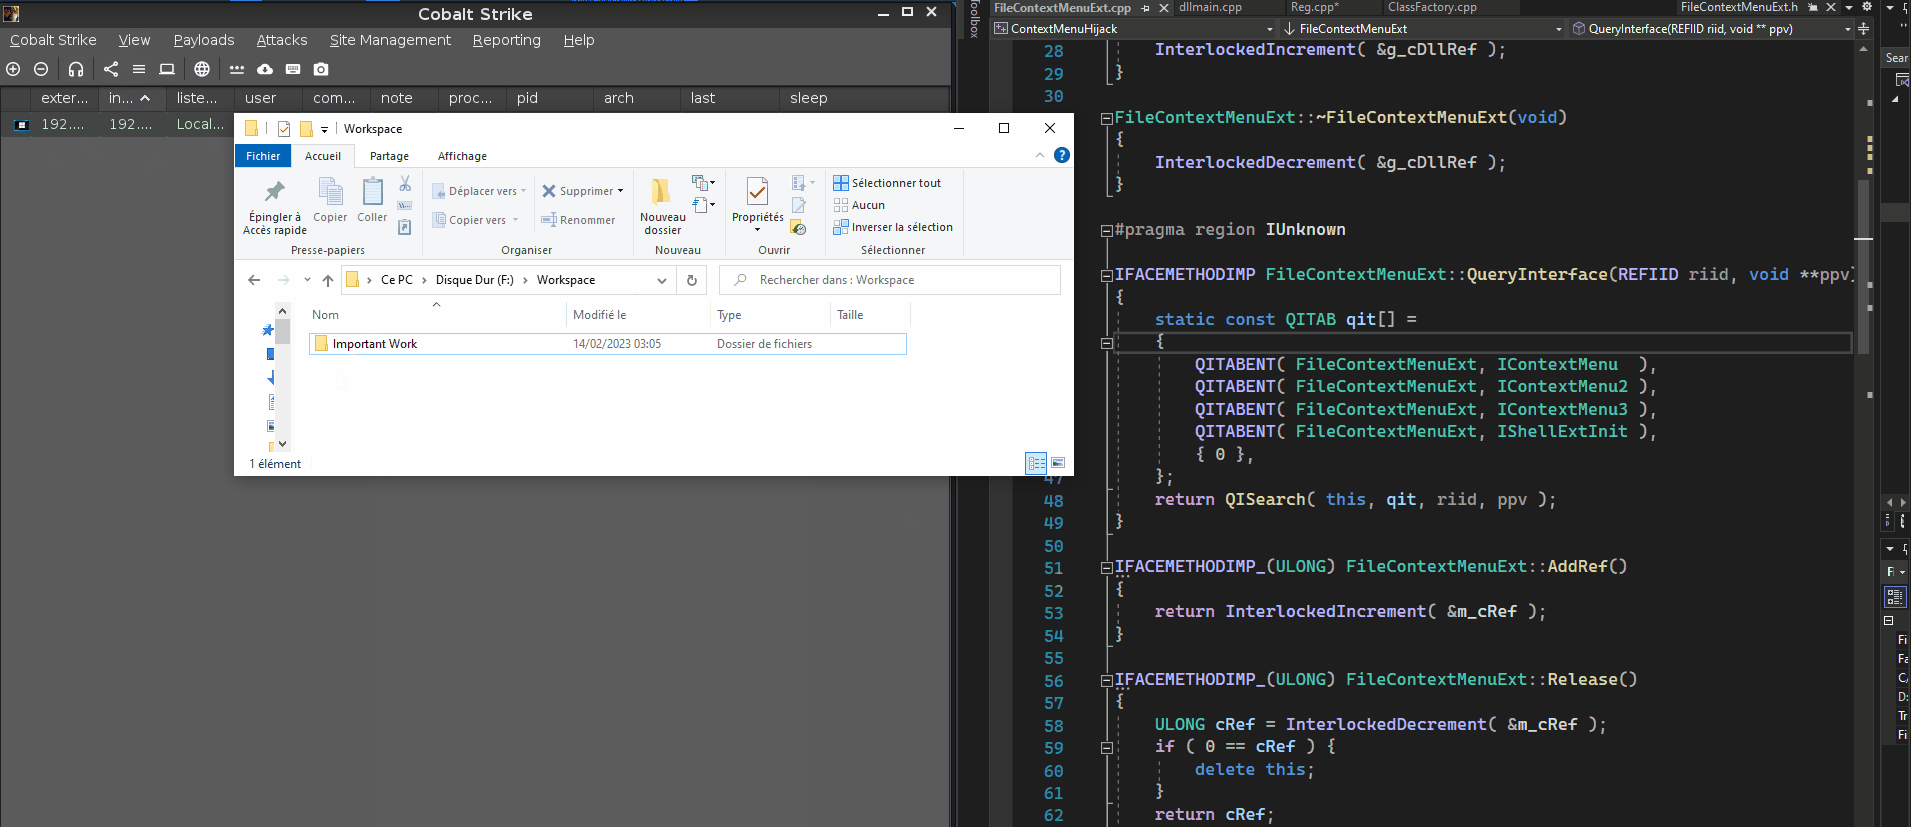
Execute a payload at each right click on a file/folder in the explorer menu for persistence

Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…

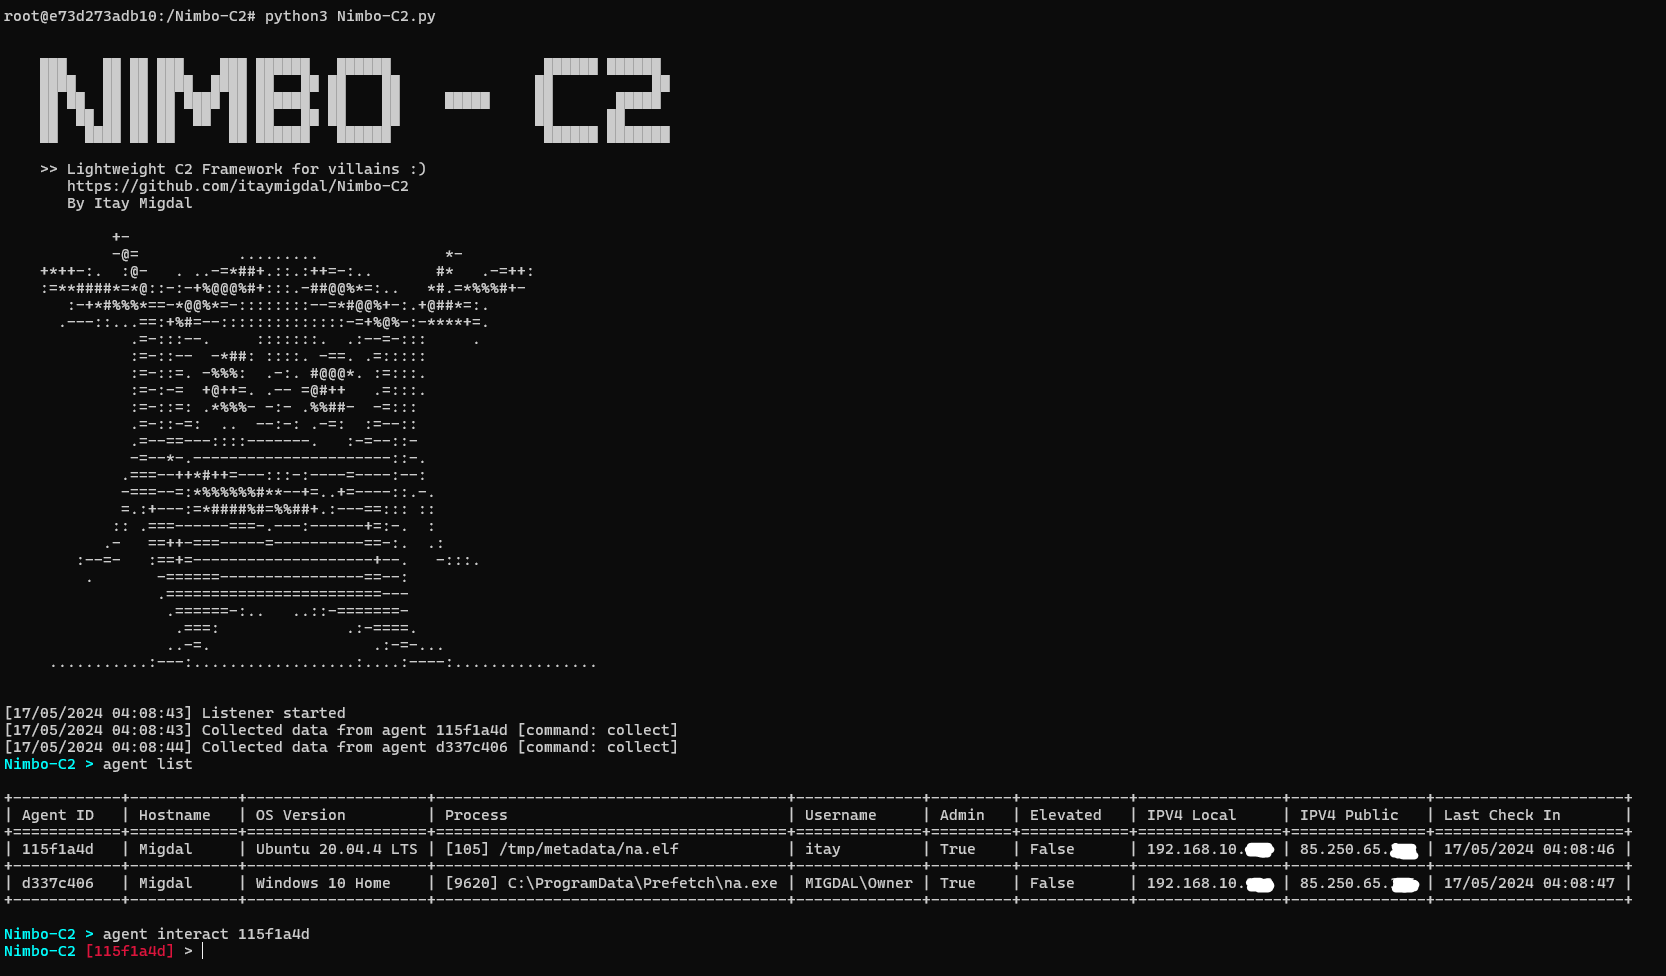
Nimbo-C2 is yet another (simple and lightweight) C2 framework

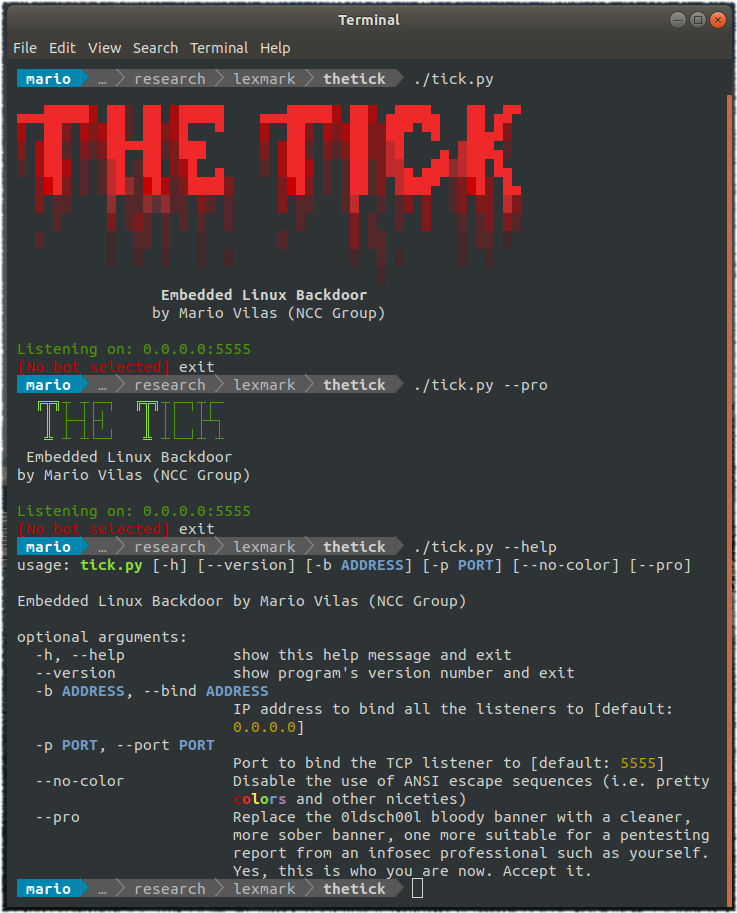
A simple embedded Linux backdoor.

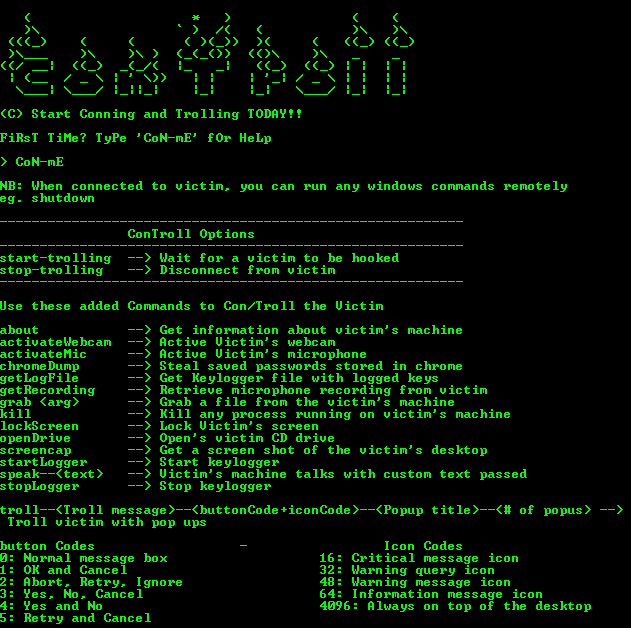
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…

A simple C2 Framework written in modern C++

A simple python reverse shell written just for fun.