
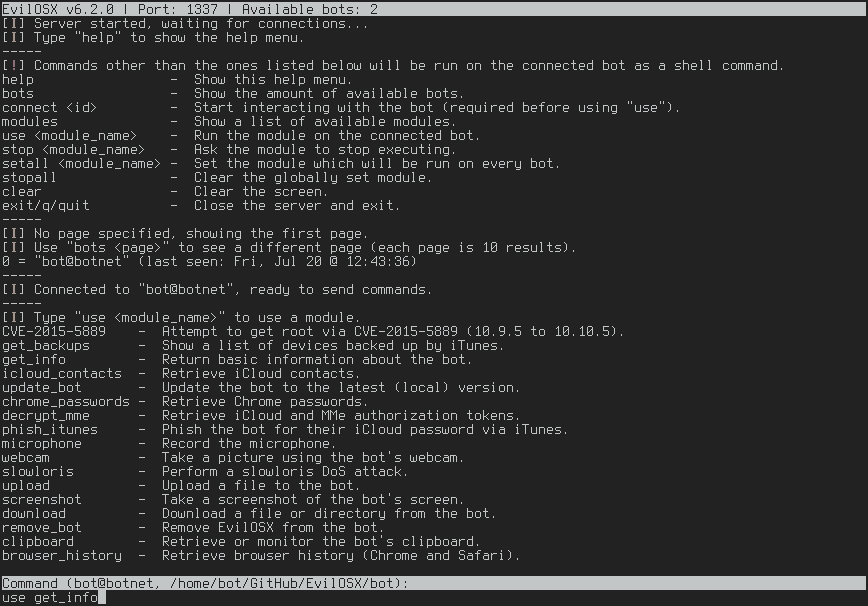
EvilOSX
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
command-and-controlinformation-gatheringpassword-cracking+6
marten4n6/evilosxAn evil RAT (Remote Administration Tool) for macOS / OS X.
 enzolovesbacon/inficere
Mac OS X rootkit - for learning purposes
 cys3c/evilosx
A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 bmax121/apatch
The patching of Android kernel and Android system
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
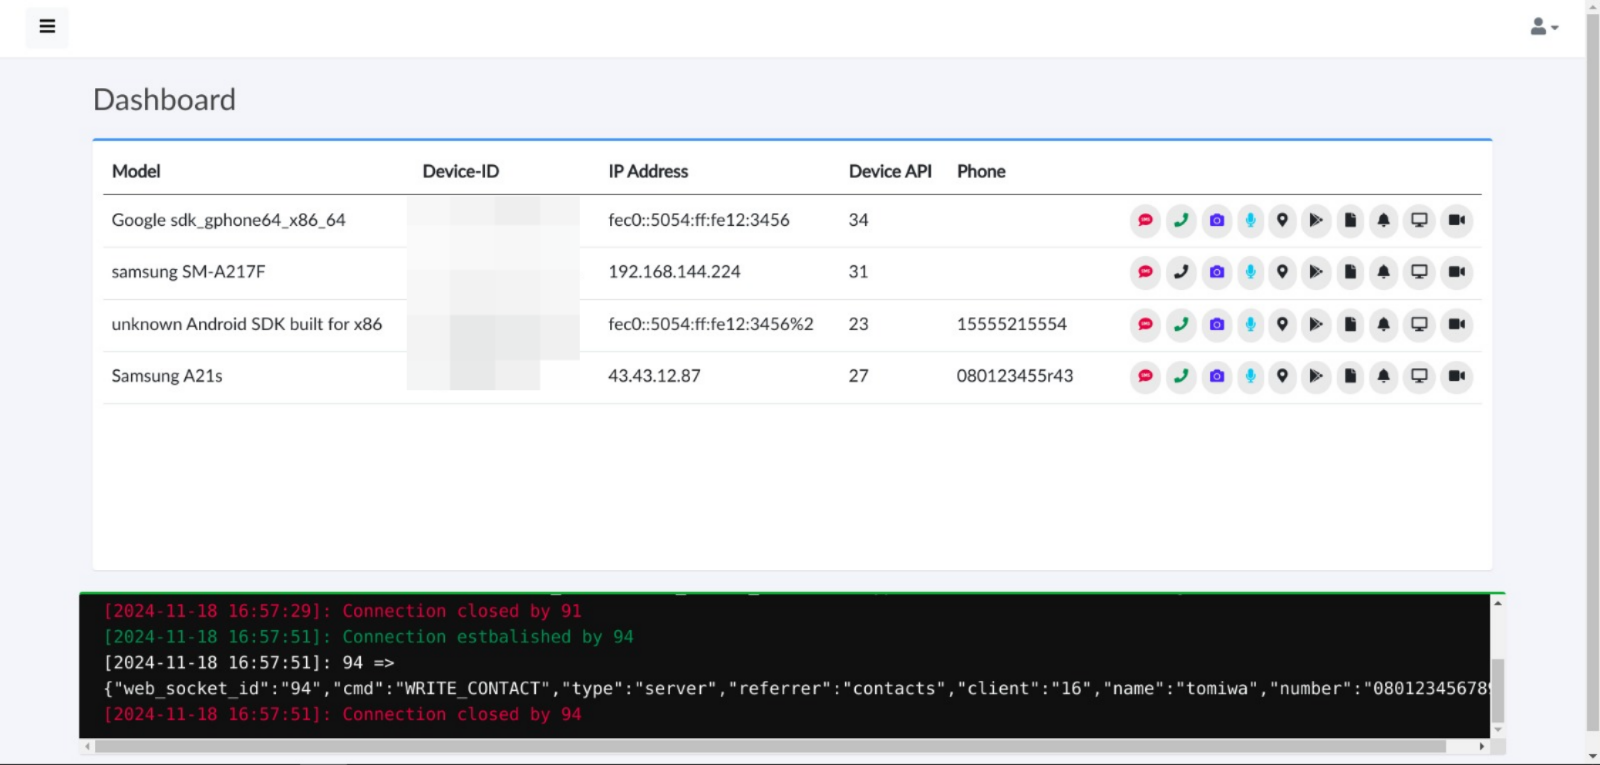 tomiwa-ot/moukthar
Android remote administration tool
 mwsrc/betterandrorat
Android Remote Access Trojan
 alephsecurity/initroot
Motorola Untethered Jailbreak: Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
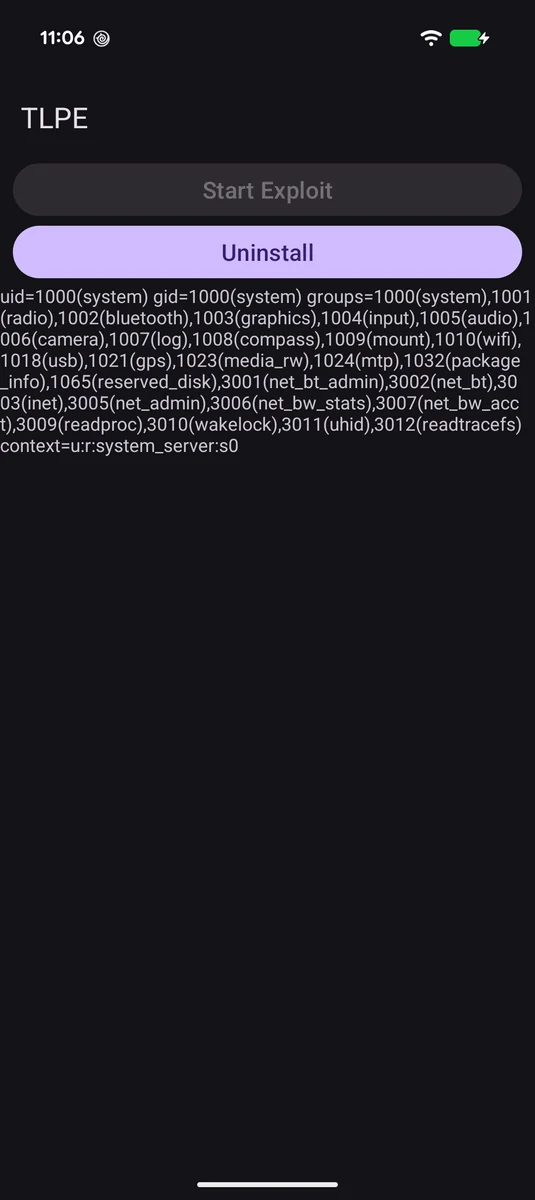 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180