
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
PersistenceSniper preview

PersistenceSniper

GitHublast-byte/persistencesniper

Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
defensive-toolsforensicsincident-response+1
2.1k
1 year ago
Trawler preview

Trawler

GitHubjoeavanzato/trawler

PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
defensive-toolsdigital-forensicsforensics+2
3421 year ago
MrKaplan preview

MrKaplan

GitHubidov31/mrkaplan

PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
defensive-toolsforensicsids-ips-evasion+3
2763 years ago
NorkNork preview

NorkNork

GitHubn00py/norknork

Powershell Empire Persistence finder
defensive-toolsforensicsincident-response+2
1189 years ago
FarsightAD preview

FarsightAD

GitHubqazeer/farsightad

PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
forensicsincident-responseinformation-gathering+5
989 months ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolsforensicshash-analysis+4
661 year ago
macos-collector preview

macos-collector

GitHublethal-forensics/macos-collector

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
digital-forensicsforensicsincident-response+2
541 month ago
mini-shai-hulud-scanner preview

mini-shai-hulud-scanner

GitHubintrudify/mini-shai-hulud-scanner

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
forensicsincident-responseioc-management+6
35 months ago
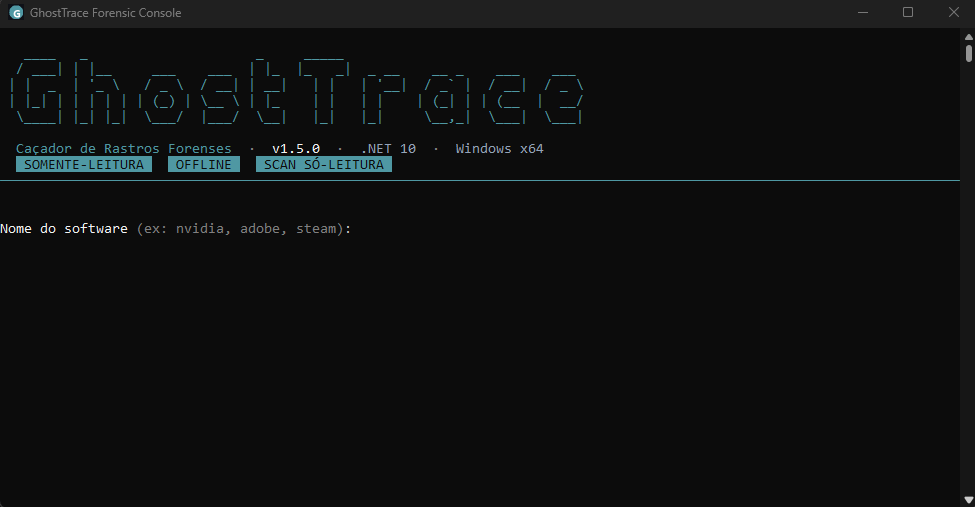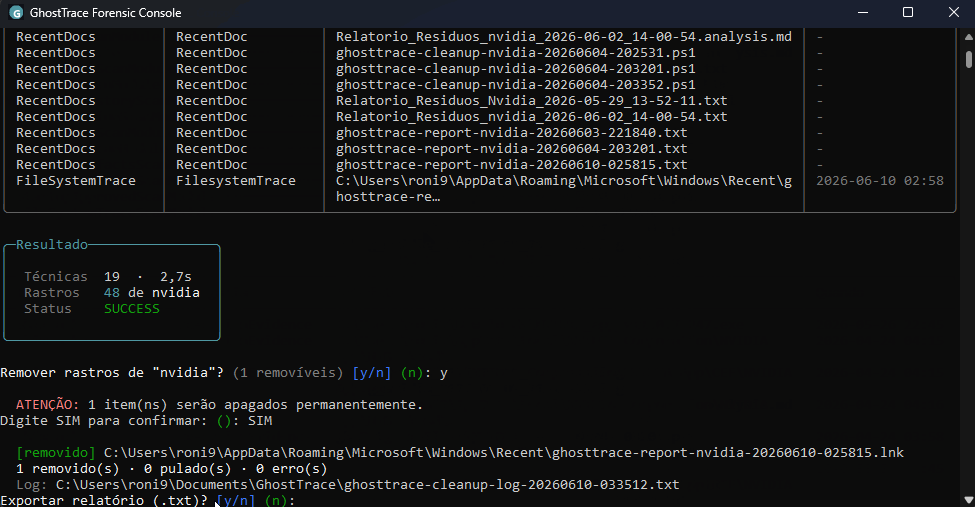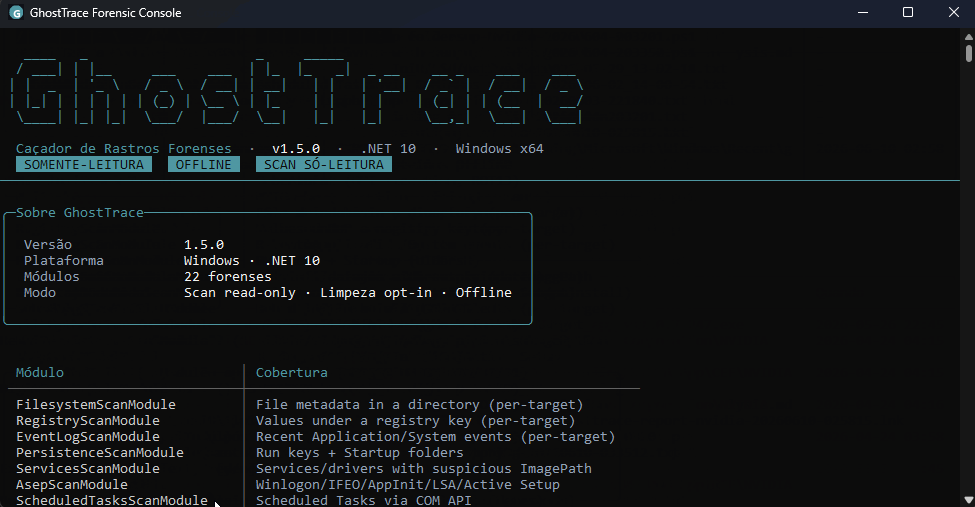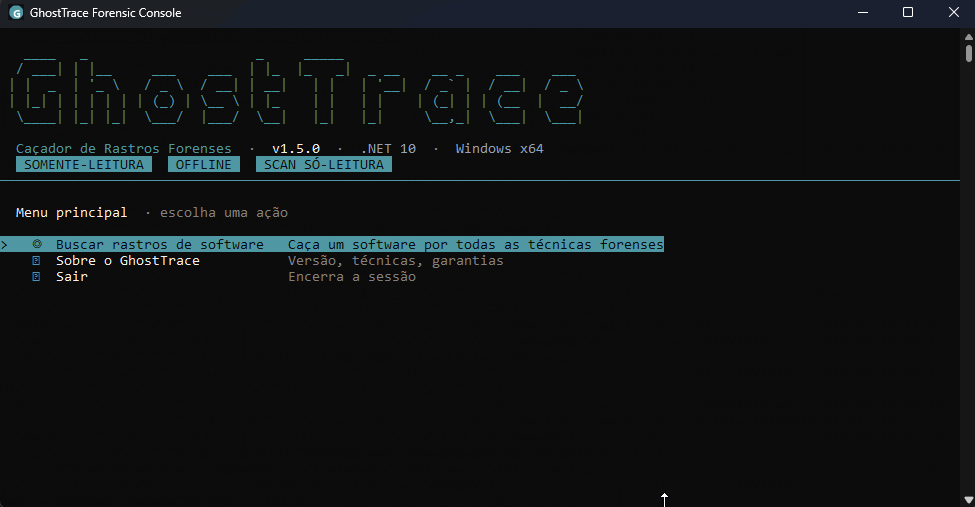
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
3 months ago
tanstack-compromise-checker preview

tanstack-compromise-checker

GitHubry-allan/tanstack-compromise-checker

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
command-and-controlforensicsincident-response+6
5 months ago
Dr0p1t-Framework preview
Archived

Dr0p1t-Framework

GitHubd4vinci/dr0p1t-framework

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
anti-botcommand-and-controlexploitation+9
1.5k7 years ago
THM-Tempest preview

THM-Tempest

GitHubczabatta/thm-tempest

TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts

command-and-controlctfdigital-forensics+9
4 months ago