
metta
 uber-common/metta
An information security preparedness tool to do adversarial simulation.
adversarial-attackdefensive-toolseducation+8
1.1k
uber-common/mettaAn information security preparedness tool to do adversarial simulation.
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 sobri3195/pegasus-gram
Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 ash1996x/cve-2025-54914-poc
Exploit for CVE-2025-54914 in Azure Networking, creating malicious routes with evasion, persistence, multi-target scanning, and reporting for…
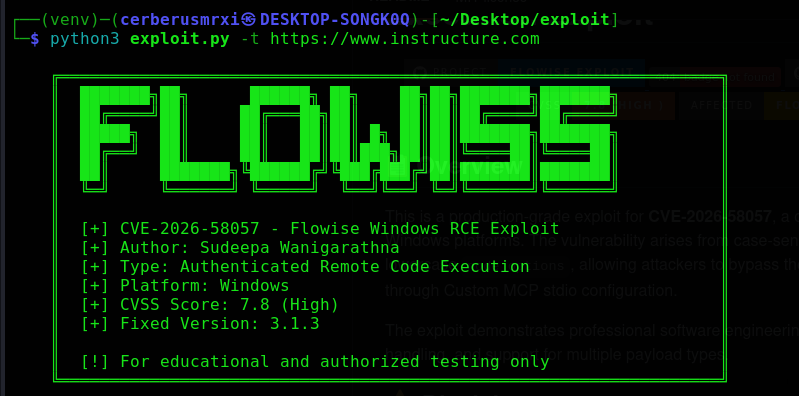 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 fazaroot/cve-2025-2539---file-away-wordpress-plugin-arbitrary-file-read
Authenticated arbitrary file read exploit for the File Away WordPress plugin (CVE-2025-2539). Includes PoC, attack flow, detection signatures, and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 redcode-labs/bashark
Bash post exploitation toolkit
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.