

GhostDriver
 blacksnufkin/ghostdriver
yet another AV killer tool using BYOVD
defensive-toolsexploitationids-ips-evasion+4
314
blacksnufkin/ghostdriveryet another AV killer tool using BYOVD
 s3cur3th1ssh1t/offensivevba
This repo covers some code execution and AV Evasion methods for Macros in Office documents
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
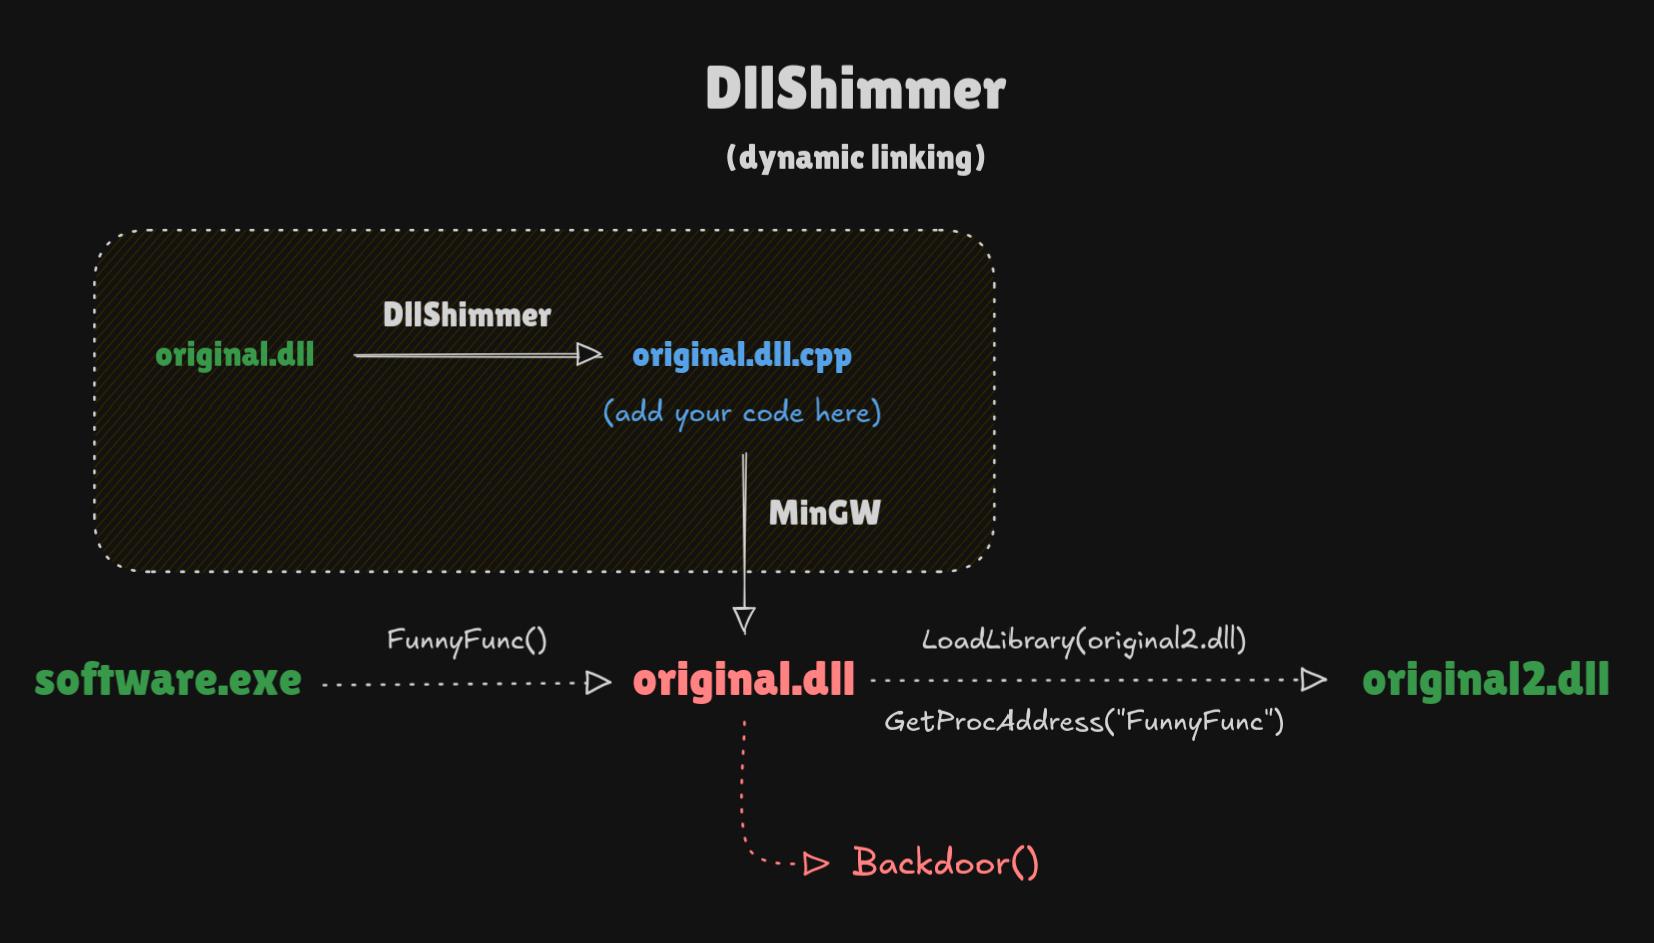 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 d00mfist/mystikal
macOS Initial Access Payload Generator
 nccgroup/accomplice
Tools for discovery and abuse of COM hijacks
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
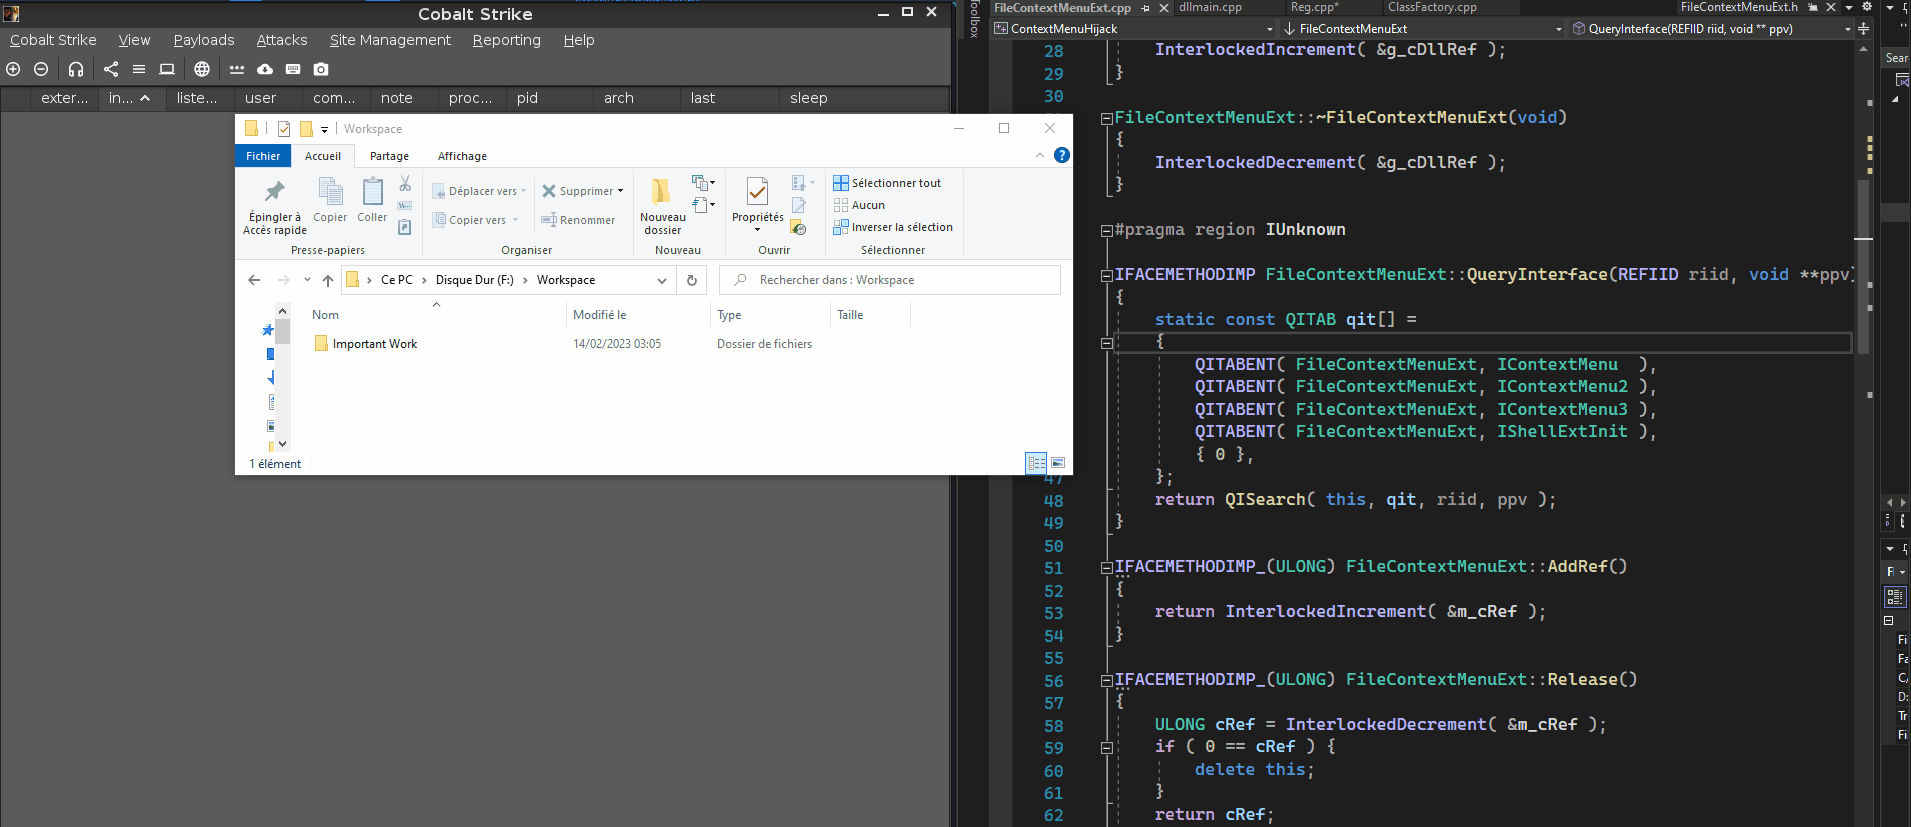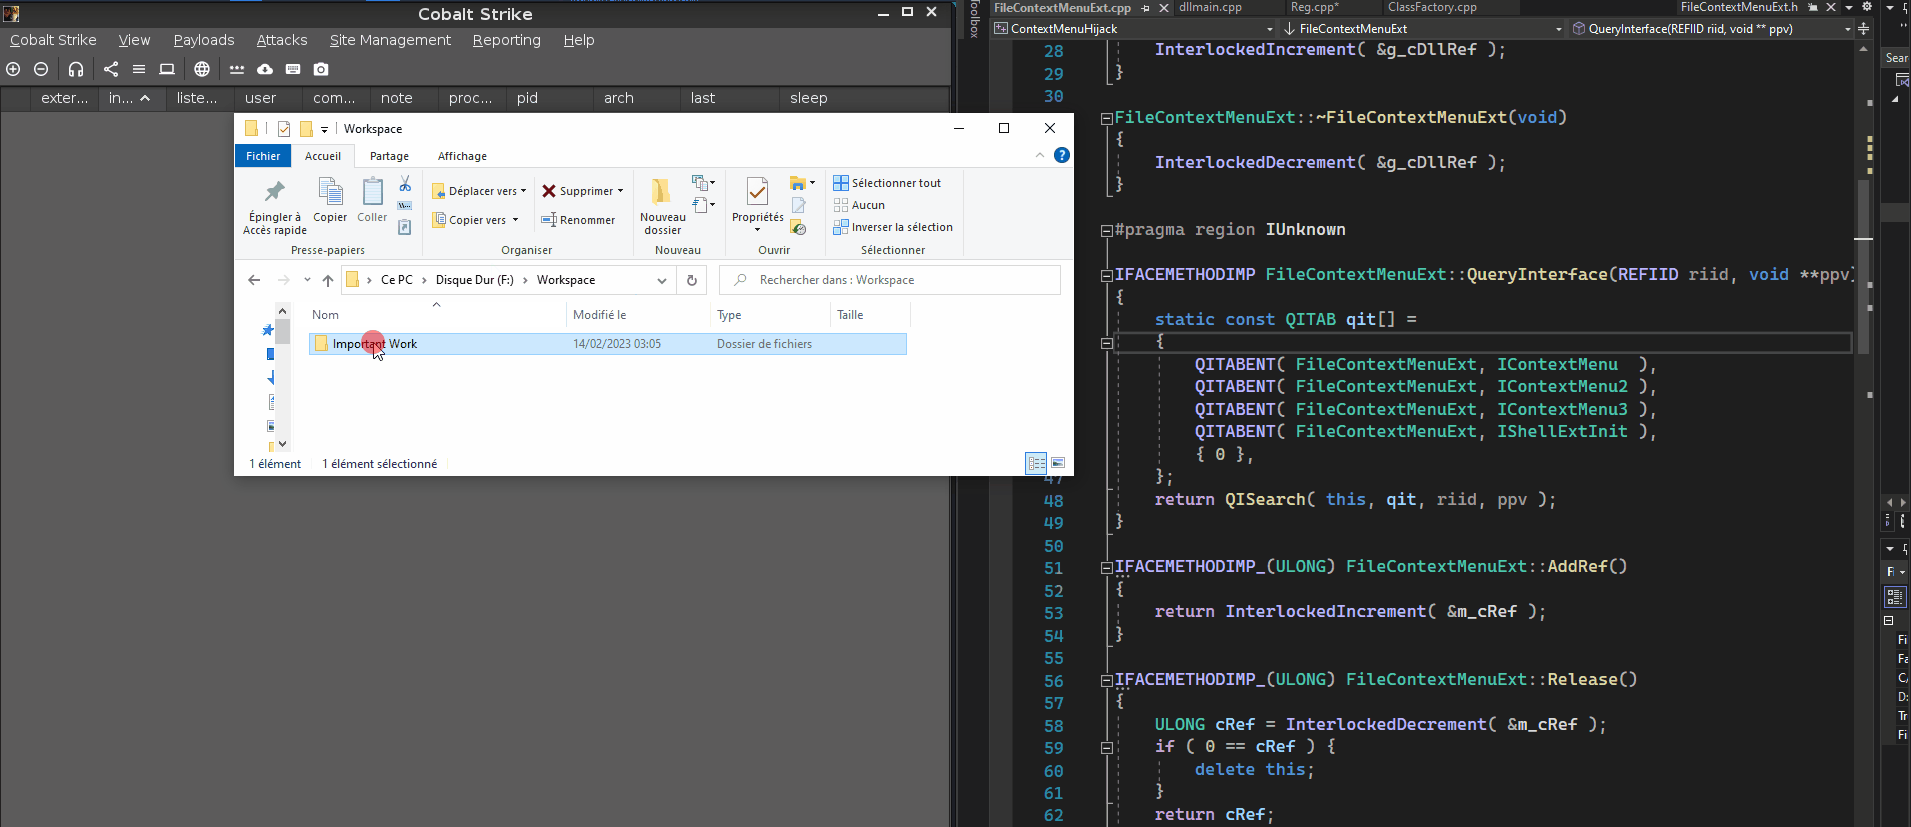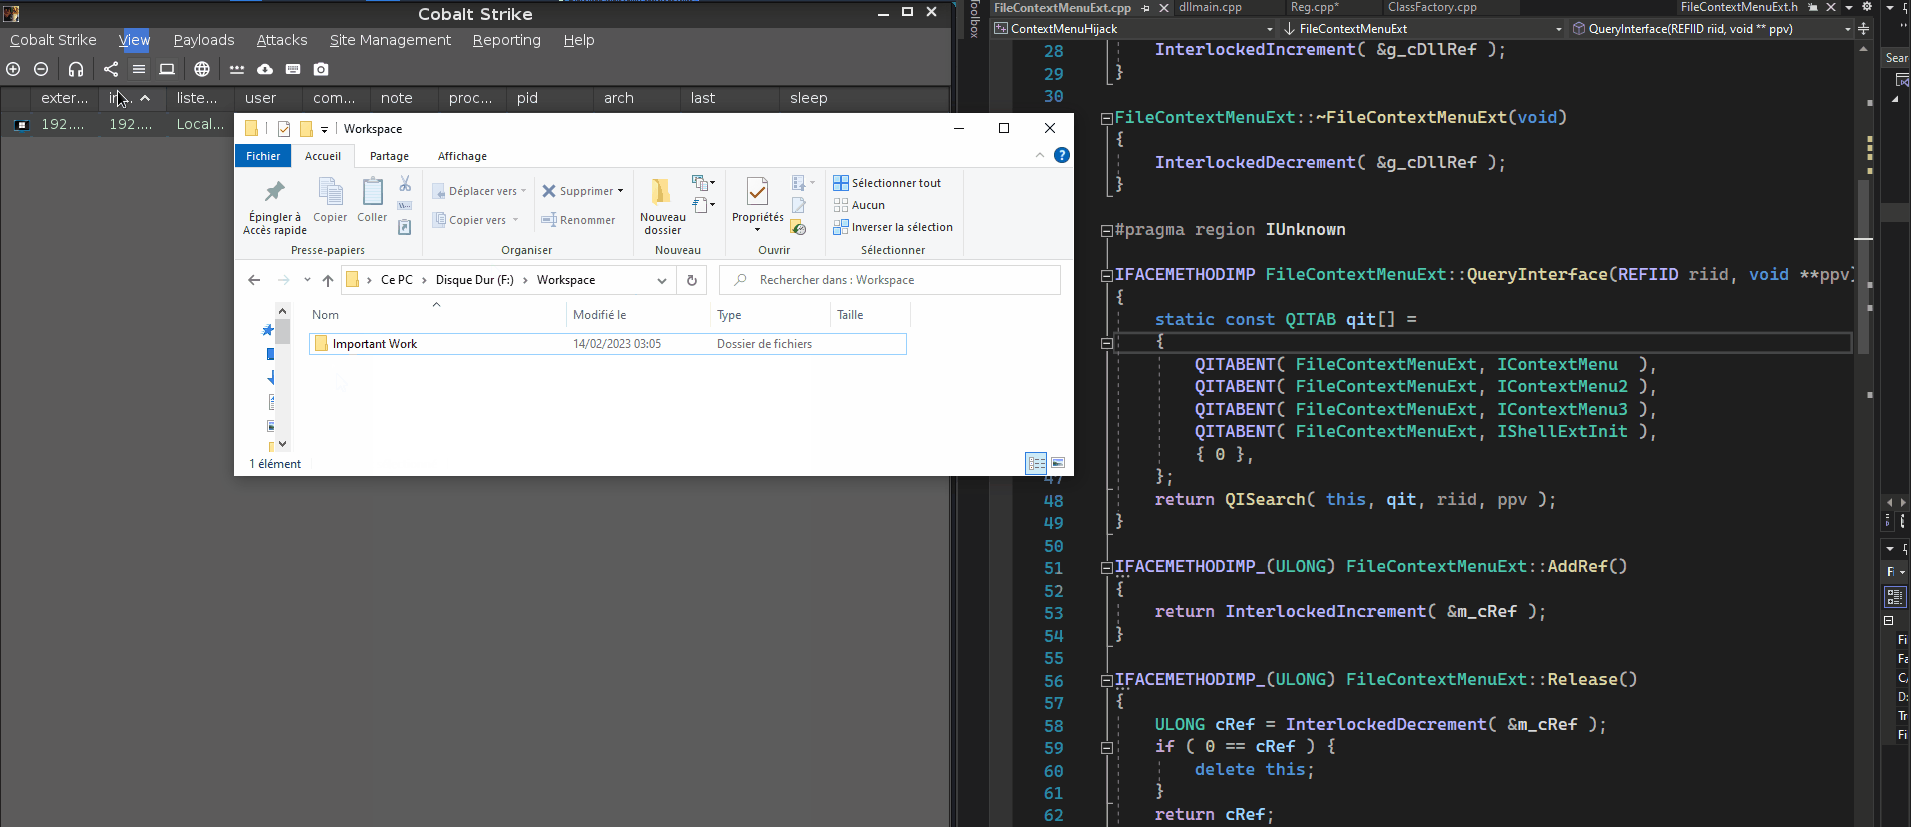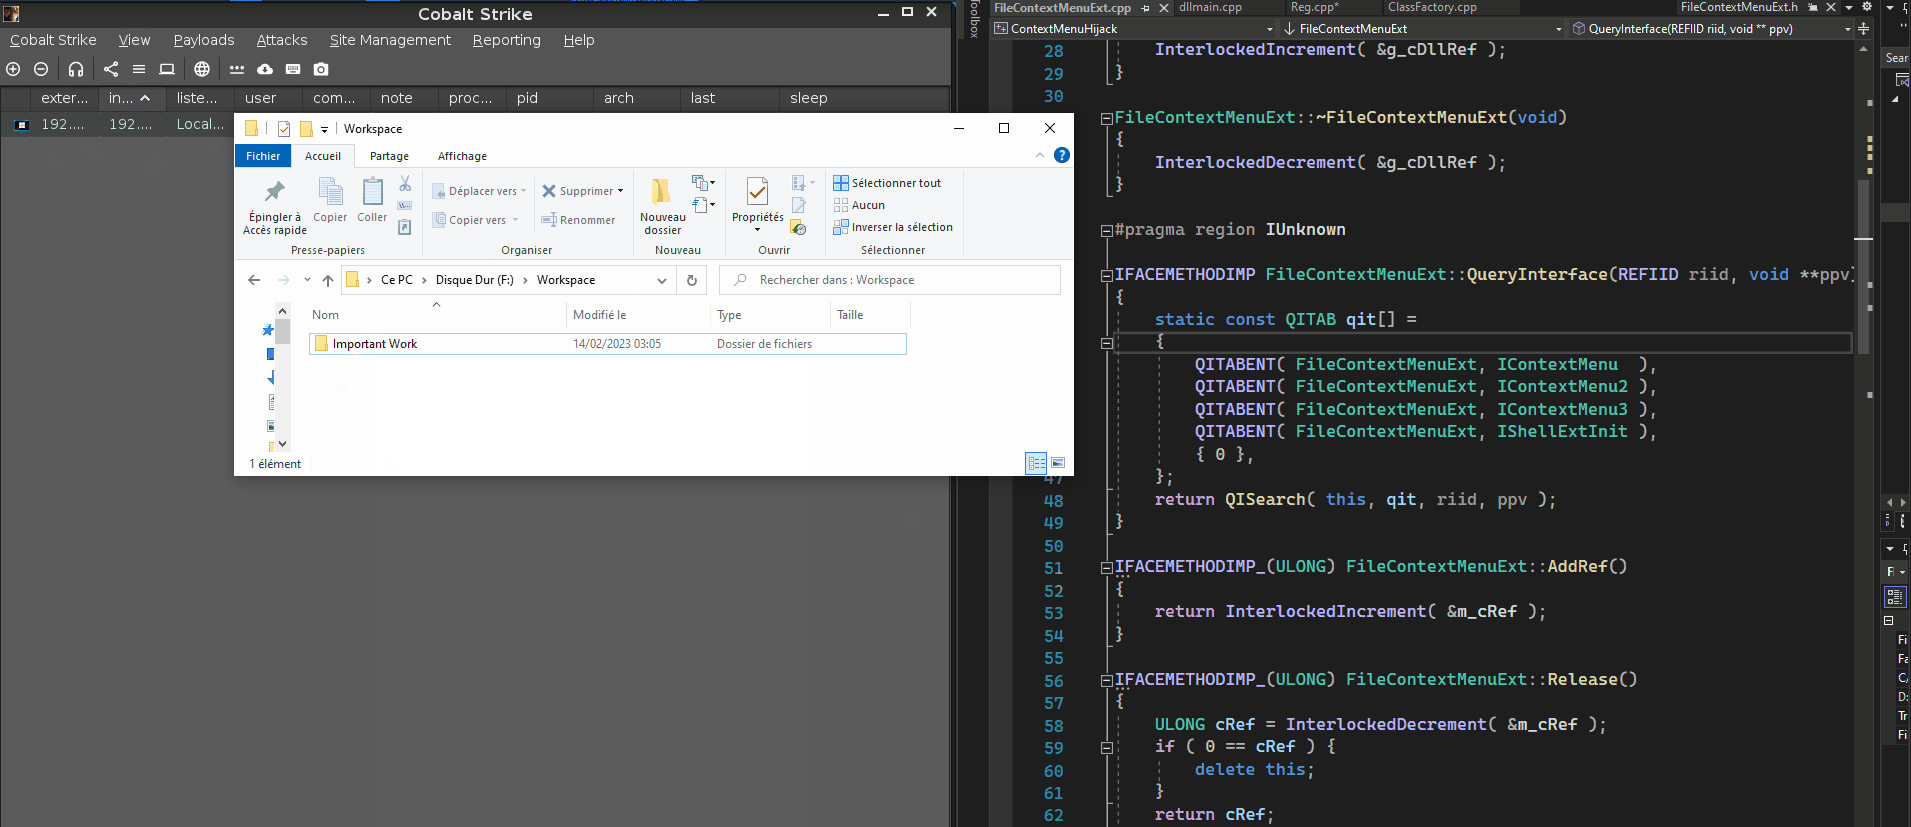 ristbs/contextmenuhijack
Execute a payload at each right click on a file/folder in the explorer menu for persistence
 ustayready/casperstager
PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
 je5442804/wptaskscheduler_cve-2024-49039
WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
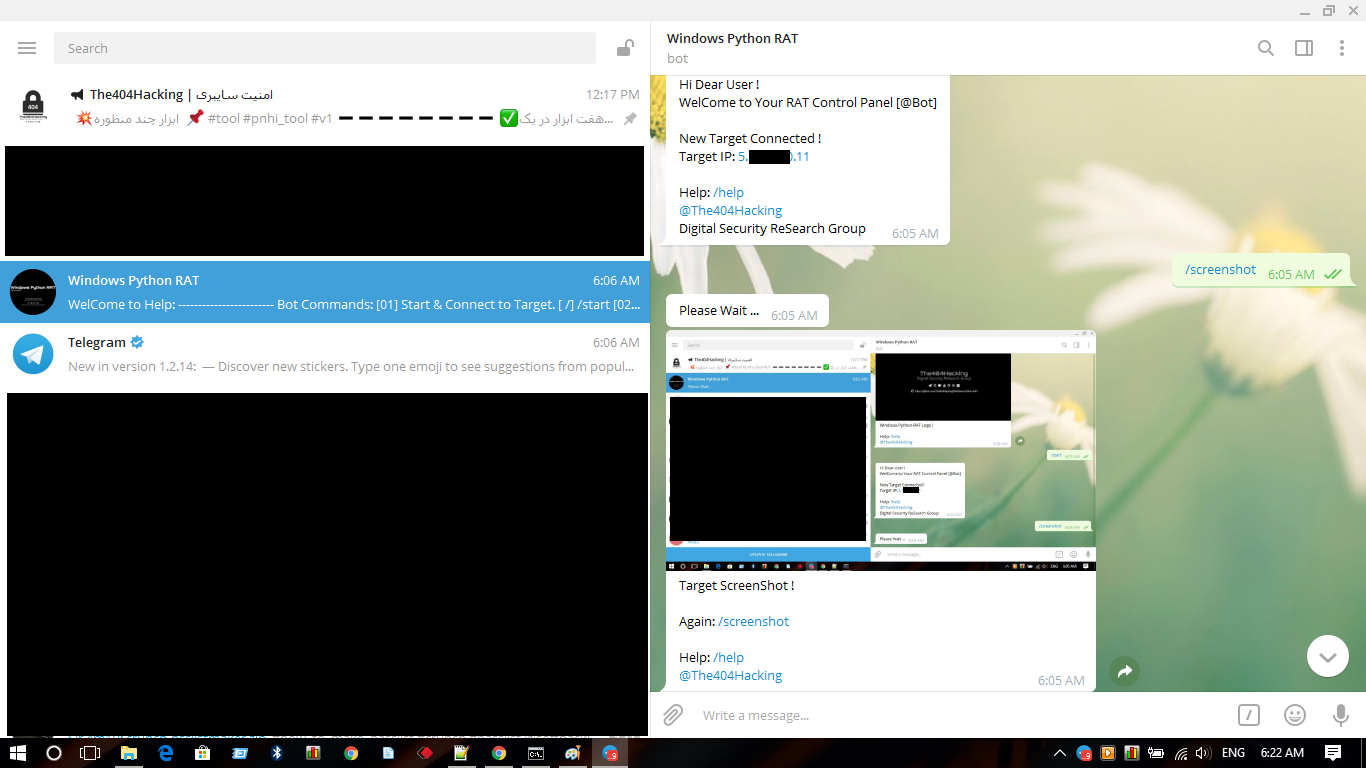 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.