
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
109 results
Powershell-RAT preview

Powershell-RAT

GitHubviralmaniar/powershell-rat

Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…

data-exfiltrationeducationpayload-generation+4
1.2k
7 years ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…

defensive-toolsmalware-analysismemory-forensics+3
22 years ago
3snake preview

3snake

GitHubblendin/3snake

Tool for extracting information from newly spawned processes
data-exfiltrationmemory-forensicspassword-attacks+4
7891 year ago
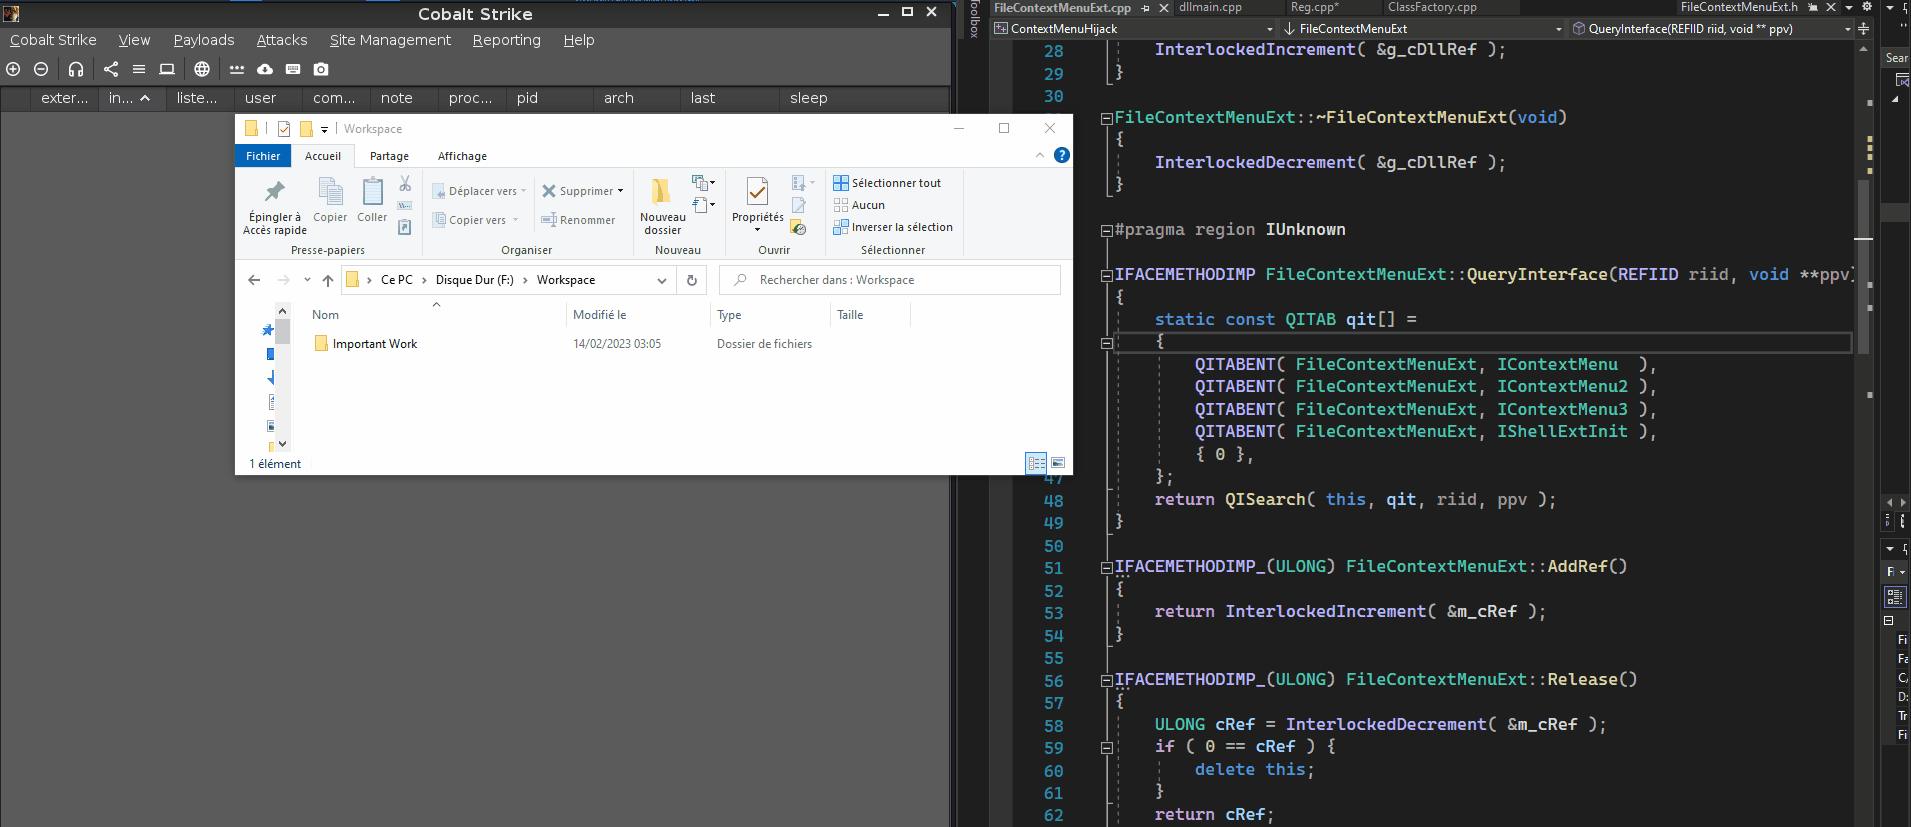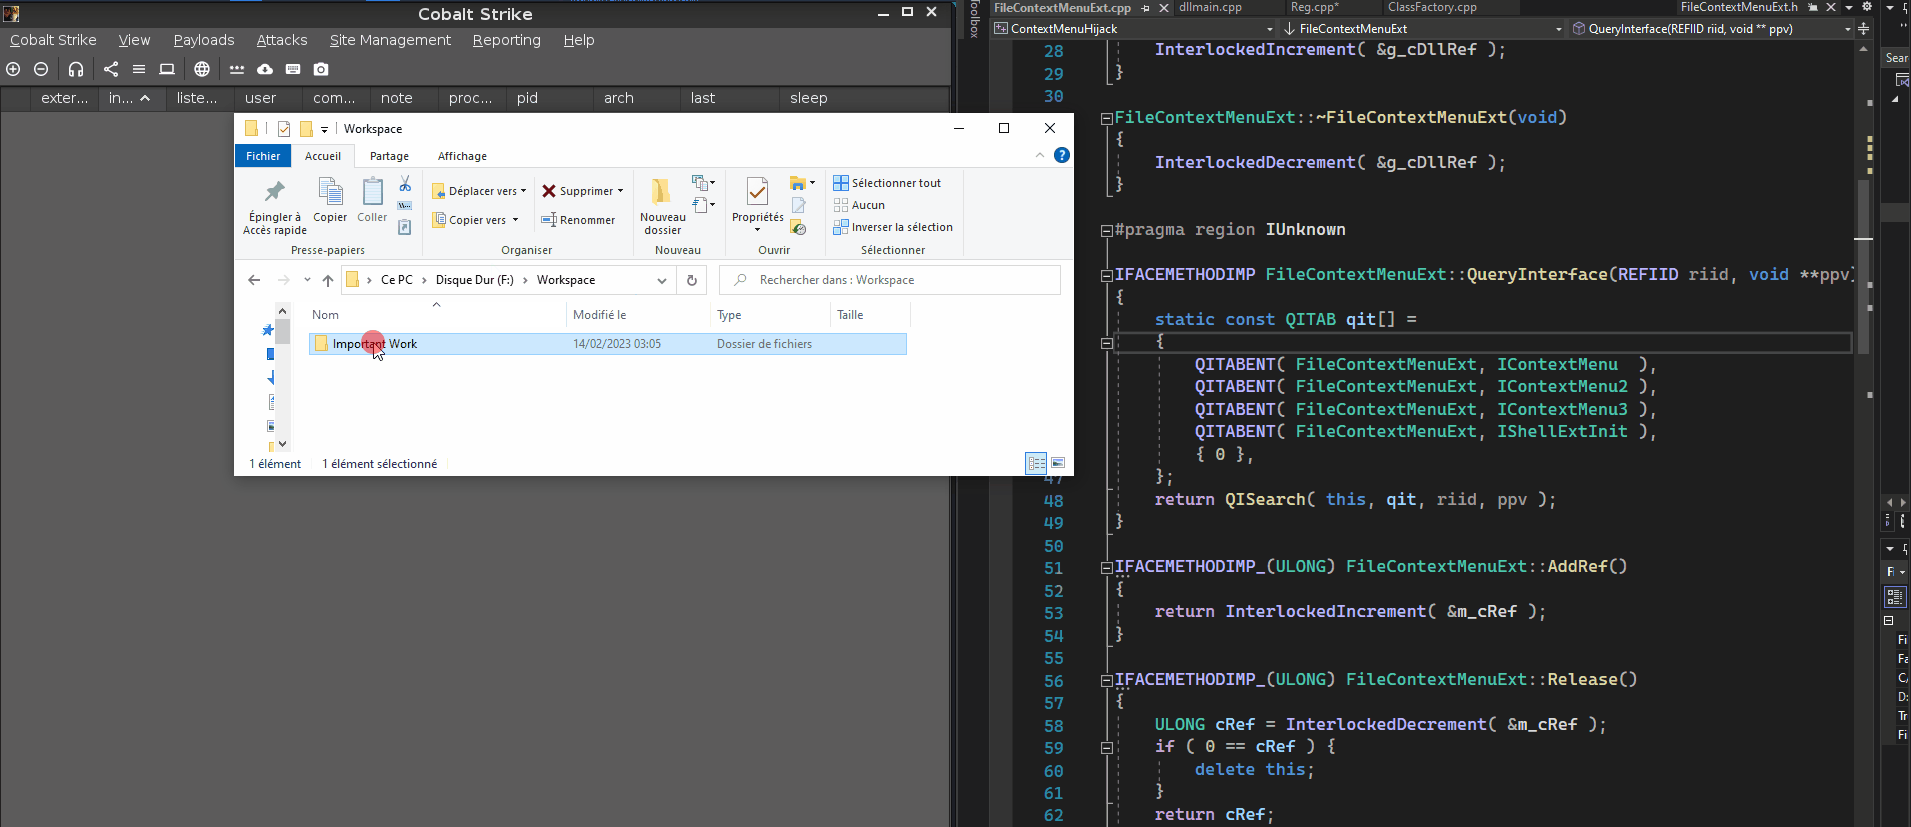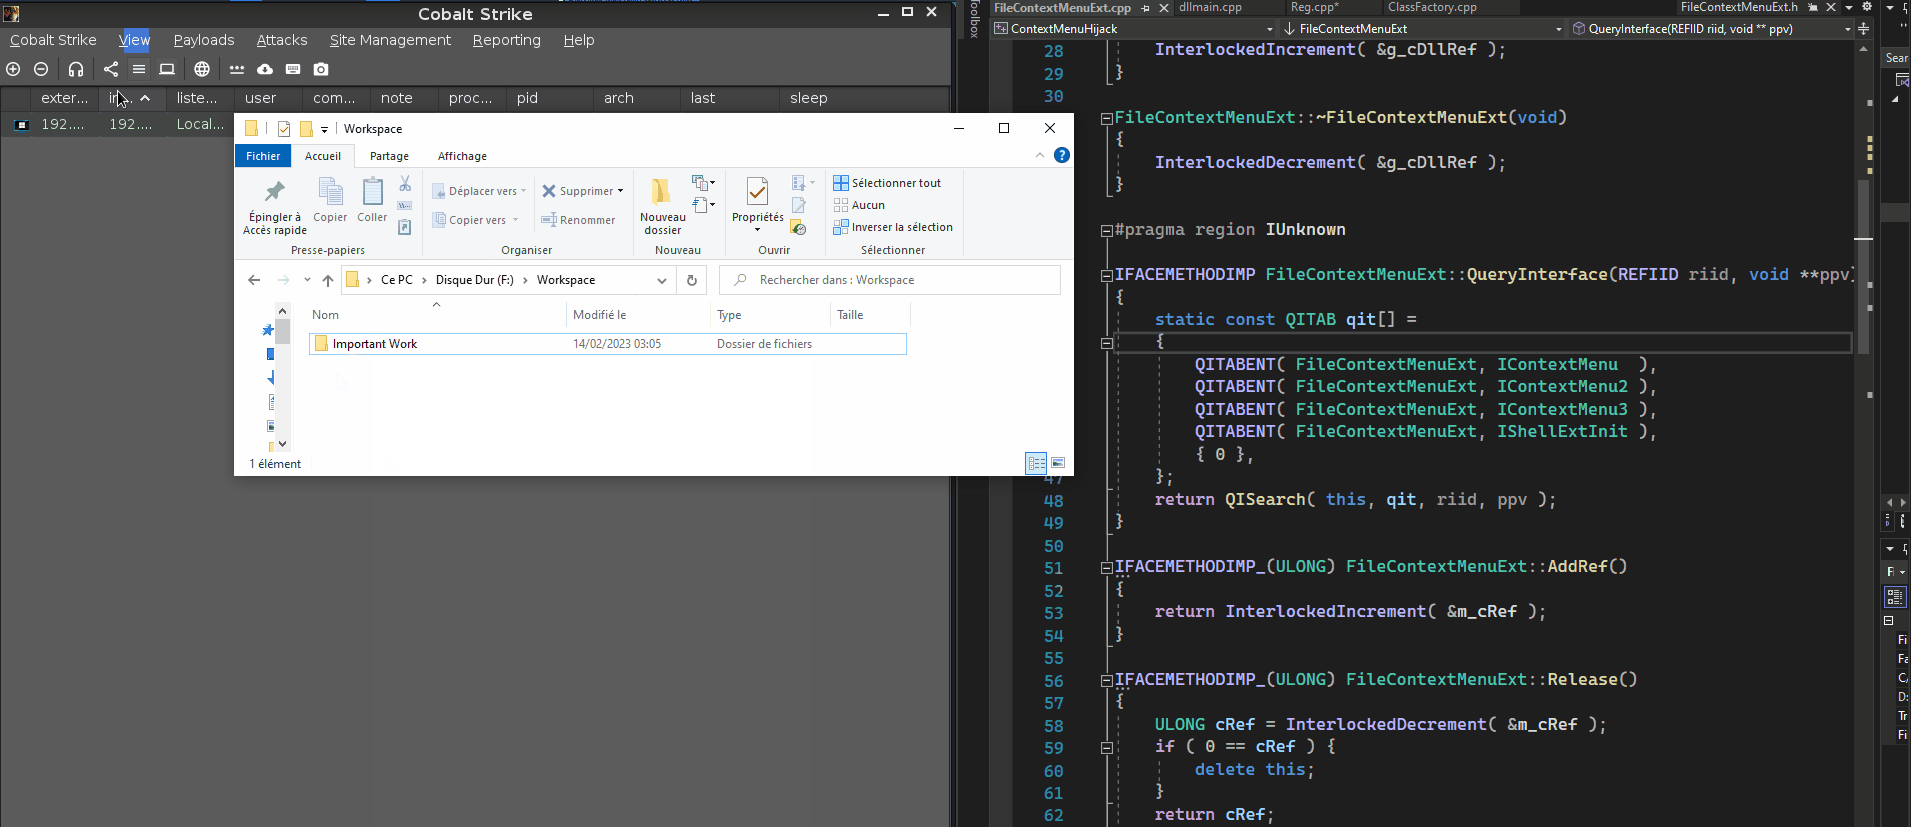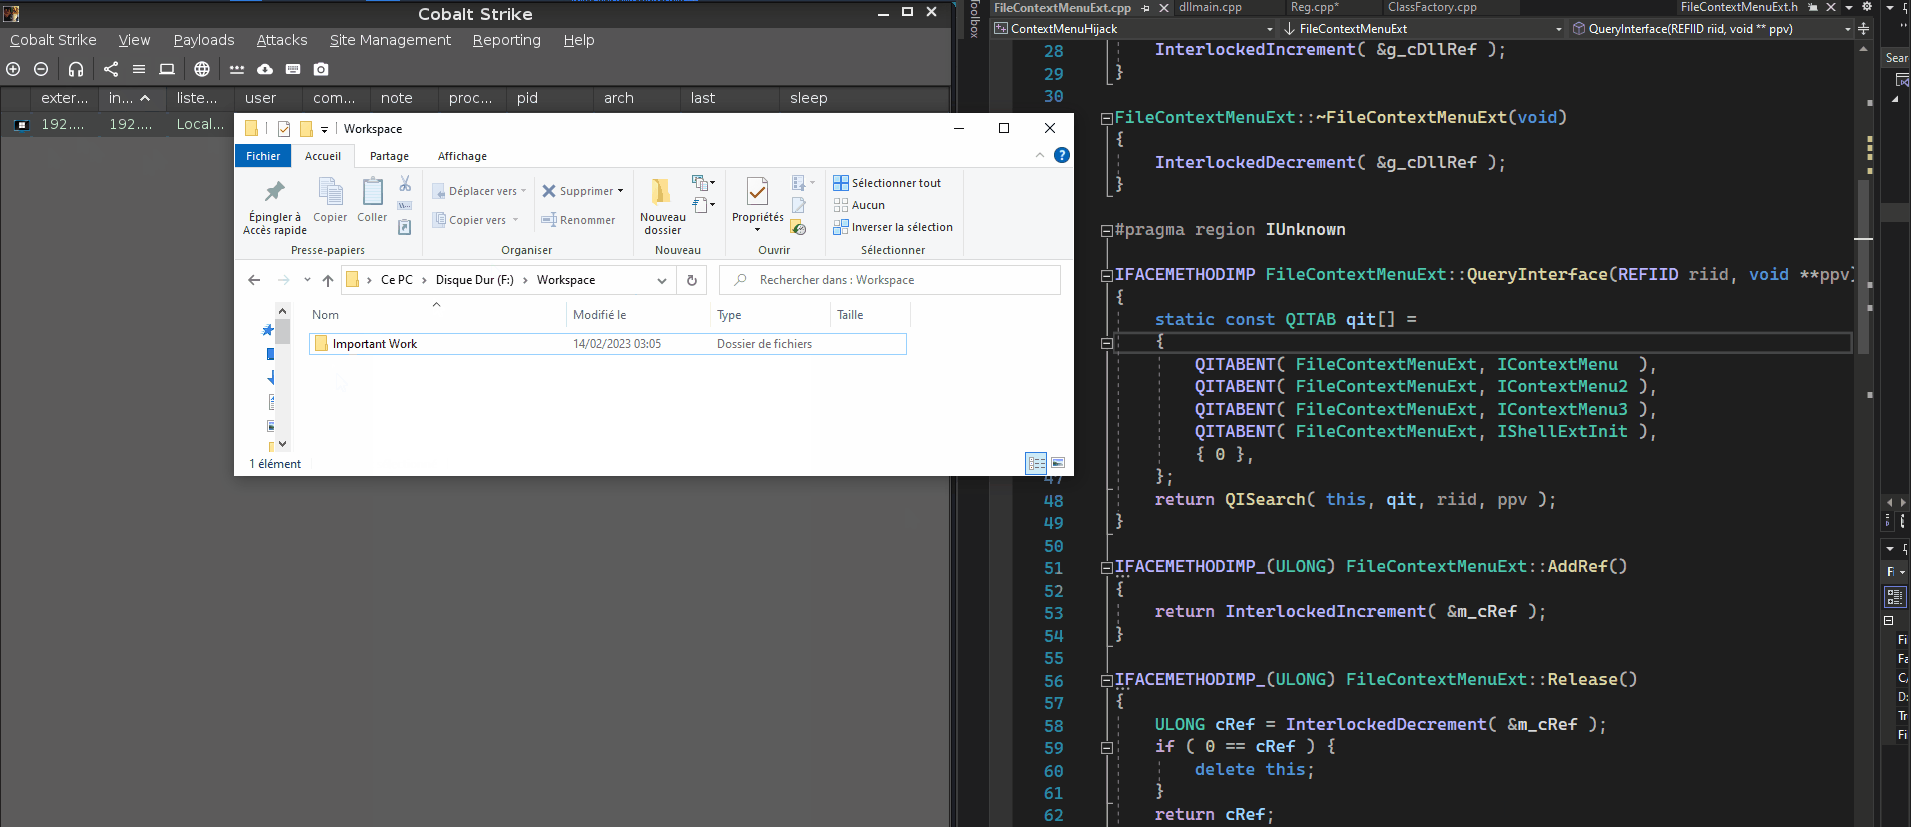
ContextMenuHijack preview

ContextMenuHijack

GitHubristbs/contextmenuhijack

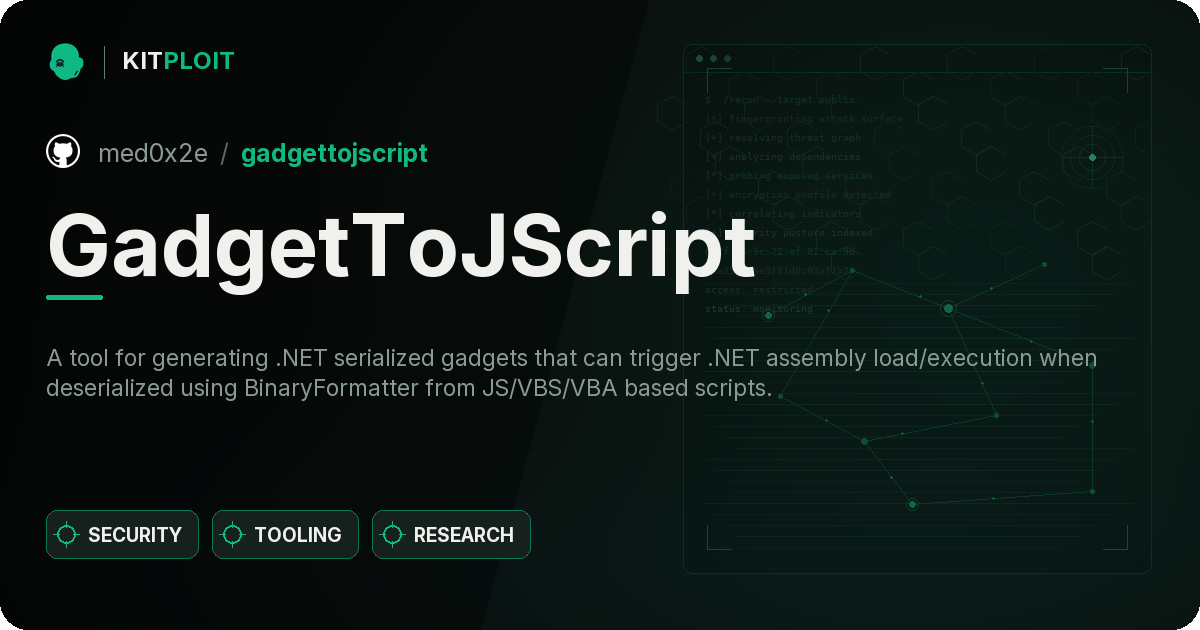
Execute a payload at each right click on a file/folder in the explorer menu for persistence
payload-developmentpersistence-mechanismspost-exploitation+1
1723 years ago
GadgetToJScript preview

GadgetToJScript

GitHubmed0x2e/gadgettojscript

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
adversarial-attackexploitationlateral-movement+5
1.1k5 years ago
IIS-Raid preview

IIS-Raid

GitHub0x09al/iis-raid

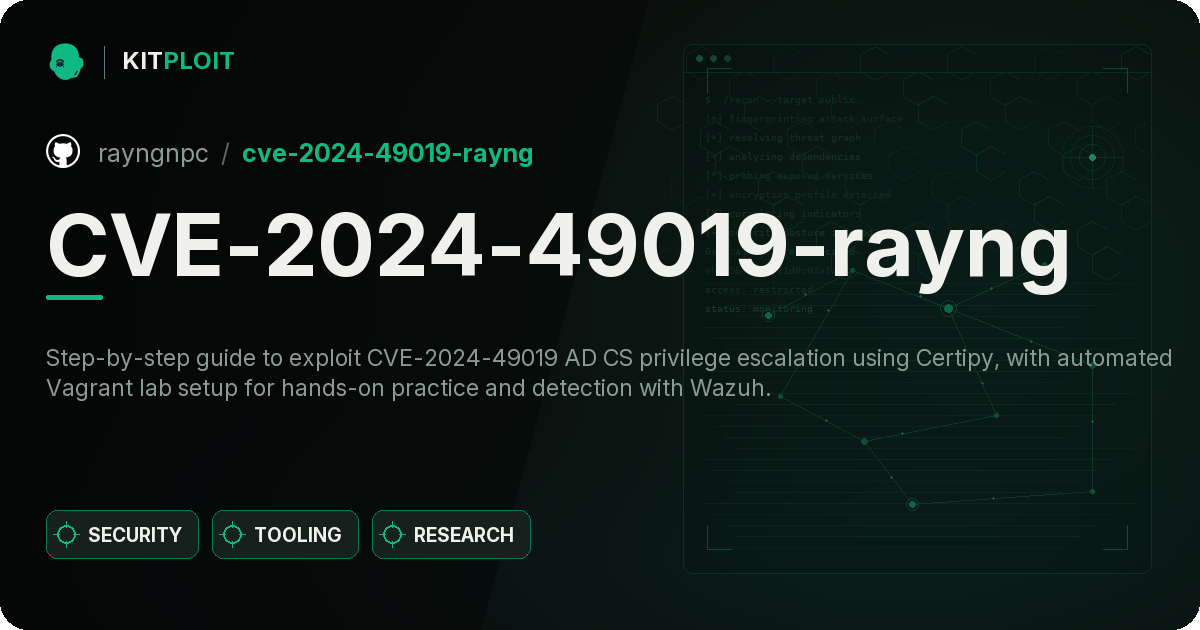
A native backdoor module for Microsoft IIS (Internet Information Services)
command-and-controlpassword-crackingpersistence-mechanisms+1
5516 years ago
CVE-2024-49019-rayng preview

CVE-2024-49019-rayng

GitHubrayngnpc/cve-2024-49019-rayng

Exploitation for CVE-2024-49019
educationexploitationlabs-practice+6
31 year ago
SharpADWS preview

SharpADWS

GitHubwh0amitz/sharpadws

Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
authenticationexploitationlateral-movement+6
6072 years ago
azazel preview

azazel

GitHubchokepoint/azazel

Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…

educationpersistence-mechanismspost-exploitation+2
8116 years ago
notRDP preview

notRDP

GitHubdagowda/notrdp

Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
command-and-controldata-exfiltrationimpersonation-tools+6
25723 days ago
postEX preview

postEX

GitHubniker-lixy/postex

Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…

information-gatheringpenetration-testingpersistence-mechanisms+4
13 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.

command-and-controldefensive-toolsids-ips-evasion+6
2.2k3 months ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.

defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
SharpGPOAbuse preview

SharpGPOAbuse

GitHubreverseclabs/sharpgpoabuse

SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
exploitationlateral-movementpenetration-testing+4
1.4k5 years ago
EDR-Preloader preview

EDR-Preloader

GitHubmalwaretech/edr-preloader

An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
defensive-toolsids-ips-evasionpersistence-mechanisms+3
5572 years ago
GoAT preview

GoAT

GitHubpetercunha/goat

🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server

command-and-controlexploitationlateral-movement+7
2619 years ago
RATel preview

RATel

GitHubfrenchcisco/ratel

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…

command-and-controlencryption-decryption-toolspayload-generation+6
2765 years ago
Previous1234567Next