

SmmBackdoor
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
exploitationfirmware-analysishardware-hacking+4
635
cr4sh/smmbackdoorFirst open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 nccgroup/winpayloads
Undetectable Windows Payload Generation
 sweetsoftware/ares
Python botnet and backdoor
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
 enigma0x3/powershell-c2
PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.
 0xdak/cve-2026-52680_exploit
Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…
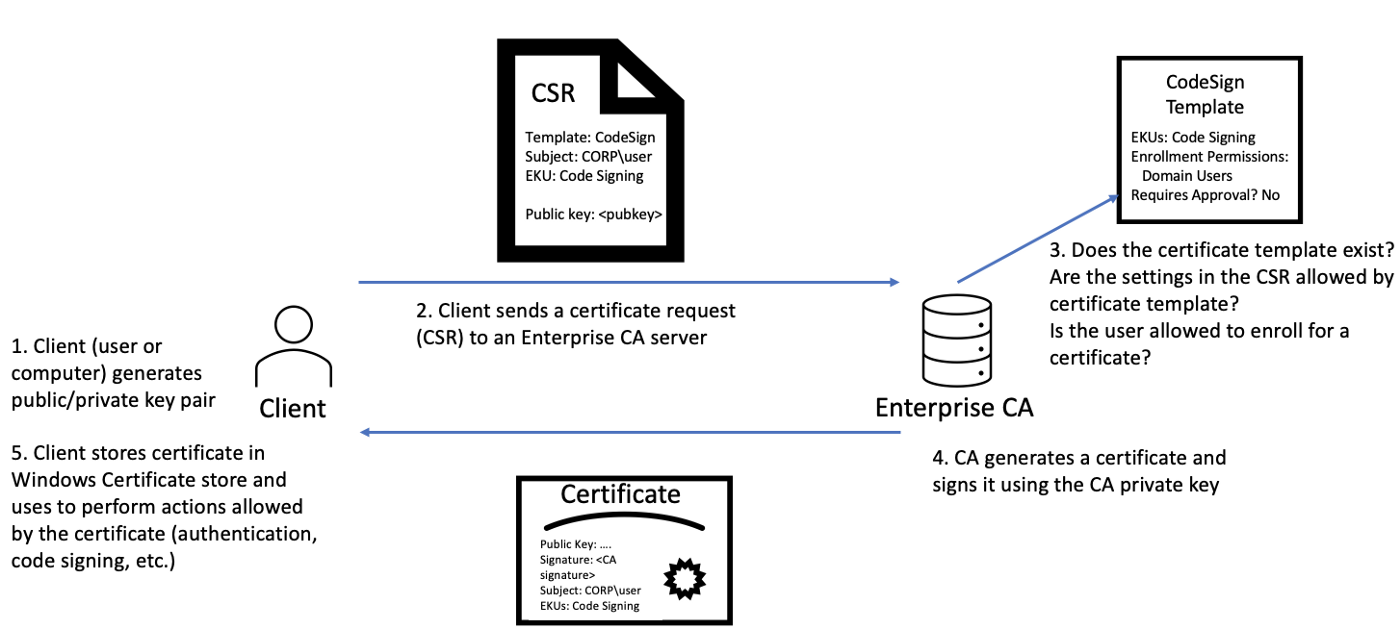 ghostpack/forgecert
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 knight0x07/winrar-cve-2025-8088-poc-rar
WinRAR 0day CVE-2025-8088 PoC RAR Archive
 gbrn1/pirate
Python Remote Access Tool
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
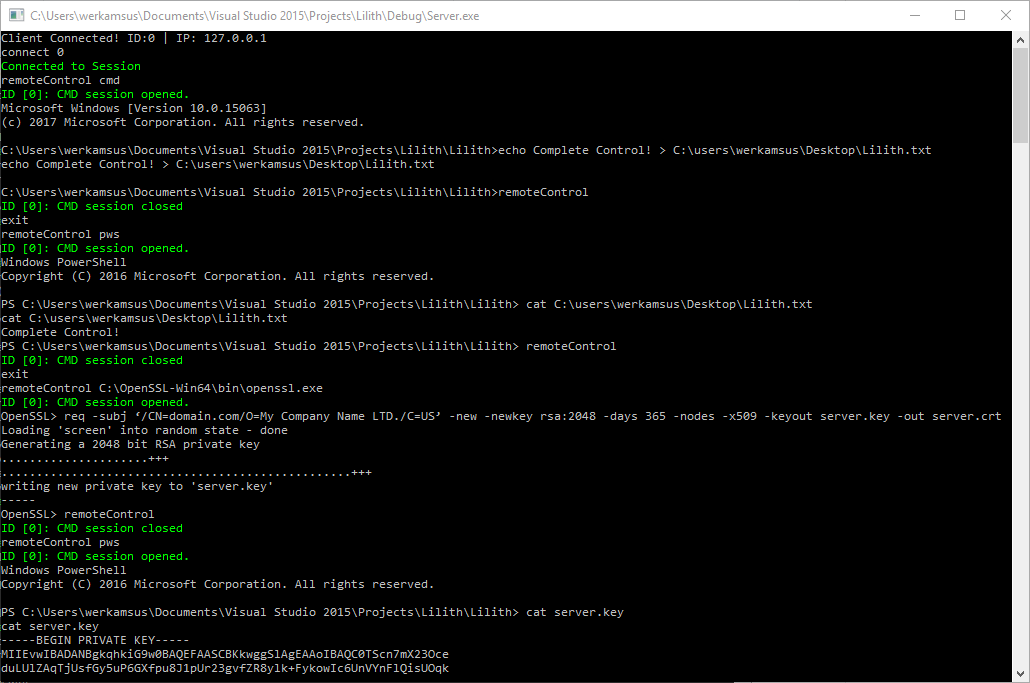 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 kkevsterrr/backdoorme
powerful auto-backdooring utility