
taowu-cobalt_strike
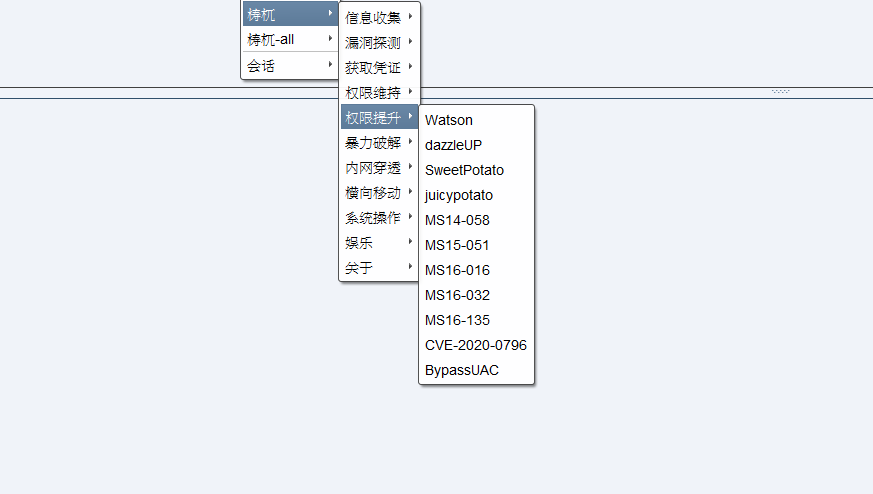
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…

Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…

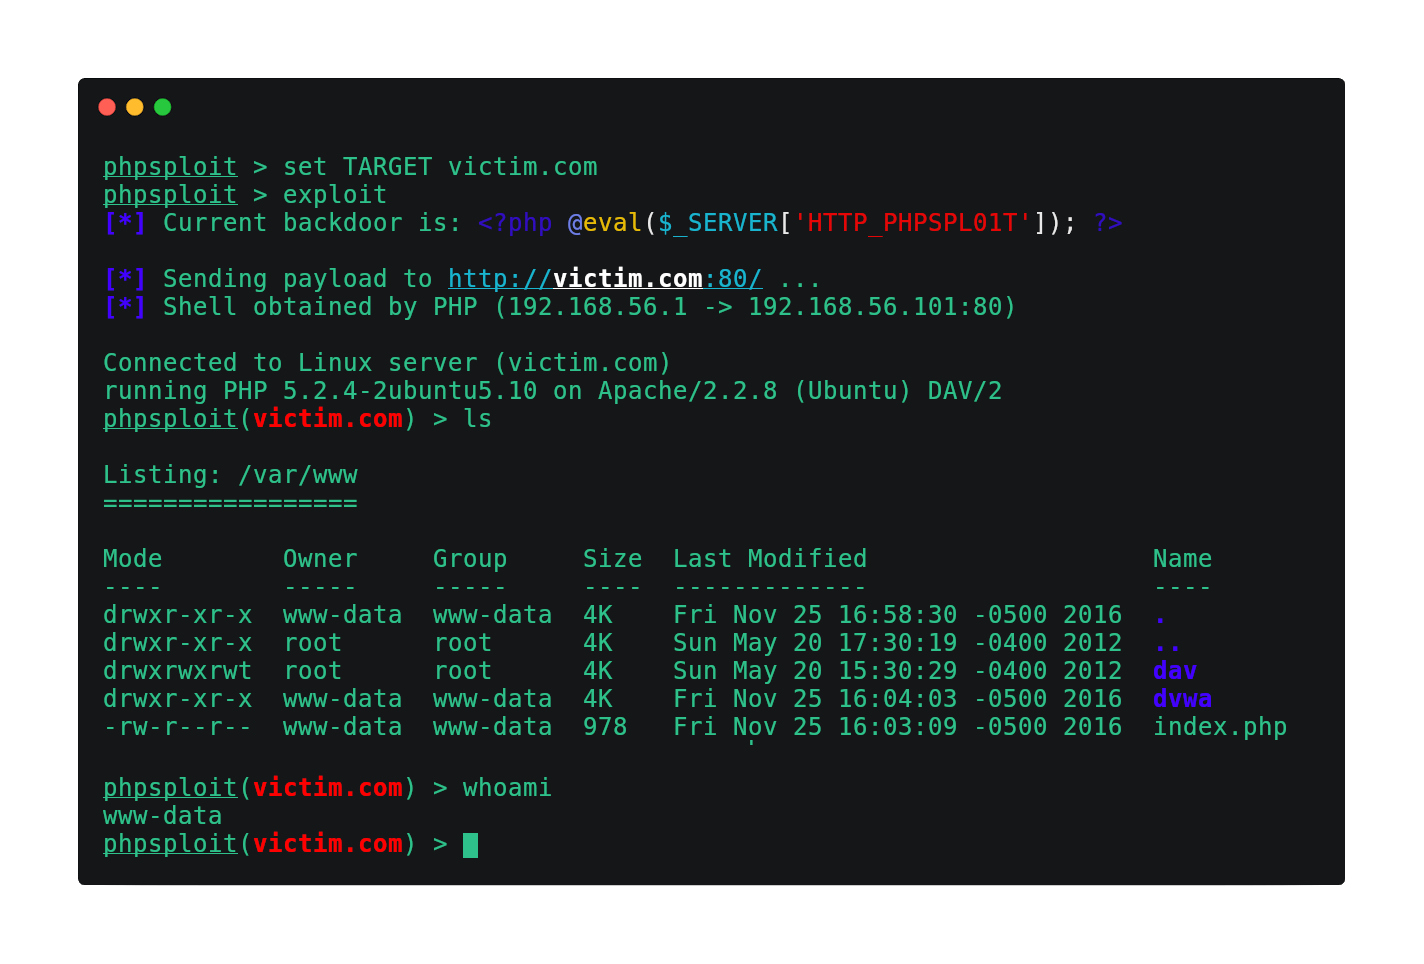
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

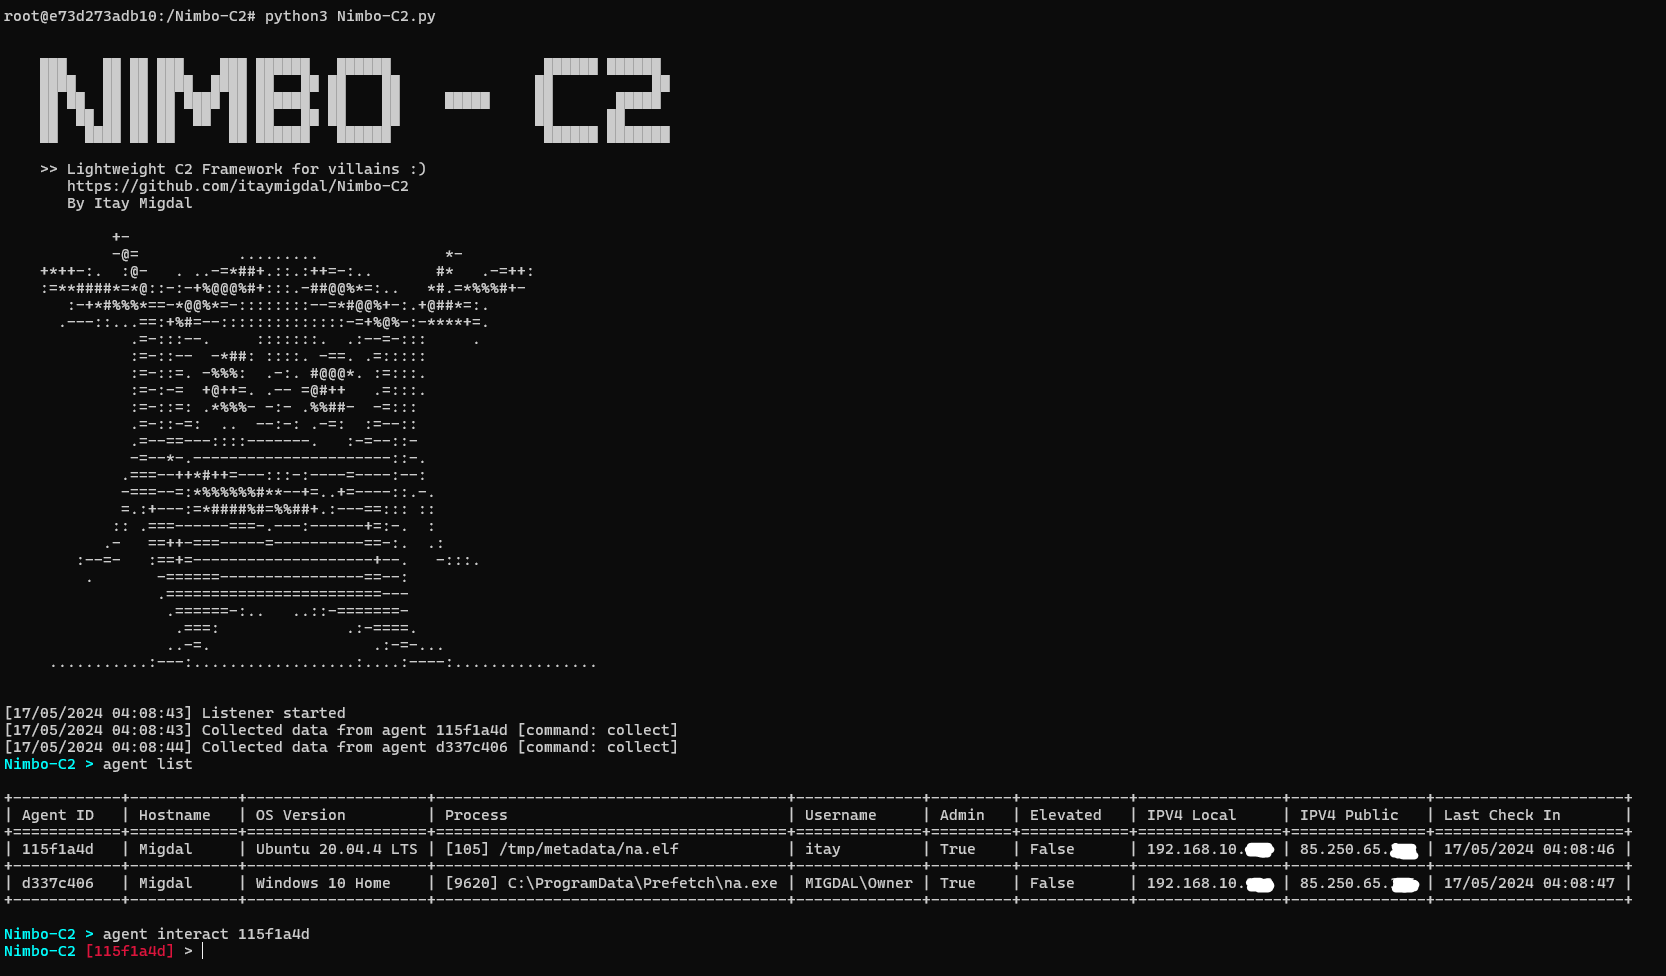
Nimbo-C2 is yet another (simple and lightweight) C2 framework

Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.


All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

A little tool to play with Windows security

Undetectable Windows Payload Generation

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

Crystal Palace Evasion kit for Sliver


Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…