APTs-Adversary-Simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

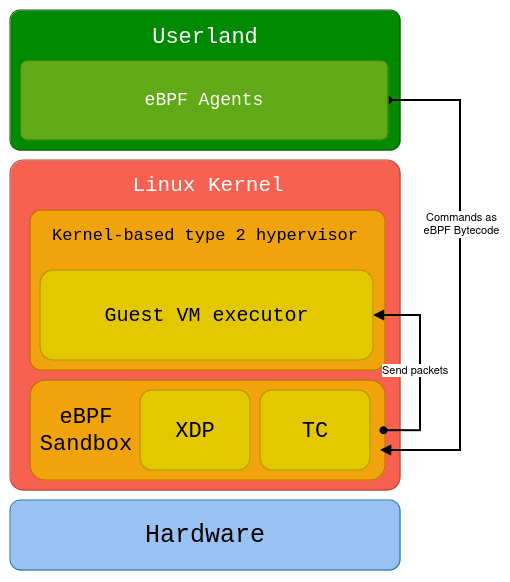
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

A native backdoor module for Microsoft IIS (Internet Information Services)

DLL Password Filter Implant with Exfiltration Capabilities

Python botnet and backdoor

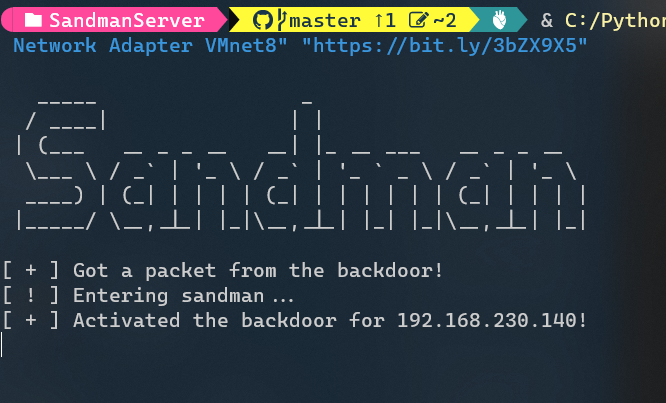
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…

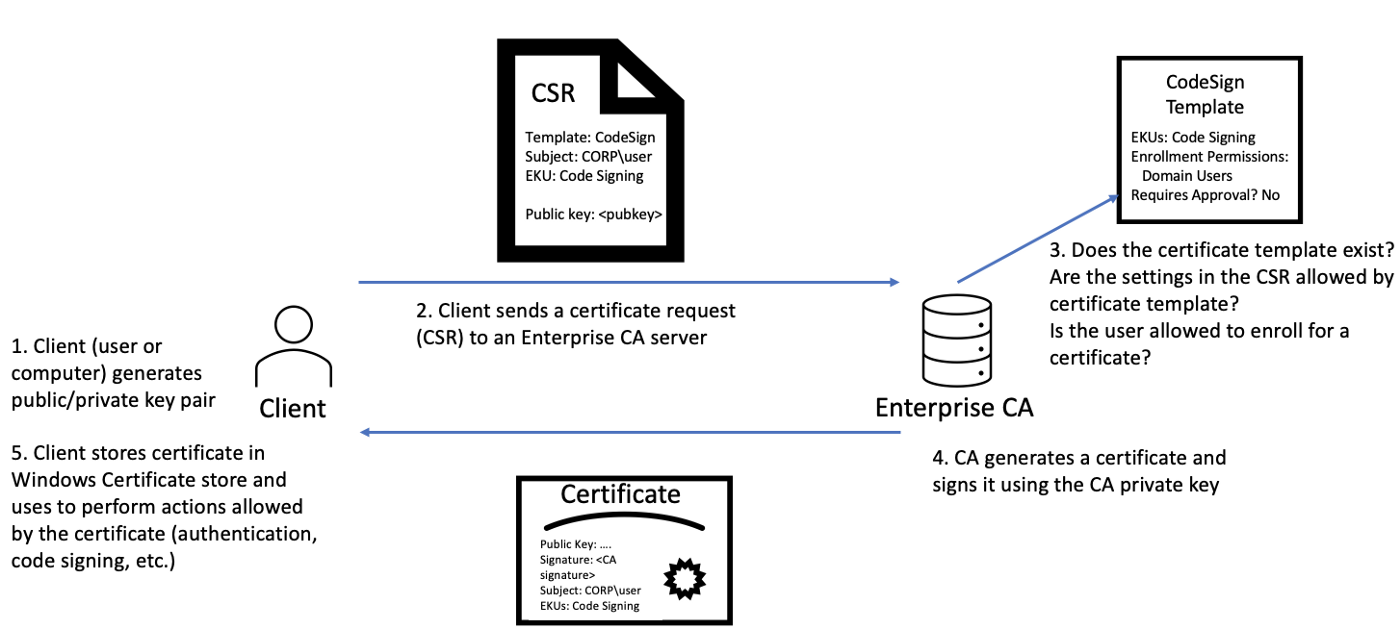
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…

powerful auto-backdooring utility

Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++

A tool to transform Chromium browsers into a C2 Implant

For when DLLMain is the only way

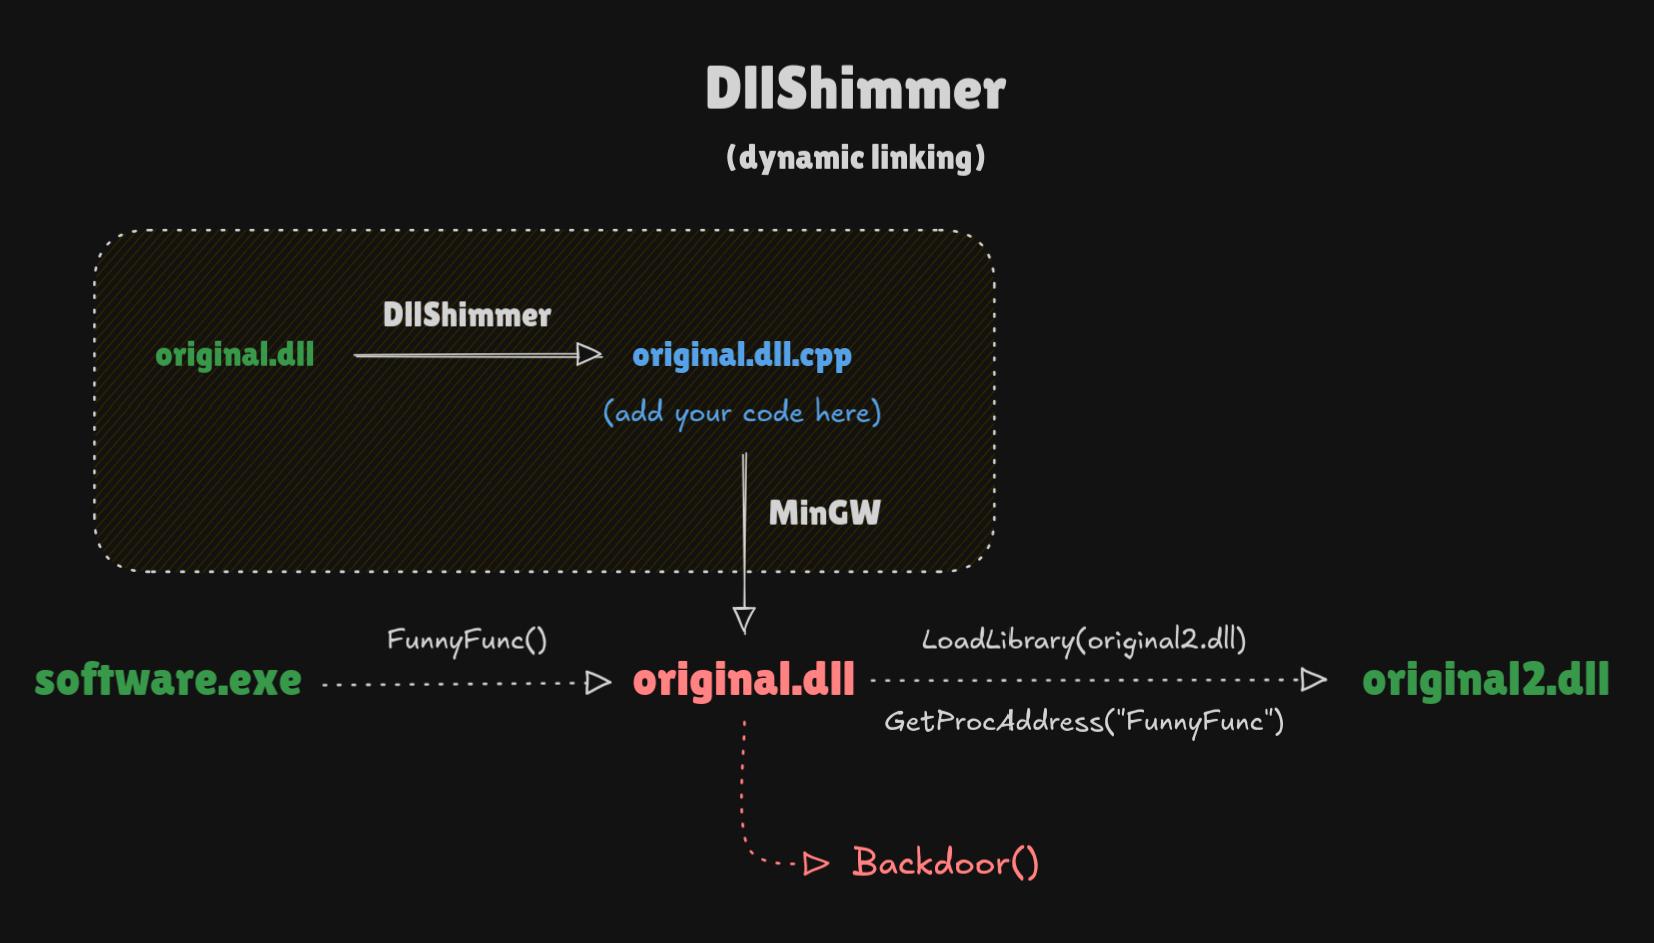
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

Tools for discovery and abuse of COM hijacks

macOS Initial Access Payload Generator

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)