

OffensiveDLR
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
code-analysiscommand-and-controldynamic-code-analysis+9
524
byt3bl33d3r/offensivedlrToolbox containing research notes & PoC code for weaponizing .NET's DLR
 0xdak/cve-2026-52680_exploit
Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 s3cur3th1ssh1t/offensivevba
This repo covers some code execution and AV Evasion methods for Macros in Office documents
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
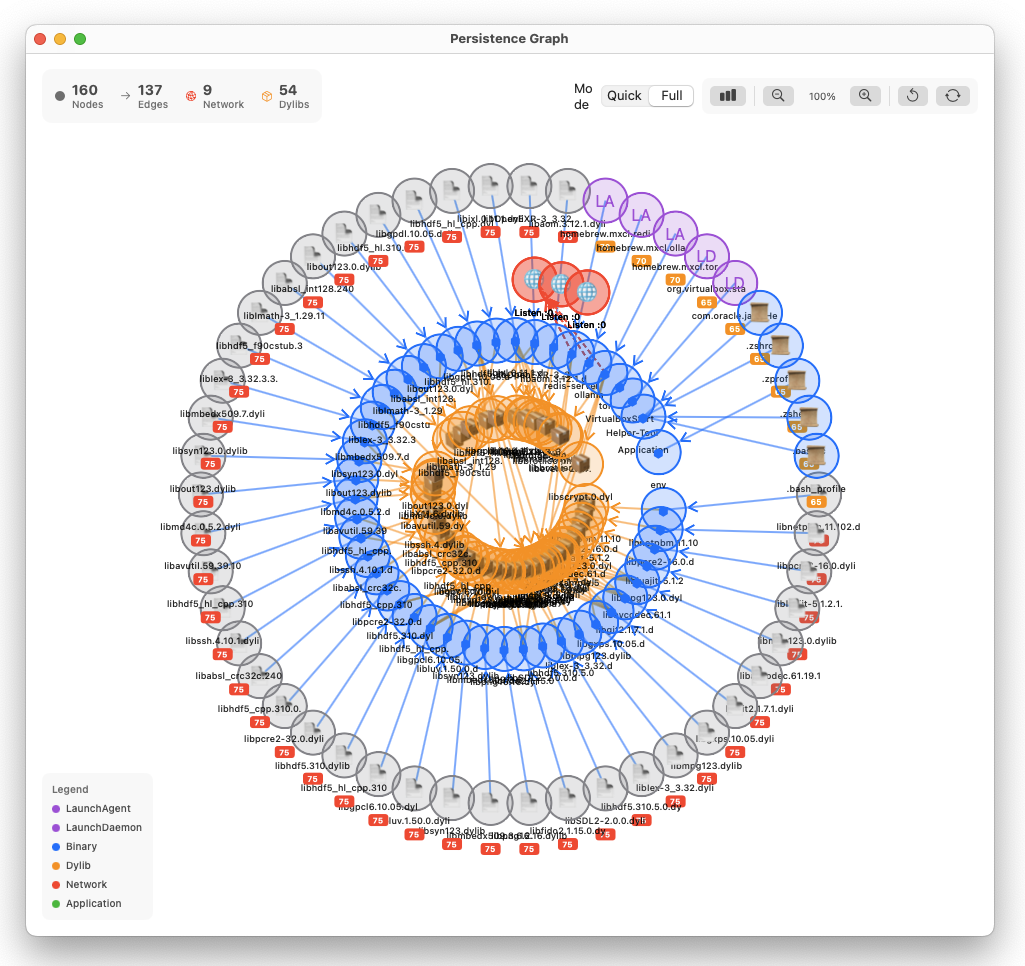 pinperepette/macpersistencechecker
macOS persistence mechanism scanner with code signature verification and timeline tracking.
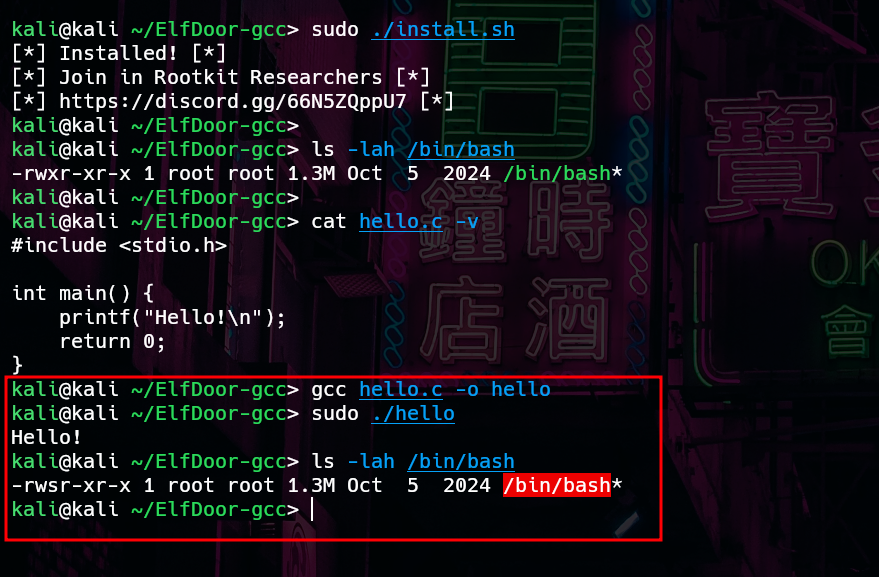 matheuzsecurity/elfdoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…
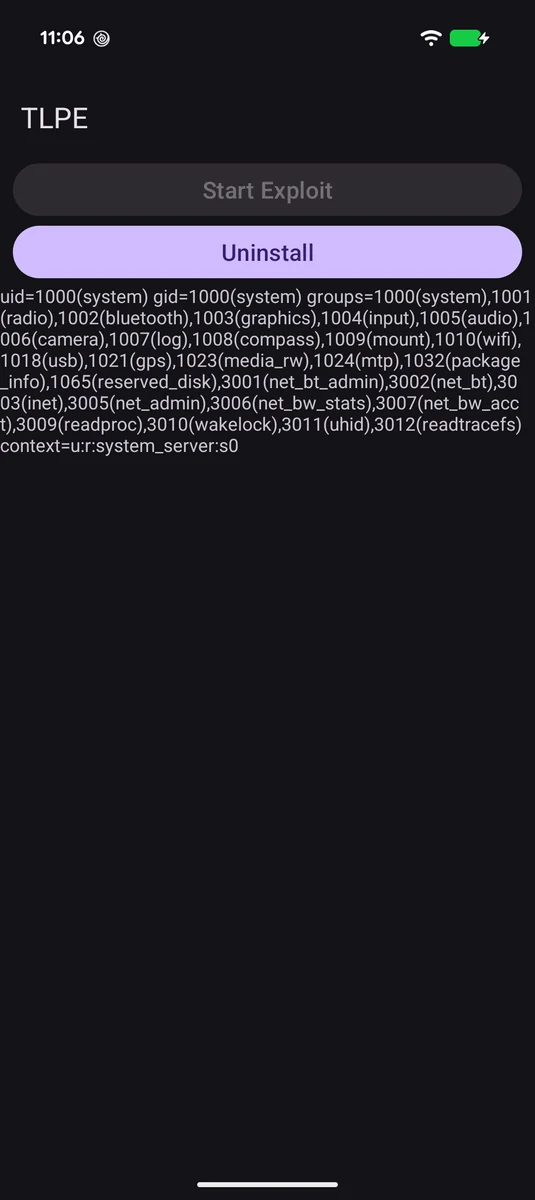 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
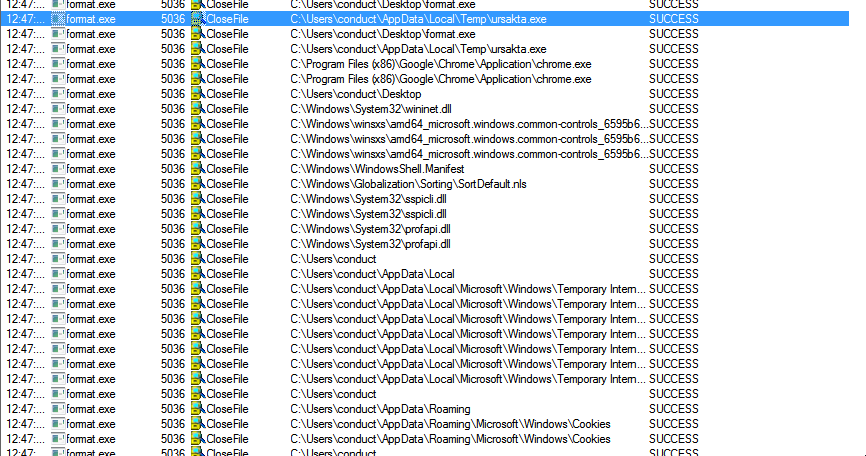 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 xforcered/scmkit
Source Code Management Attack Toolkit
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…