

Archived
Lime-RAT
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
command-and-controlcryptographydata-exfiltration+7
1.1k
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 cys3c/evilosx
A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.
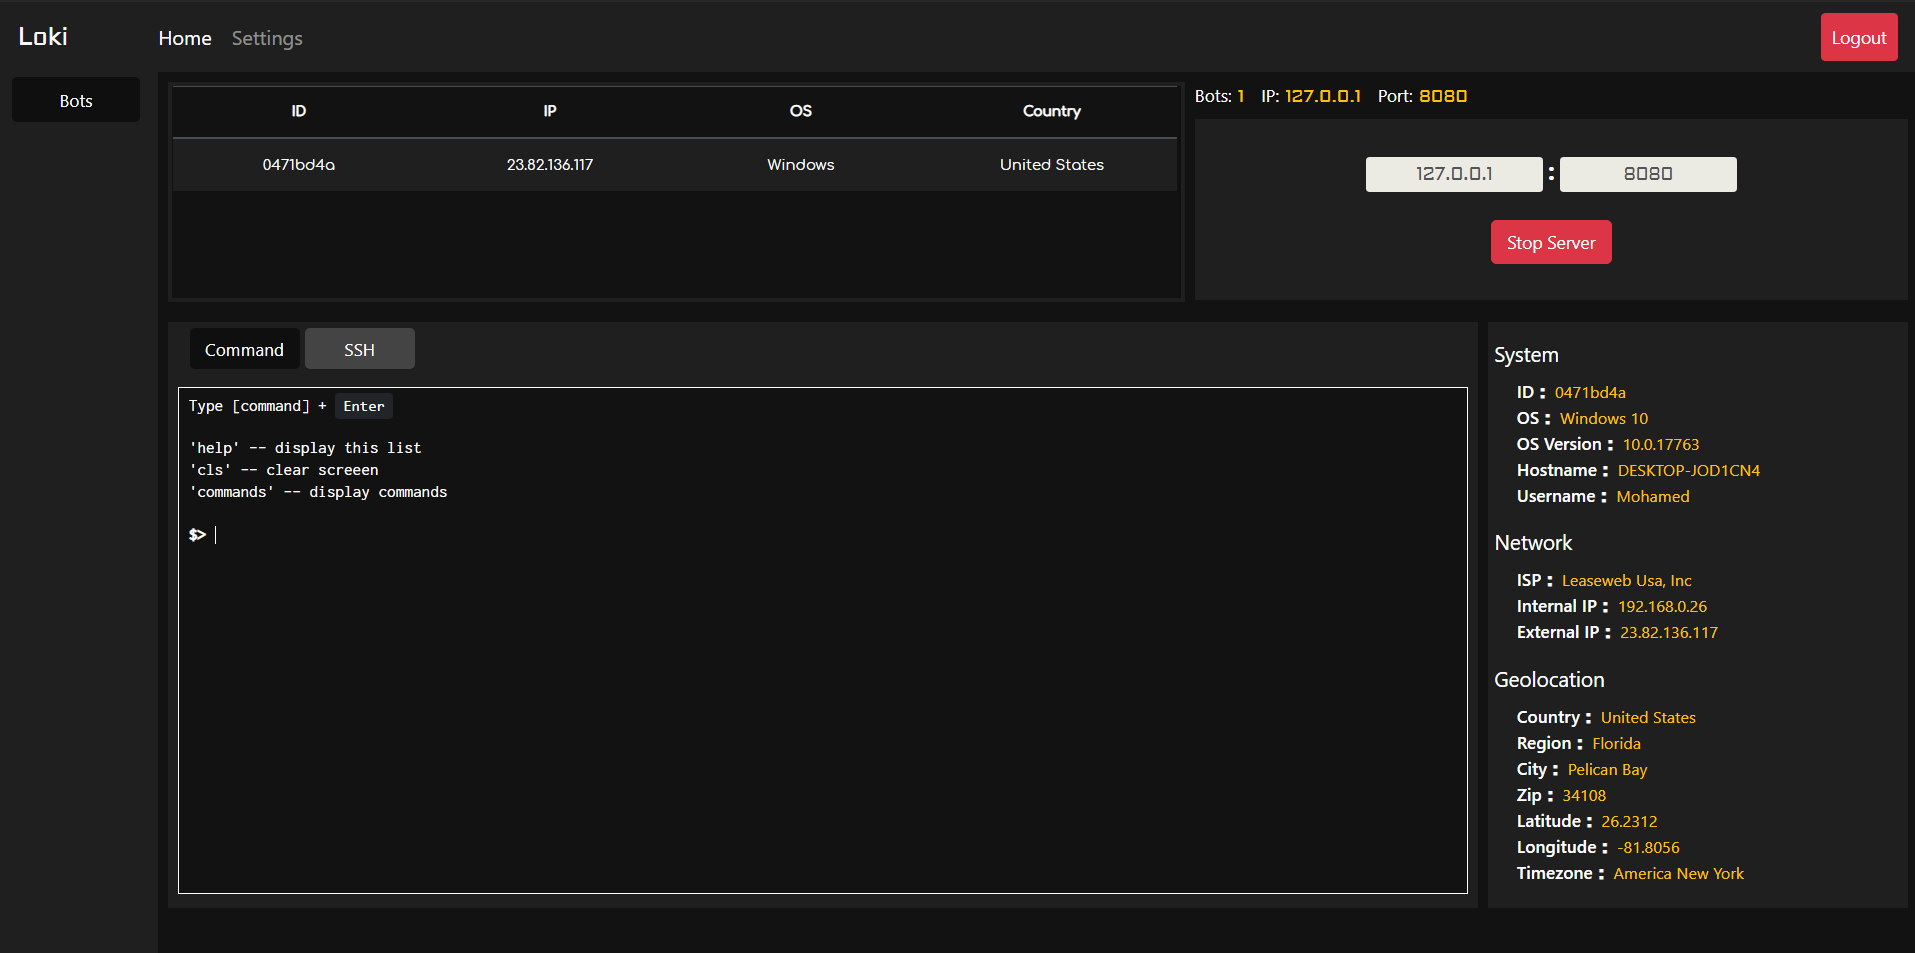
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
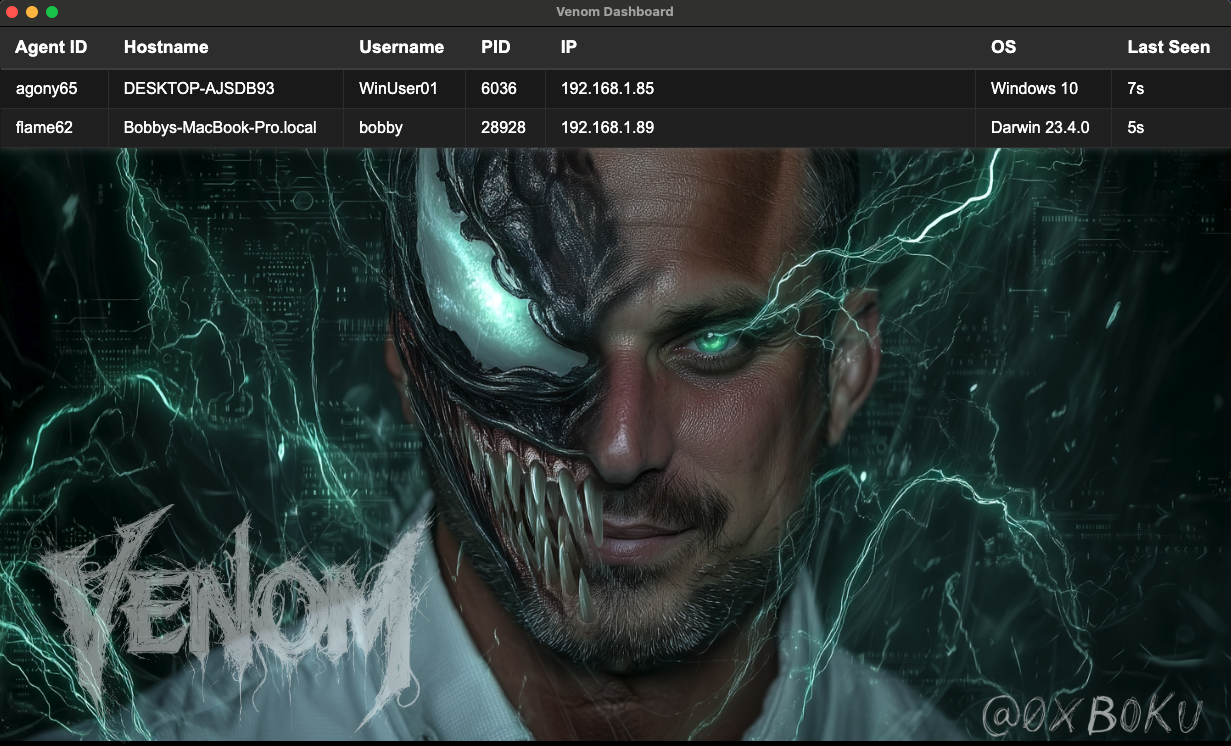 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
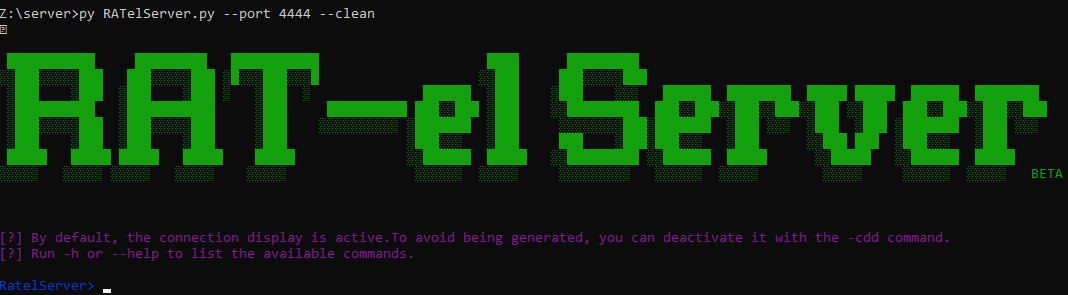 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 facebookarchive/weasel
DNS covert channel implant for Red Teams.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 cenobyte-vincit/encrypted-linux-kernel-modules
encrypted-linux-kernel-modules