
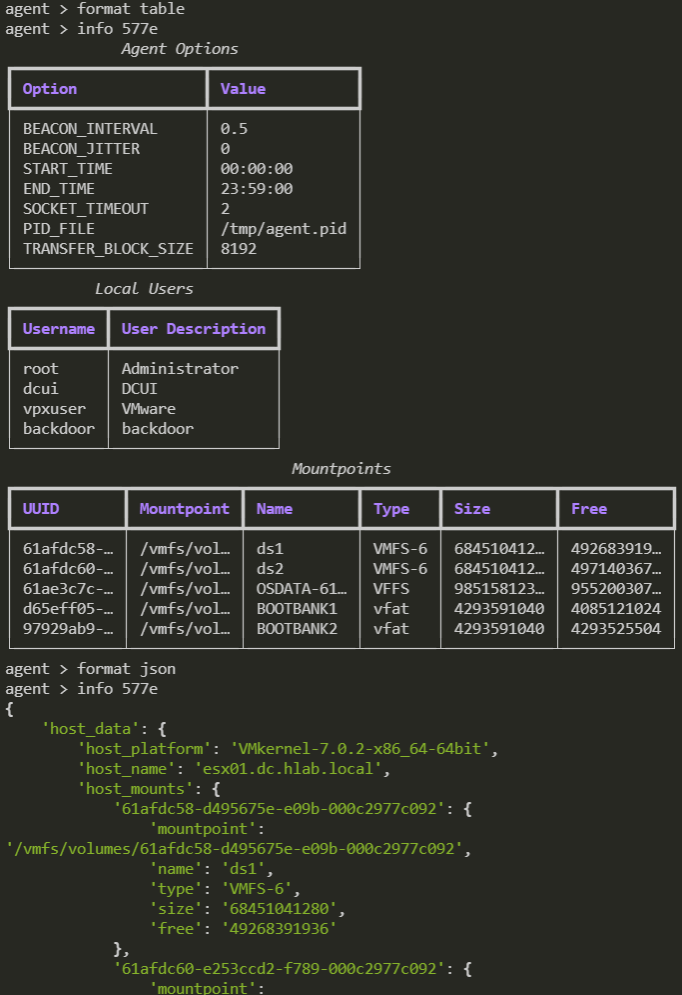
reave
 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
command-and-controldata-exfiltrationexploit-frameworks+8
psmths/reaveWIP Post-exploitation framework tailored for hypervisors.
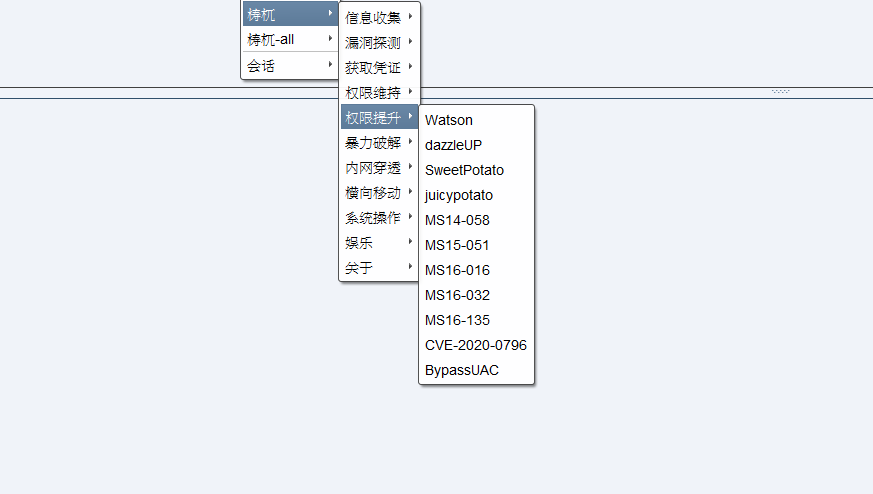 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
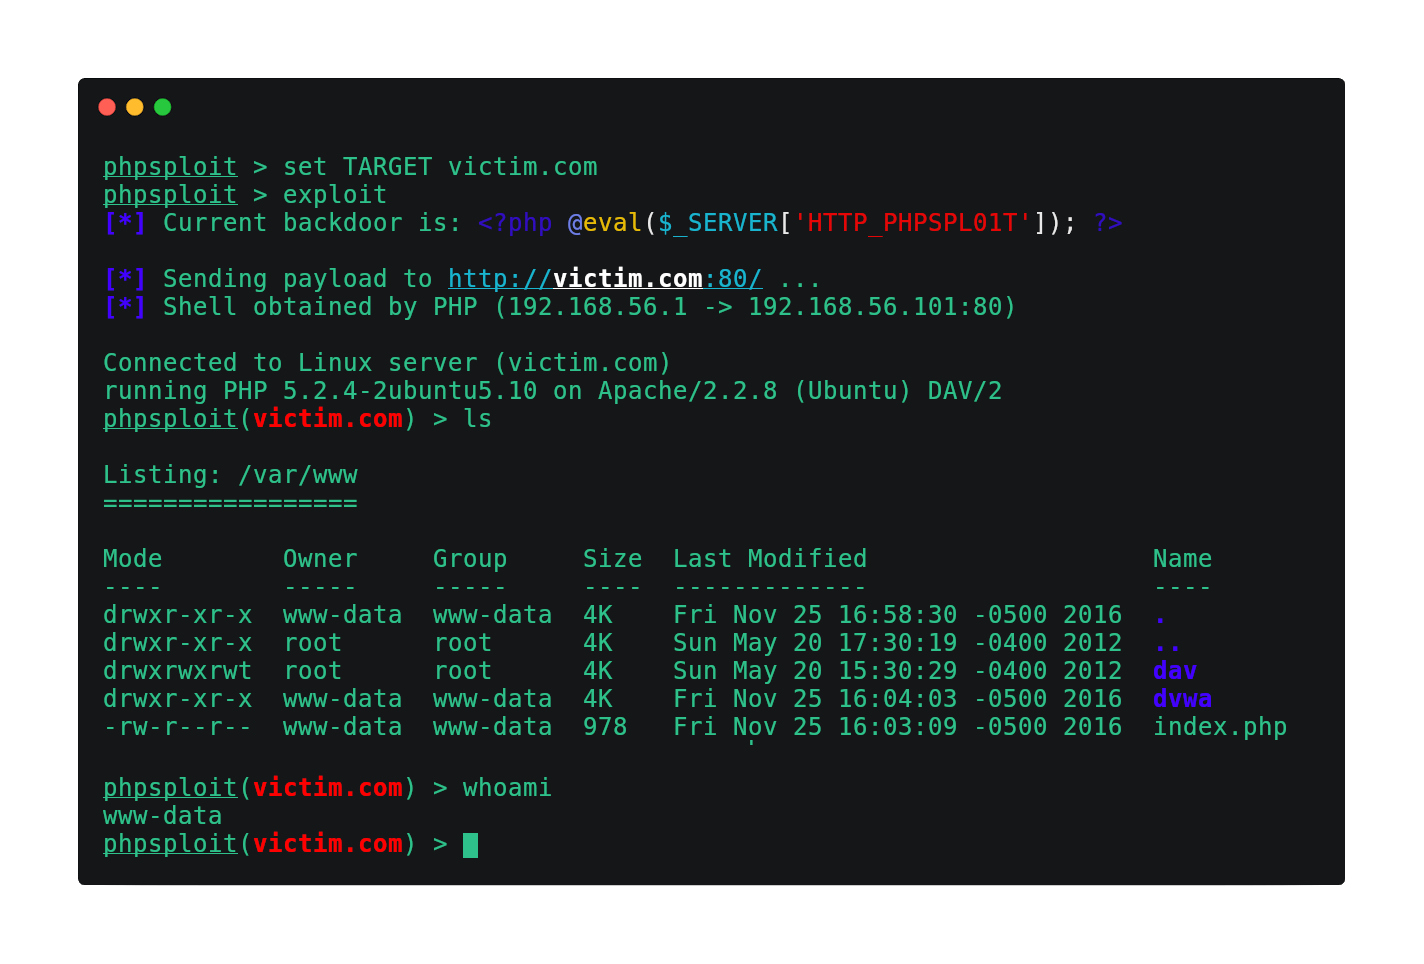 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
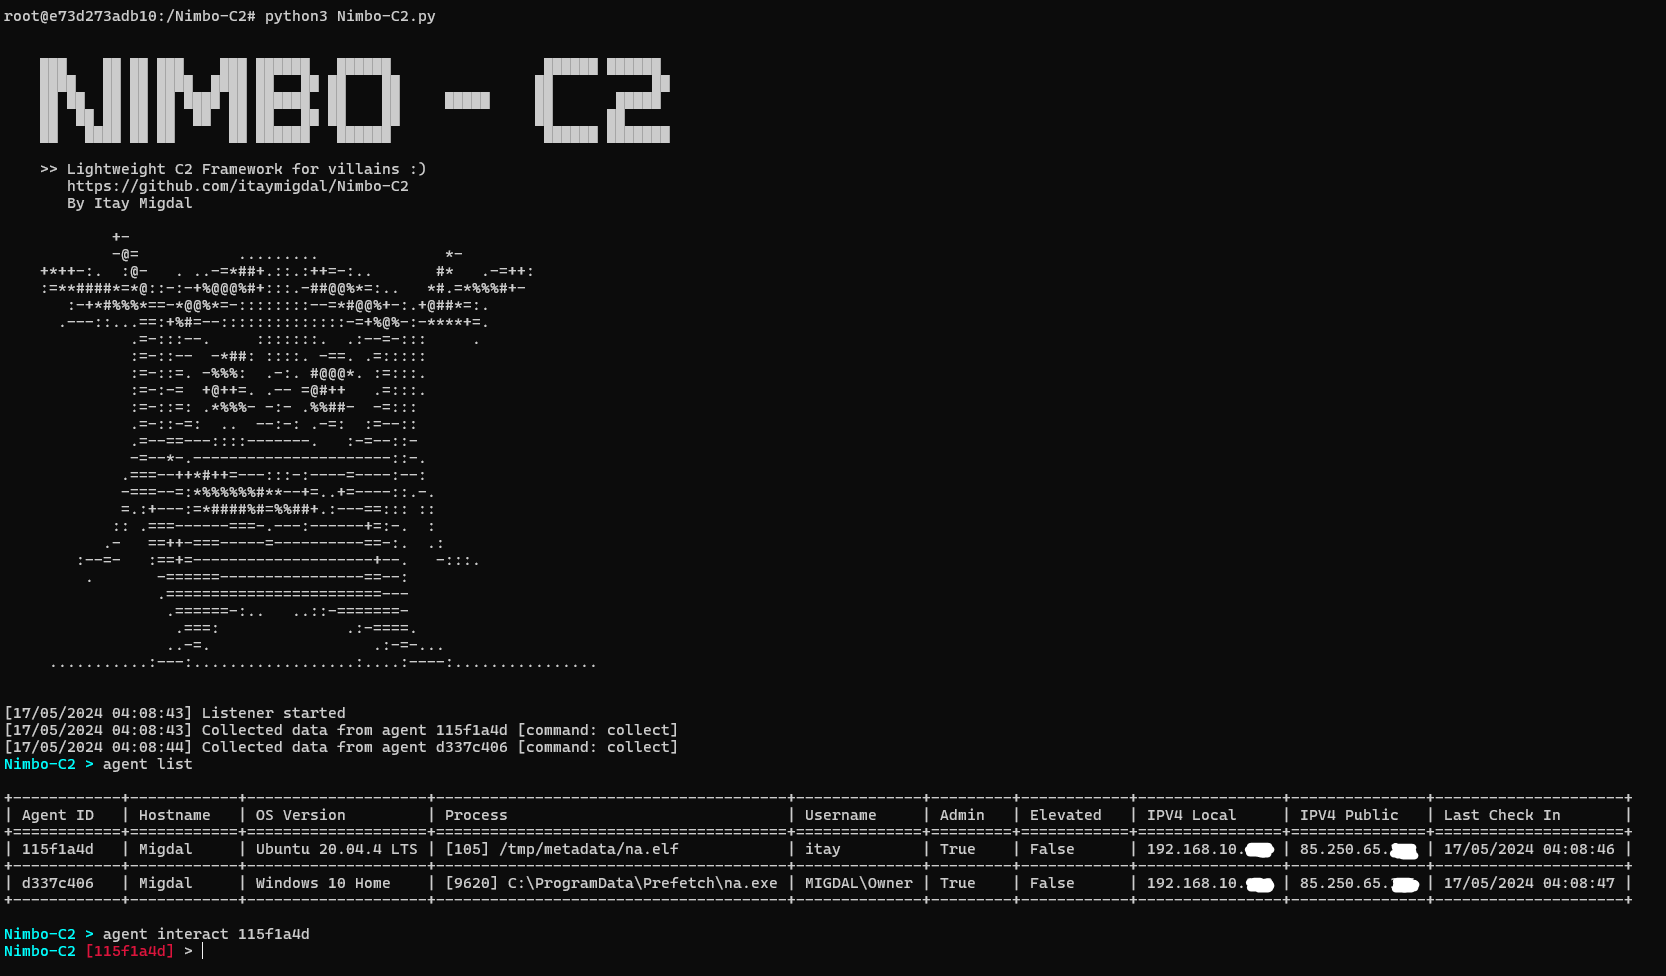 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.

 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
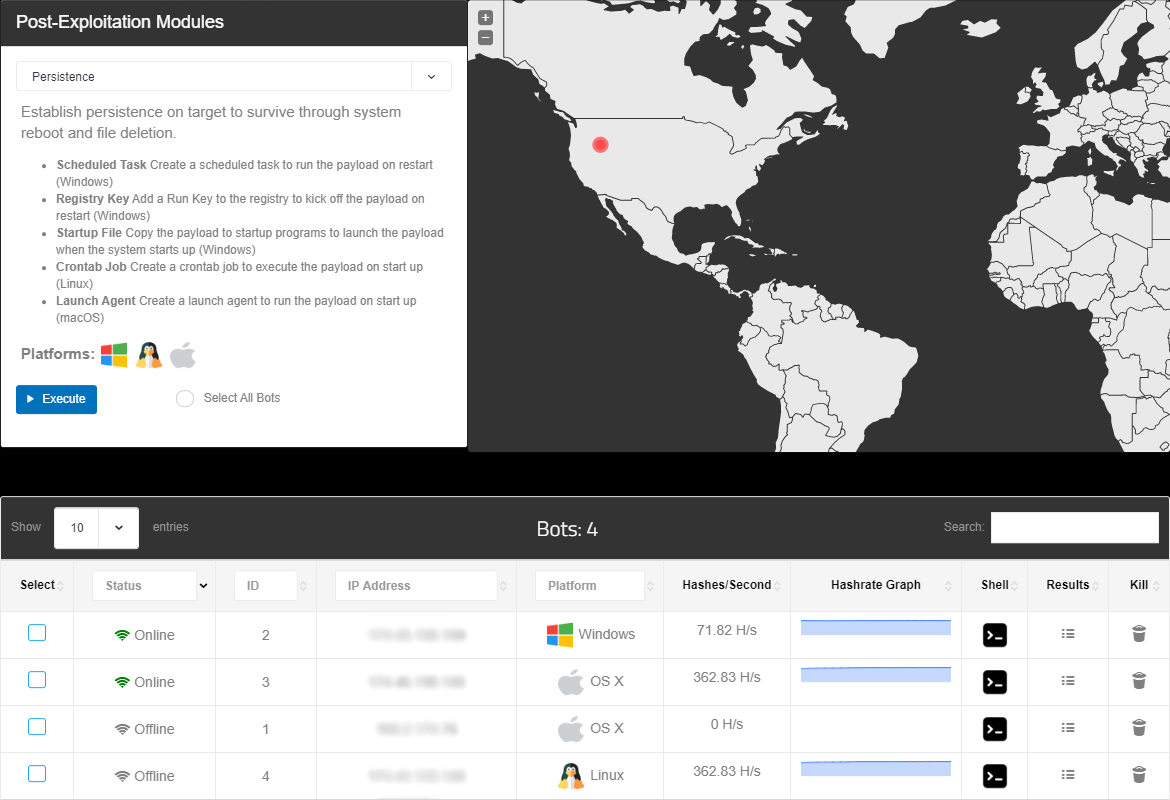 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 redcode-labs/neurax
A framework for constructing self-spreading binaries
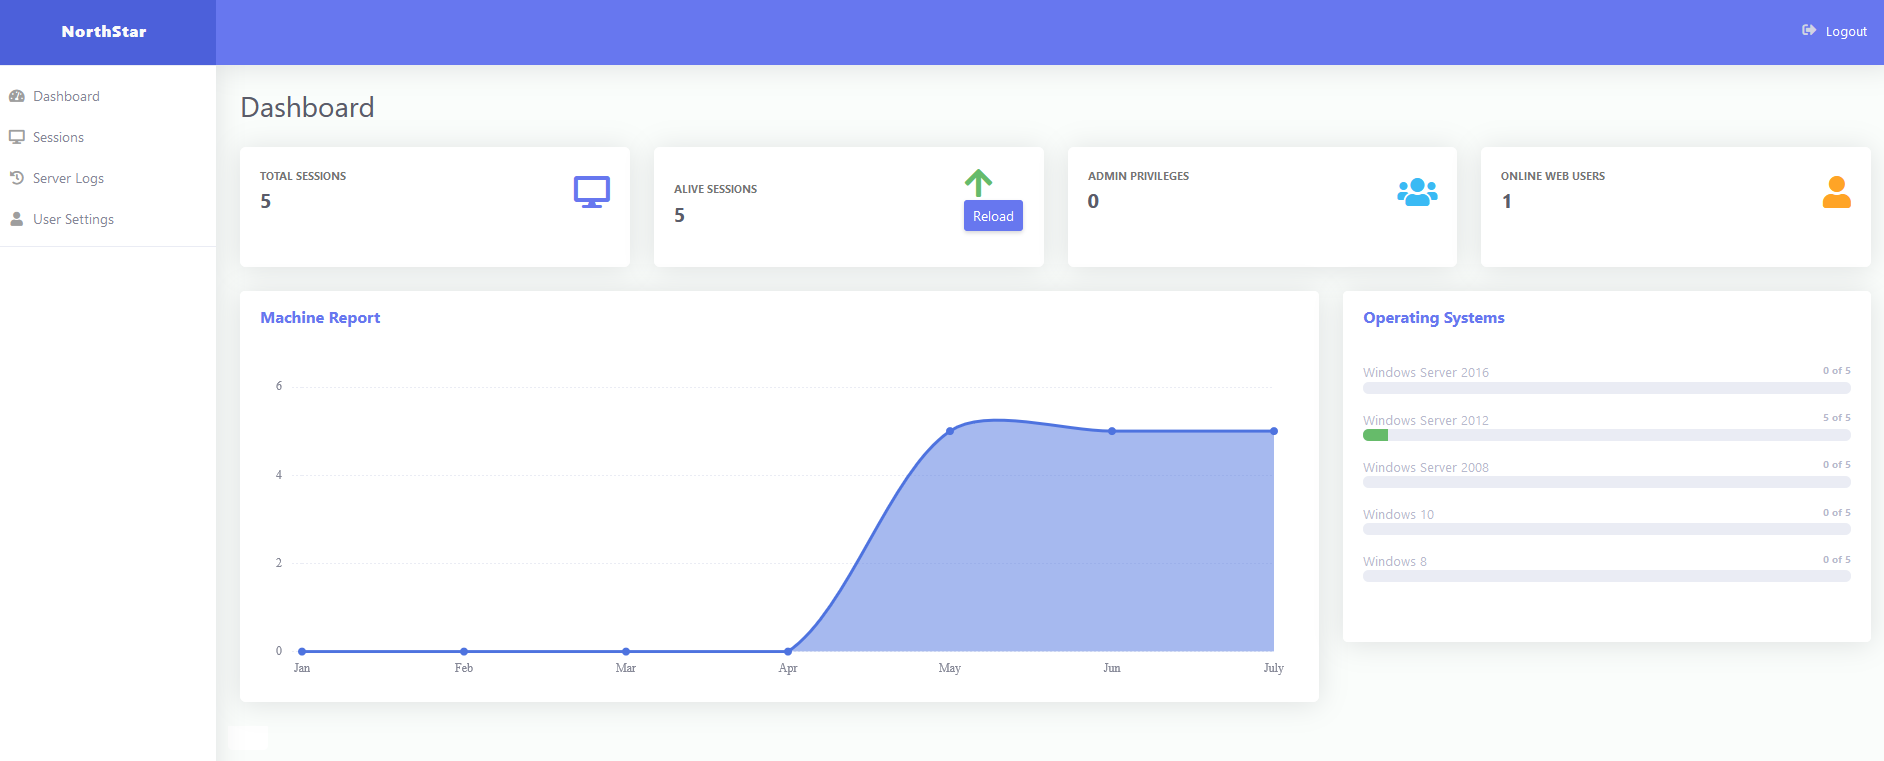 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
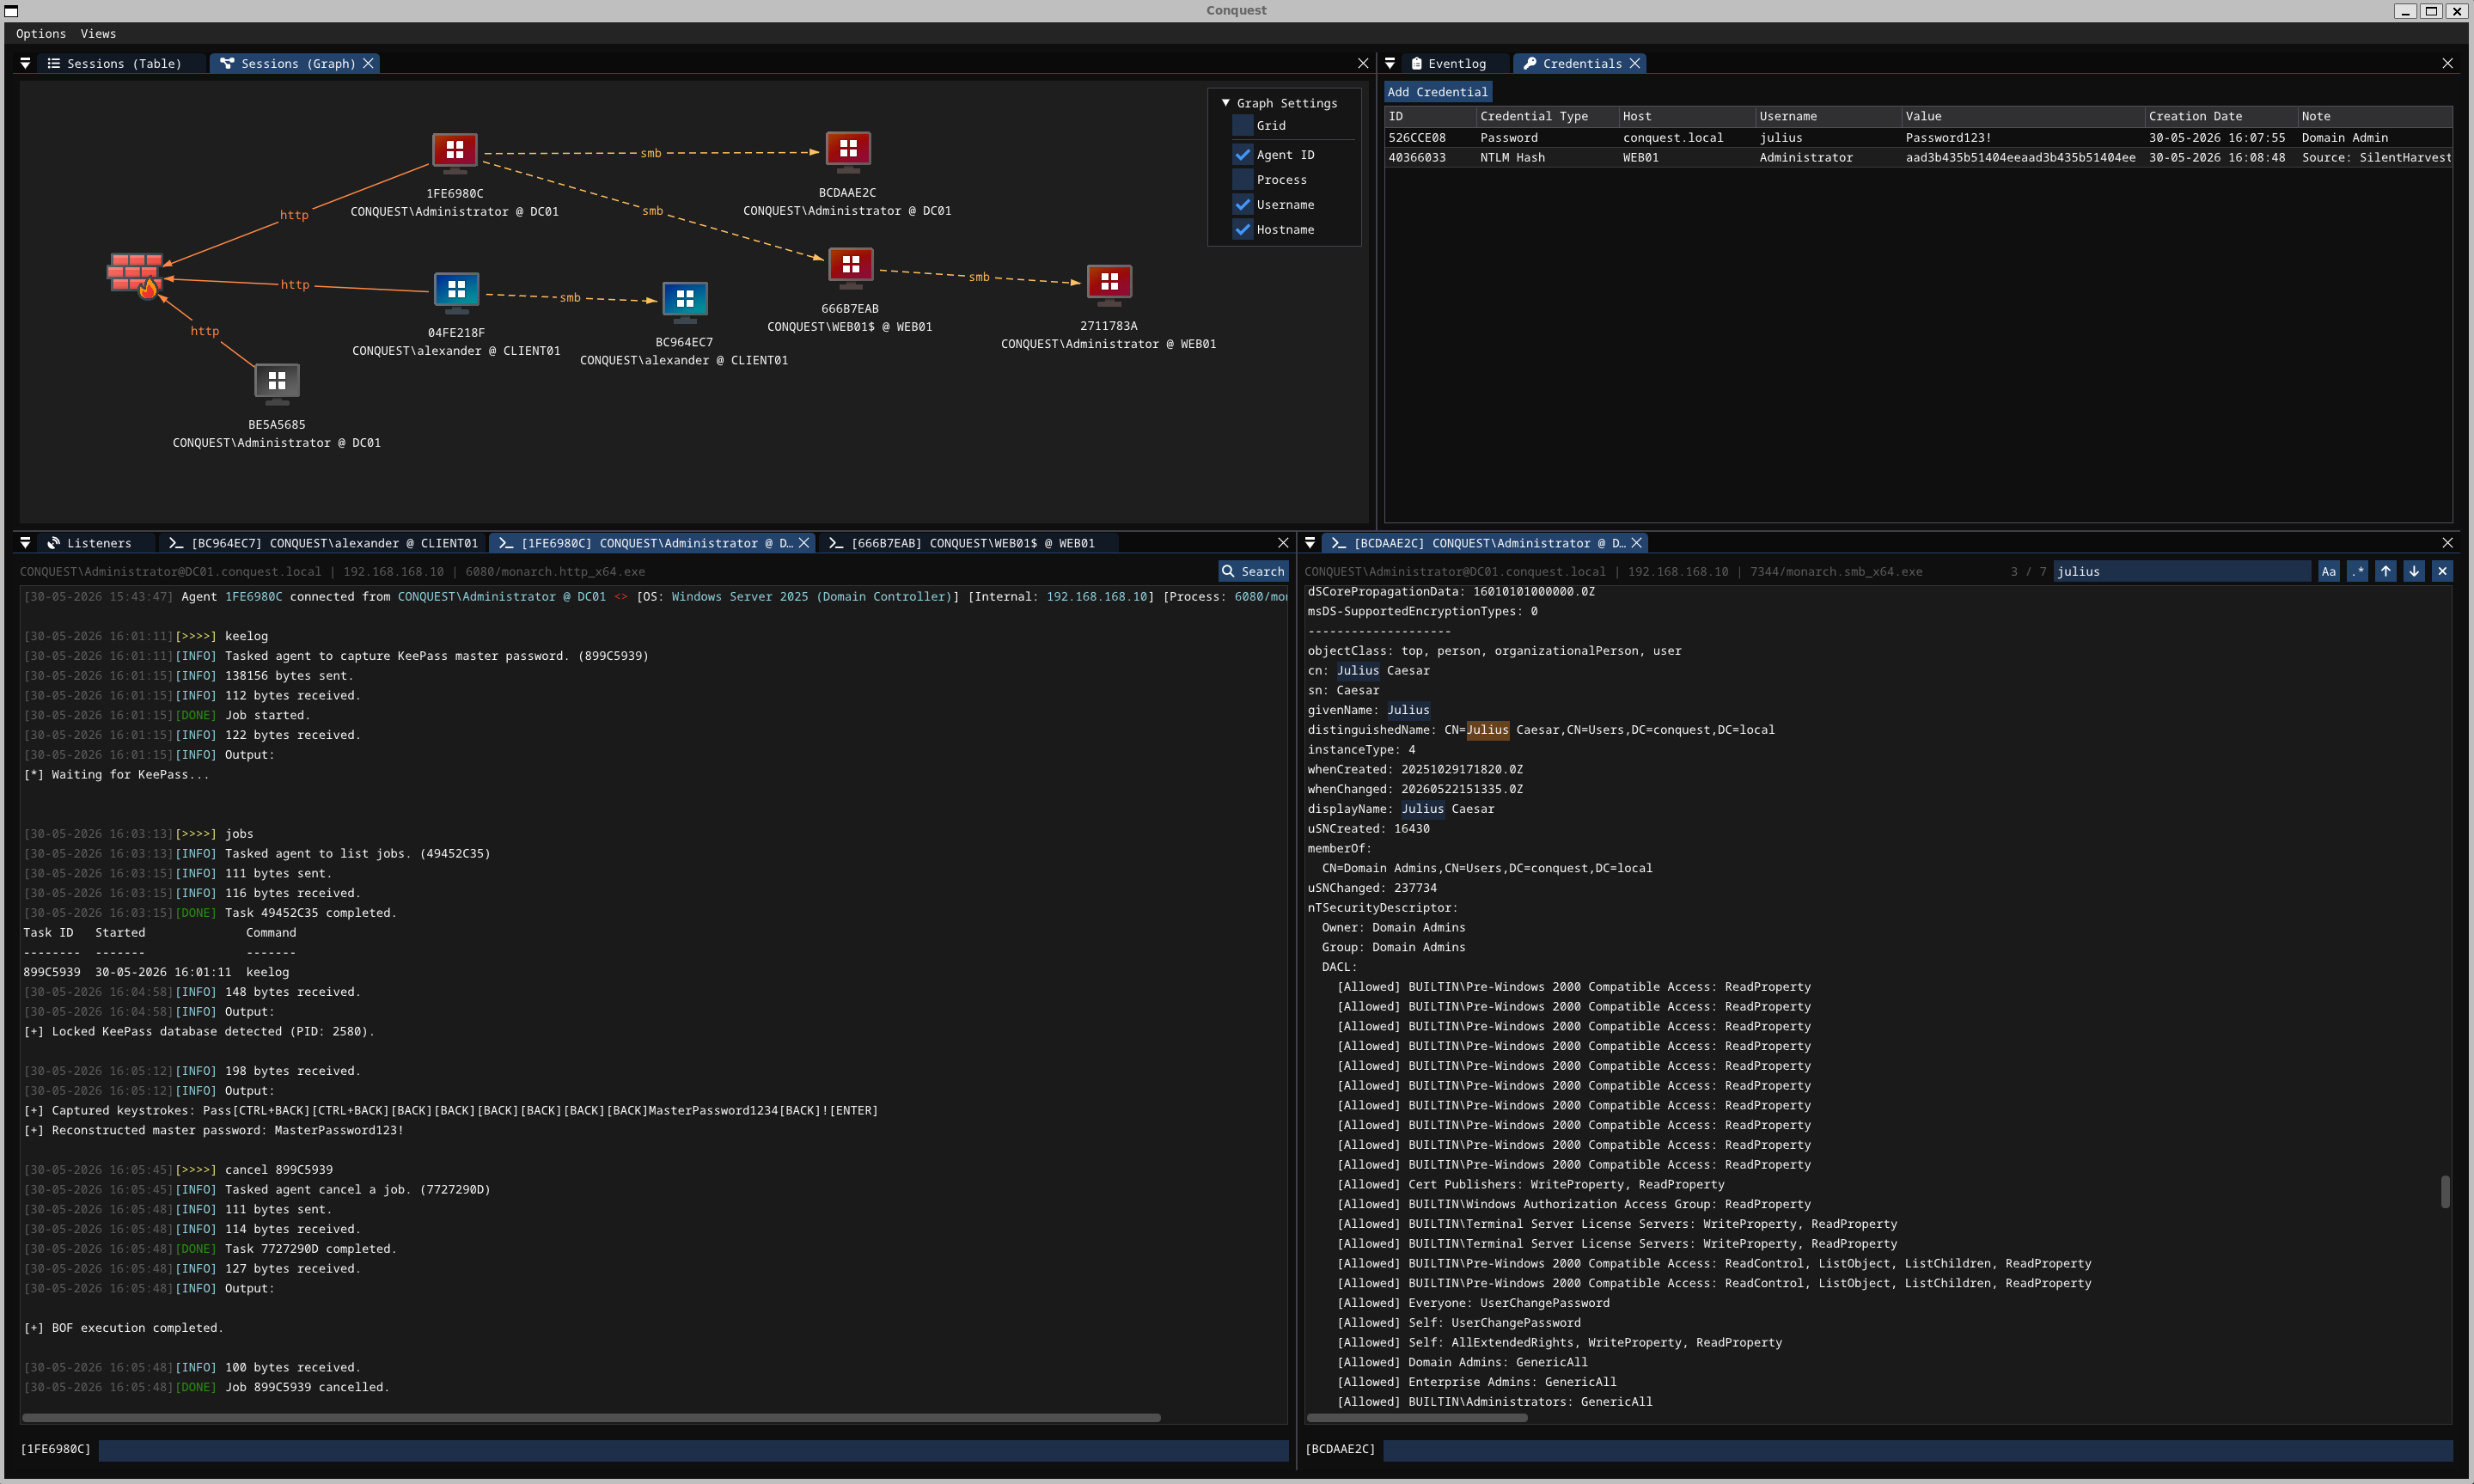 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
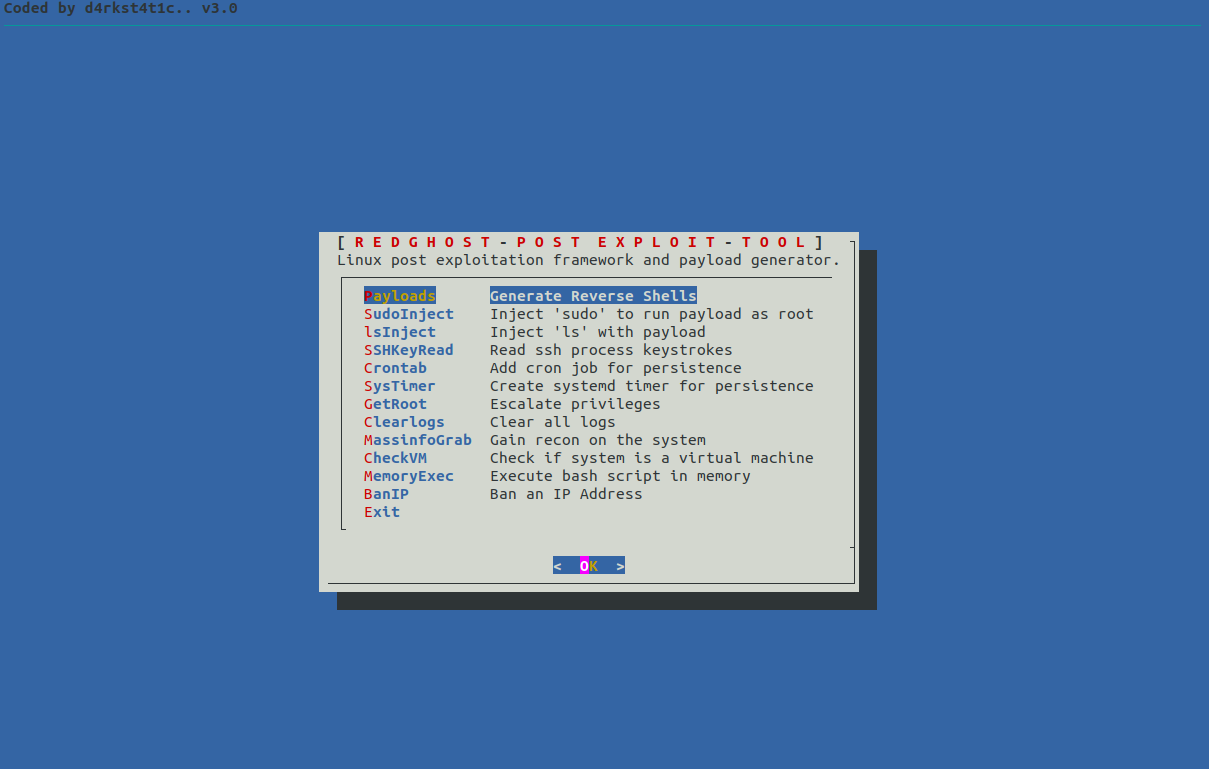 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…