CVE-2026-6875-PoC-Exploit

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

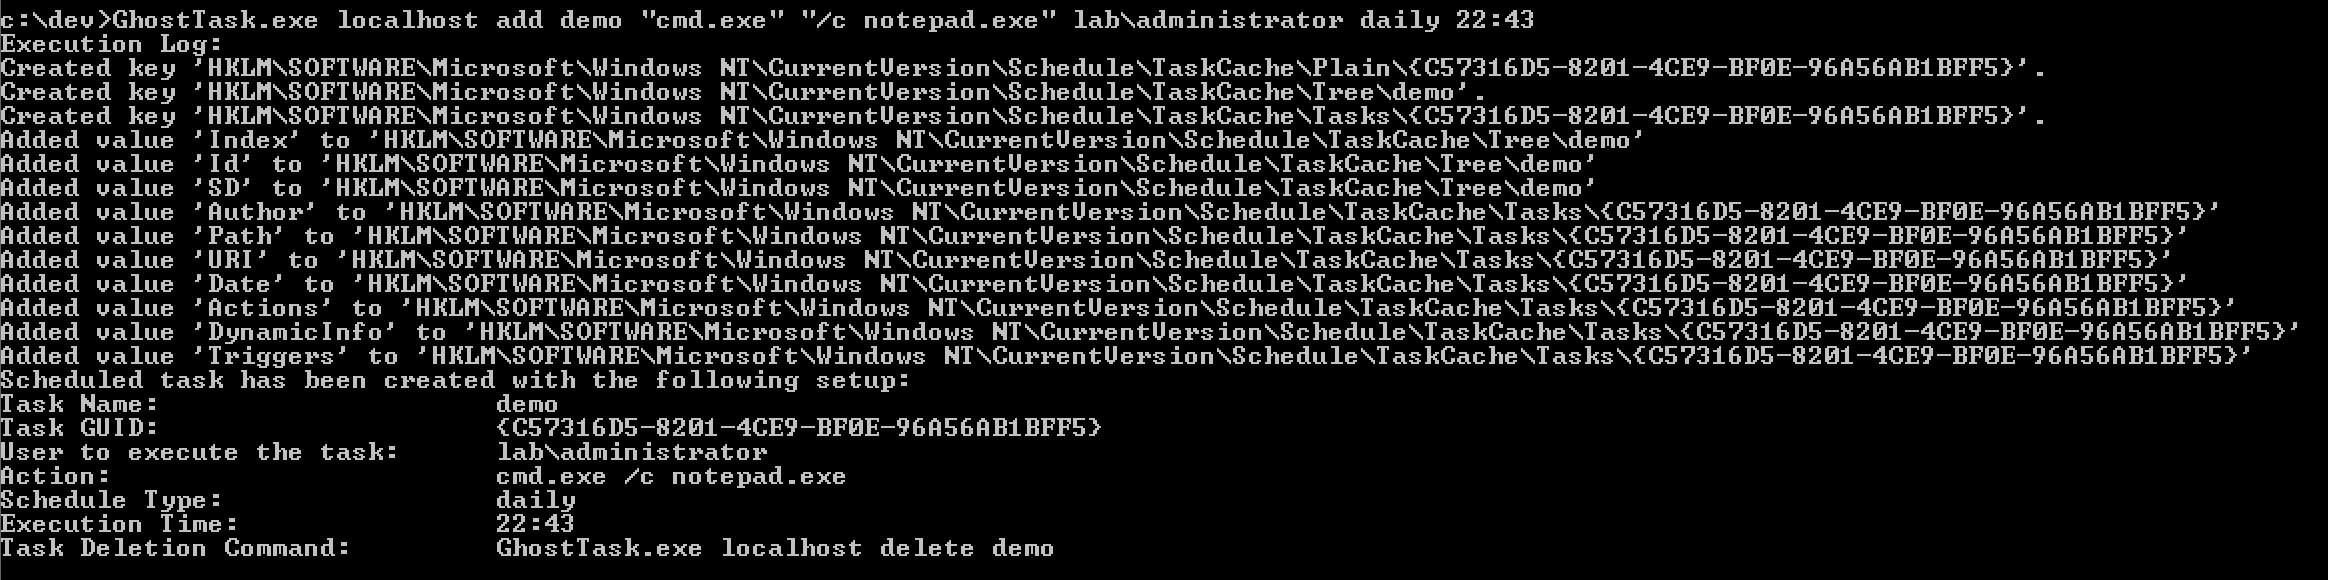
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.

Trying to tame the three-headed dog.

Automated Persistence and Lateral Movement using GCP Patch Management

SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…

A Windows Remote Administration Tool in Visual Basic with UNC paths

Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

PowerSploit - A PowerShell Post-Exploitation Framework

Local & remote Windows DLL Proxying

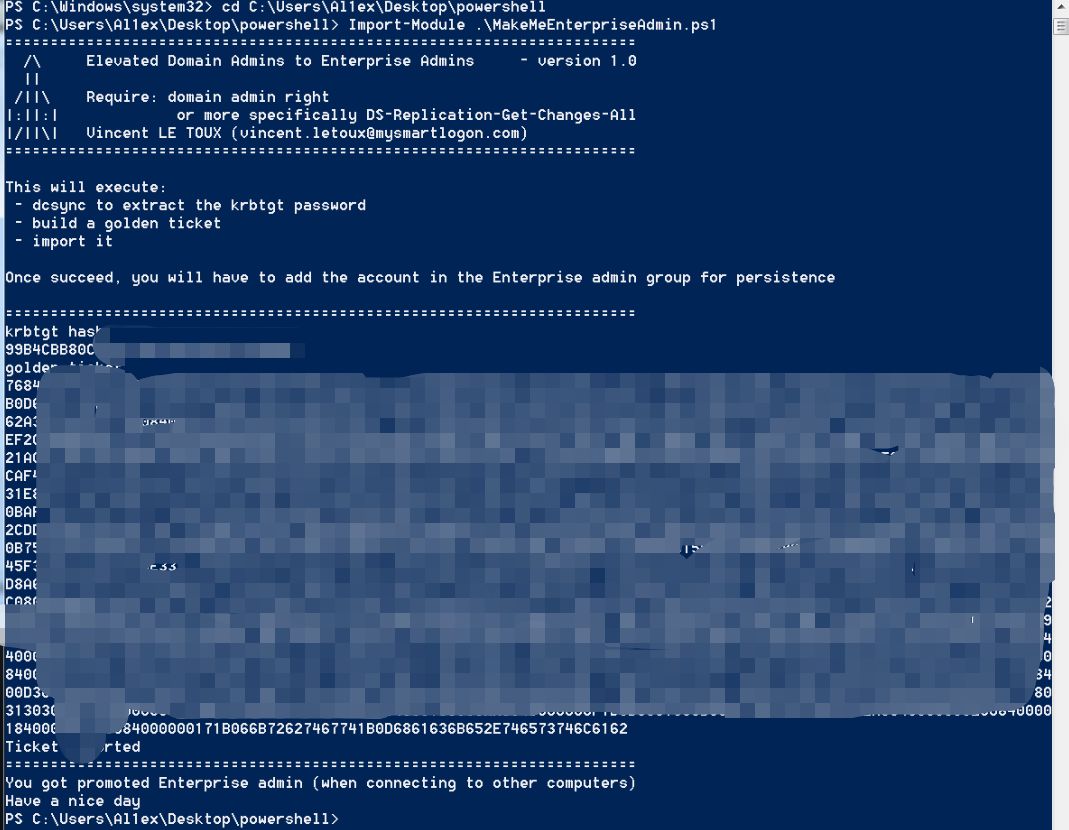
MakeMeEnterpriseAdmin

Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…

A script to automate keystrokes through a graphical desktop program.

TCP Port Redirection Utility

exp for CVE-2019-0887

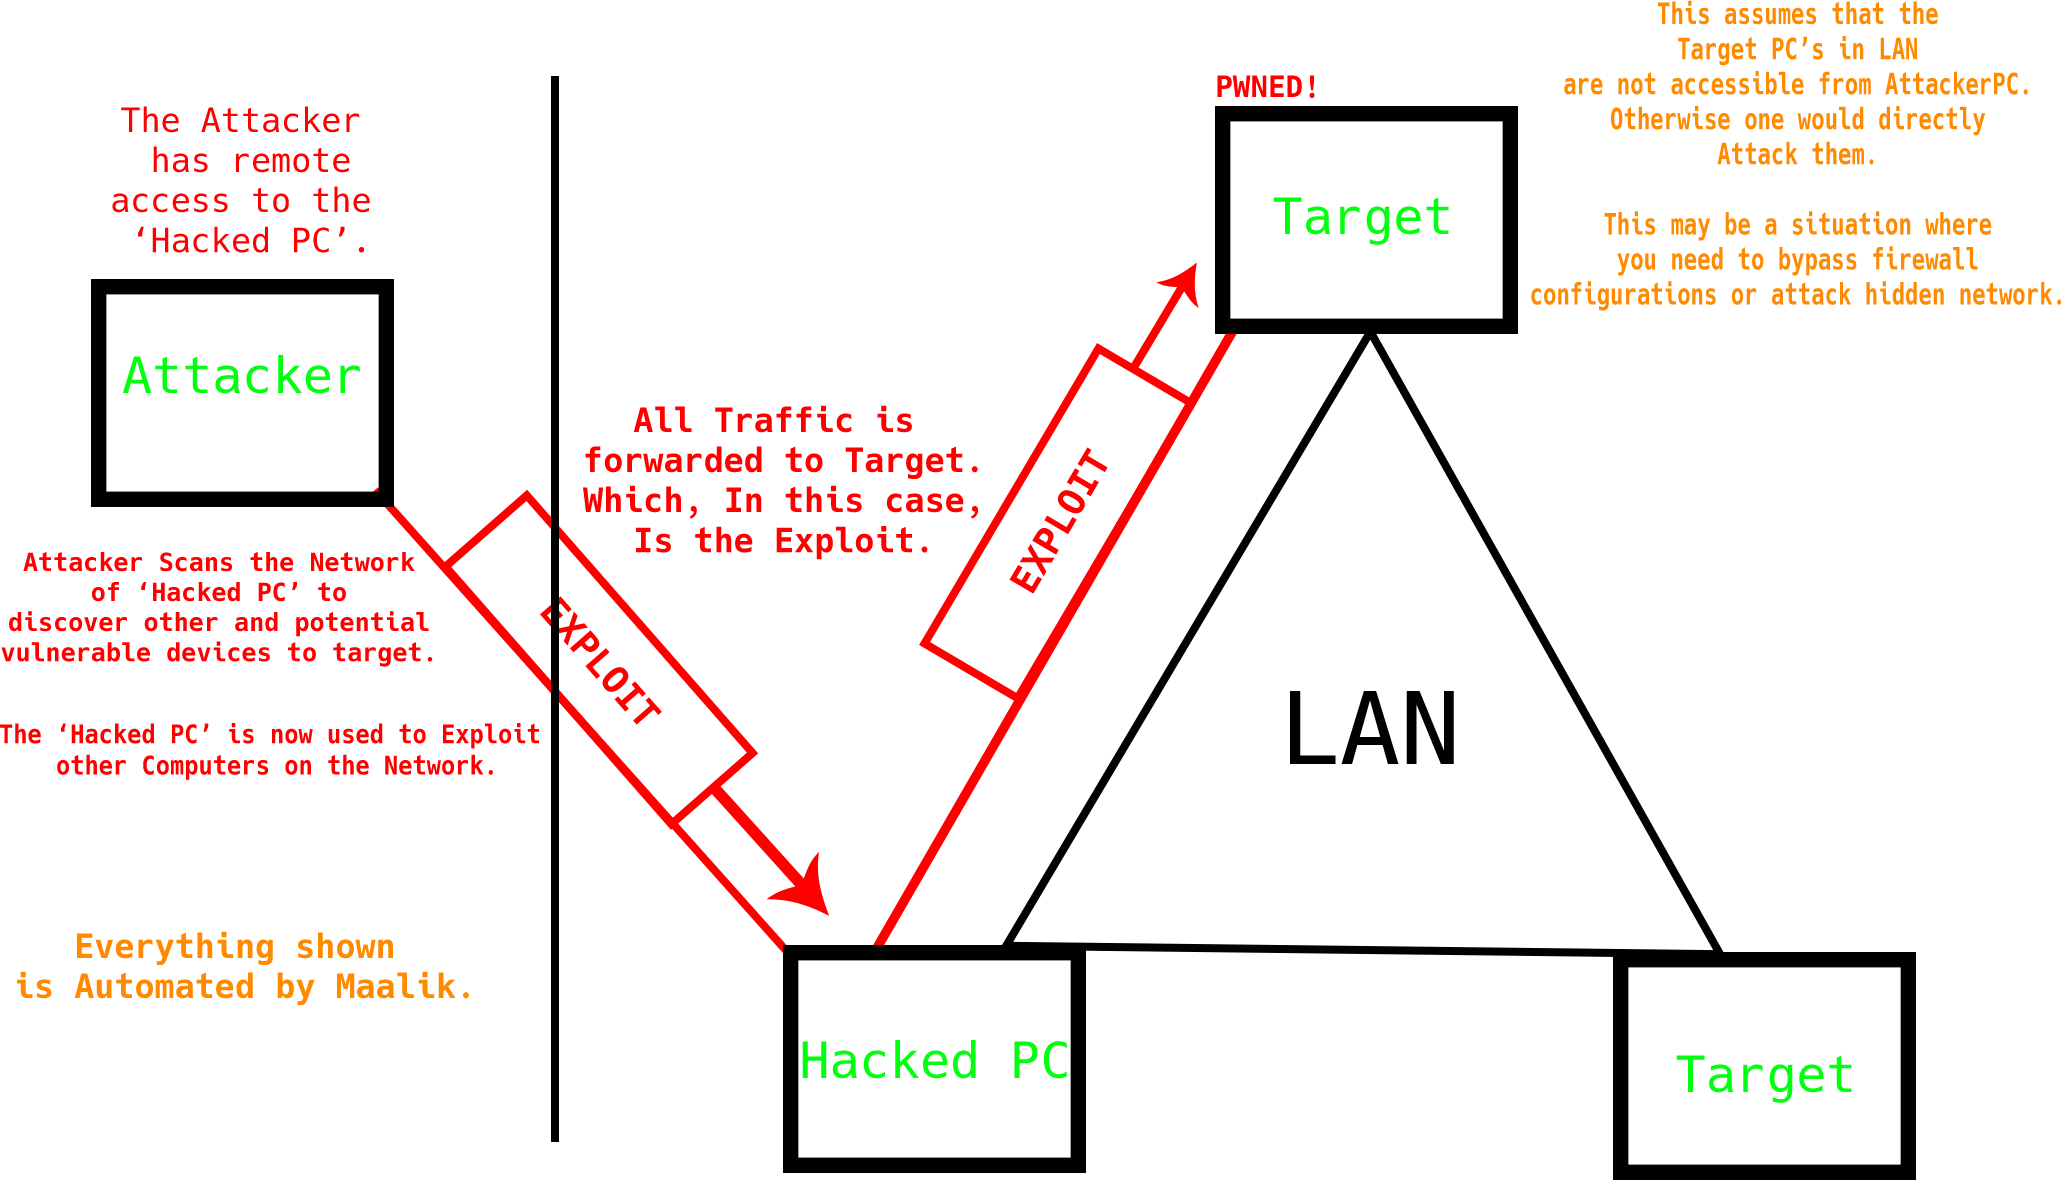
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.

A framework for constructing self-spreading binaries