
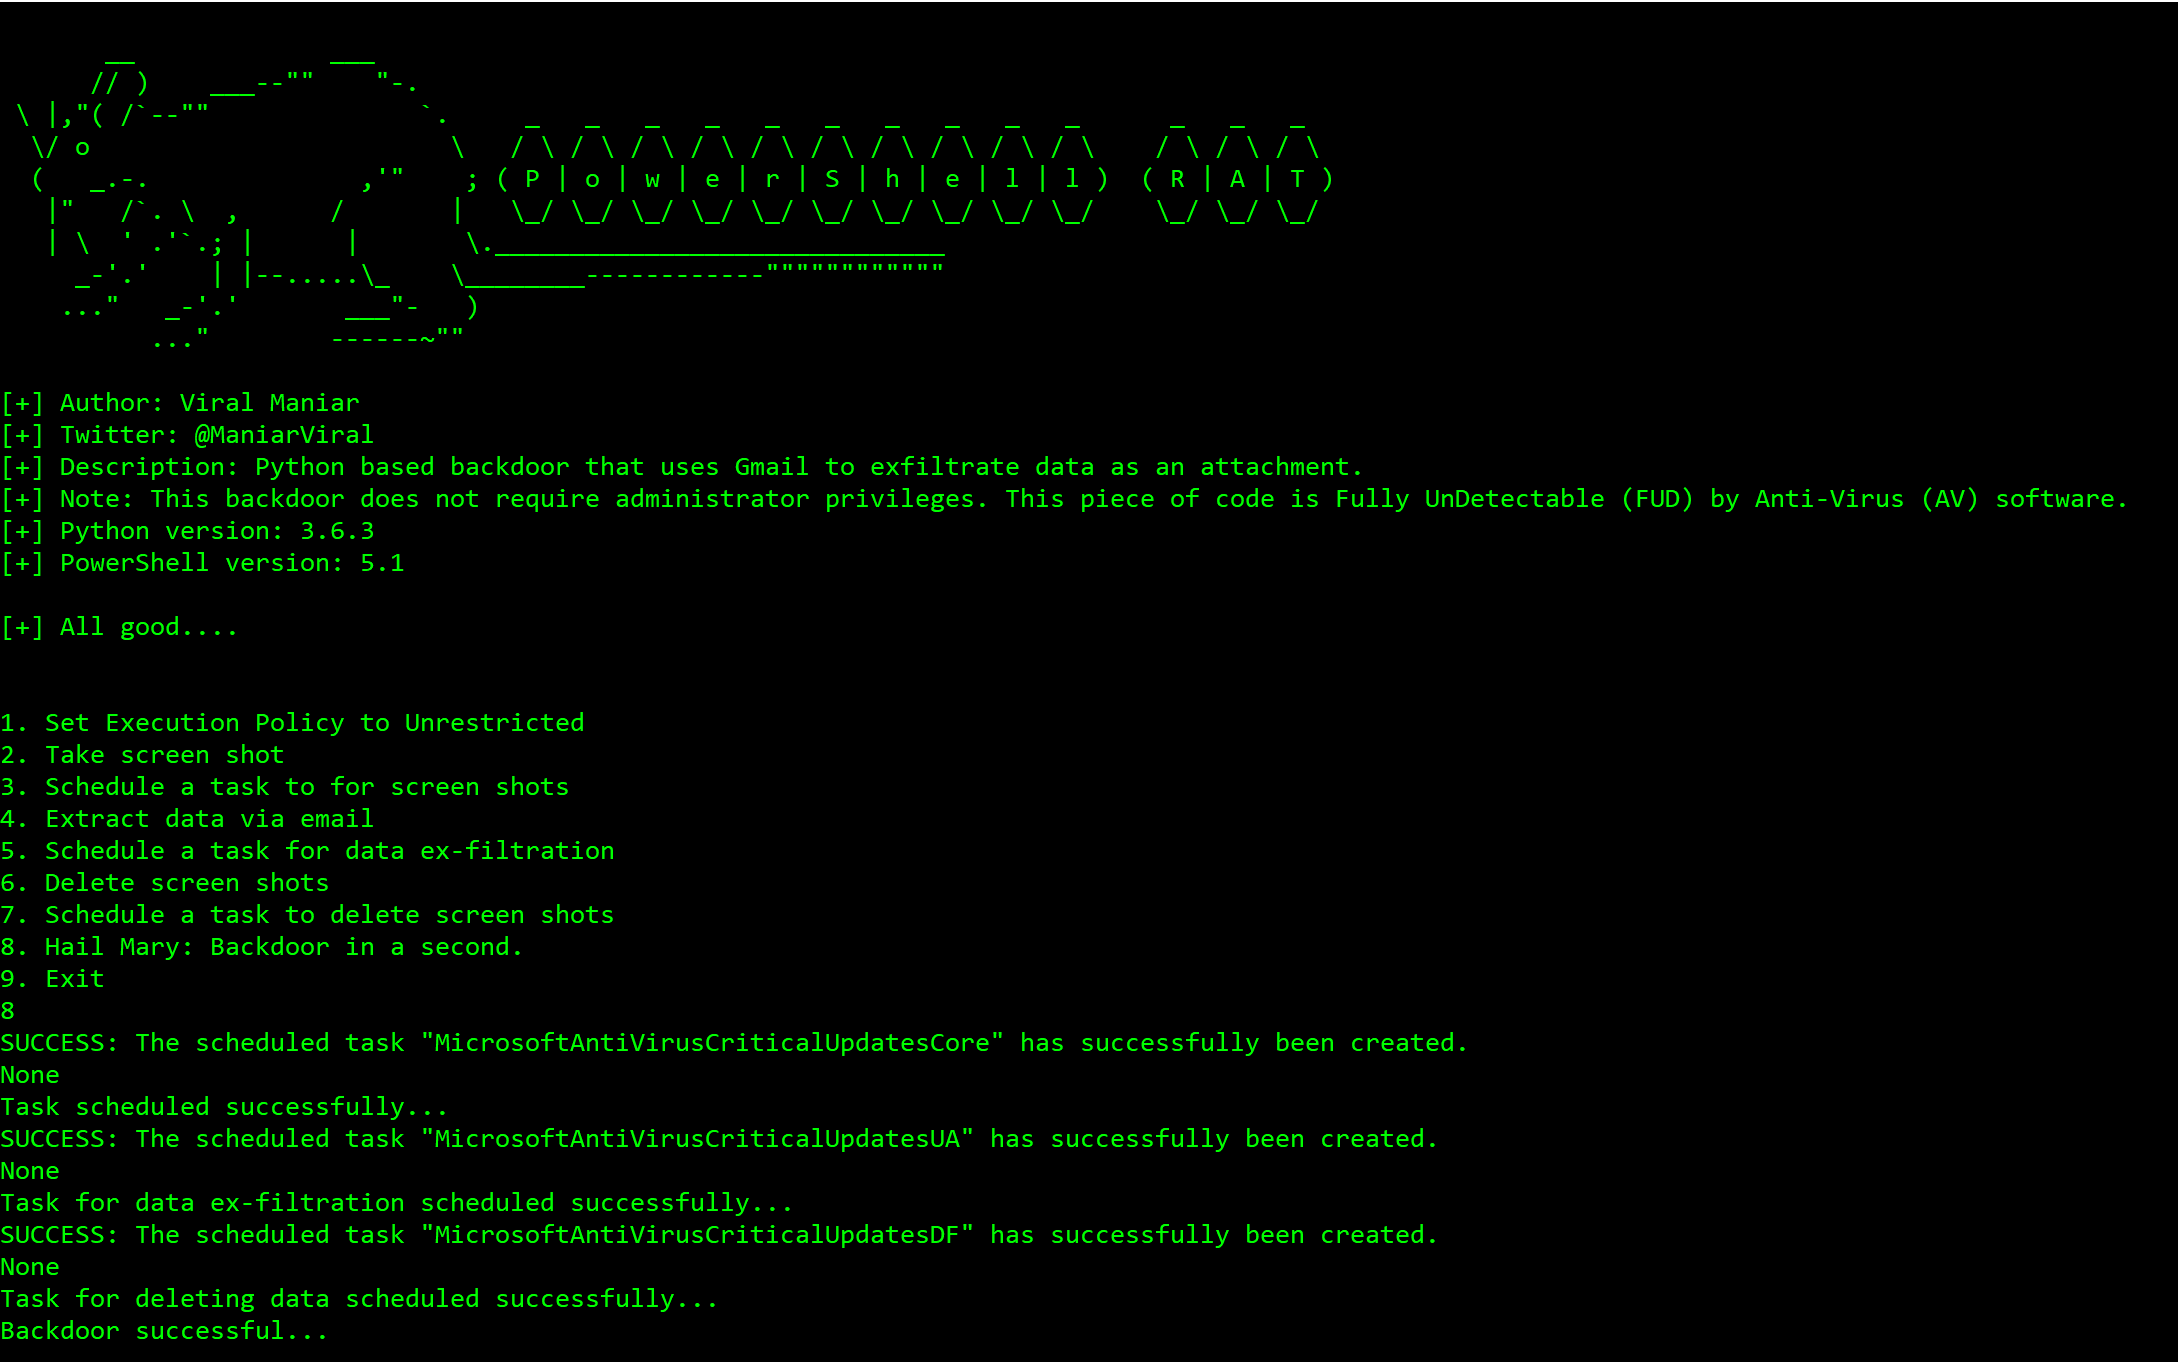
Powershell-RAT
 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
data-exfiltrationeducationpayload-generation+4
1.2k
viralmaniar/powershell-ratPython based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
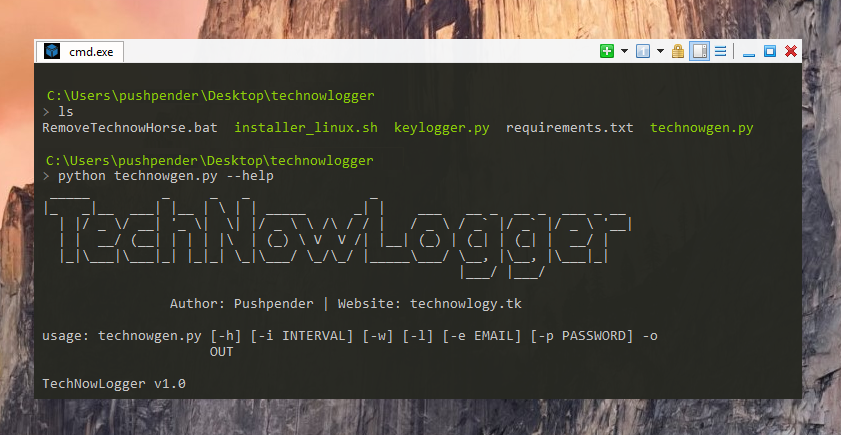 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
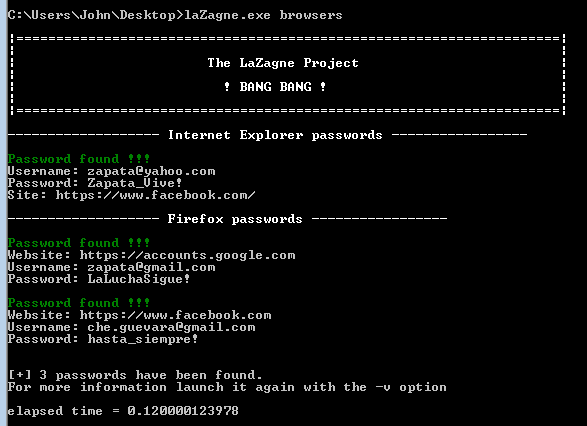 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
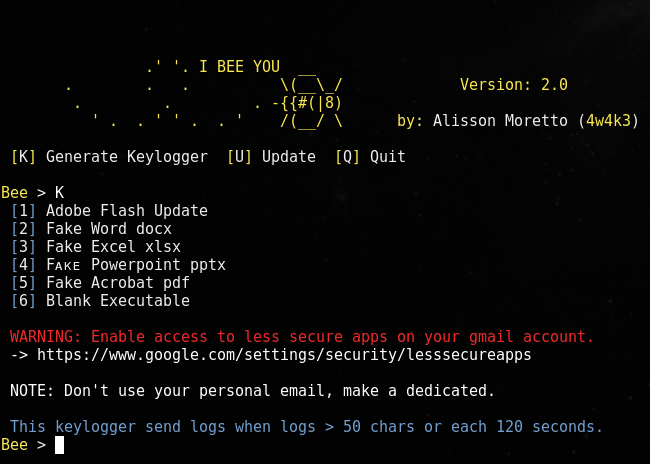 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.
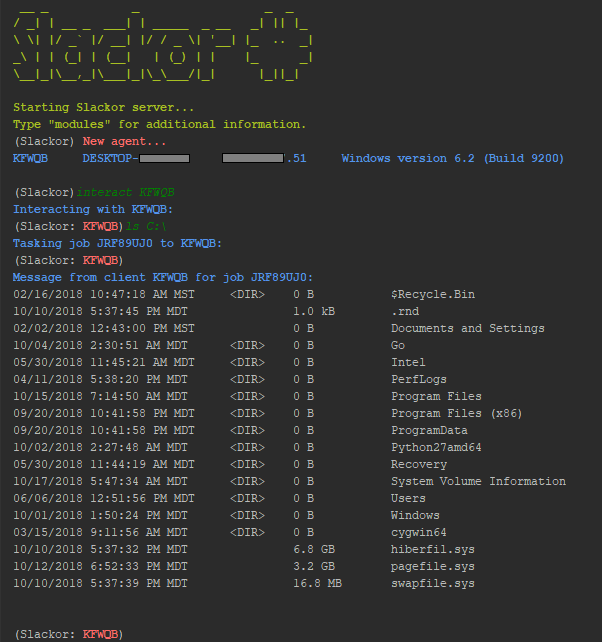 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
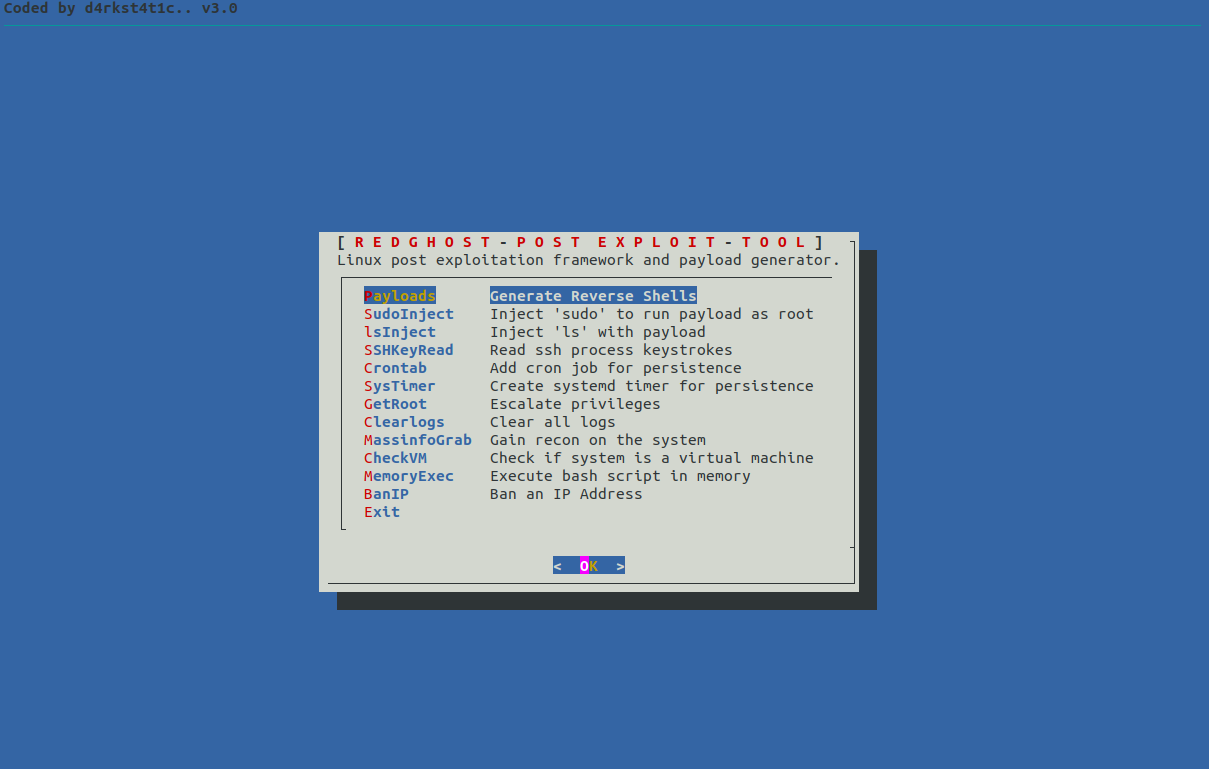 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 sensepost/ruler
A tool to abuse Exchange services
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
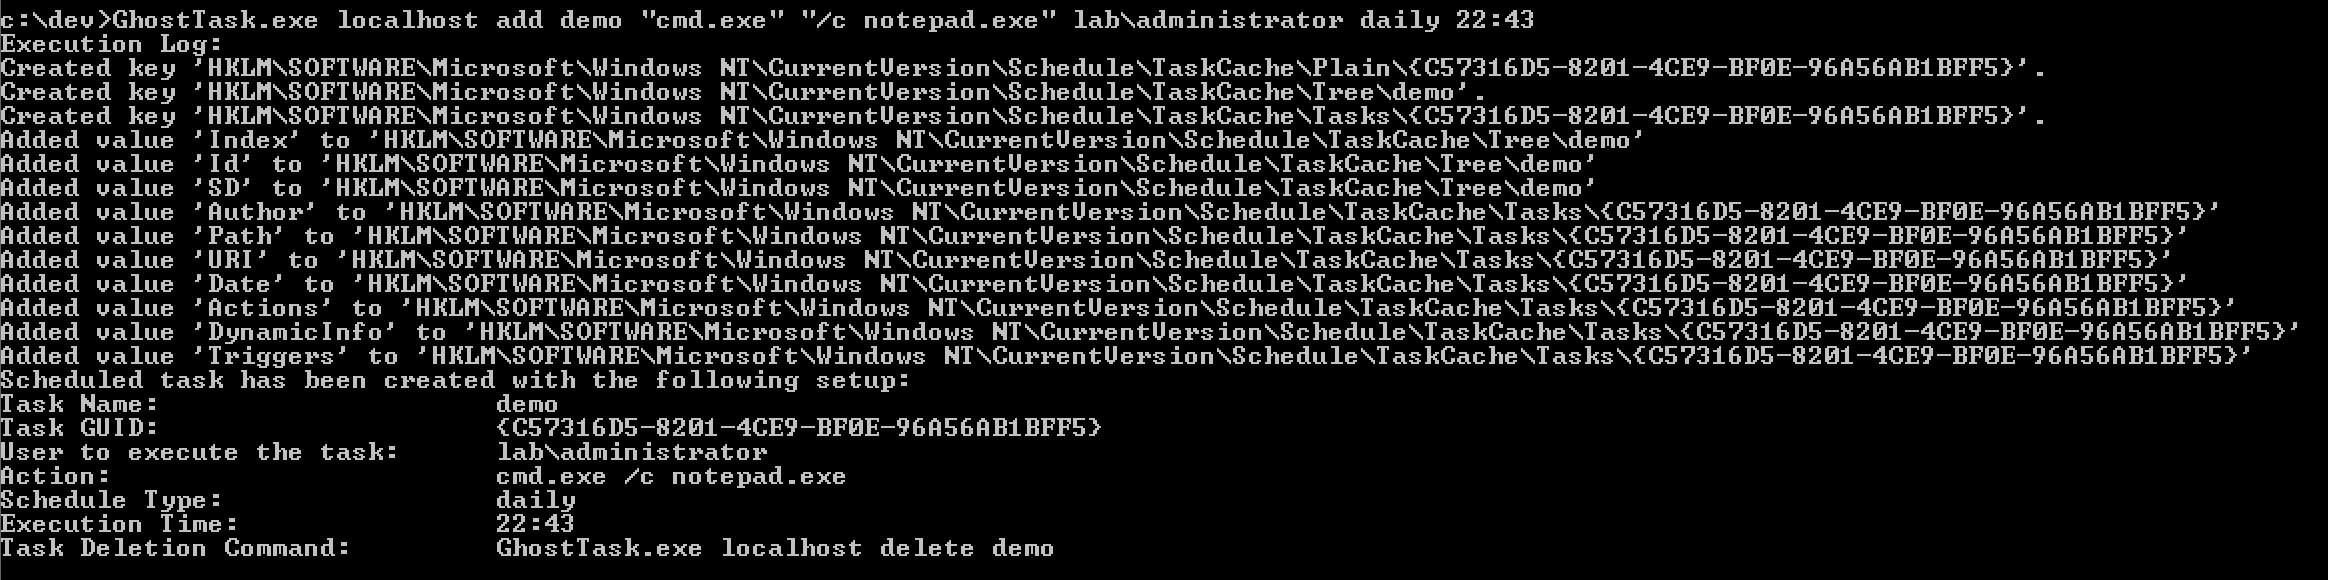 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
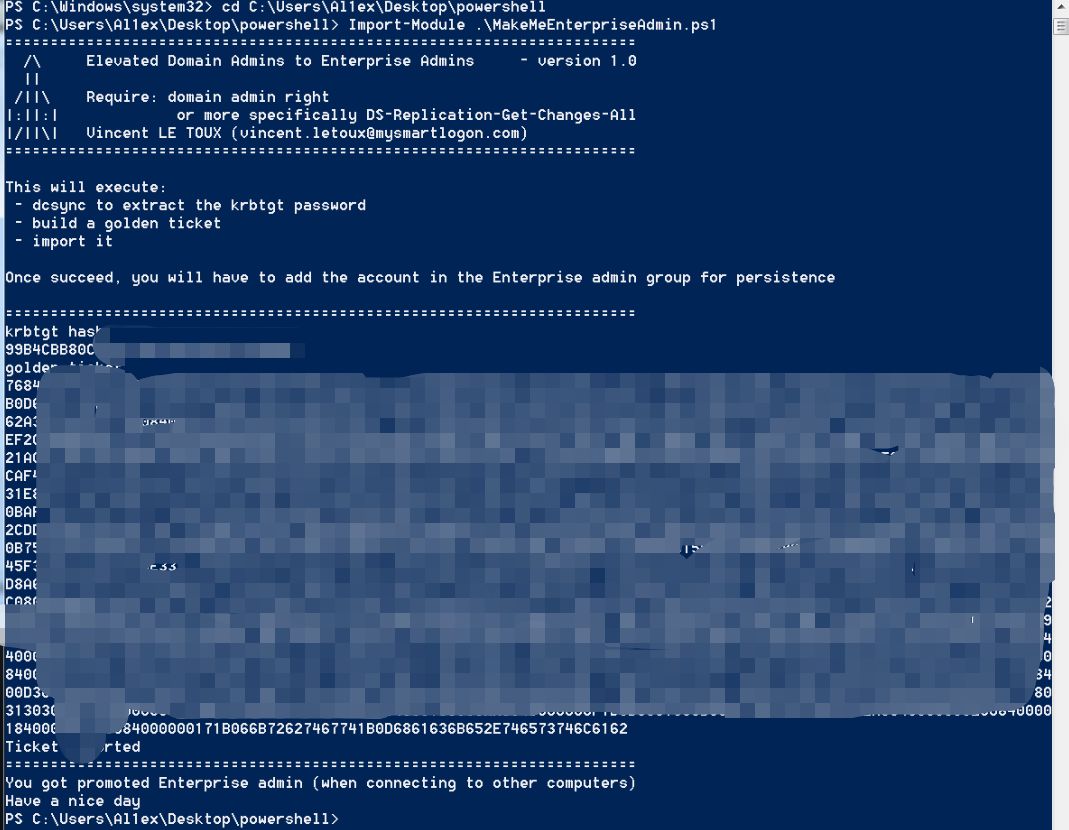 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin