
Archived
RAT-via-Telegram
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
command-and-controldata-exfiltrationpassword-cracking+6
713
mvrozanti/rat-via-telegramWindows Remote Administration Tool via Telegram
 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
 synacktiv/dlhell
Local & remote Windows DLL Proxying
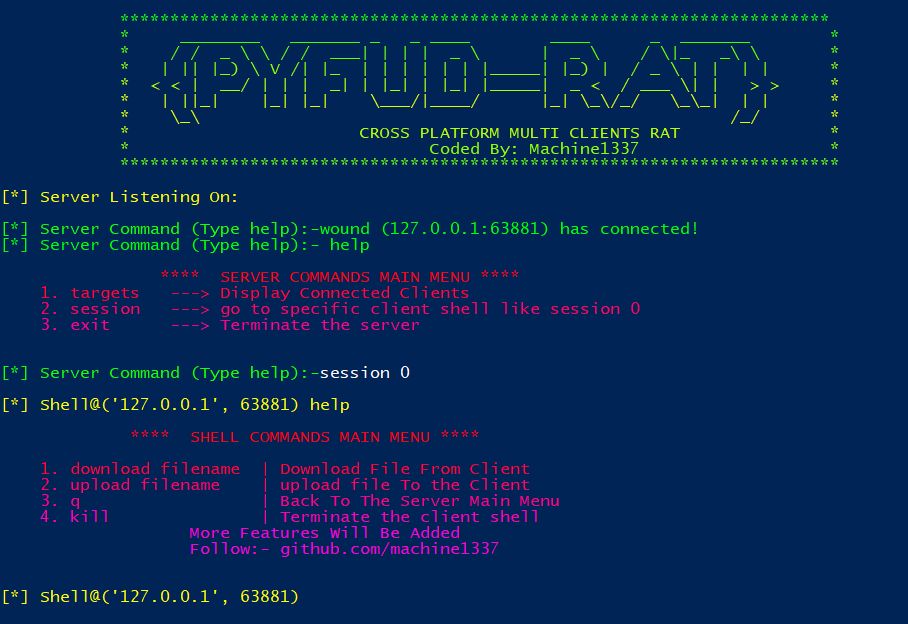 machine1337/pyfud
CROSS PLATFORM REMOTE ACCESS TROJAN (RAT)
 xforcered/scmkit
Source Code Management Attack Toolkit
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 salaheldinfikri/kalim_backdoor
Kalim backdooe Malware Report
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting