
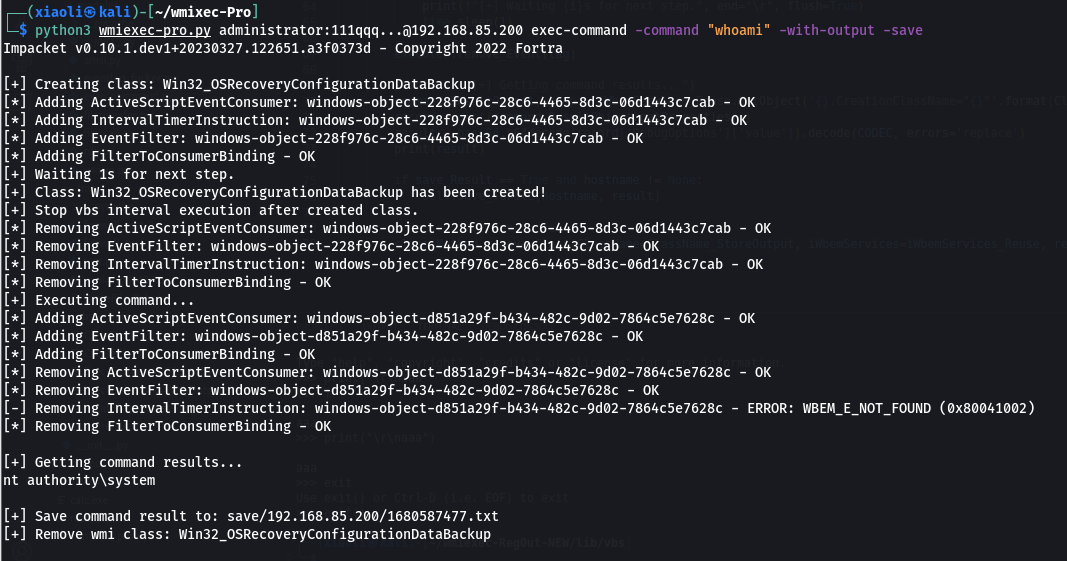
wmiexec-Pro
 xiaolichan/wmiexec-pro
New generation of wmiexec.py
information-gatheringlateral-movementpenetration-testing+5
xiaolichan/wmiexec-proNew generation of wmiexec.py
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
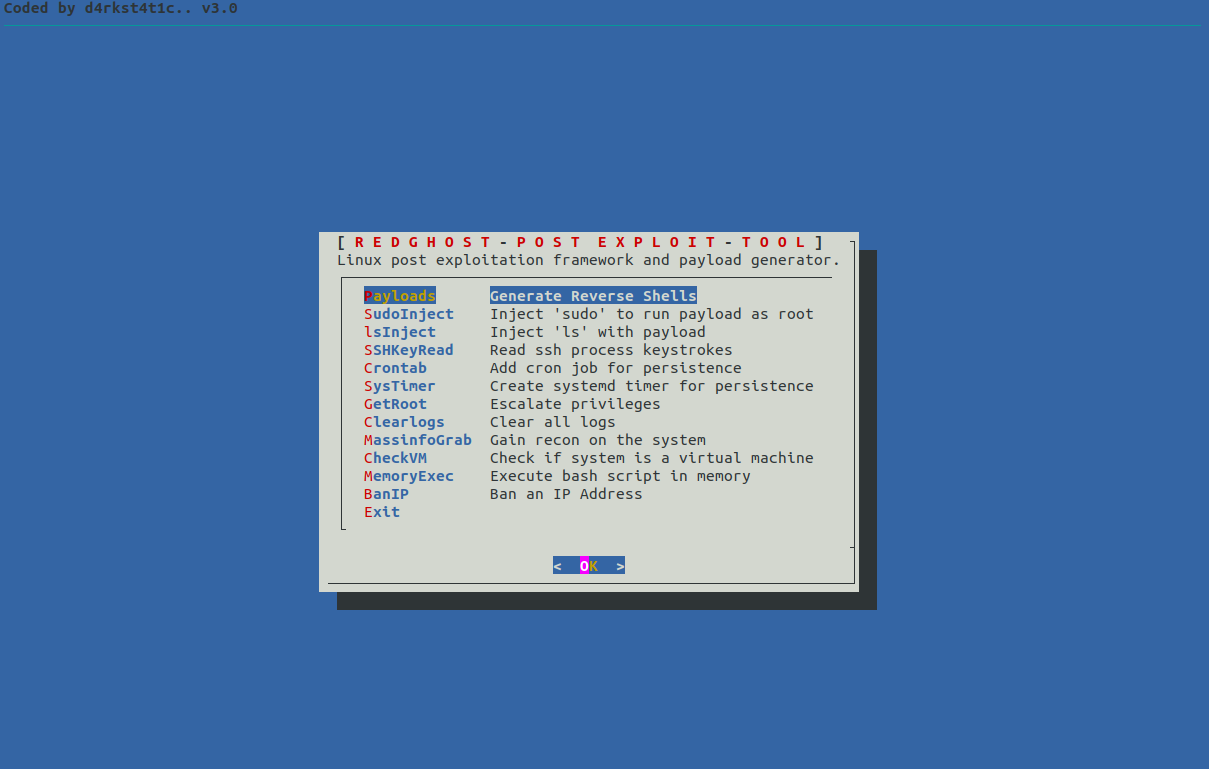 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
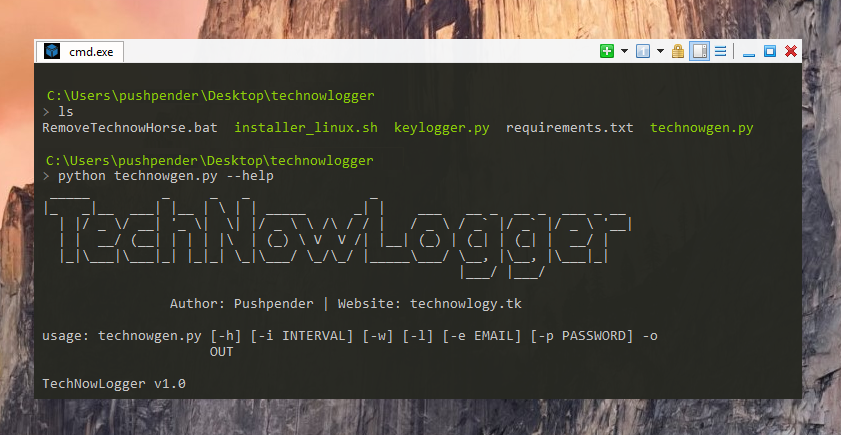 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
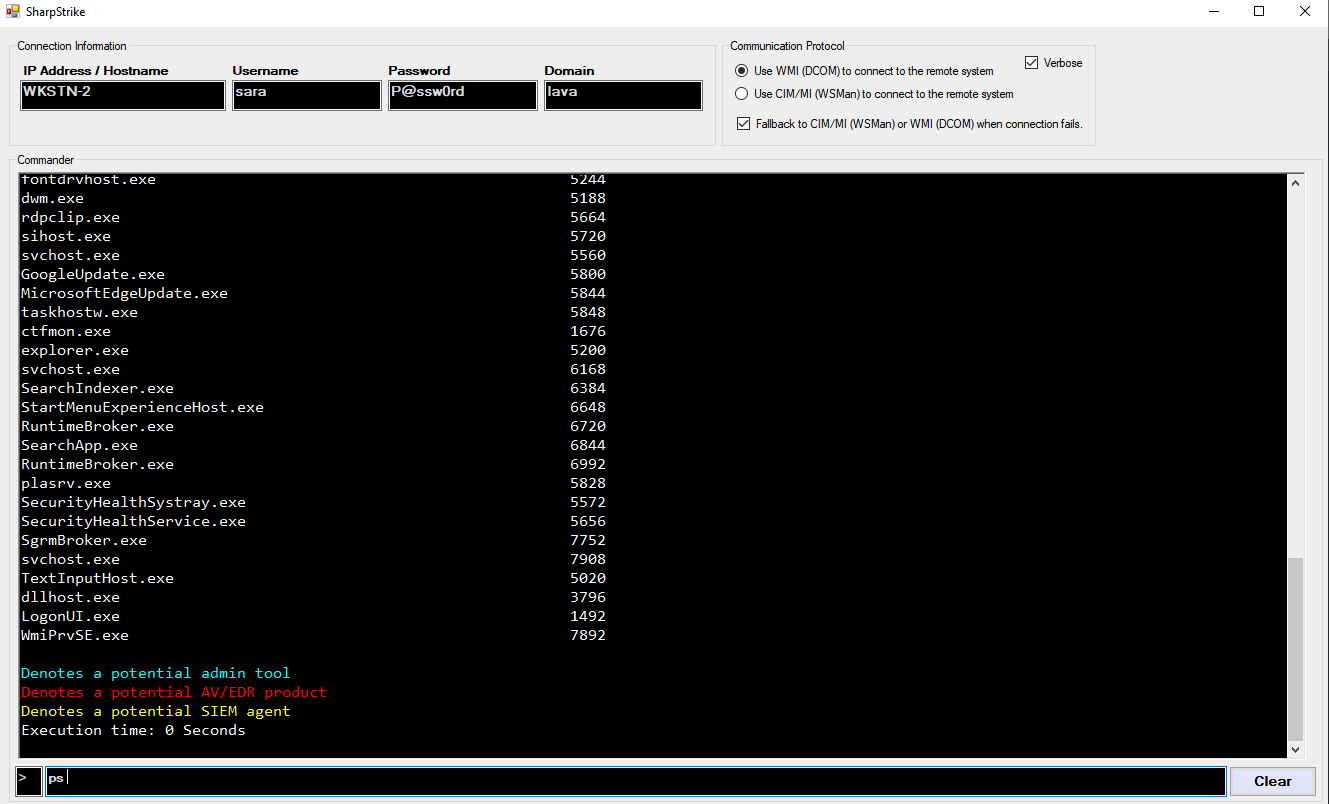 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
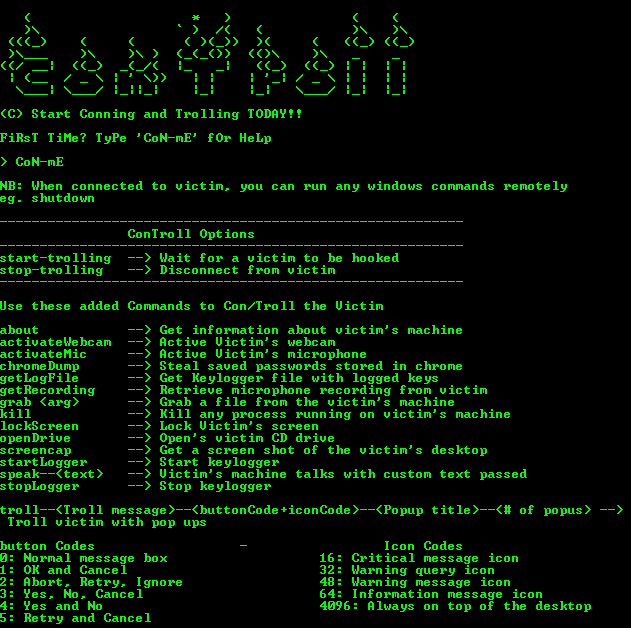 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
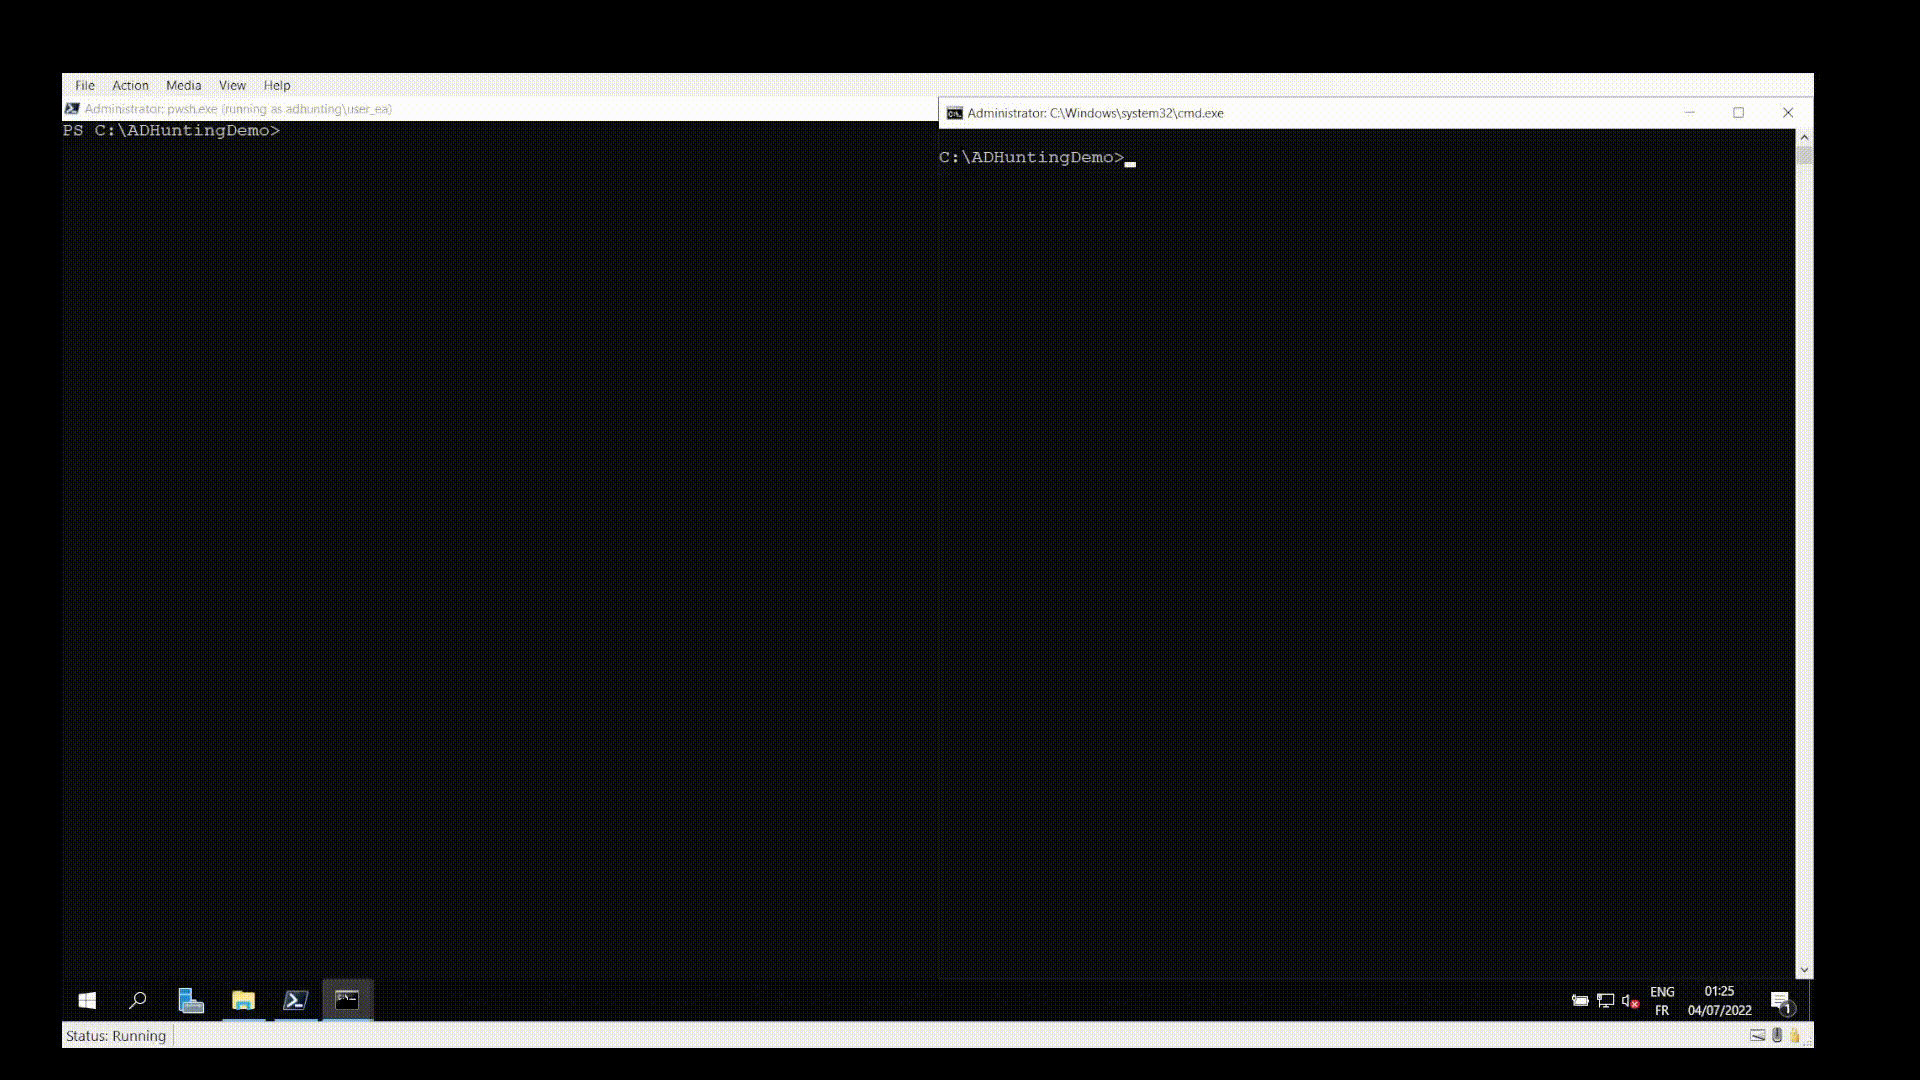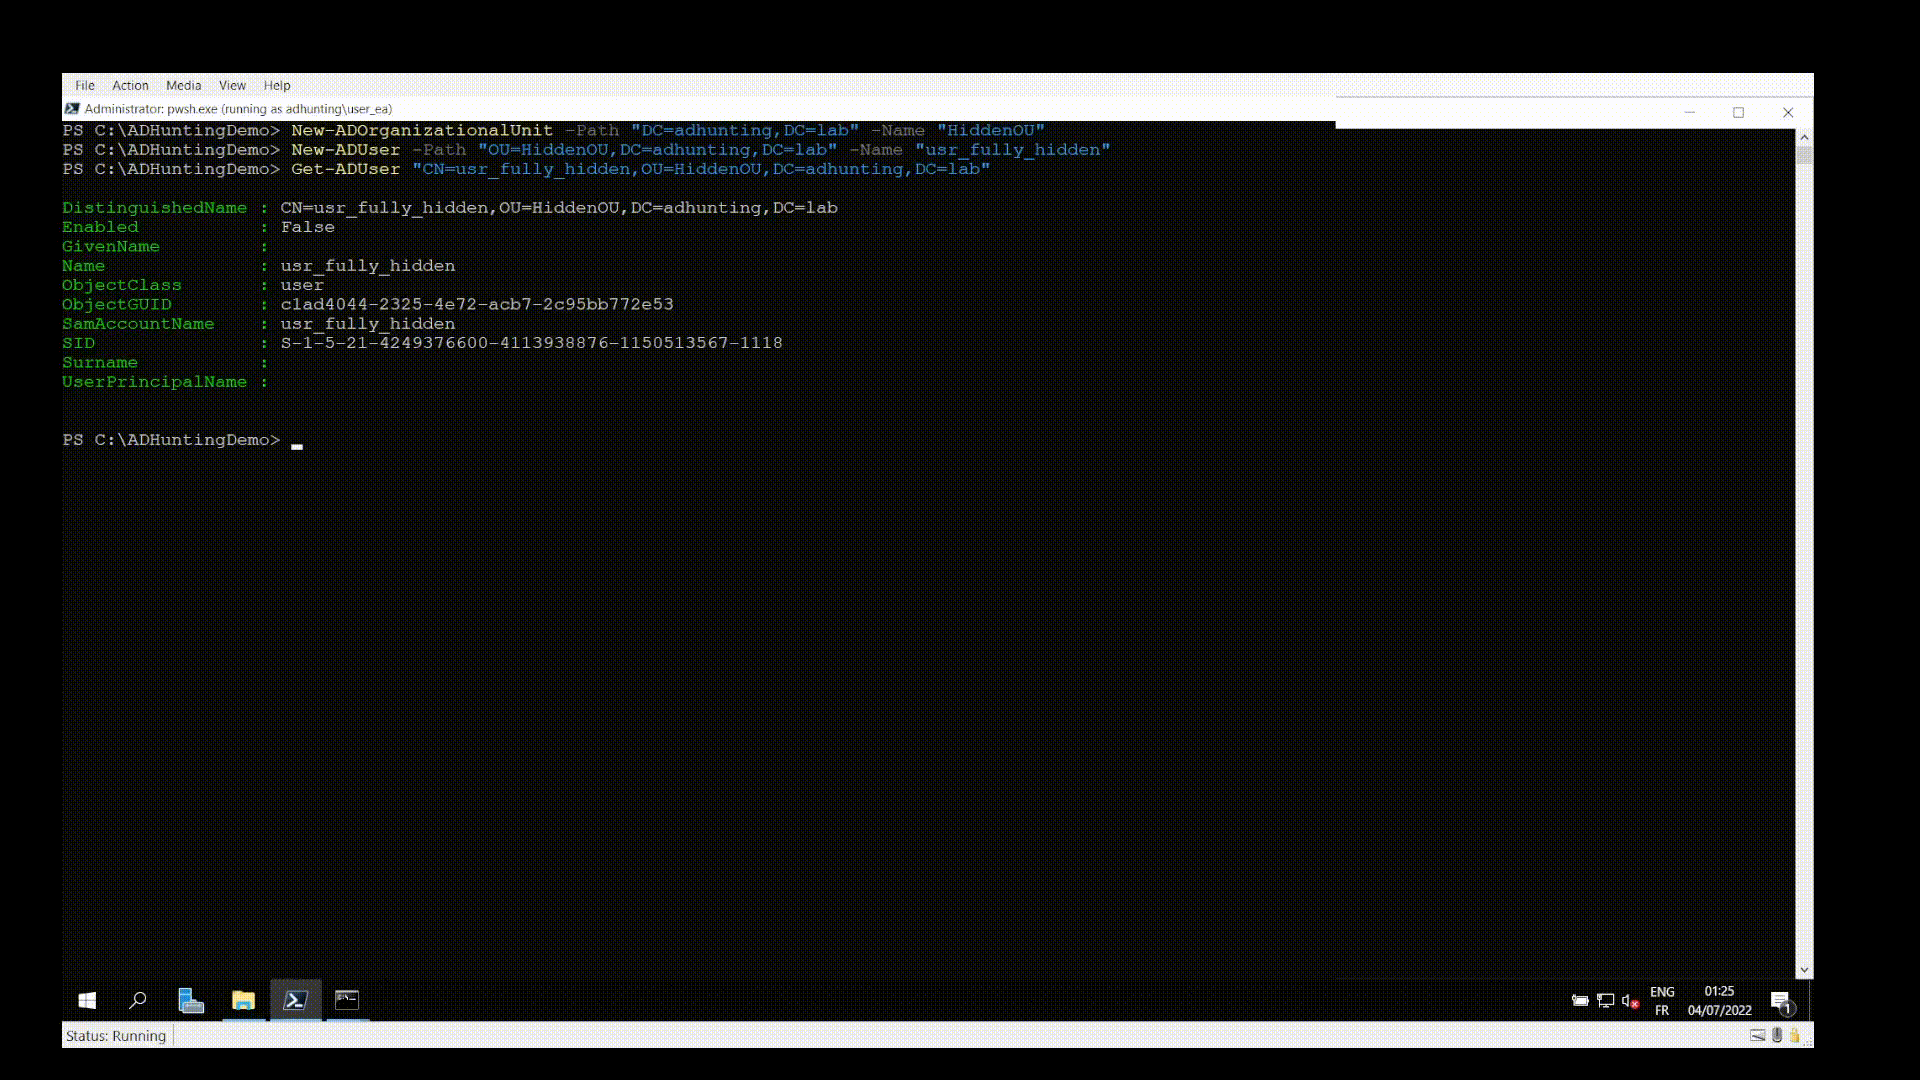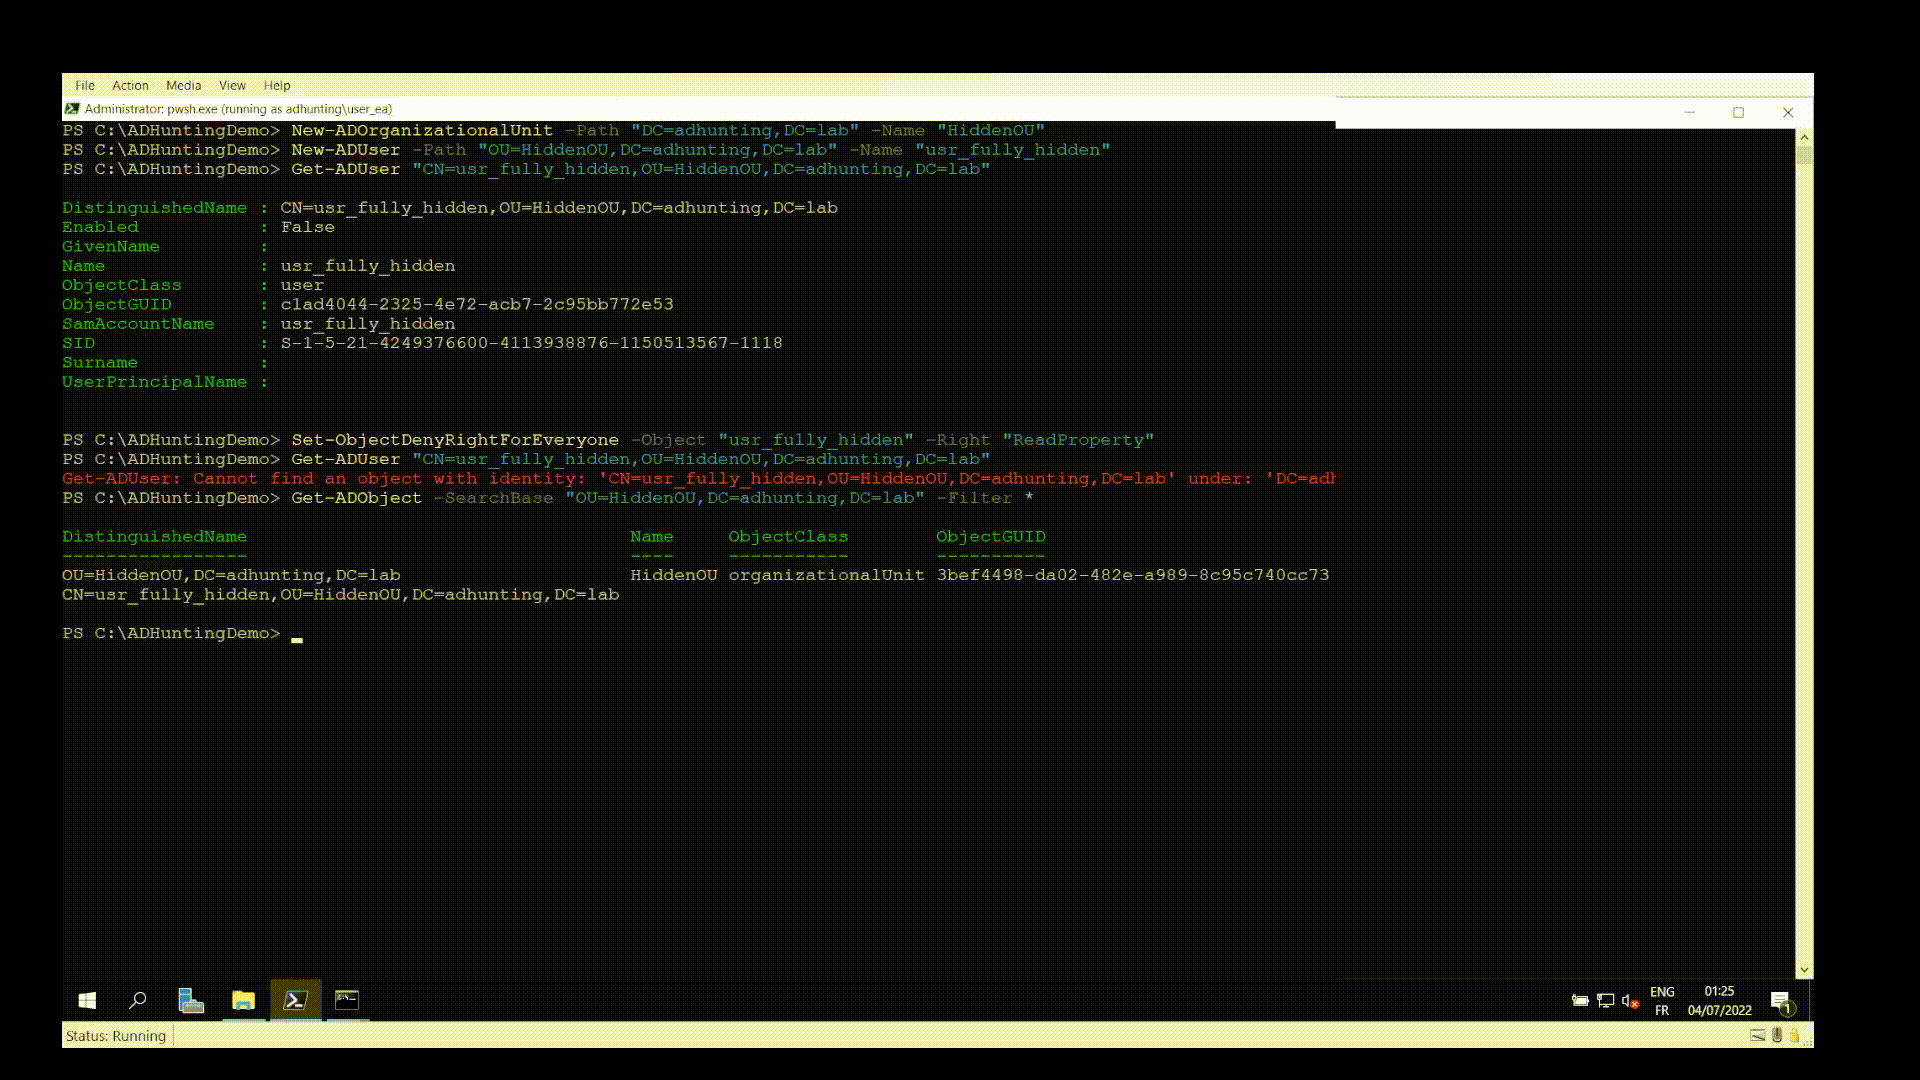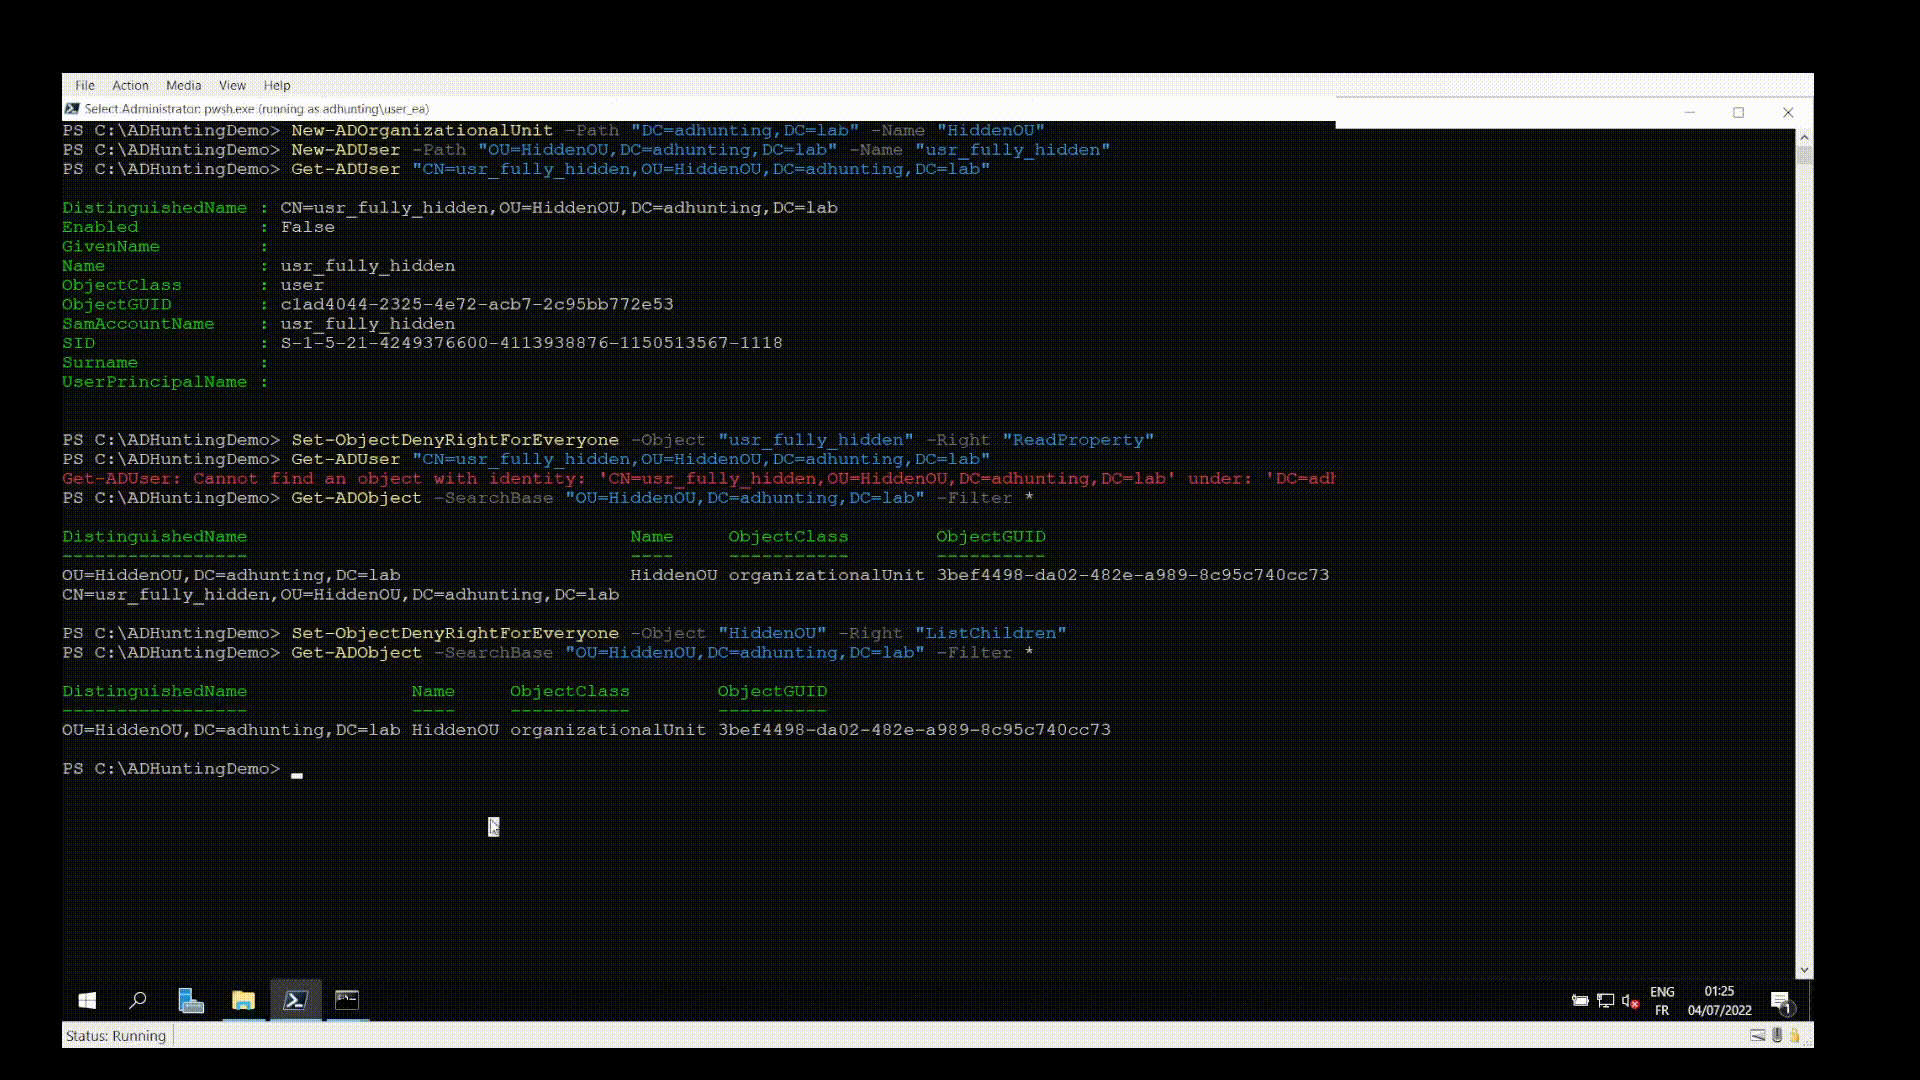 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 xforcered/scmkit
Source Code Management Attack Toolkit
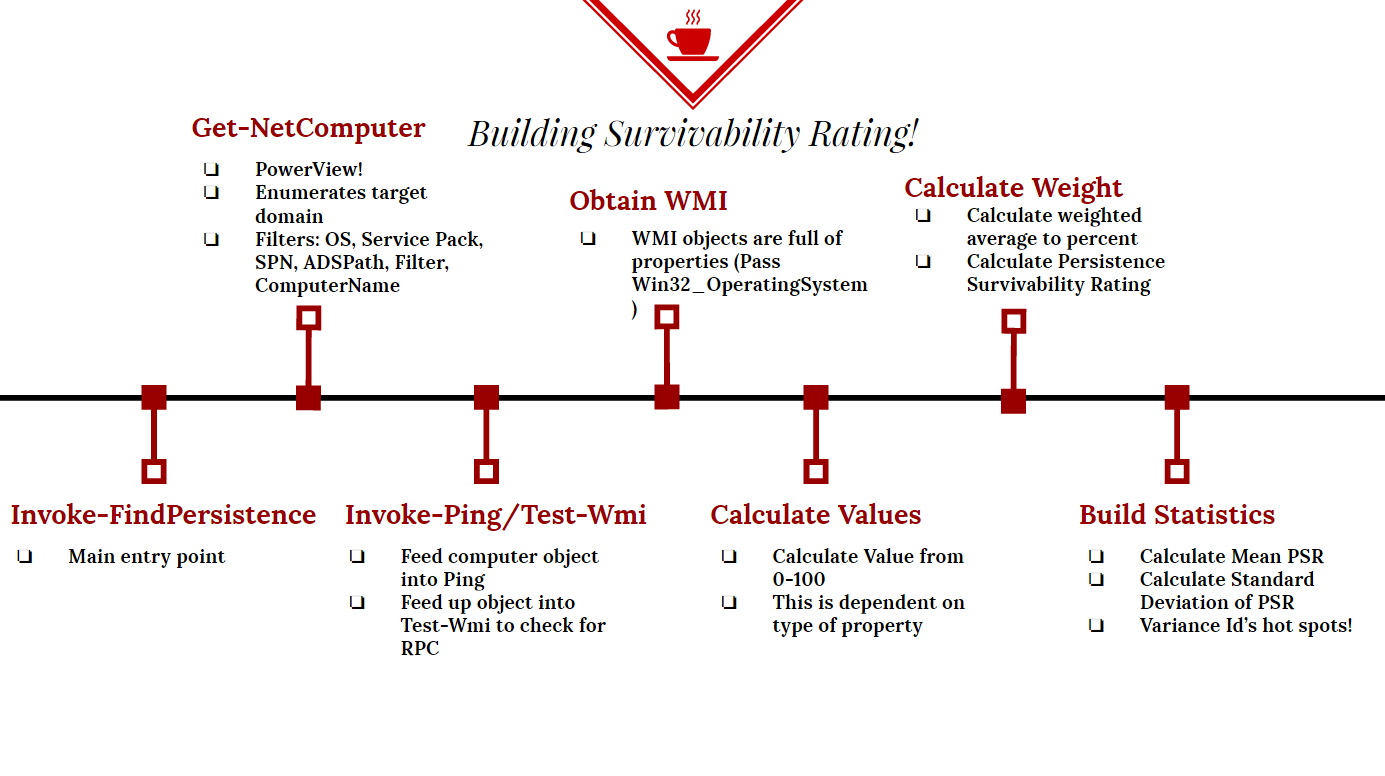 killswitch-gui/persistence-survivability
Powershell Persistence Locator
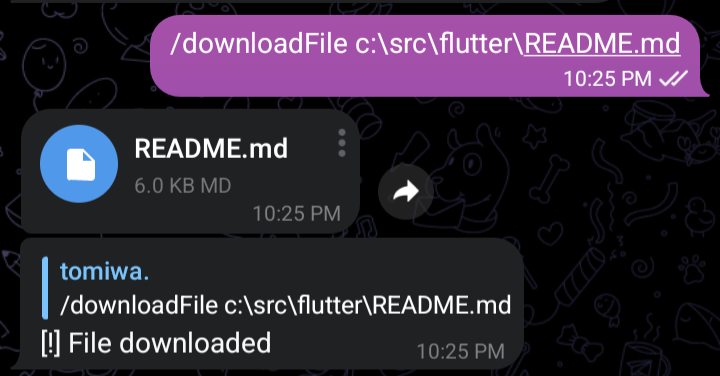 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 al1ex/pentest-command
Pentest-Command
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit