redpill
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
defensive-toolsinformation-gatheringlateral-movement+6
r00t-3xp10it/redpillAssist reverse tcp shells in post-exploration tasks
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 qazeer/farsightad
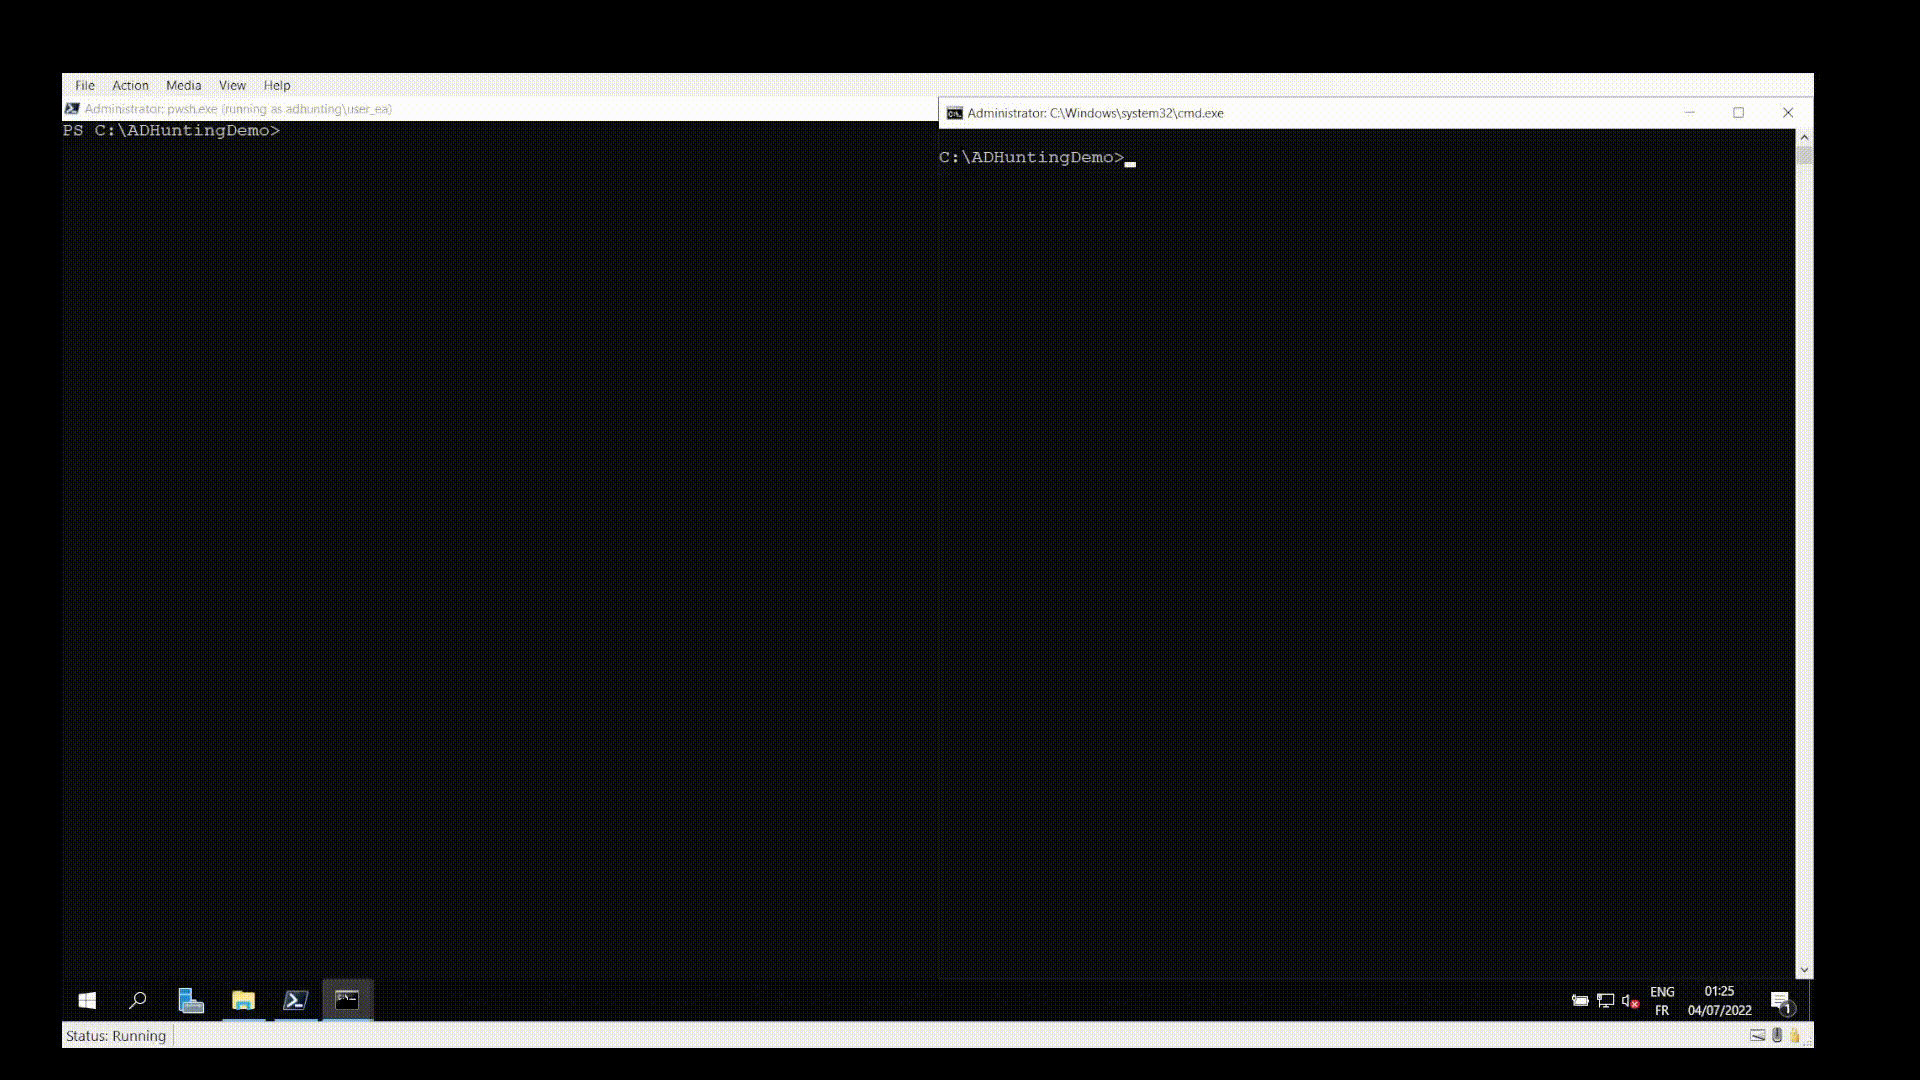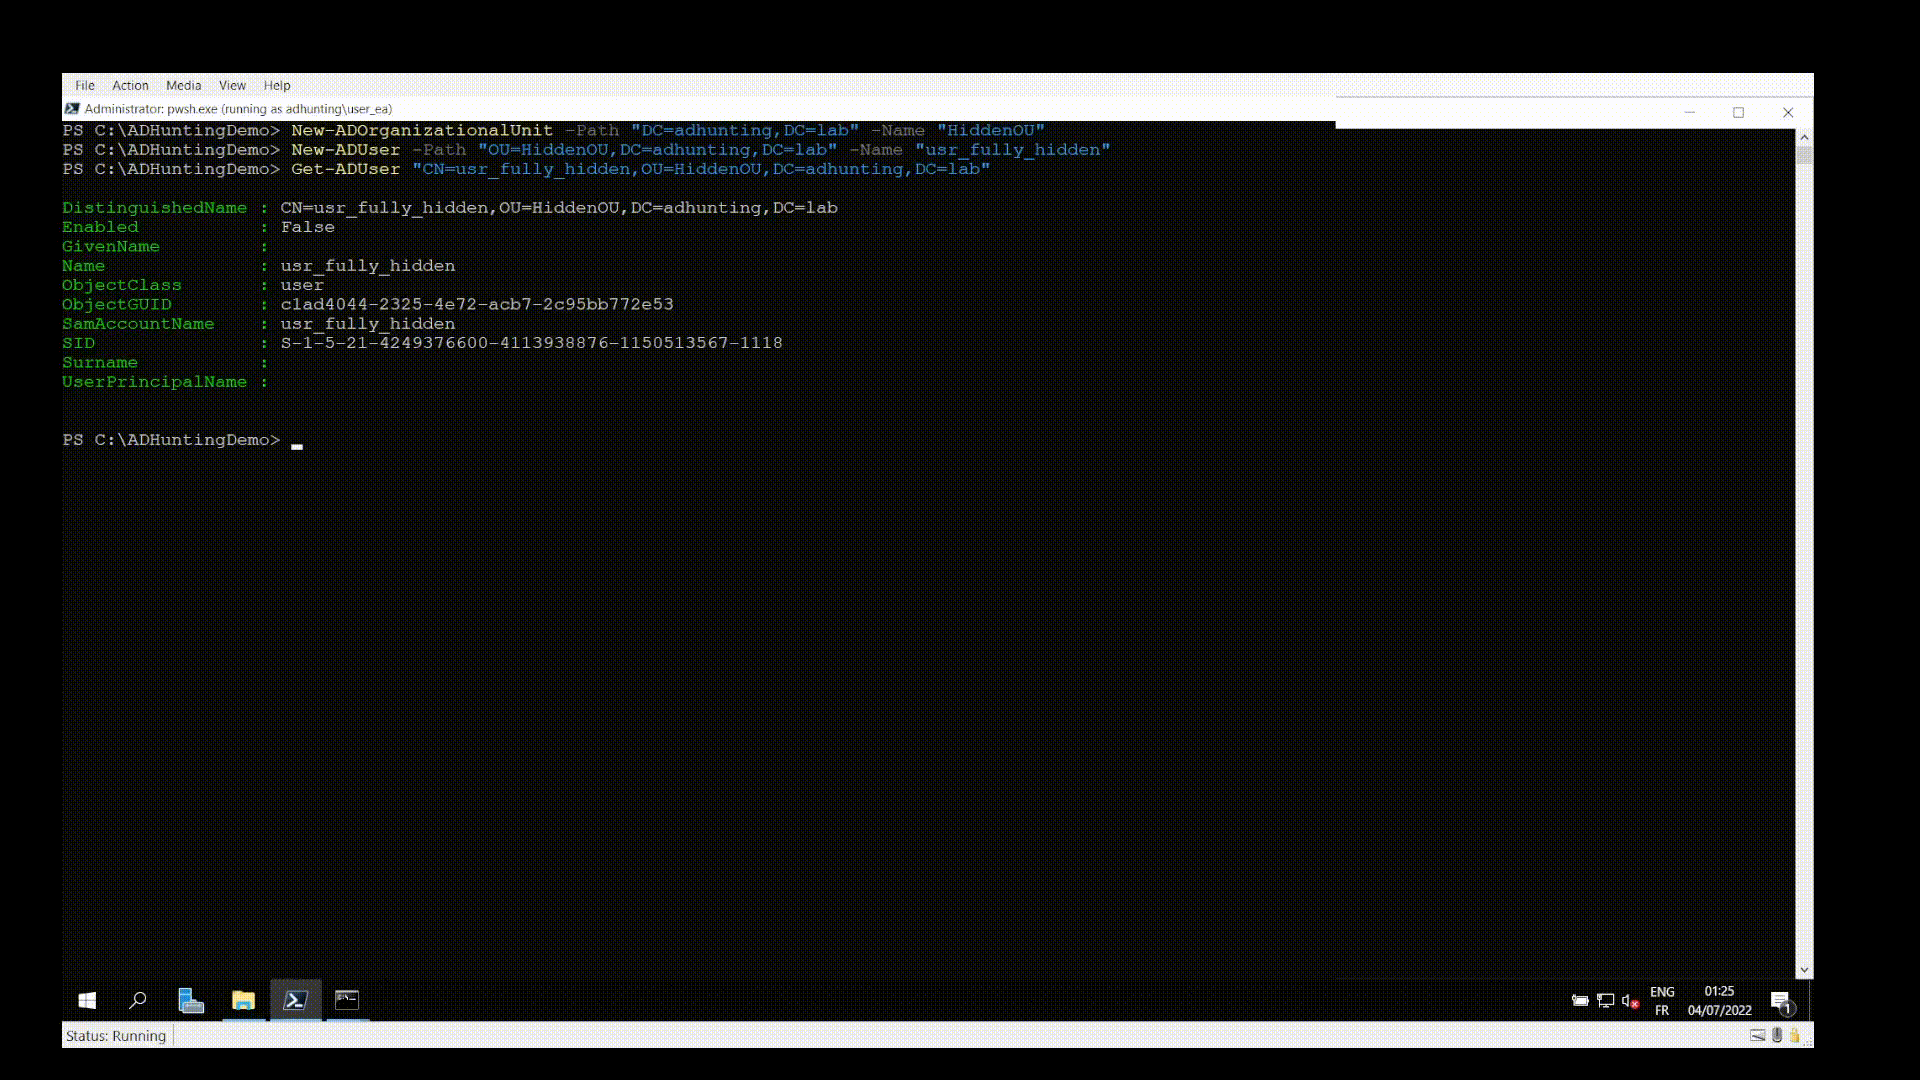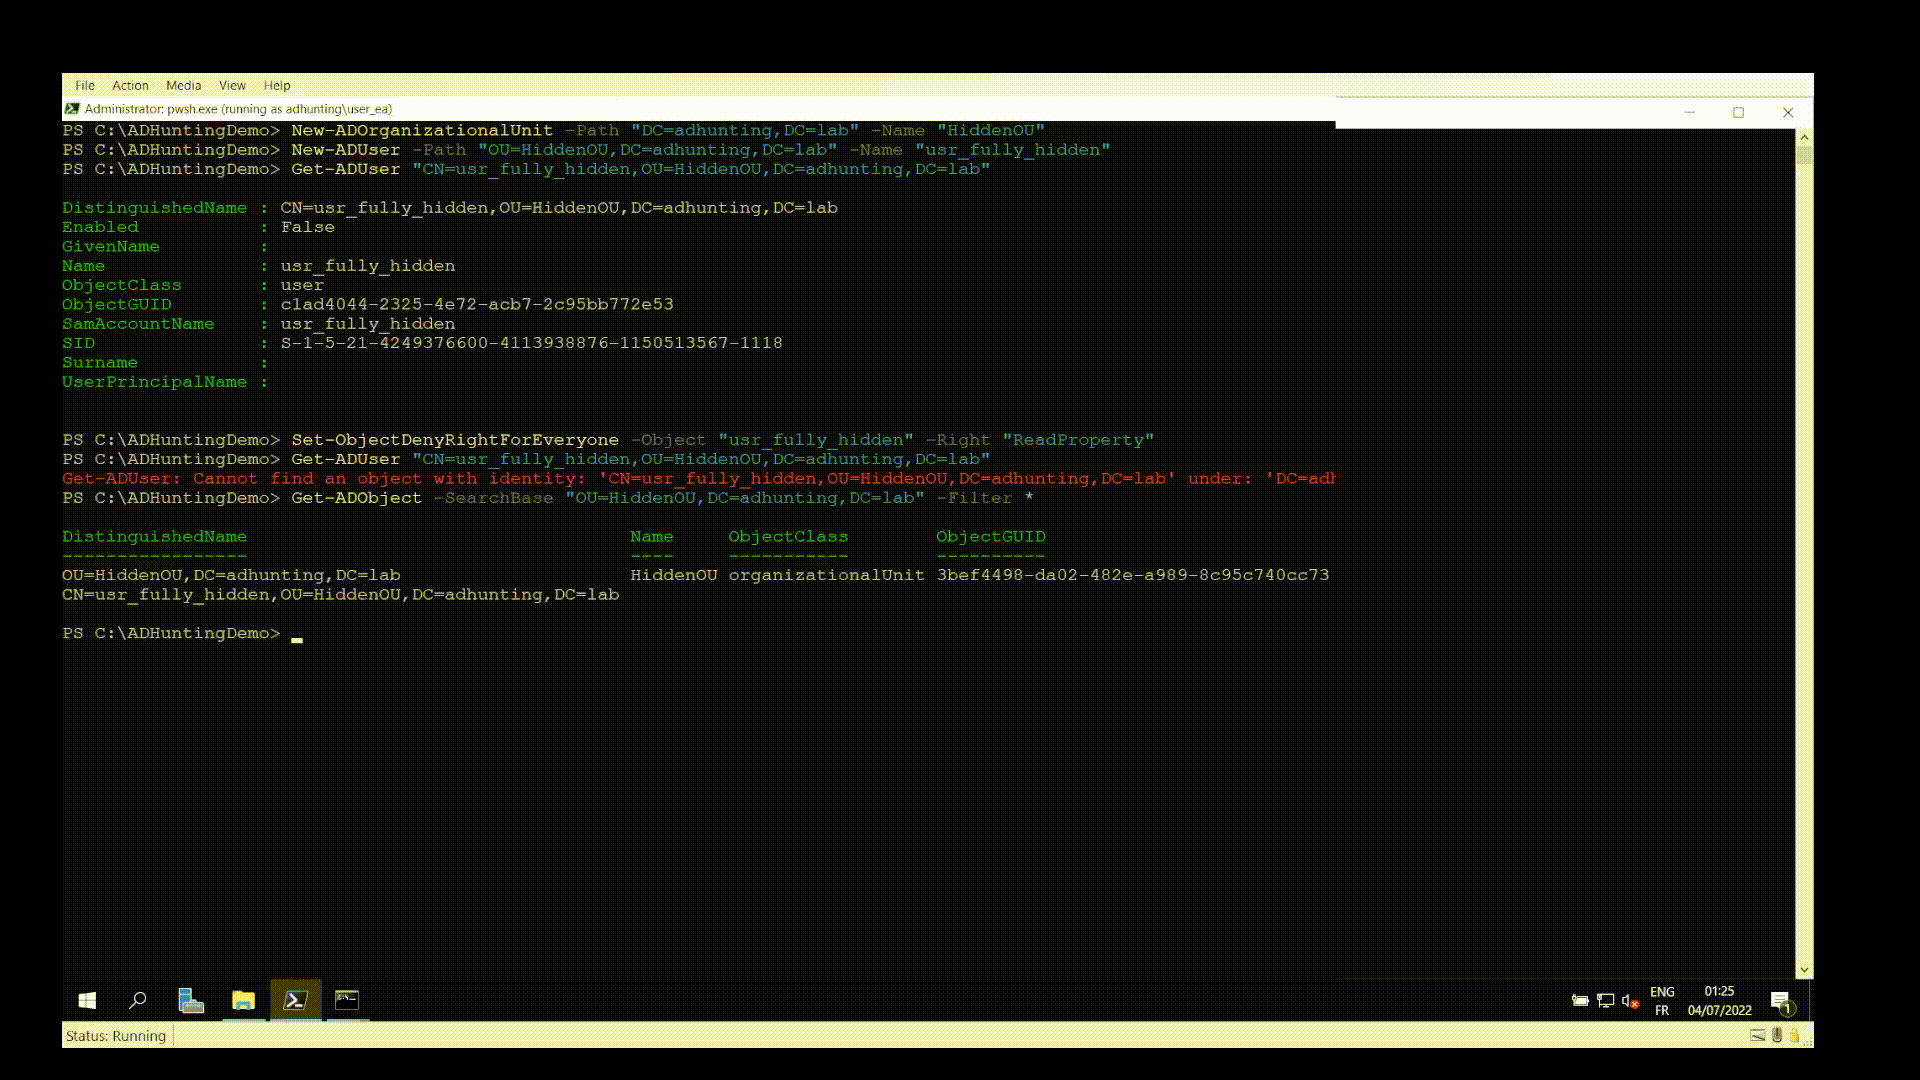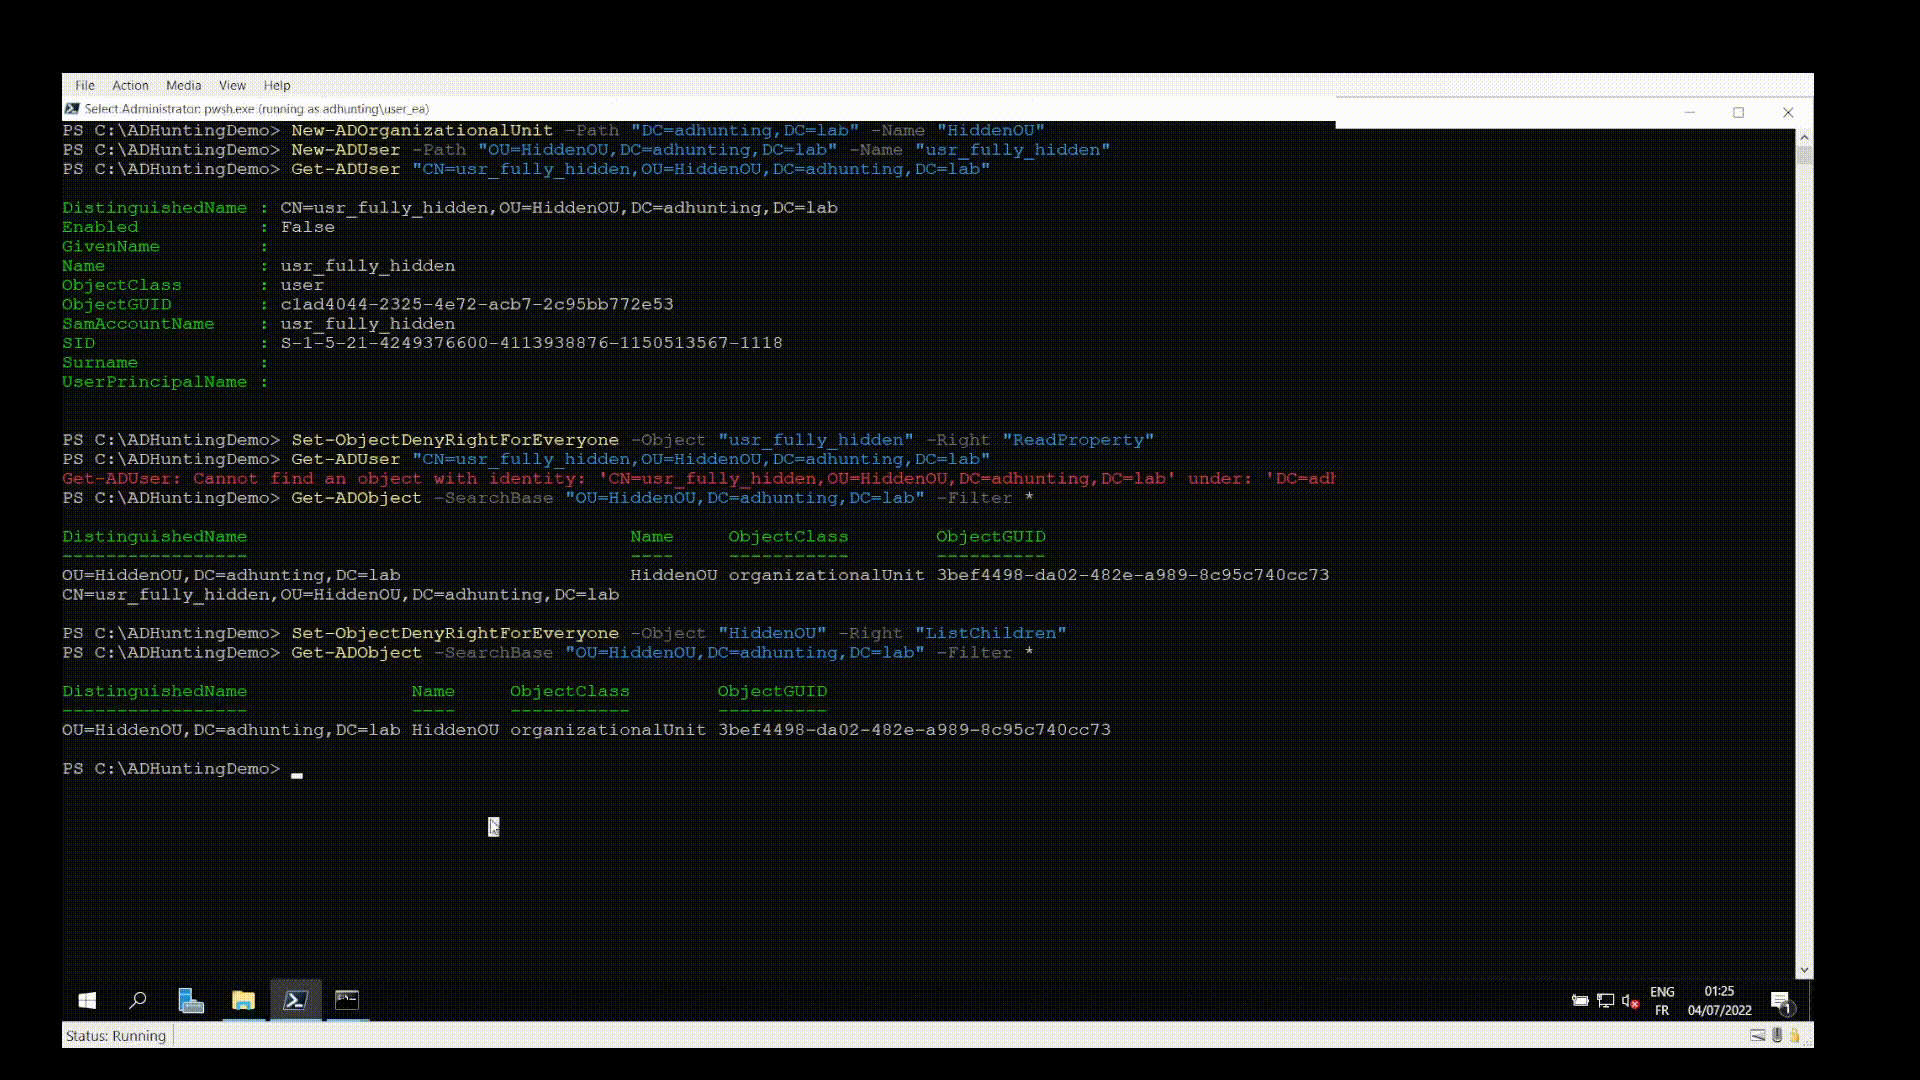
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 xforcered/scmkit
Source Code Management Attack Toolkit
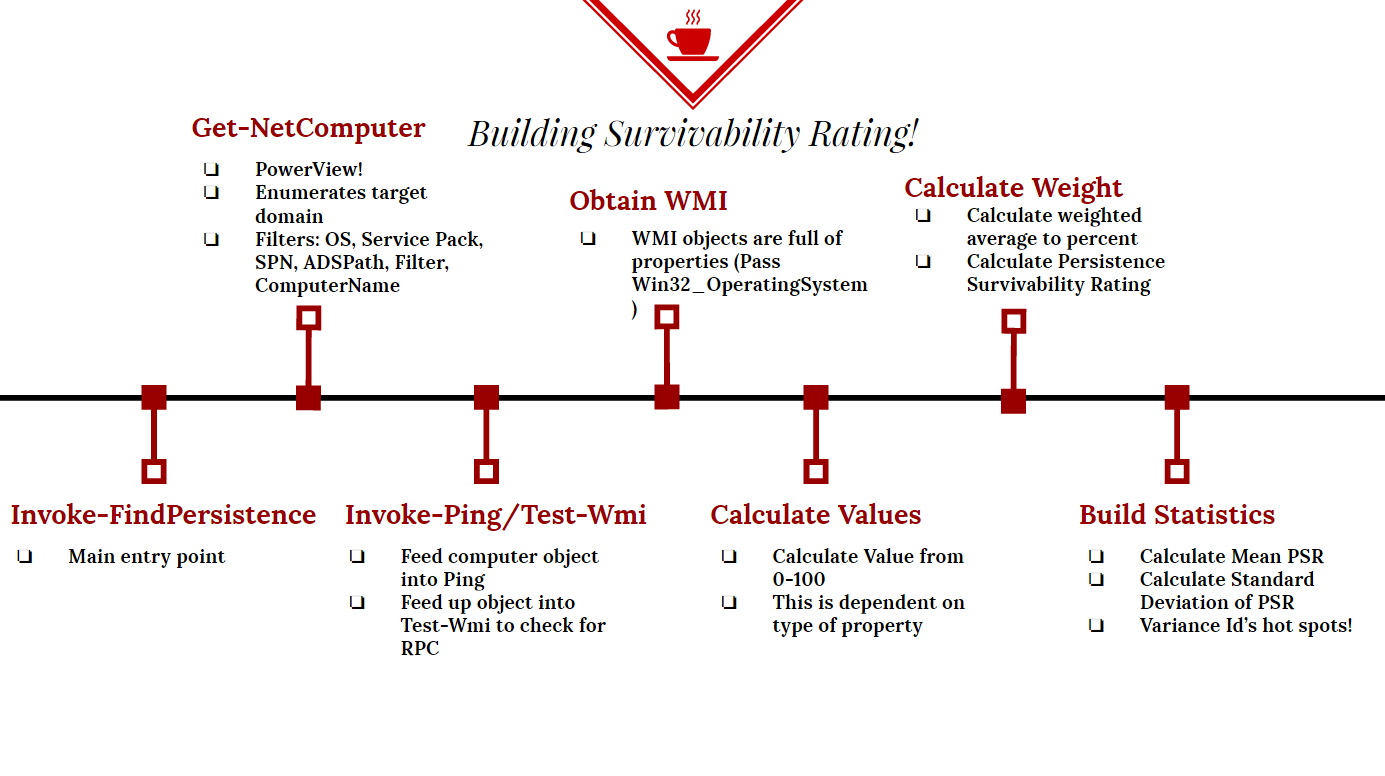 killswitch-gui/persistence-survivability
Powershell Persistence Locator
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
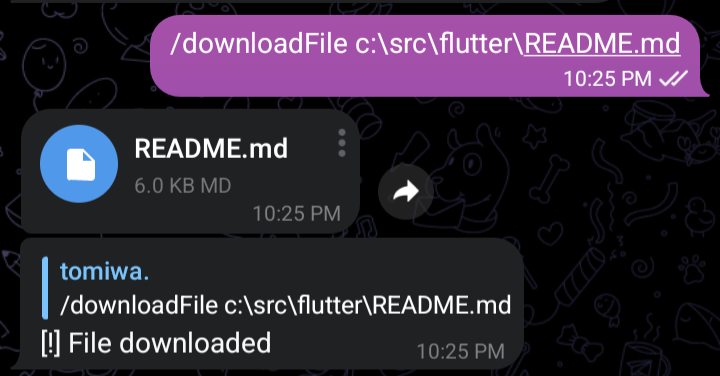 tomiwa-ot/telegram-c2
Control a system remotely via telegram
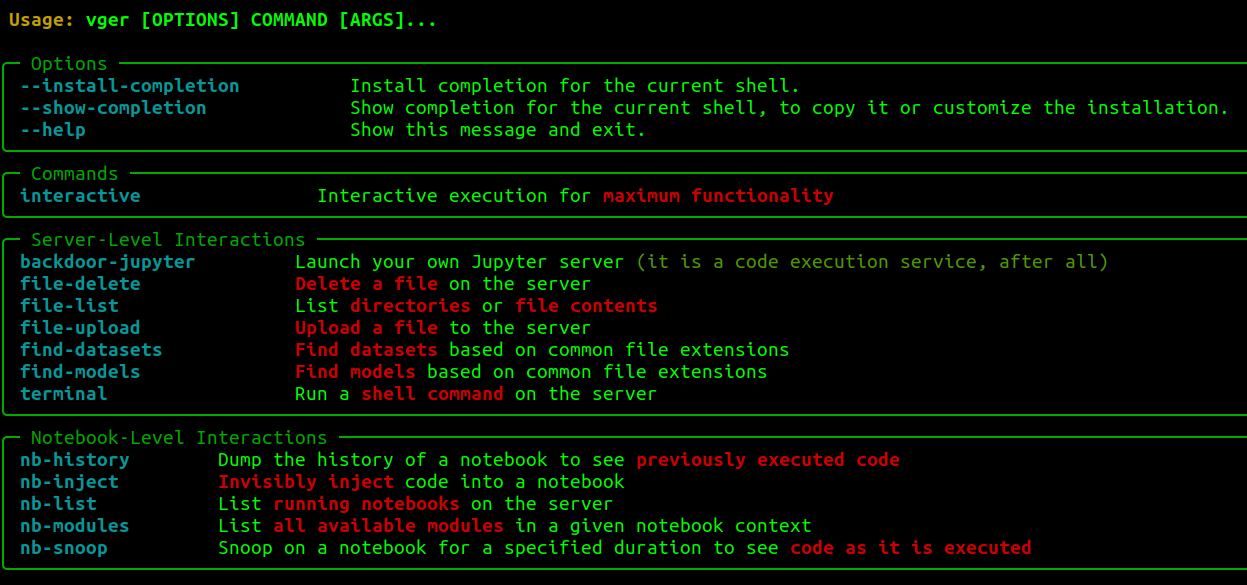 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 synacktiv/extloader
A chromium extension exploitation toolkit
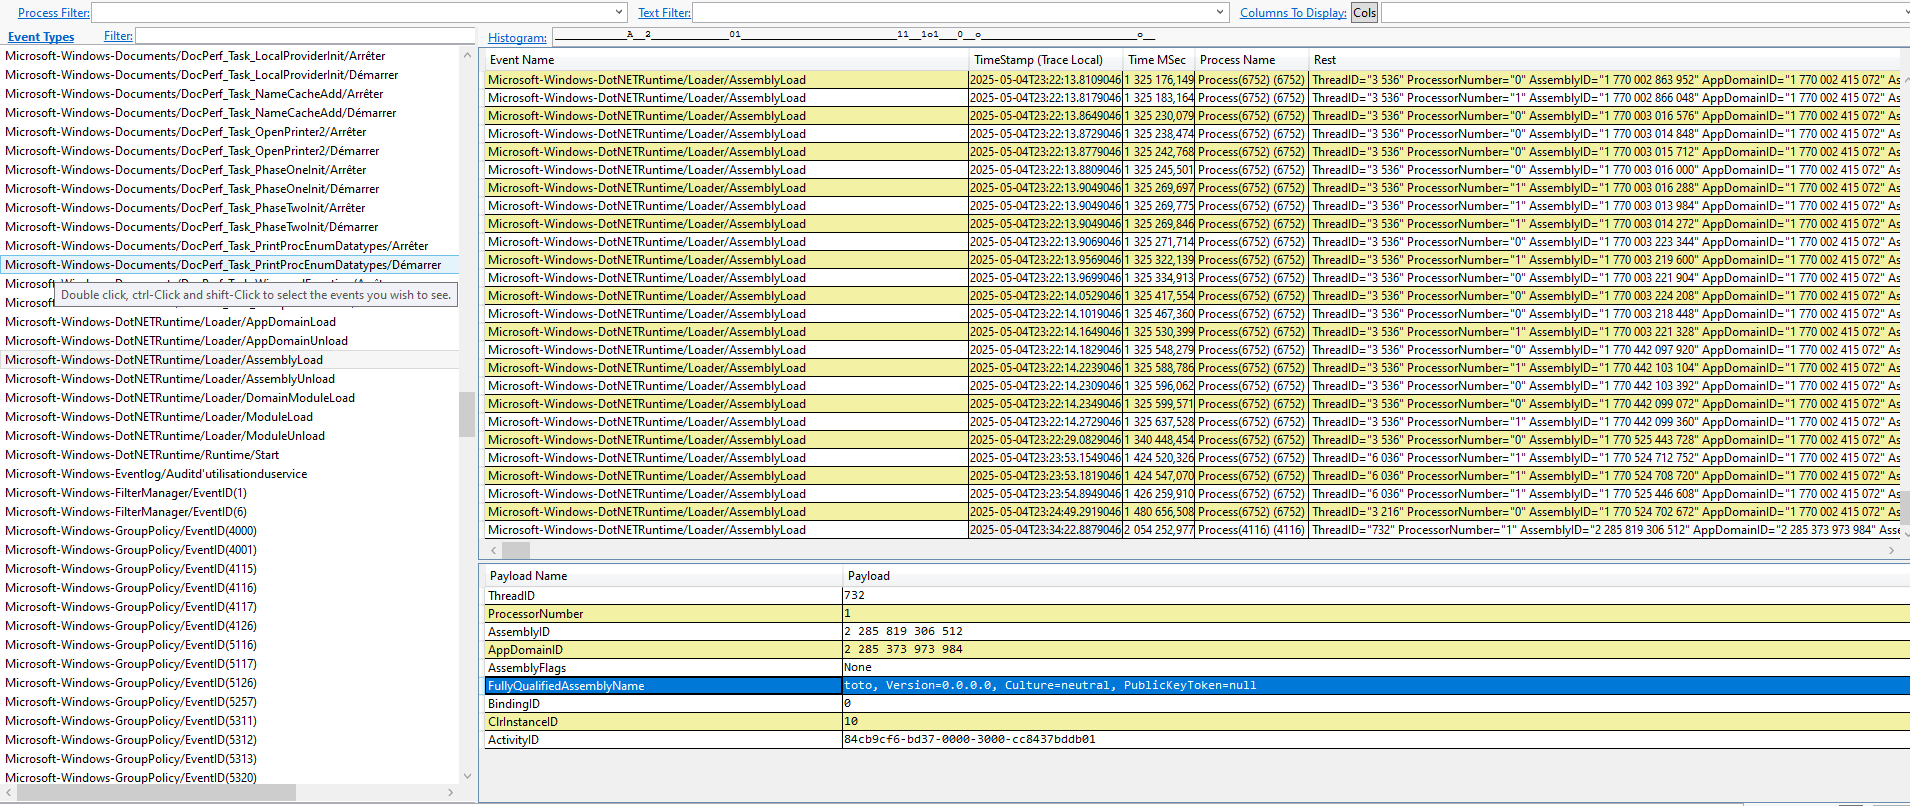 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
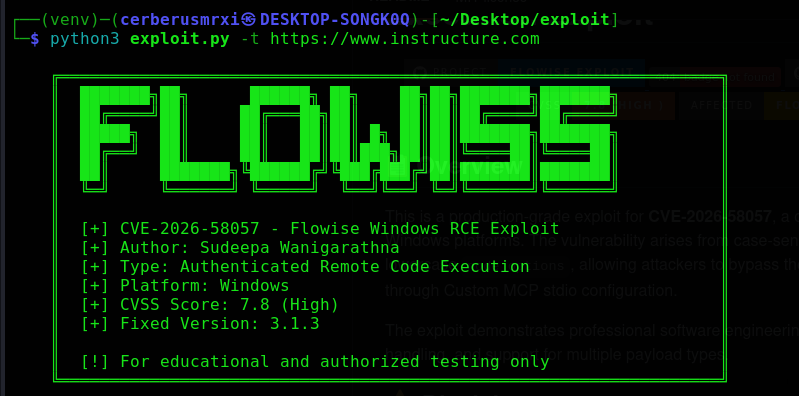 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…