
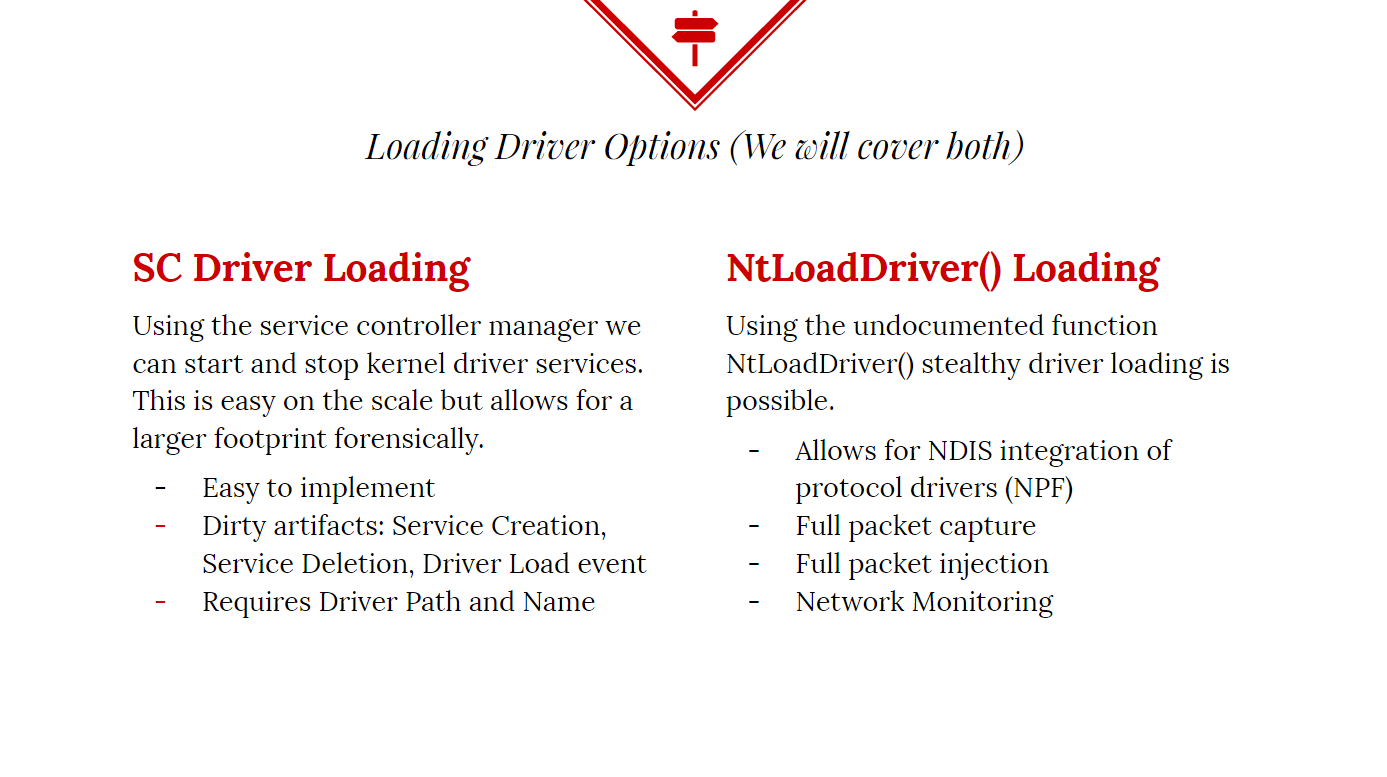
HotLoad-Driver
 killswitch-gui/hotload-driver
C++
exploitationpayload-developmentpersistence-mechanisms+3
8810 years ago
killswitch-gui/hotload-driverC++
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)