
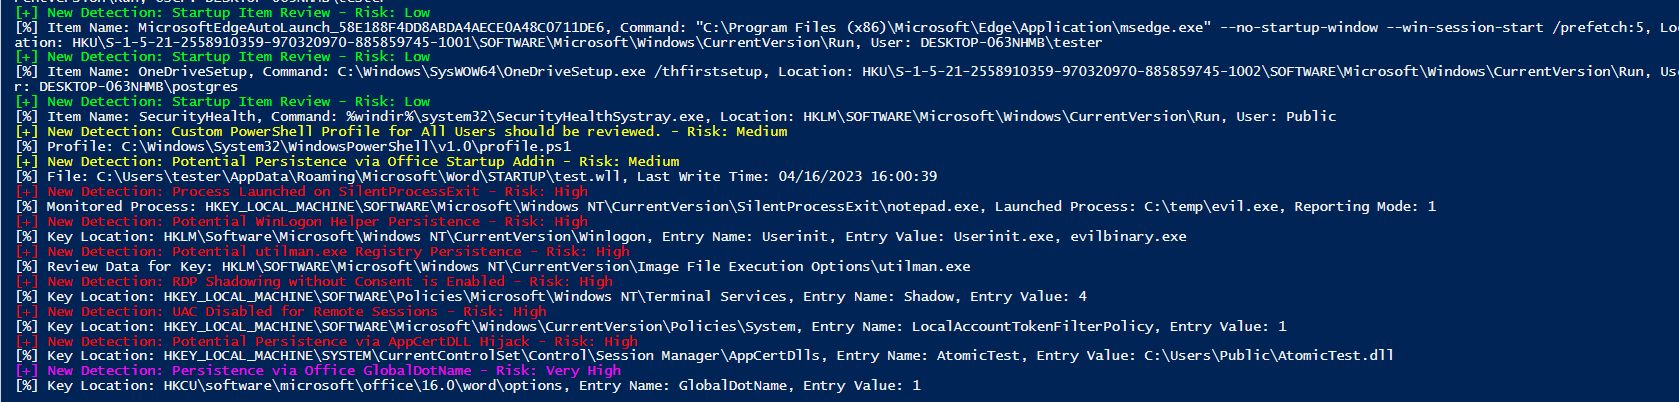
Trawler
 joeavanzato/trawler
PowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
defensive-toolsdigital-forensicsforensics+2
3411 year ago
joeavanzato/trawlerPowerShell script helping Incident Responders discover potential adversary persistence mechanisms.
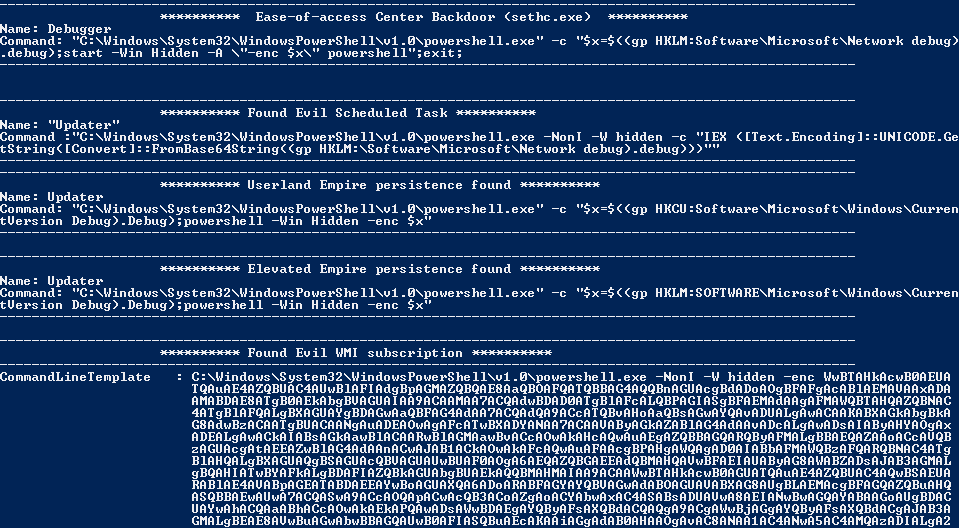 n00py/norknork
Powershell Empire Persistence finder
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
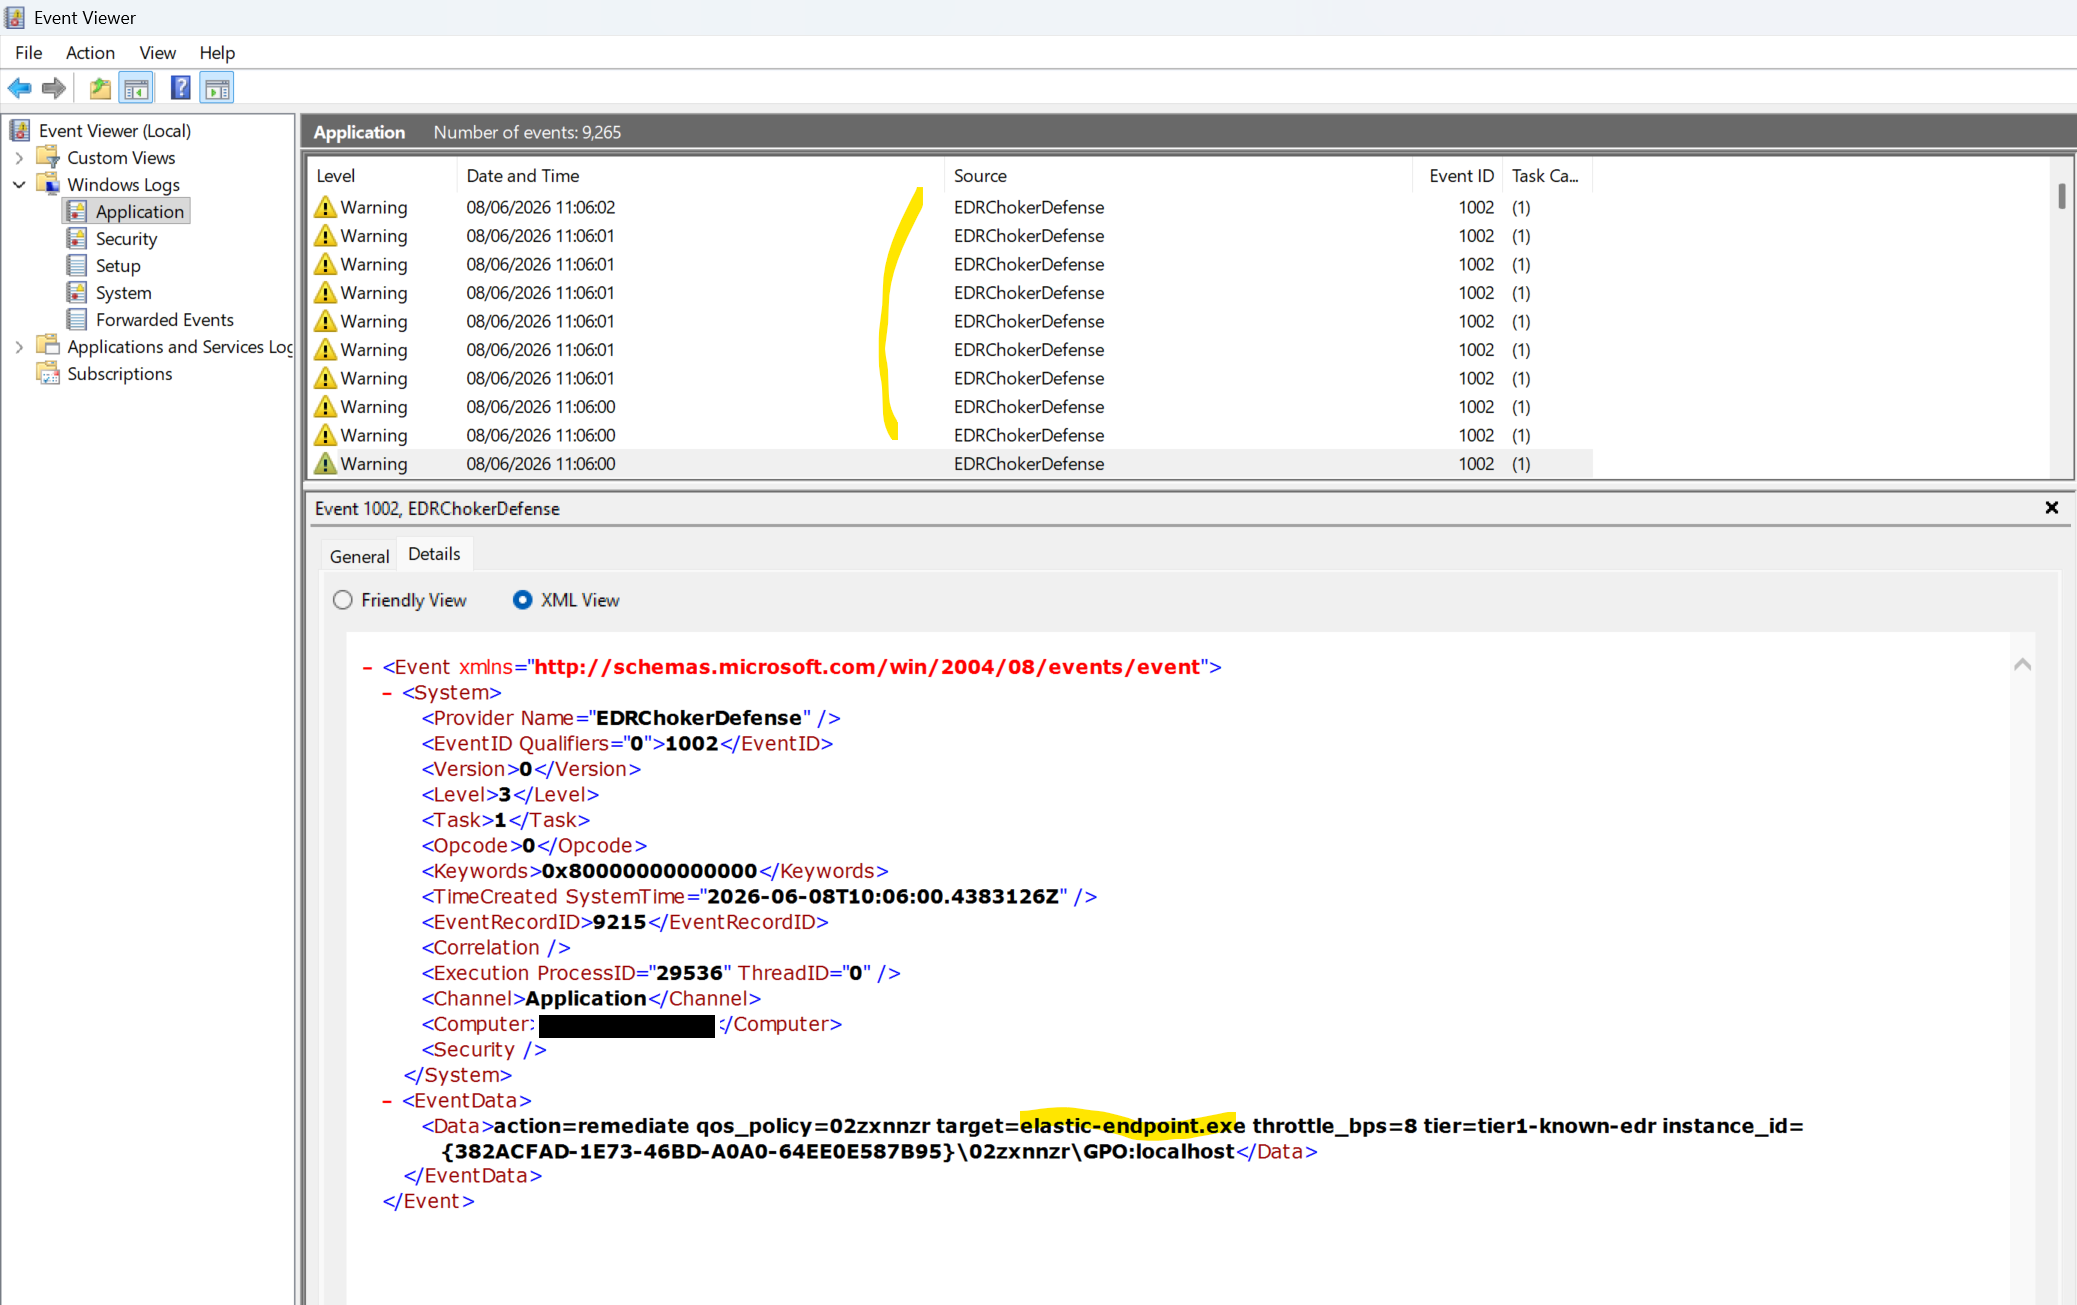 sbousseaden/edrunchoker
EDRUnChoker - fileless WMI defense that removes EDRChoker QoS throttling policies
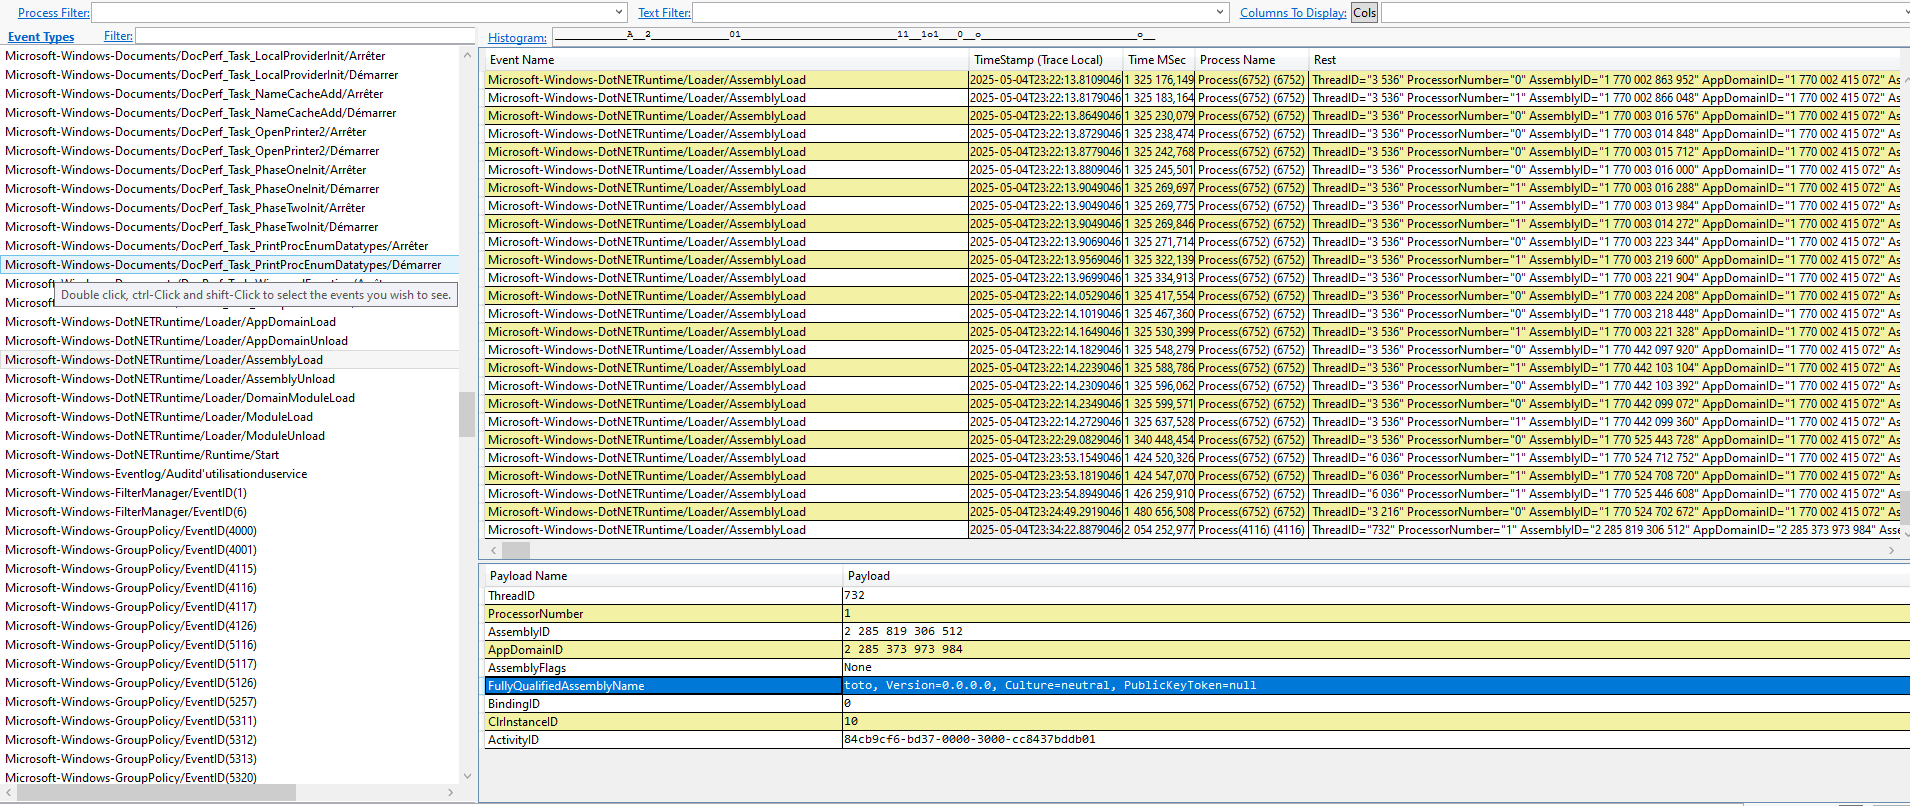 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints
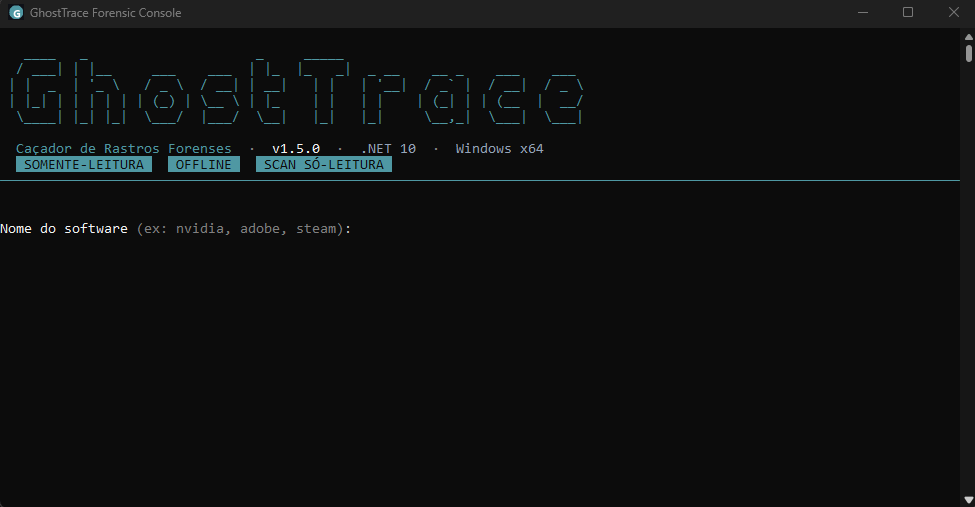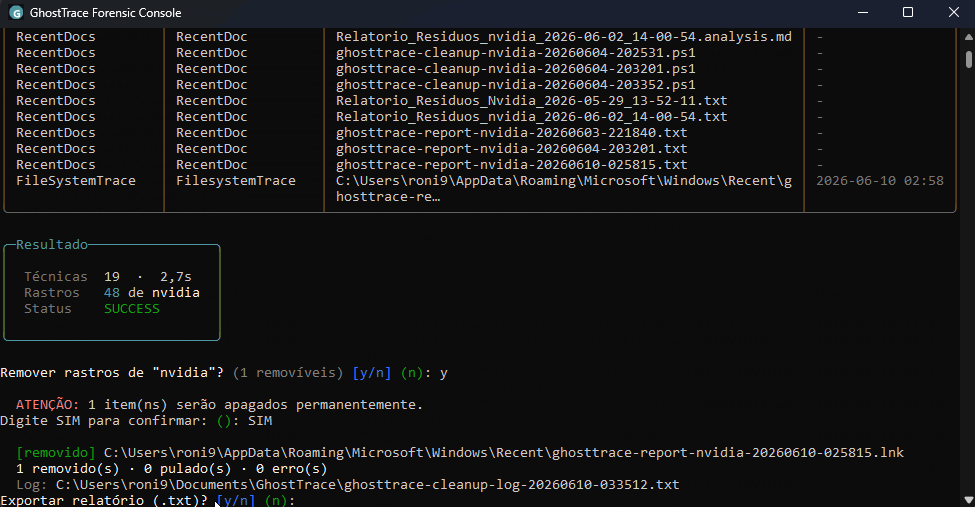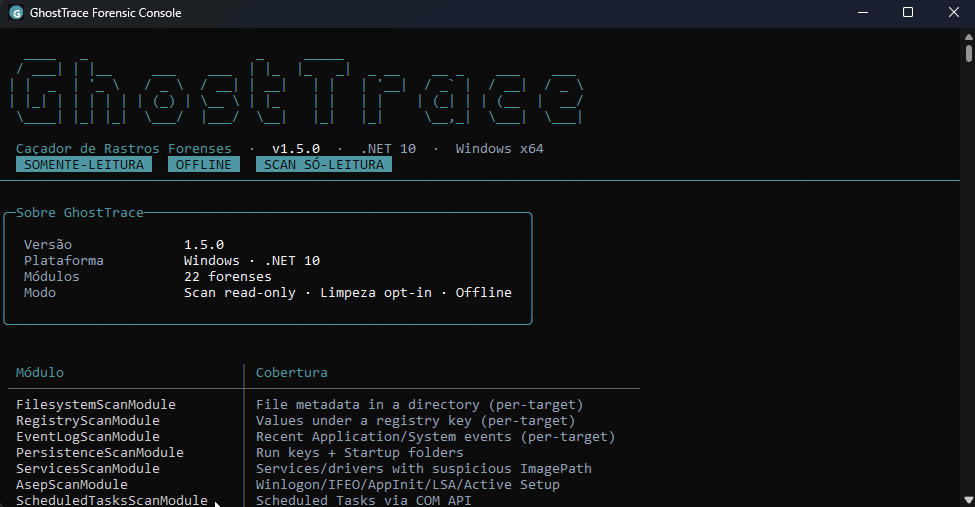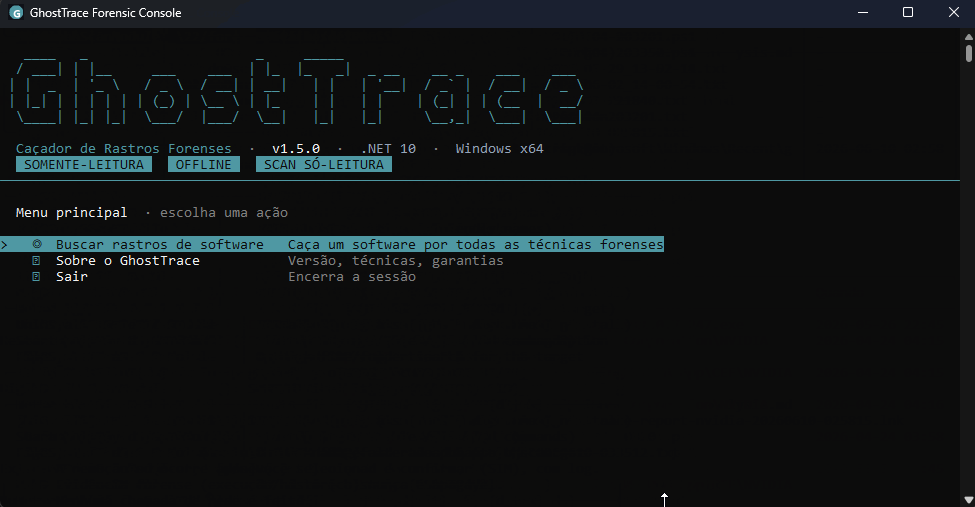 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 fastmo/cve-2022-28672
CVE-2022-28672 Vulnerabilidad Foxit PDF Reader - UaF - RCE - JIT Spraying