Fsociety-CVE-2024-0670-CheckMK-LPE

🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.

🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.

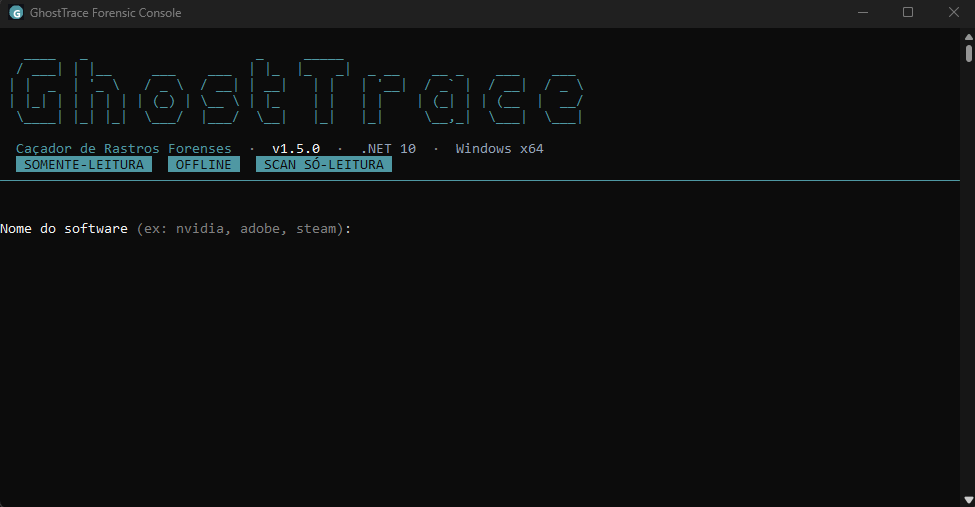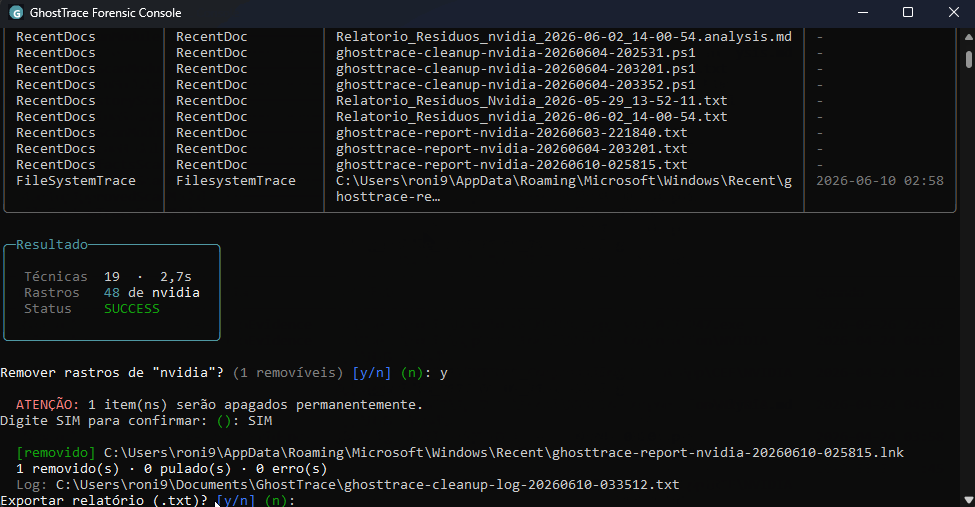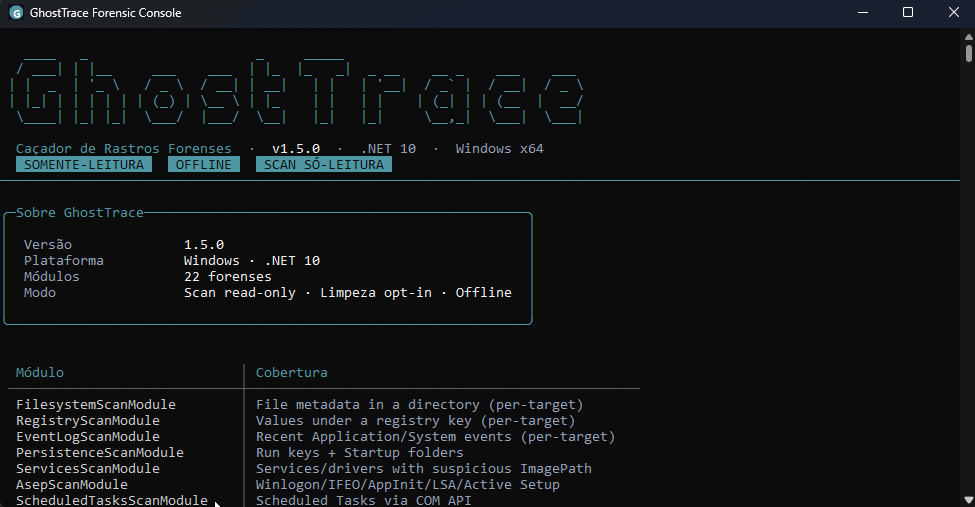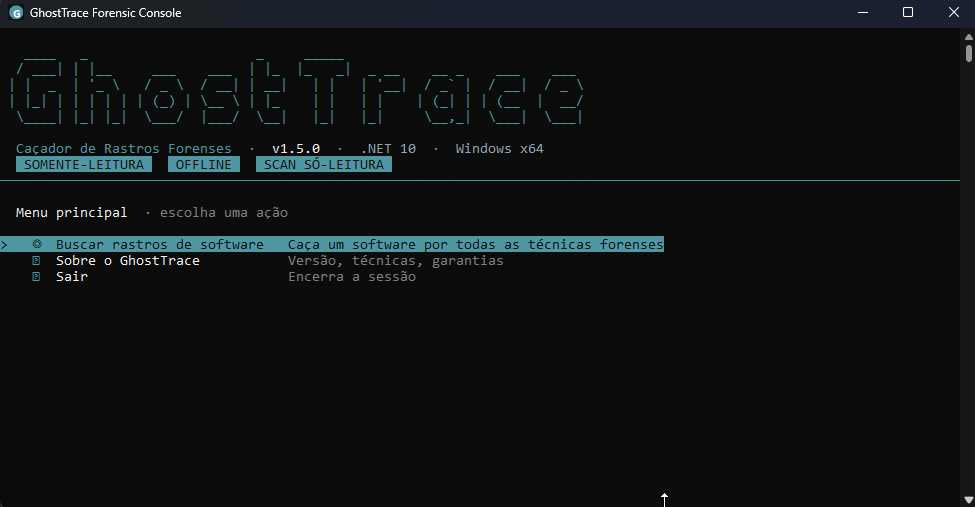
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

Exploitation for CVE-2024-49019

POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE

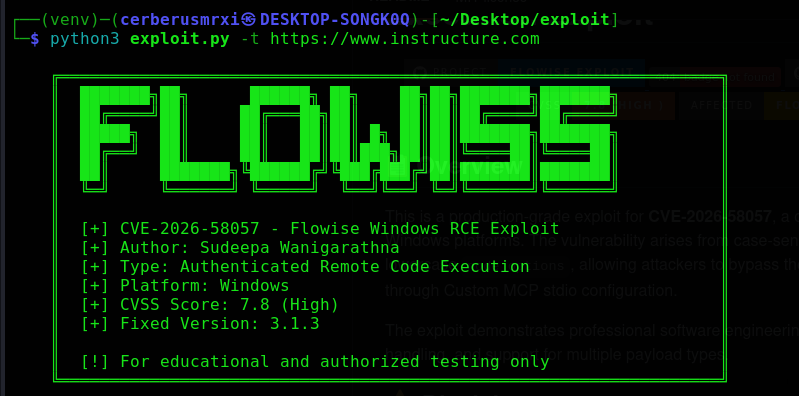
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.

Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…

CVE-2026-33017 - Langflow Unauthenticated RCE Exploit

Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Just poc for CVE 2024-54085

Herramienta avanzada de explotación transversal de ruta de WinRAR para CVE-2025-8088

Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…

Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…

[AI-assisted] Root method for Lenovo IdeaTab A1000G (MT8317, kernel 3.4.0, Android 4.1) via CVE-2016-5195 (Dirty COW)

Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence