Windows-Defender-Security-Auditor-CVE-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

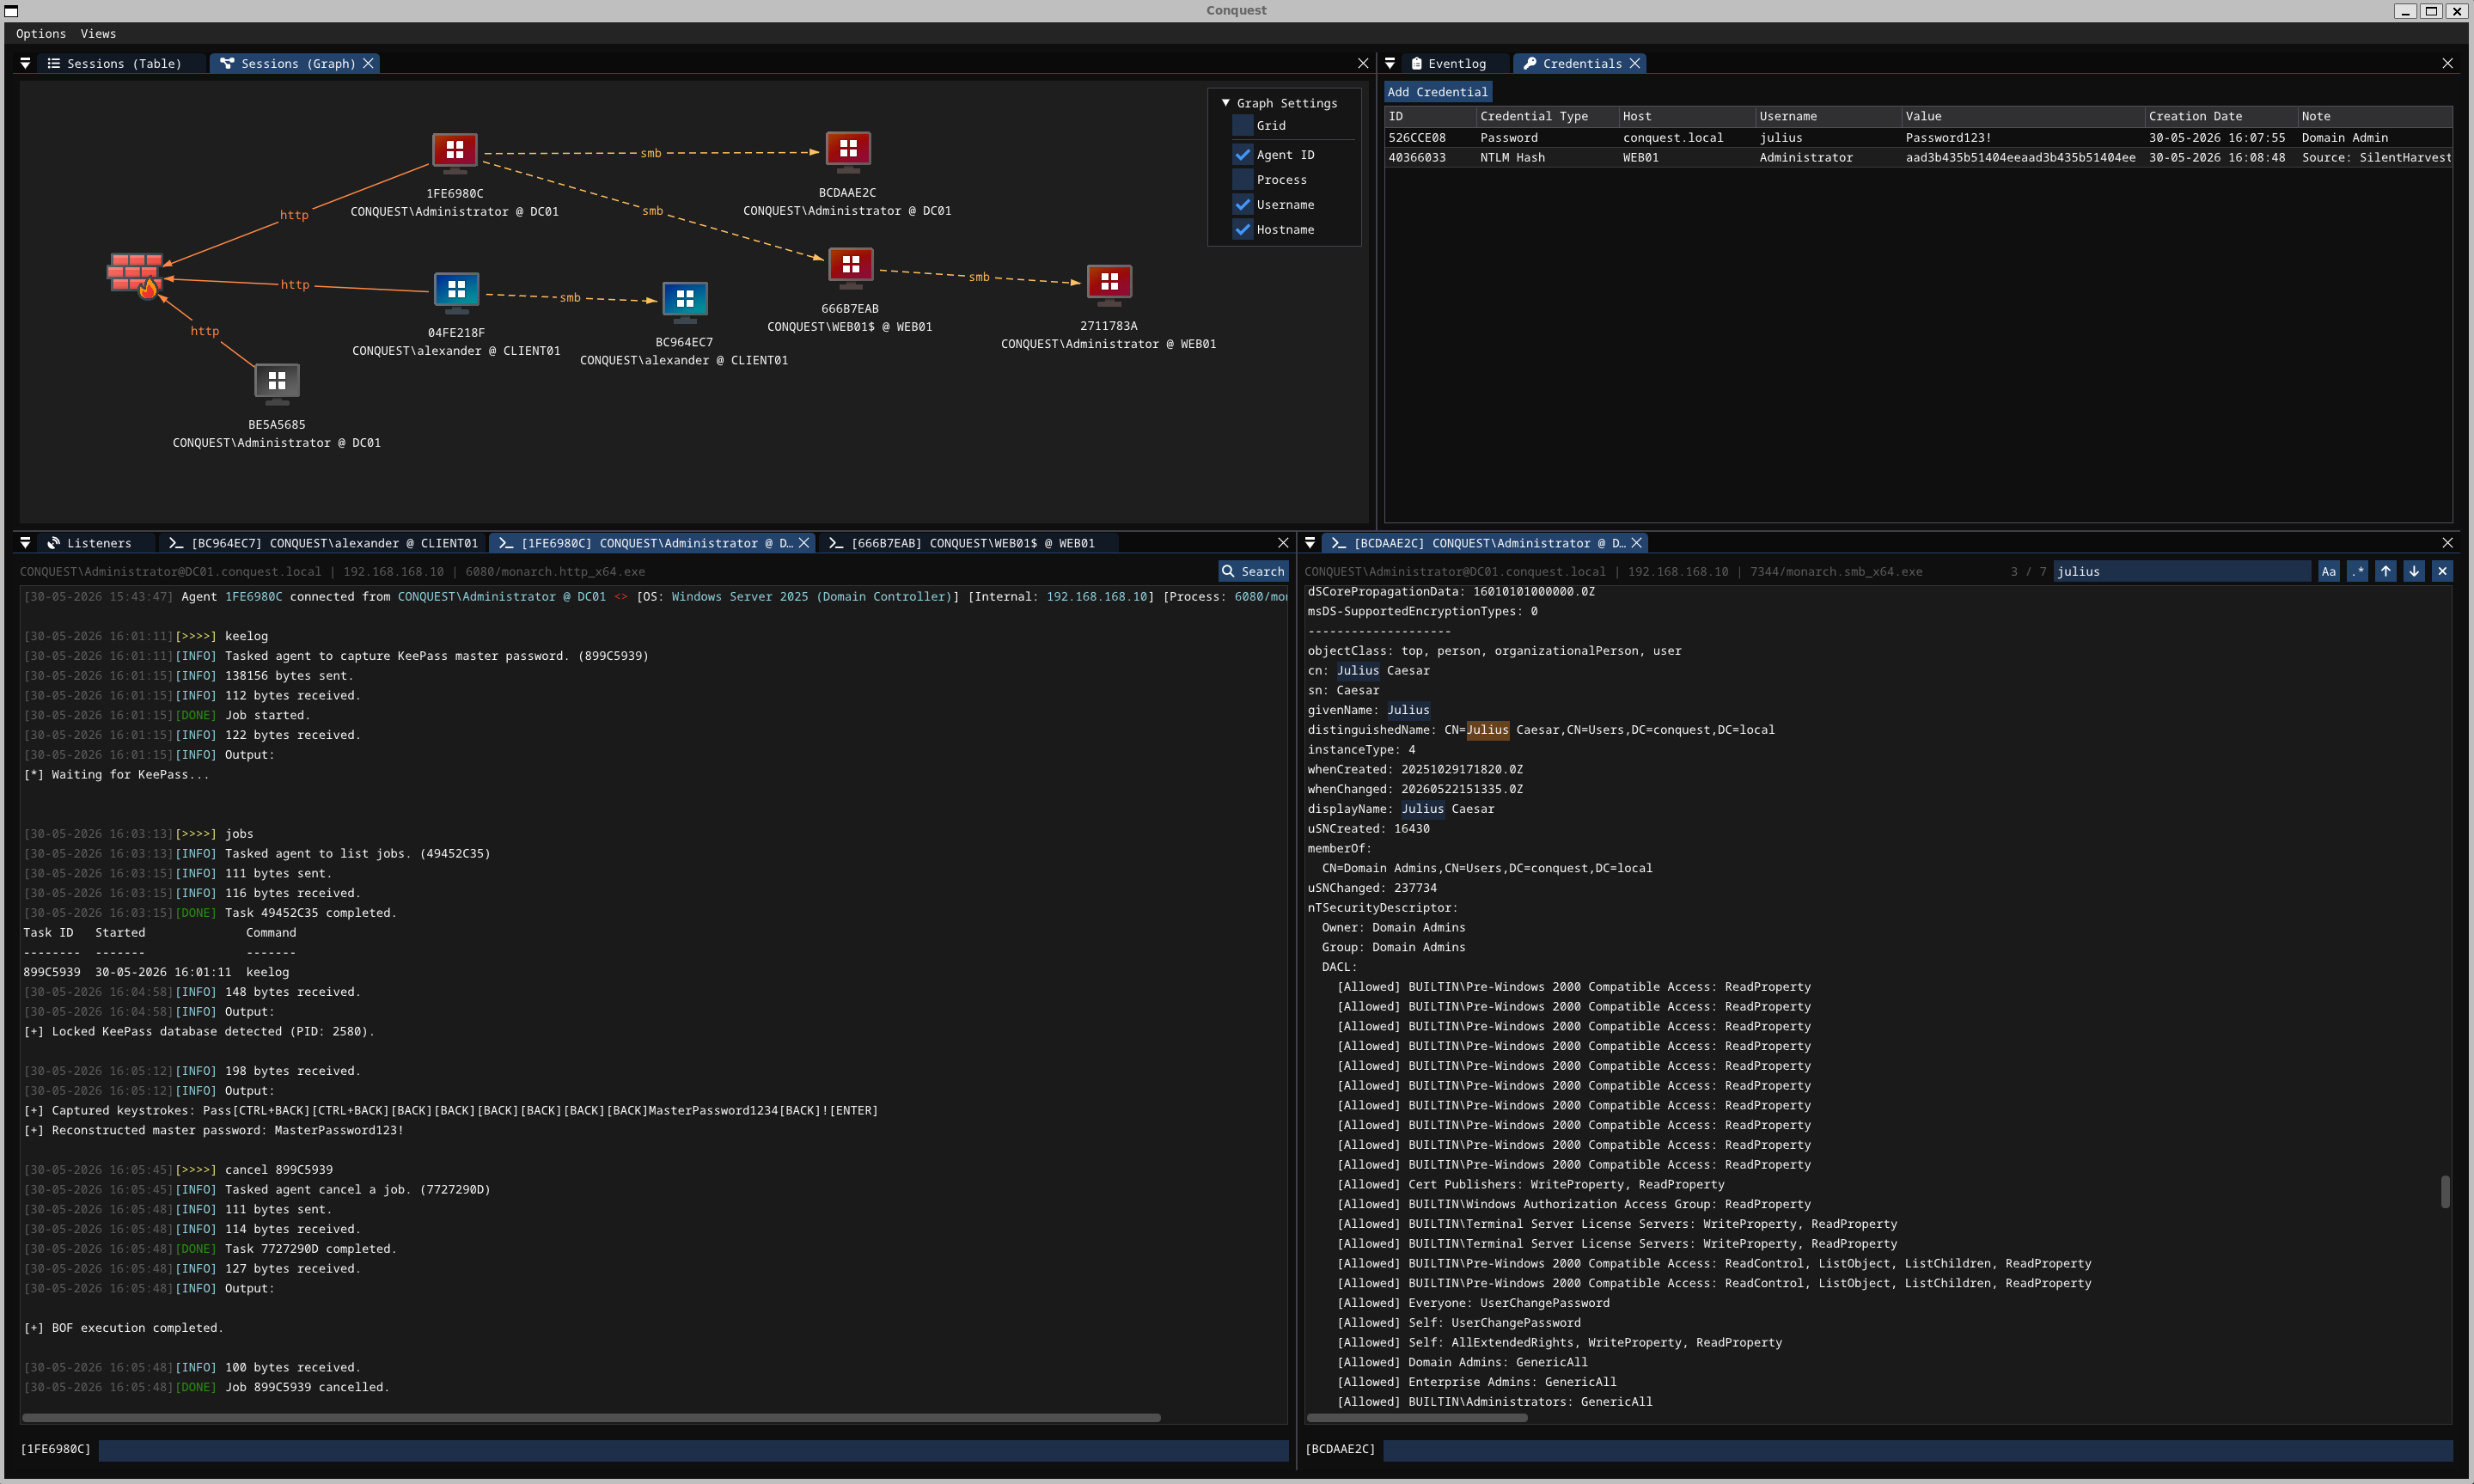
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…

Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc

Code developed to steal certain browser config files (history, preferences, etc)

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

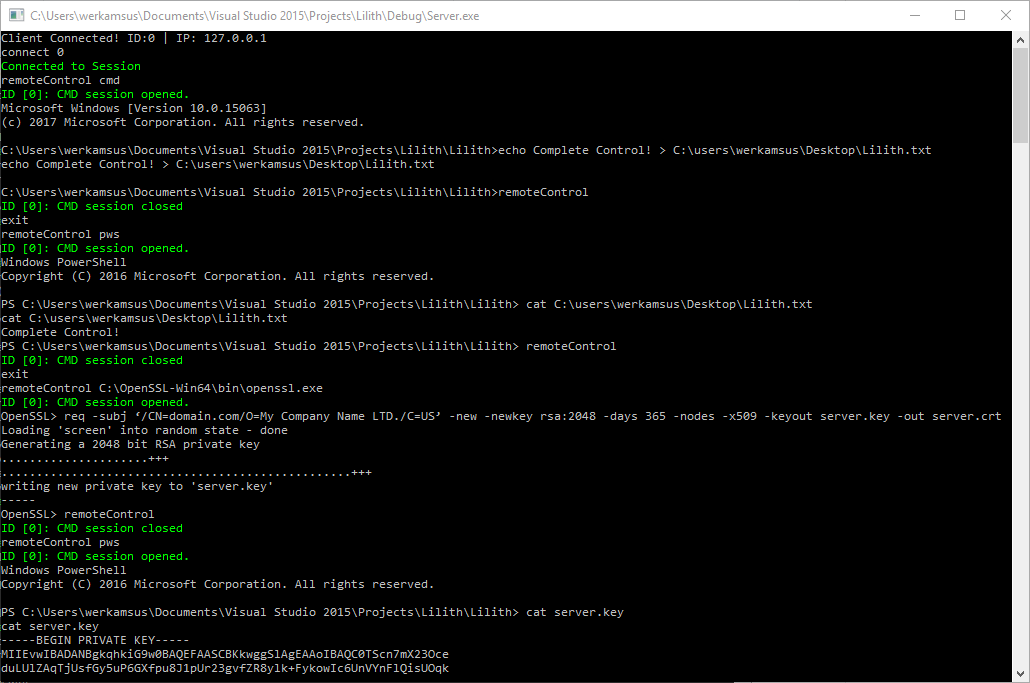
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++