

Active-Directory-Exploitation-Cheat-Sheet
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourcesdata-exfiltrationeducation+6
integration-it/active-directory-exploitation-cheat-sheetA cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 thegeekht/loki.rat
Loki.Rat is a fork of the Ares RAT, it integrates new modules, like recording , lockscreen , and locate options. Loki.Rat is a Python Remote Access…
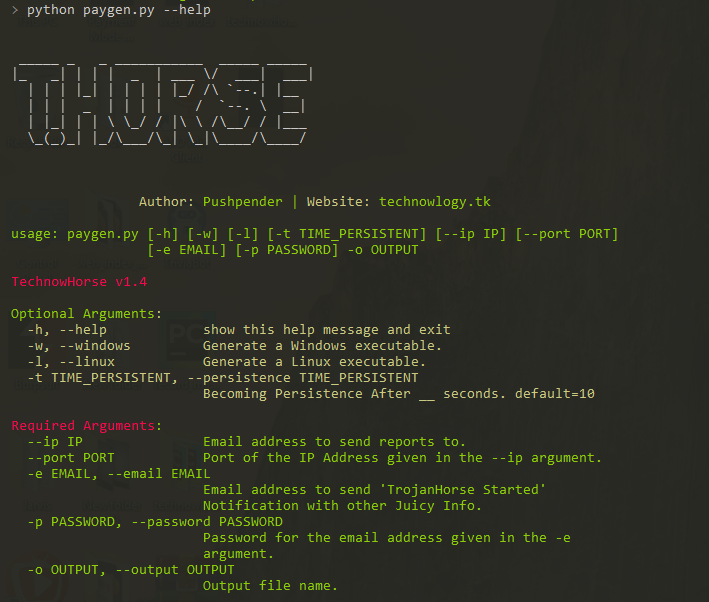 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
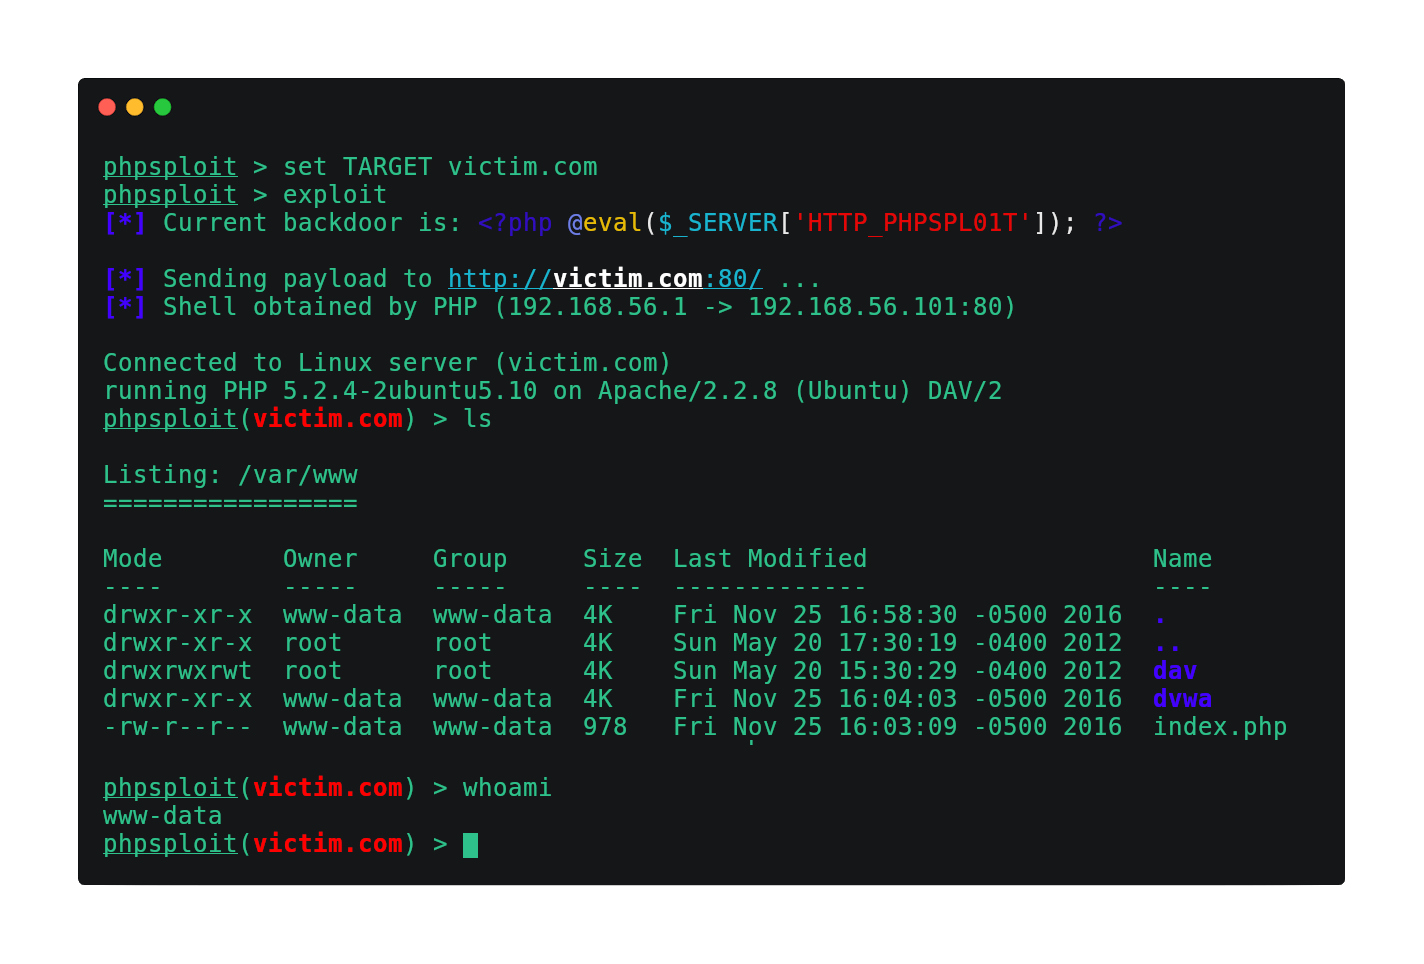 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 nccgroup/winpayloads
Undetectable Windows Payload Generation
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
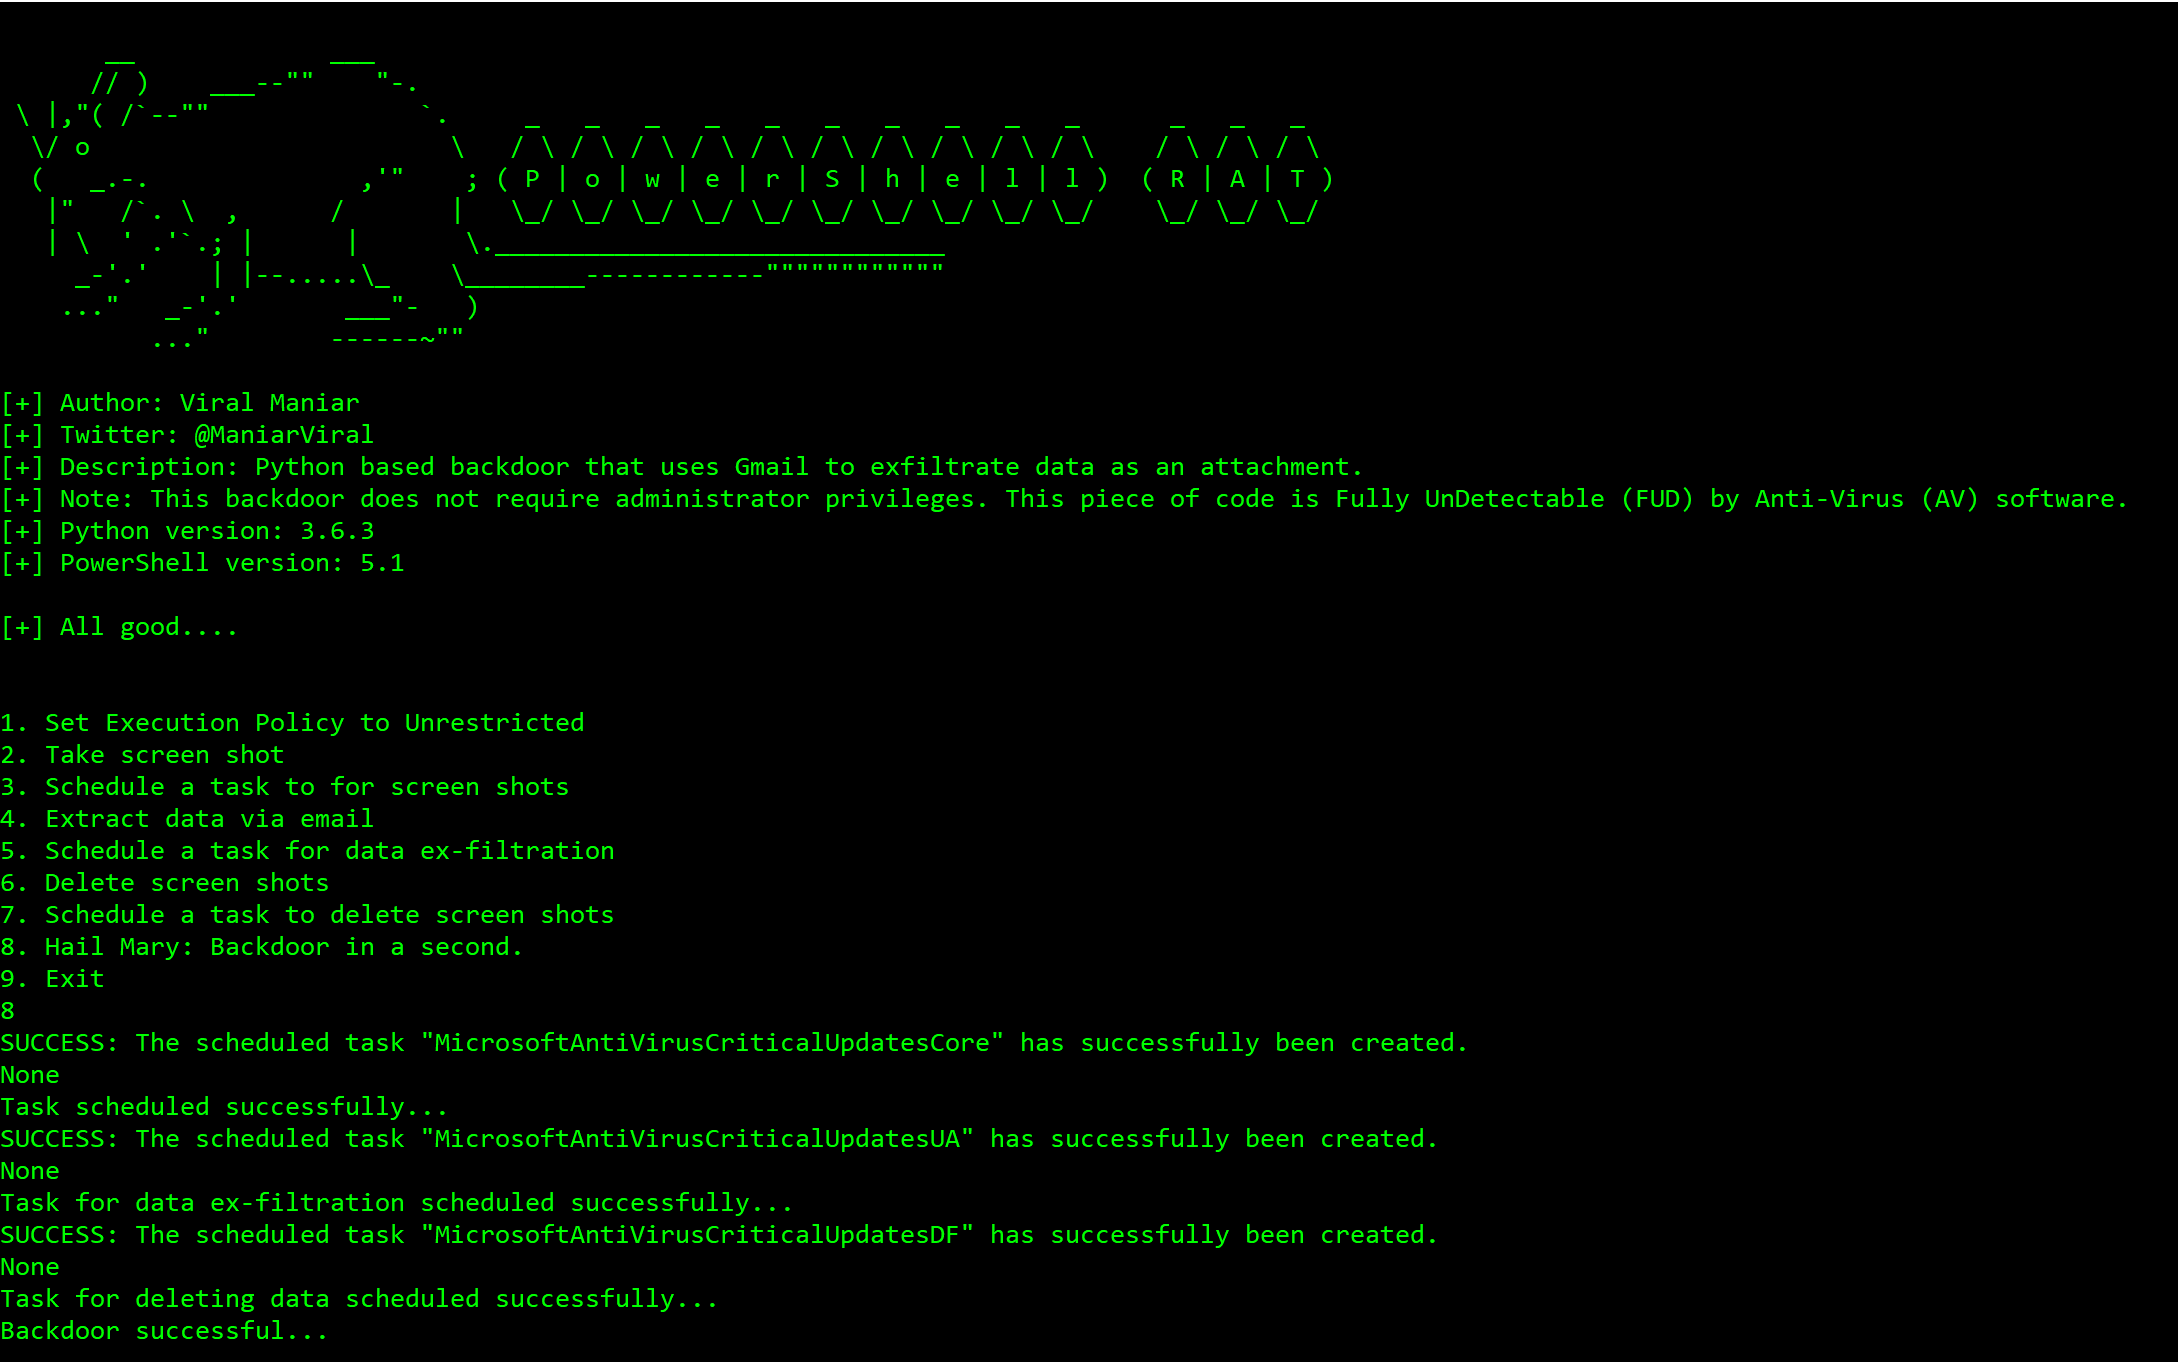 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 gentilkiwi/mimikatz
A little tool to play with Windows security
 mustafadalga/wildlogger
This is a keylogger that collects all the data and e-mail it in a set time with system information which includes device S/N and hardware specs,…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…