CVE-2026-98260-OnePlus16-PYB110-Jailbreak

CVE-2026-98260 (exec: posix CPU timer UAF) - one-command temporary root for OnePlus 16 (PYB110) from uid 2000 shell, with KernelSU/FinaSU handover

CVE-2026-98260 (exec: posix CPU timer UAF) - one-command temporary root for OnePlus 16 (PYB110) from uid 2000 shell, with KernelSU/FinaSU handover

CVE-2026-98260 一键 root | 玄戒 O1 家族:Xiaomi Pad 7S Pro 12.5 (violin) / Pad 7 Ultra (jinghu) / 15S Pro (dijun),内核 6.18.21 | 可选加载 KernelSU / SukiSU /…

Memory-only local root exploit chain for Xiaomi 17 Pro (pandora) on OS4.0.5.0, using a POSIX CPU timer UAF to disable SELinux, overwrite creds, and…

Android front end for CVE-2026-98260: root shell + KernelSU late-load through Shizuku

CVE-2026-98260 (exec: posix timer UAF) LKM jailbreak for OPPO Find X10 Pro Max (PMX110) and OnePlus 16 (PYB110): one-command root via shell uid 2000,…

GhostKey - CVE-2026-98260 一键提权工具(Shizuku + NDK Native)

GhostKey - CVE-2026-98260 一键提权工具(Shizuku + NDK Native)

Android kernel LPE exploit for CVE-2026-98260 (POSIX CPU timer UAF), ported to OPPO Pad Air 5 / MT6878, gaining temporary root and loading KernelSU.

One-tap Android root for Samsung Galaxy devices, built around the CVE-2026-98260 timer exploit.

Android app that checks a supported Vivo X200 Ultra, then uses Shizuku to attempt temporary root with CVE-2026-98260 and load KernelSU. Optional boot…

Proof-of-concept hostile Meterpreter agent and writeup for CVE-2026-87690, a path traversal in Metasploit's ios_image_gather module leading to…

Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…

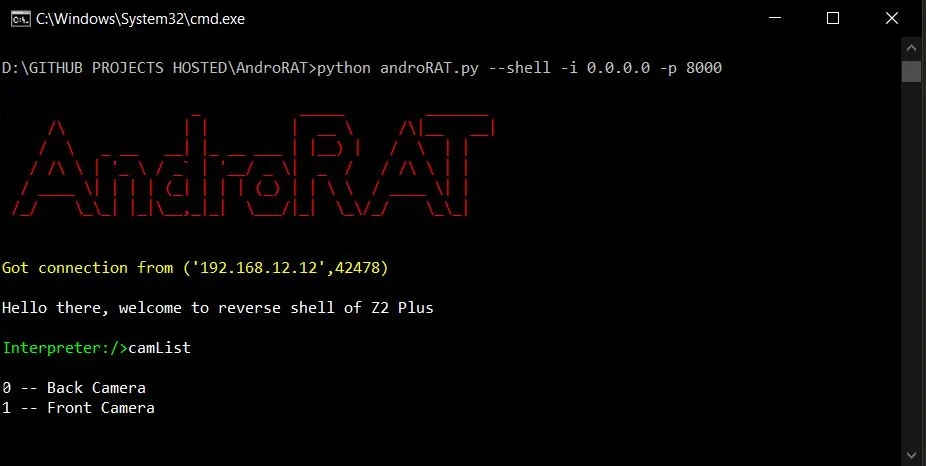
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

Confluence CVE 2021,2022,2023 利用工具,支持命令执行,哥斯拉,冰蝎 内存马注入

TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain

.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…

Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…