

Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
b23r0/heroinnA cross platform C2/post-exploitation framework.
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 mythicagents/xenon
A Mythic agent for Windows written in C
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 ghostpack/rubeus
Trying to tame the three-headed dog.
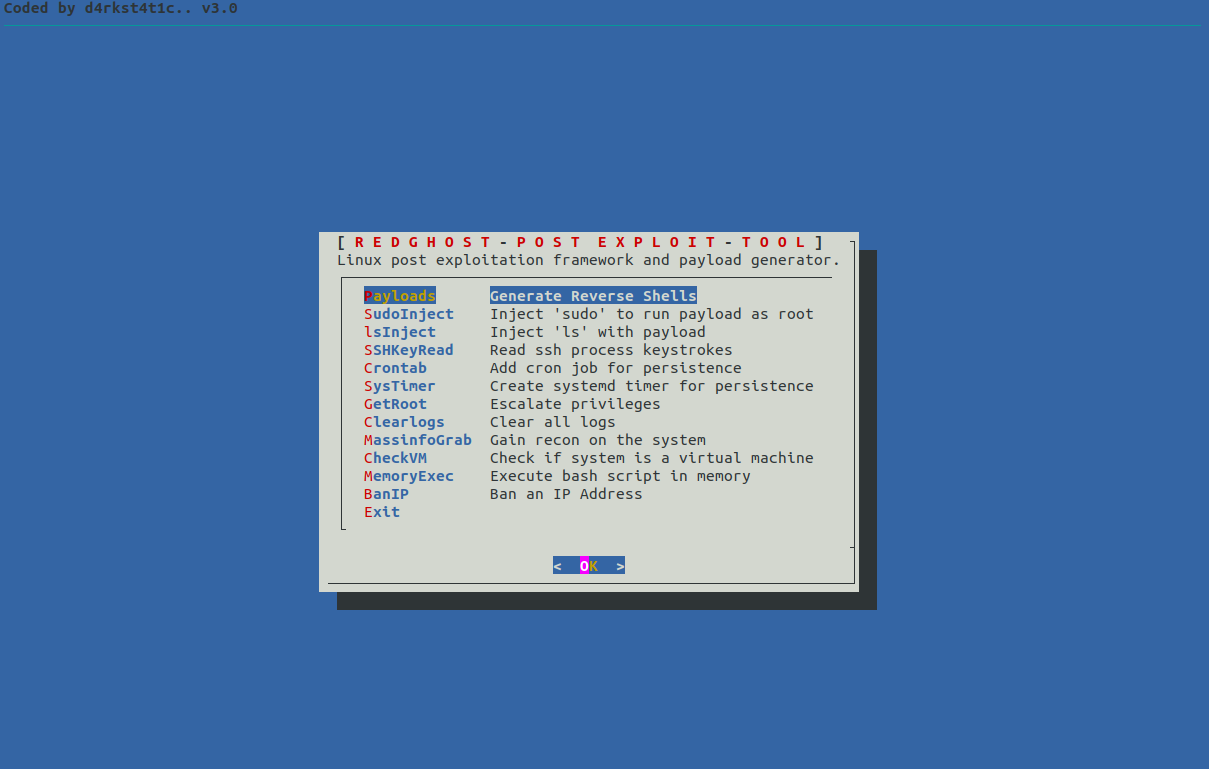 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
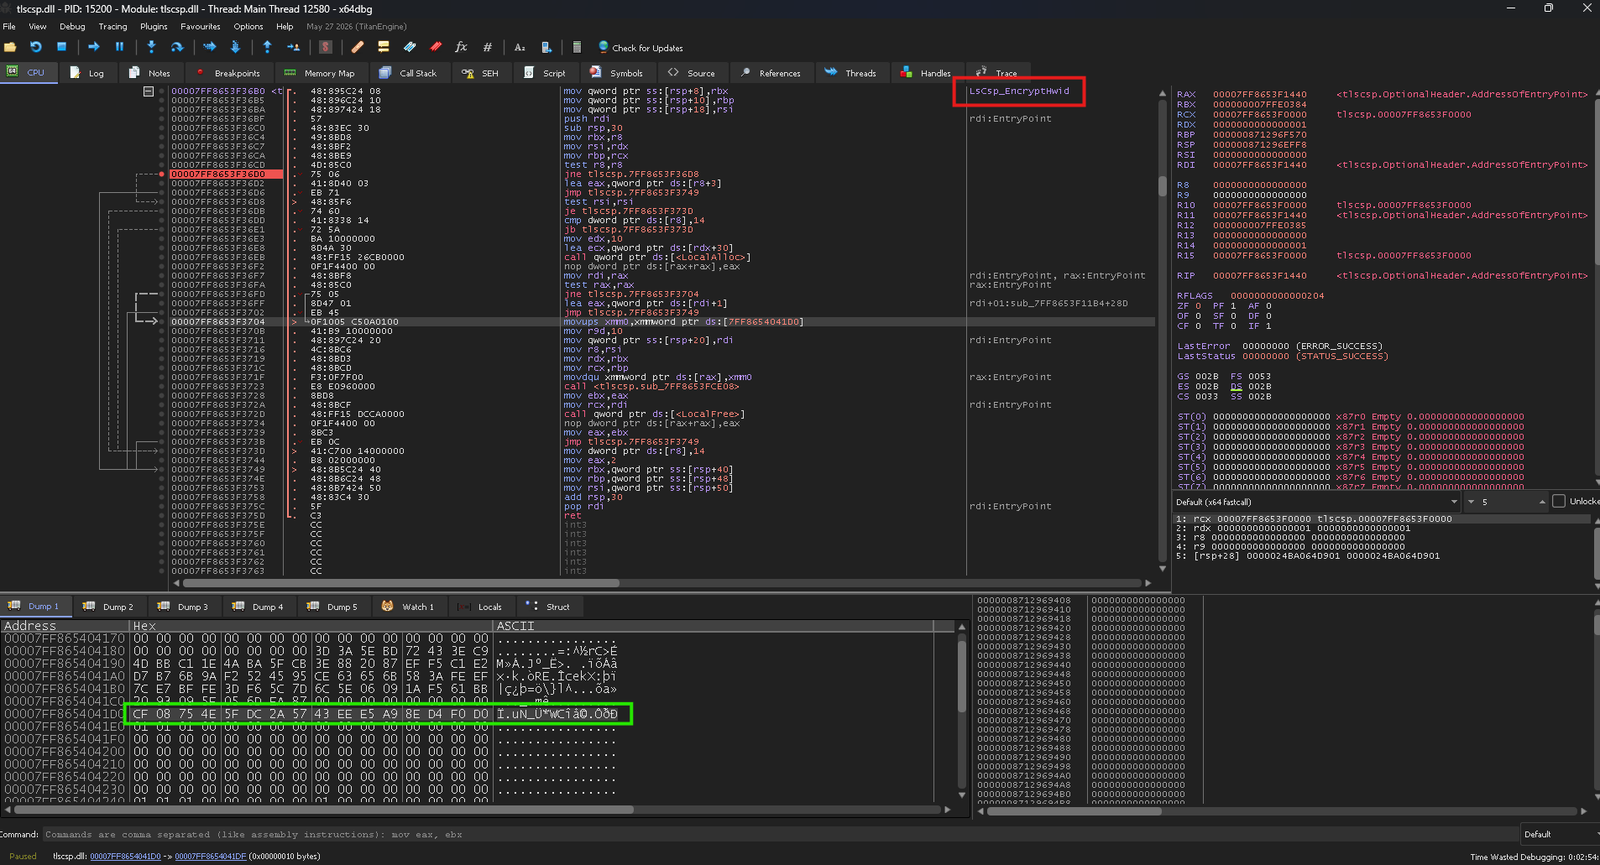 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 gentilkiwi/mimikatz
A little tool to play with Windows security