

FolkPatch
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.3k
lyravoid/folkpatchRoot access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 blendin/3snake
Tool for extracting information from newly spawned processes
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 nicetop1027/cve-2026-discord
Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
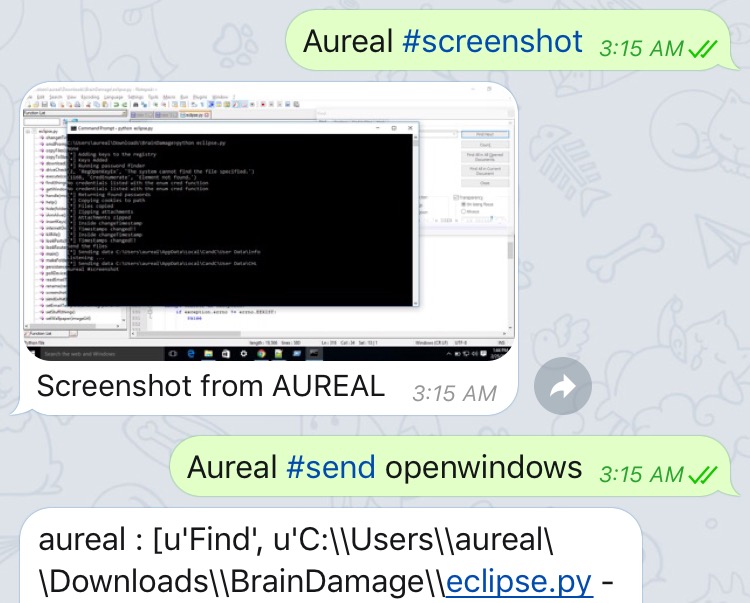 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 niker-lixy/postex
Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
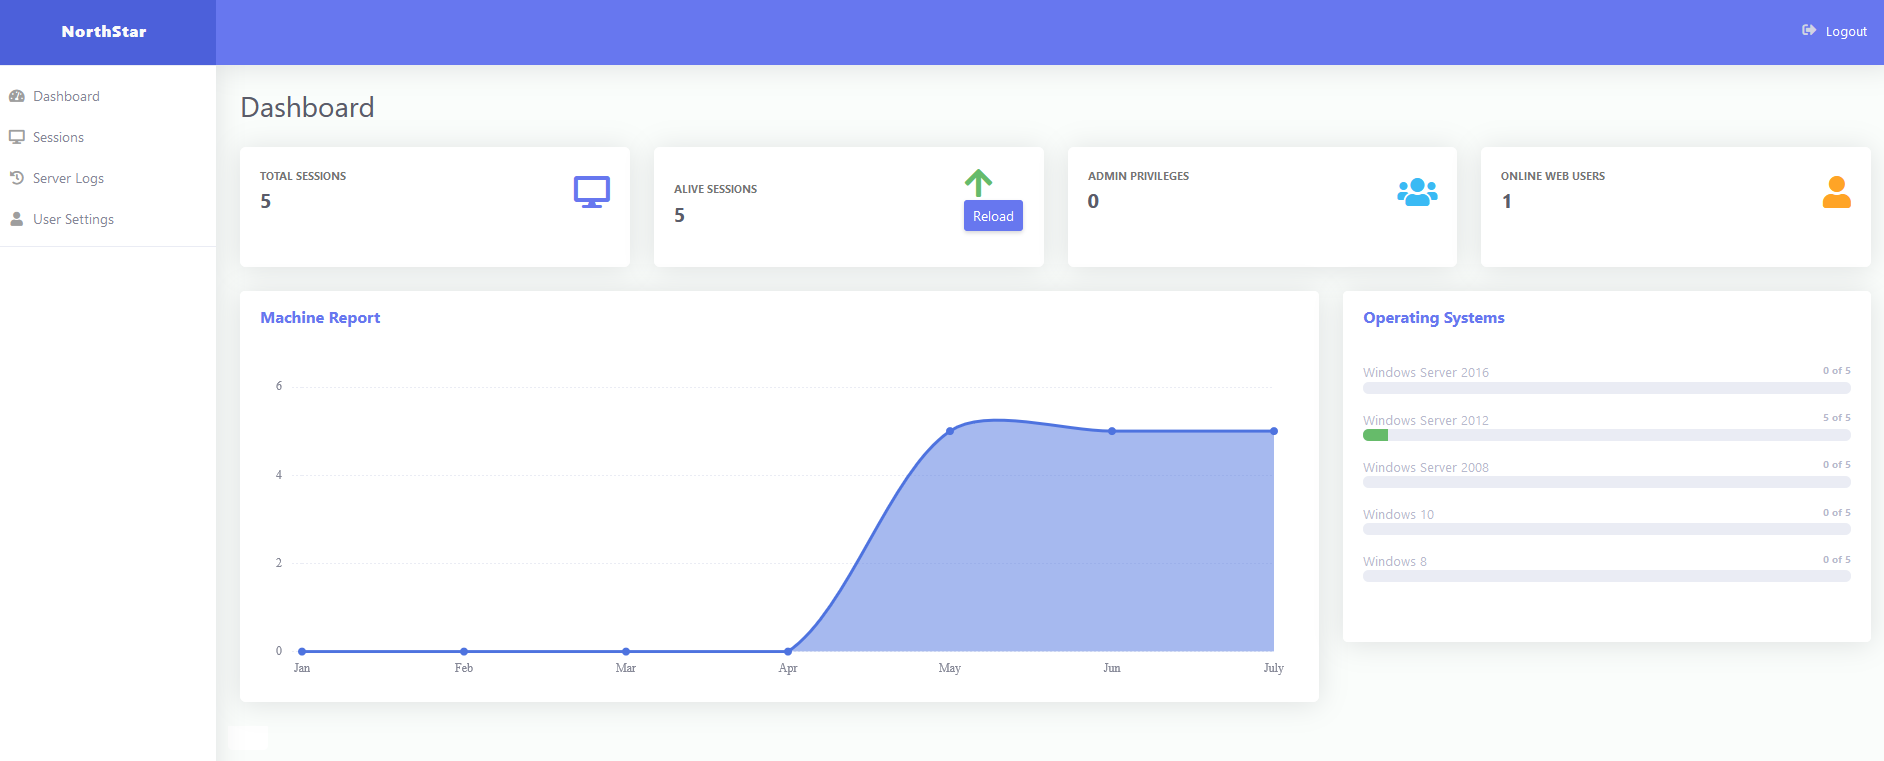 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 rayngnpc/cve-2024-49019-rayng
Exploitation for CVE-2024-49019
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.