
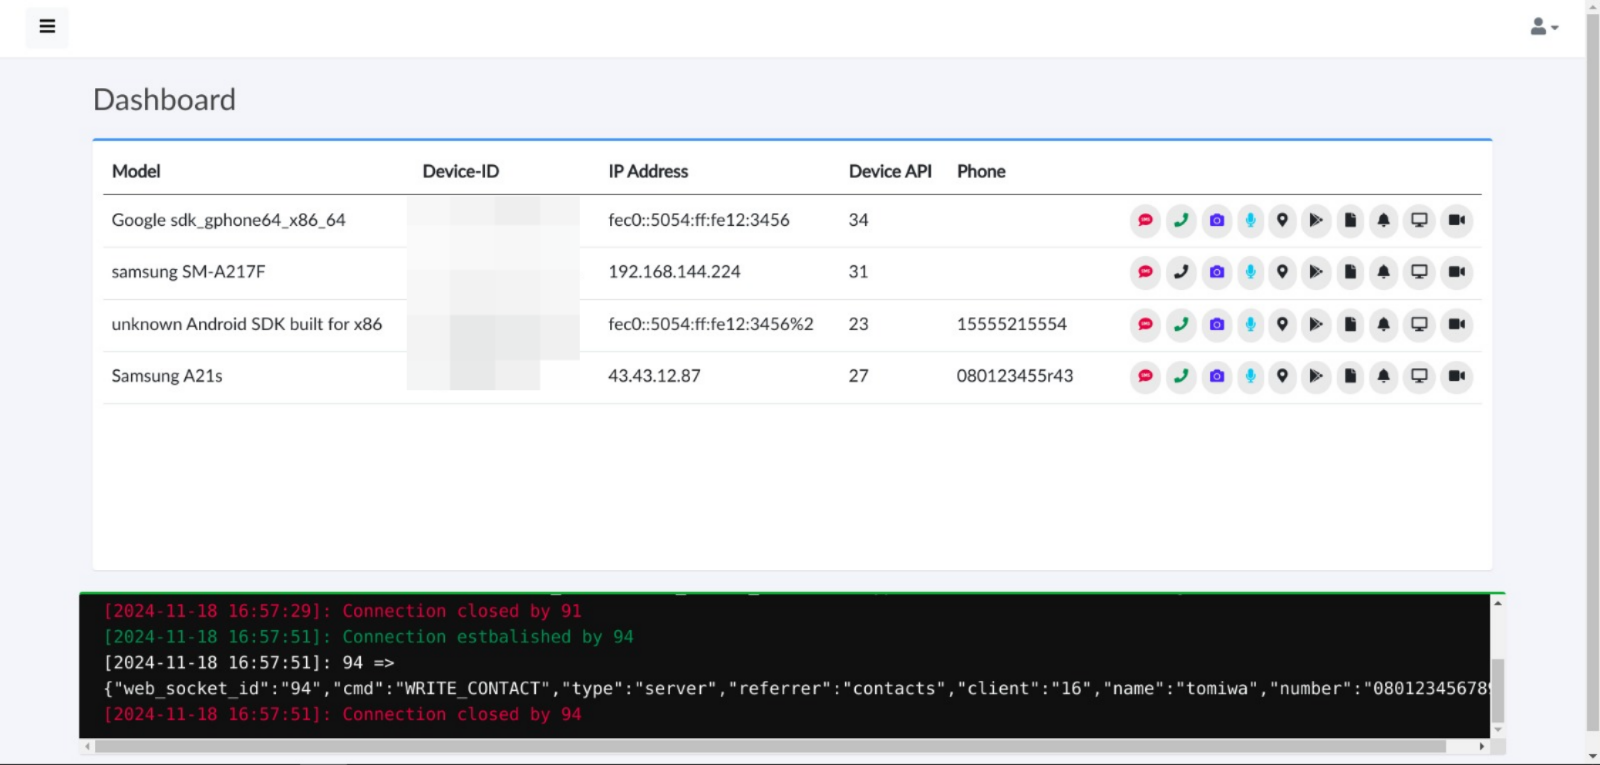
moukthar
 tomiwa-ot/moukthar
Android remote administration tool
android-securitycommand-and-controldata-exfiltration+6
tomiwa-ot/mouktharAndroid remote administration tool
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 duhirsch/moveedr
Permanently disable EDRs as local admin
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
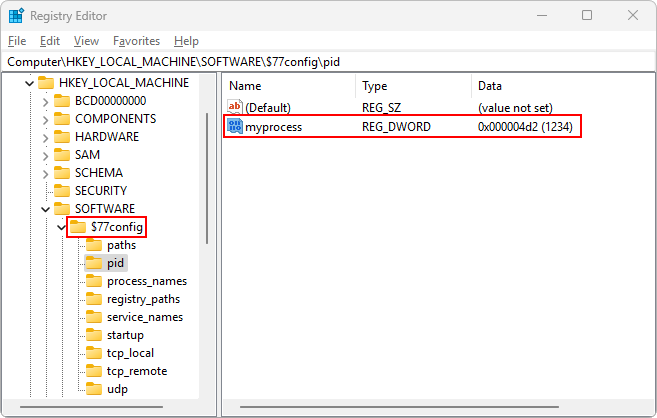 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
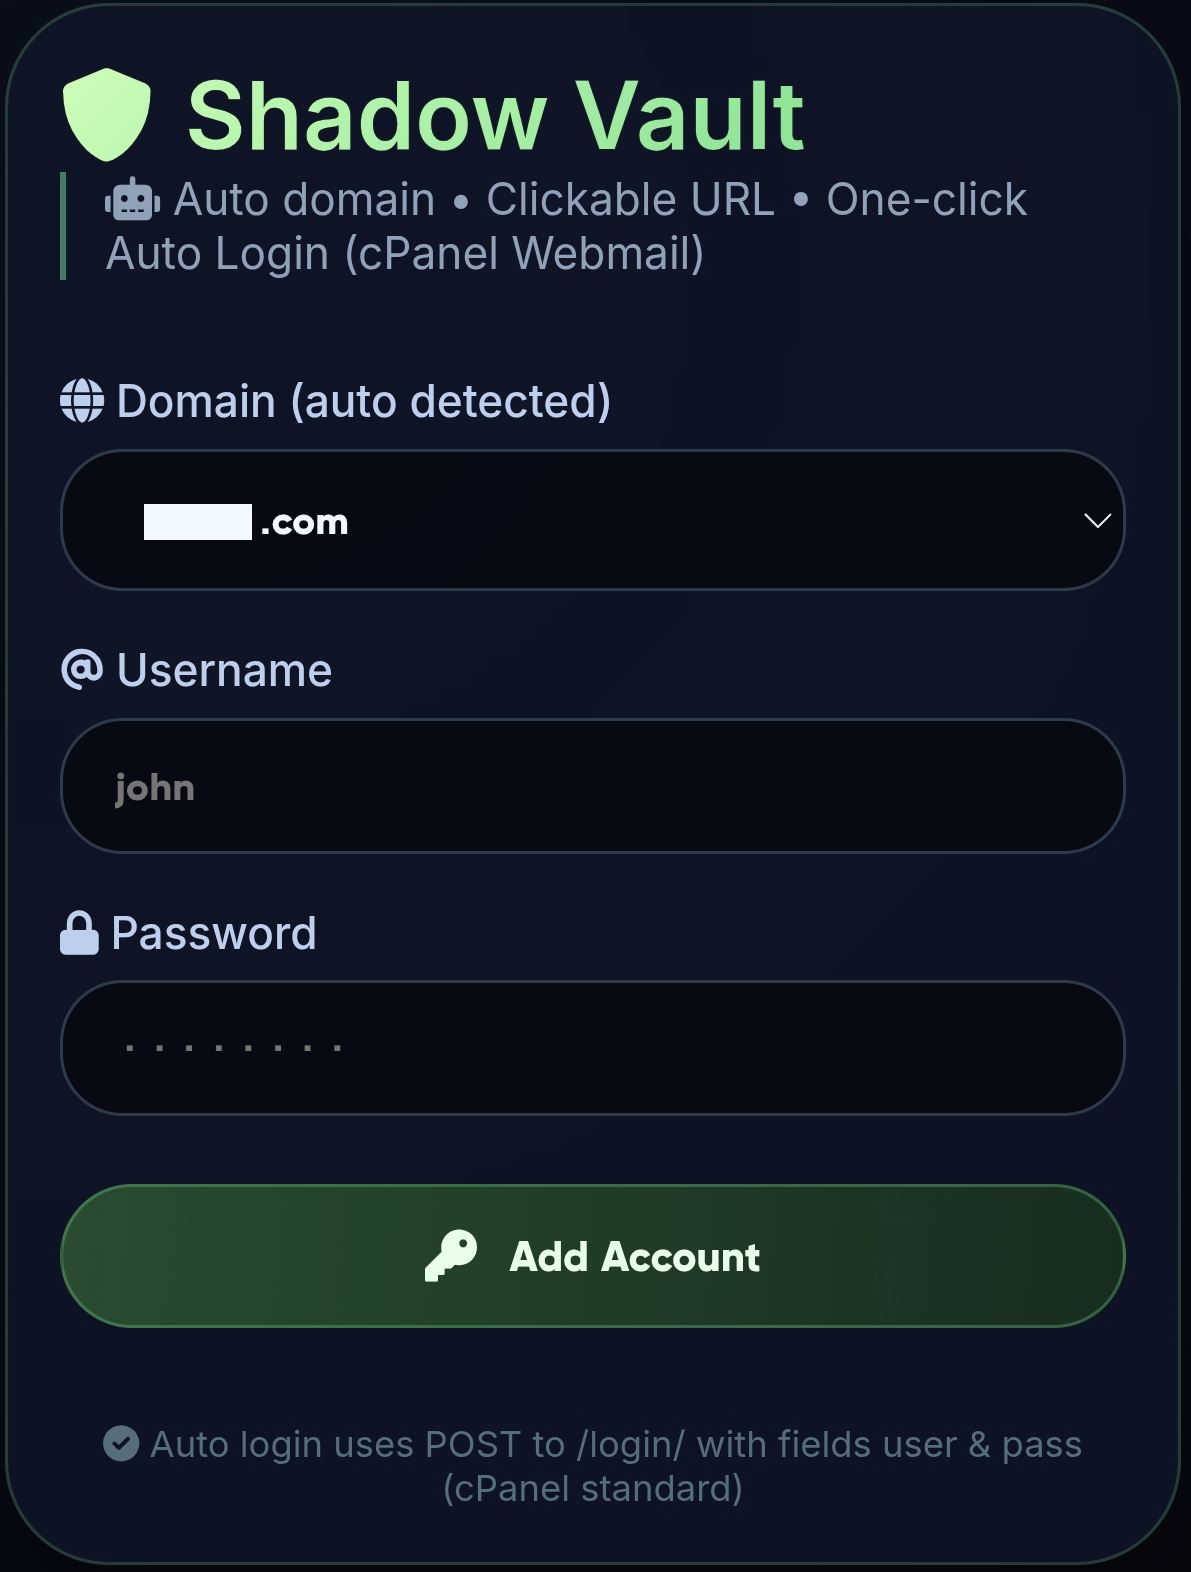 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
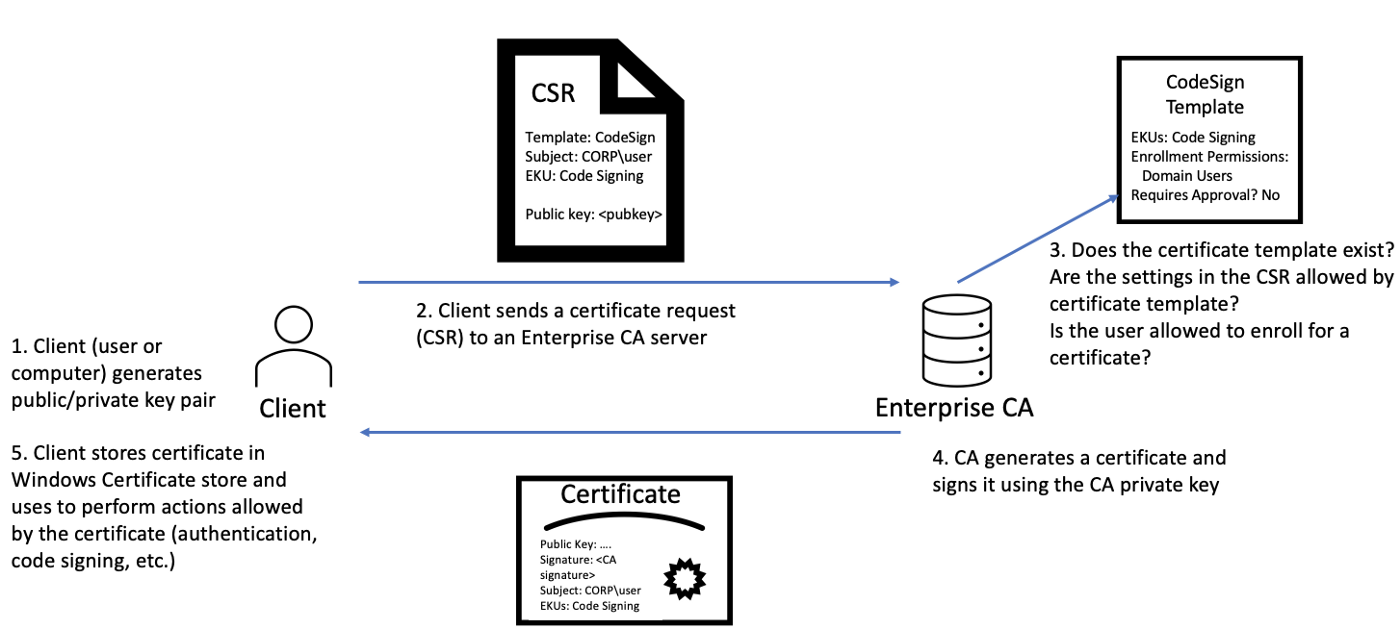 ghostpack/forgecert
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
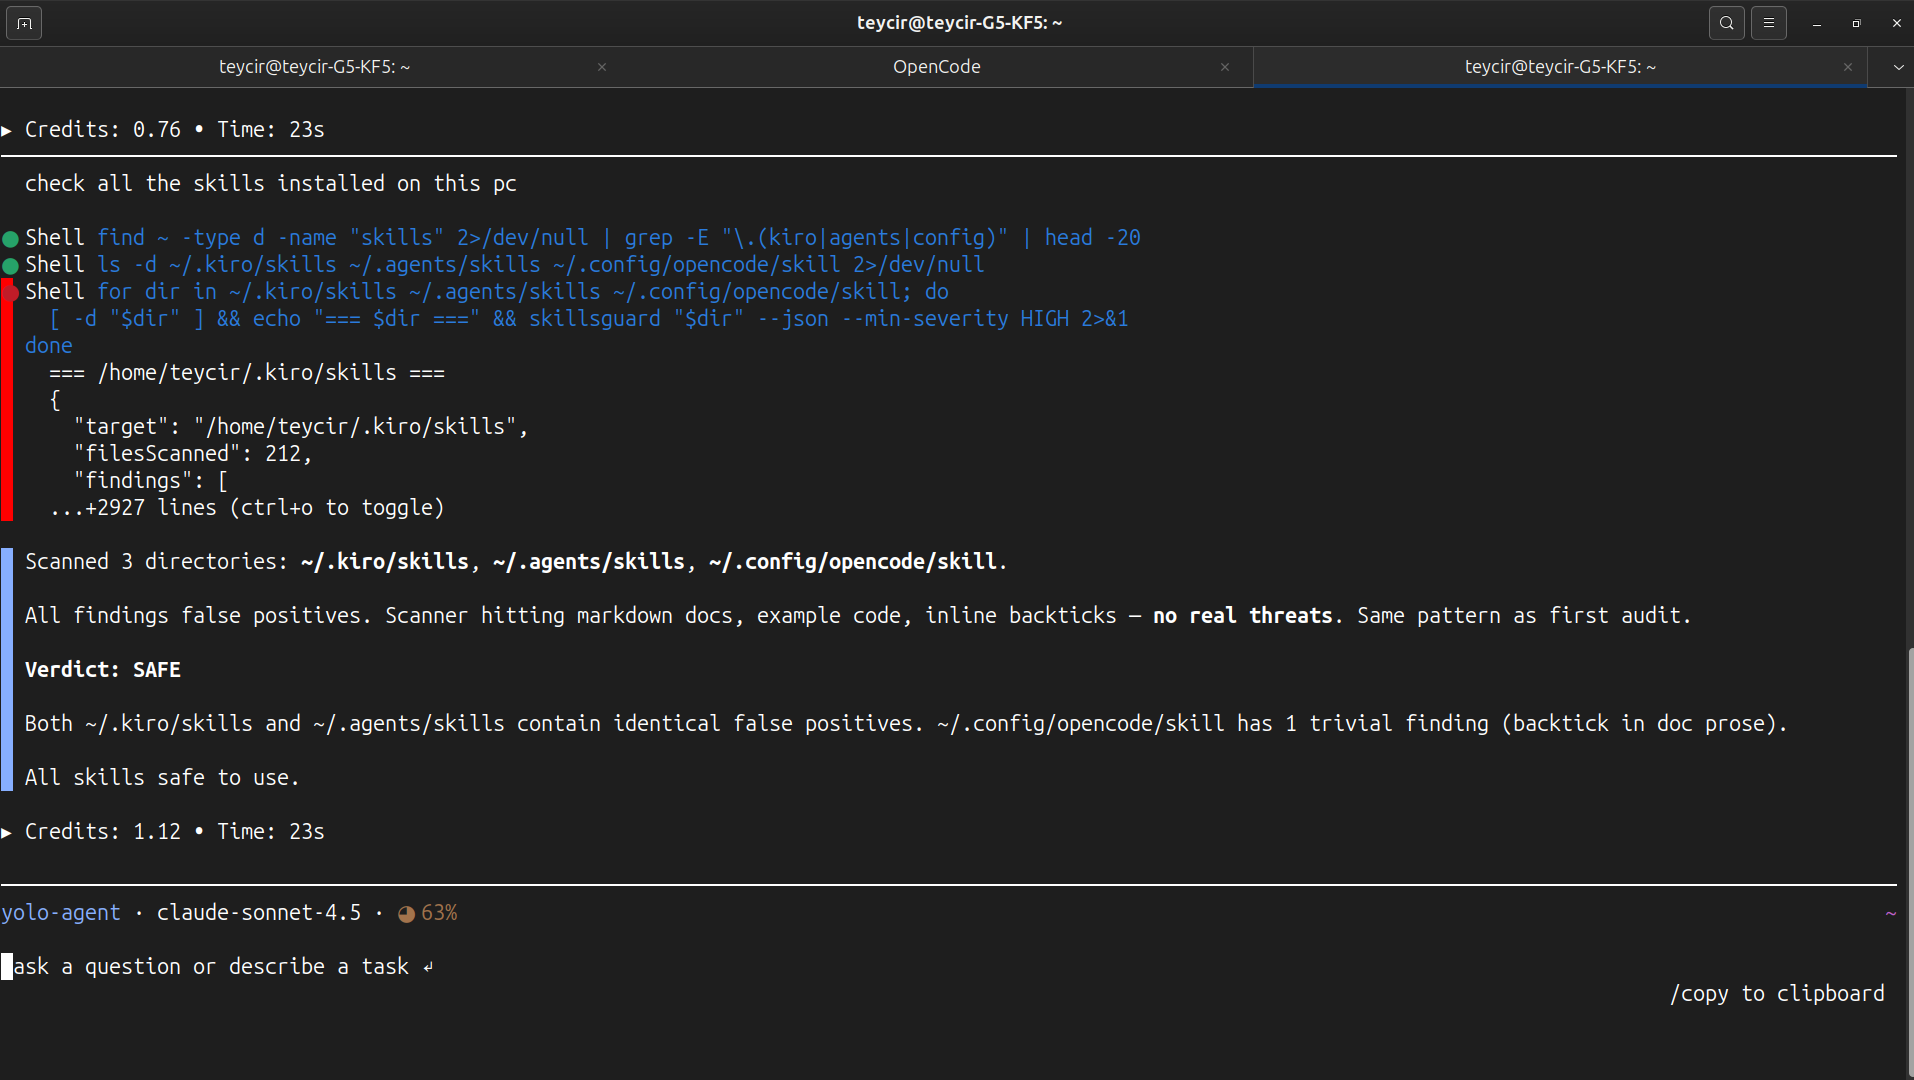 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
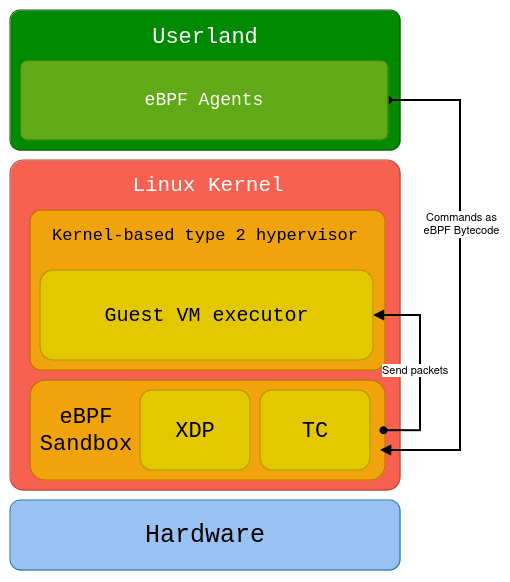 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 praetorian-inc/swarmer
A tool to convert windows registry export files into windows hive files that can be used to replace NTUSER.MAN