
link
 postrequest/link
link is a command and control framework written in rust
command-and-controlexploit-frameworkspayload-development+2
postrequest/linklink is a command and control framework written in rust
 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
 openrce/paimei
A reverse engineering framework written in Python.
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3

 redsiege/persistassist
Fully modular persistence framework
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
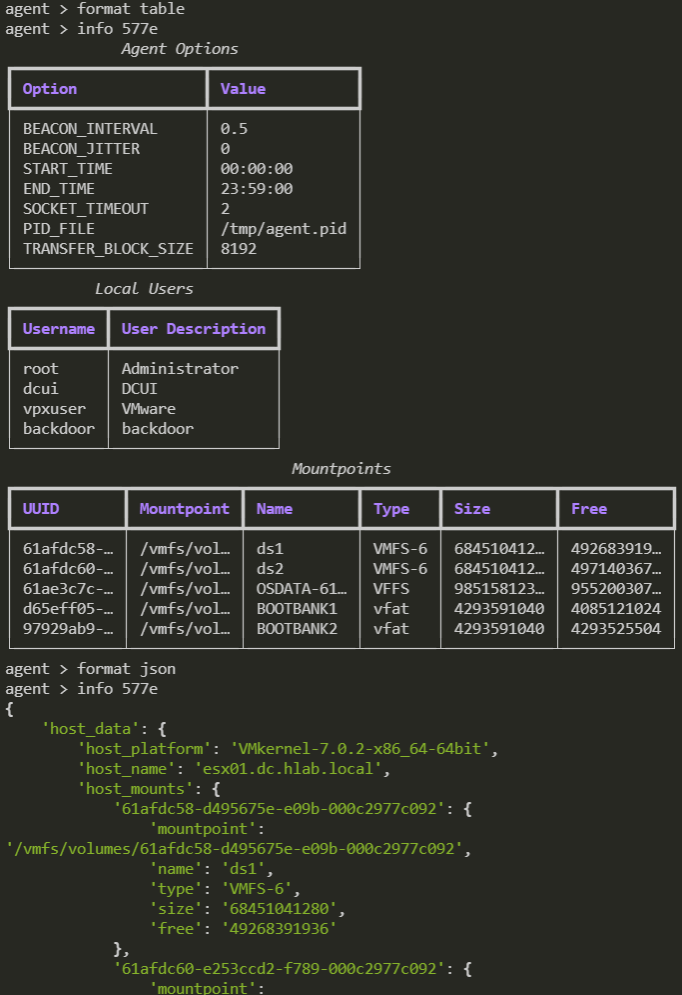 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 mythicagents/nimplant
A cross-platform implant written in Nim
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
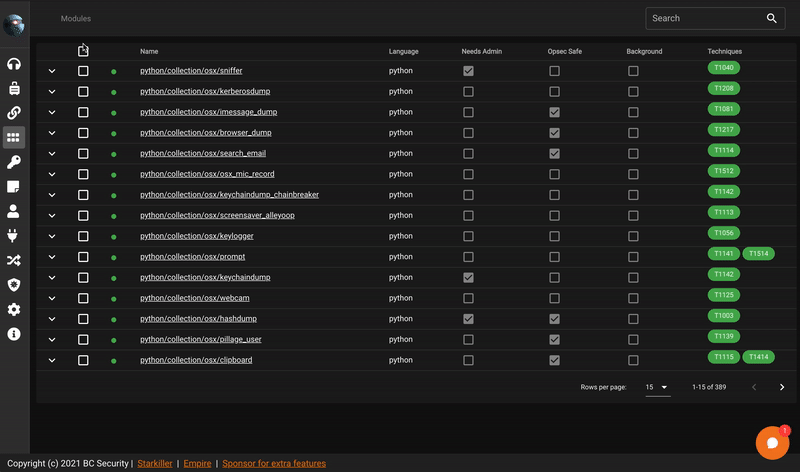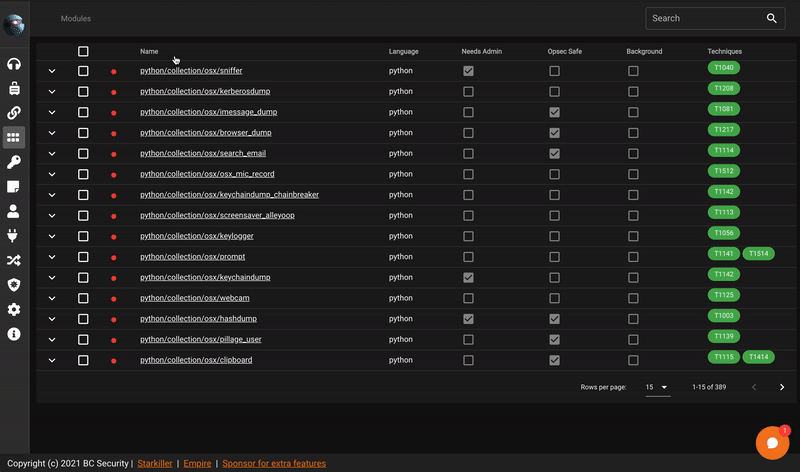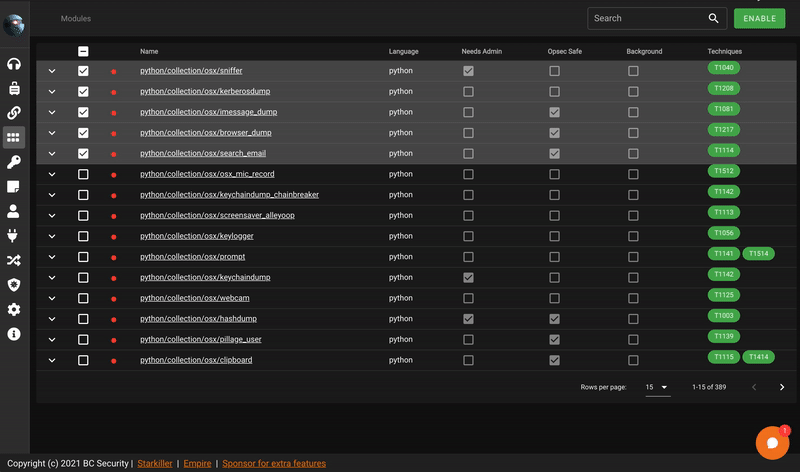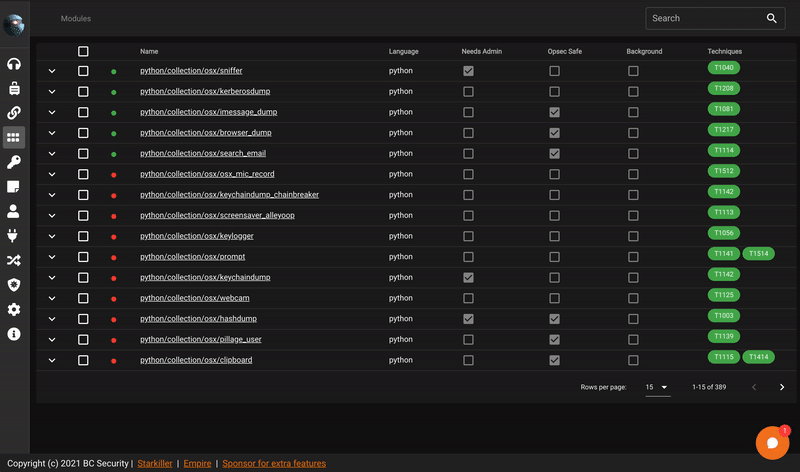 bc-security/starkiller
Starkiller is a Frontend for PowerShell Empire.
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.