
CVE-2024-38472
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
command-and-controlexploit-frameworkslateral-movement+6
abdurahmon3236/cve-2024-38472Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 arno0x/dbc2
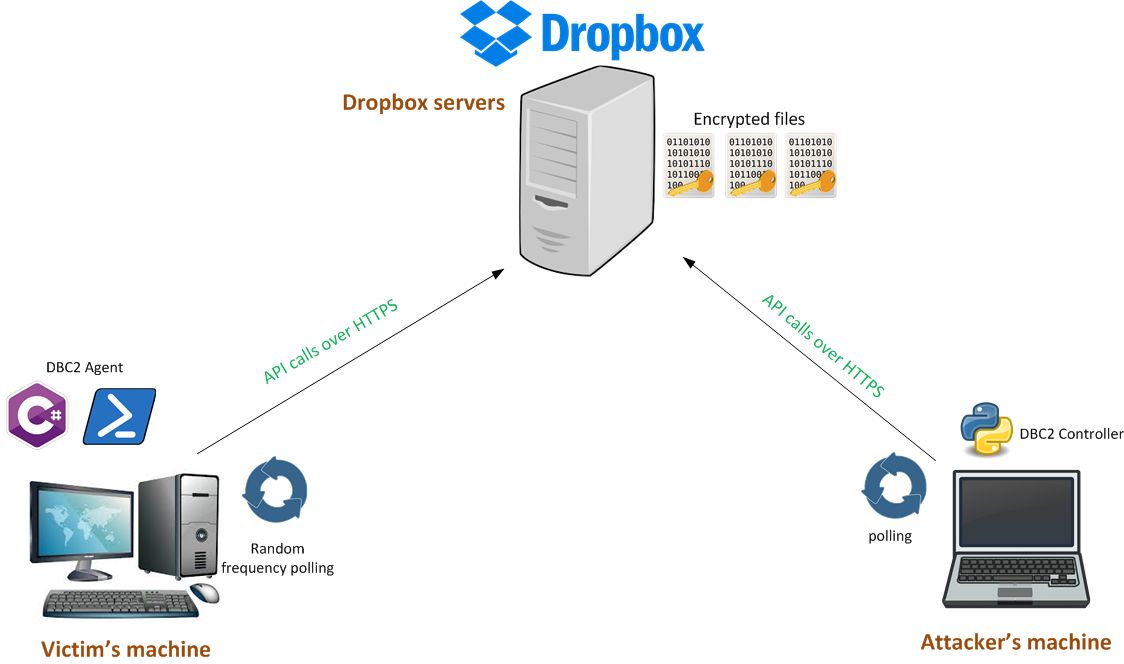
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
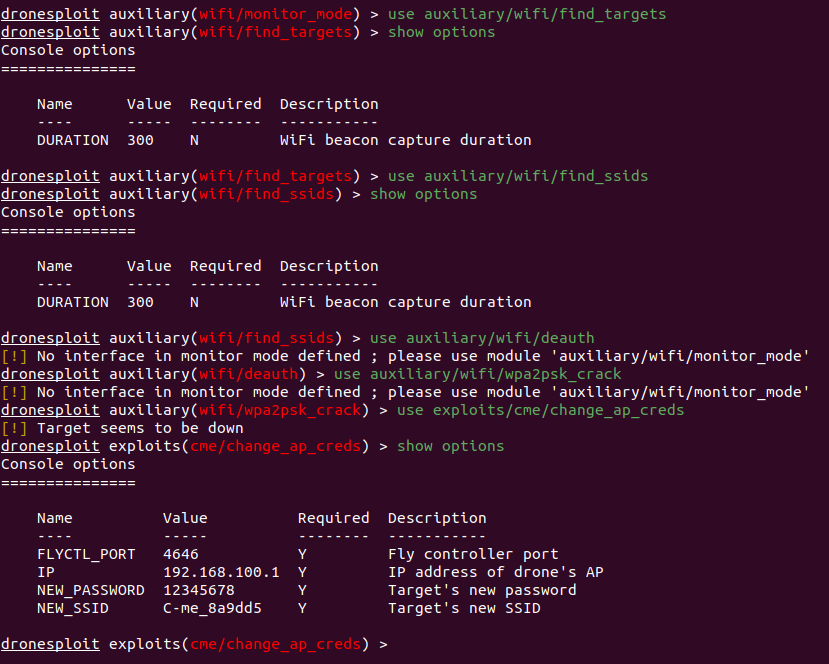 dronesploit/dronesploit
Metasploit-style console framework for pentesting commercial drones, featuring modular exploits for wireless attacks, SSID/password manipulation, and…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

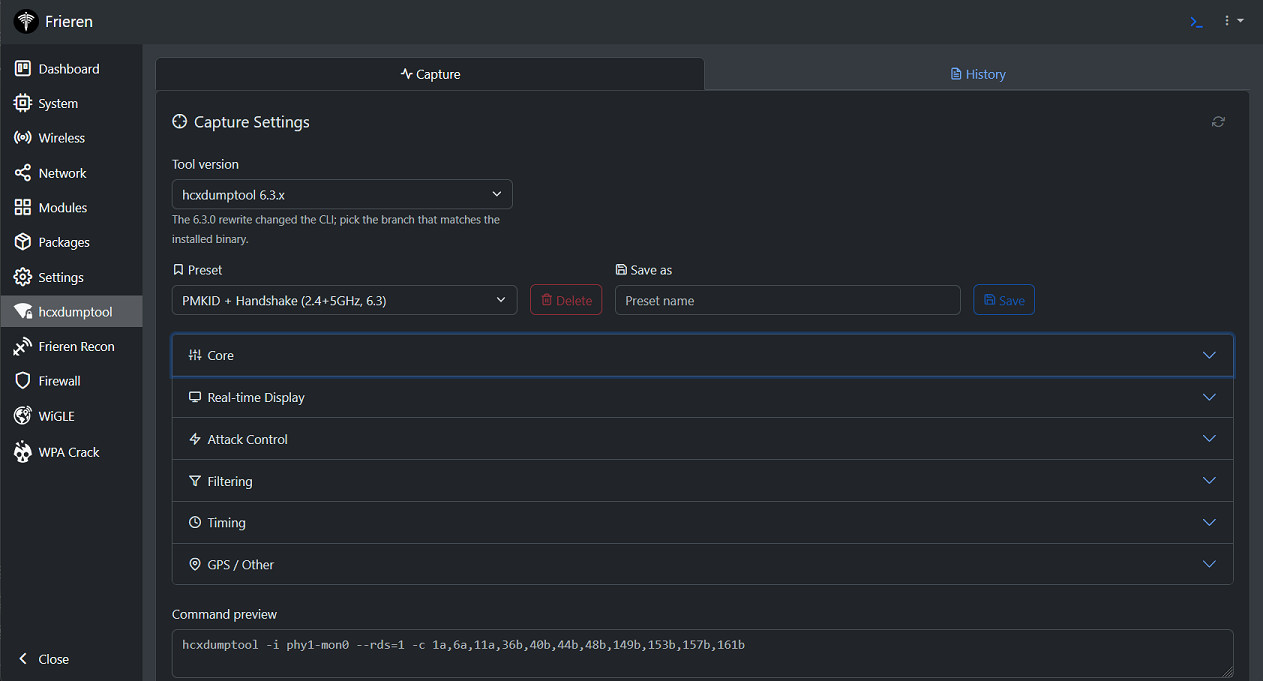 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 blacksnufkin/pwnbox-kali
Bash Script to automate the process of setting up a new Kali Linux virtual machine to look a like HTB PwnBox
 pownjs/pown
Pown.js is a security testing an exploitation toolkit built on top of Node.js and NPM.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…