
ghostlock-vagrant-box
 daniyal48/ghostlock-vagrant-box
An isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…
ctfeducationexploitation+3
1
daniyal48/ghostlock-vagrant-boxAn isolated Vagrant testbed designed to simulate a complete attack chain: Initial access via the Nginx heap buffer overflow (CVE-2026-42533) followed…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
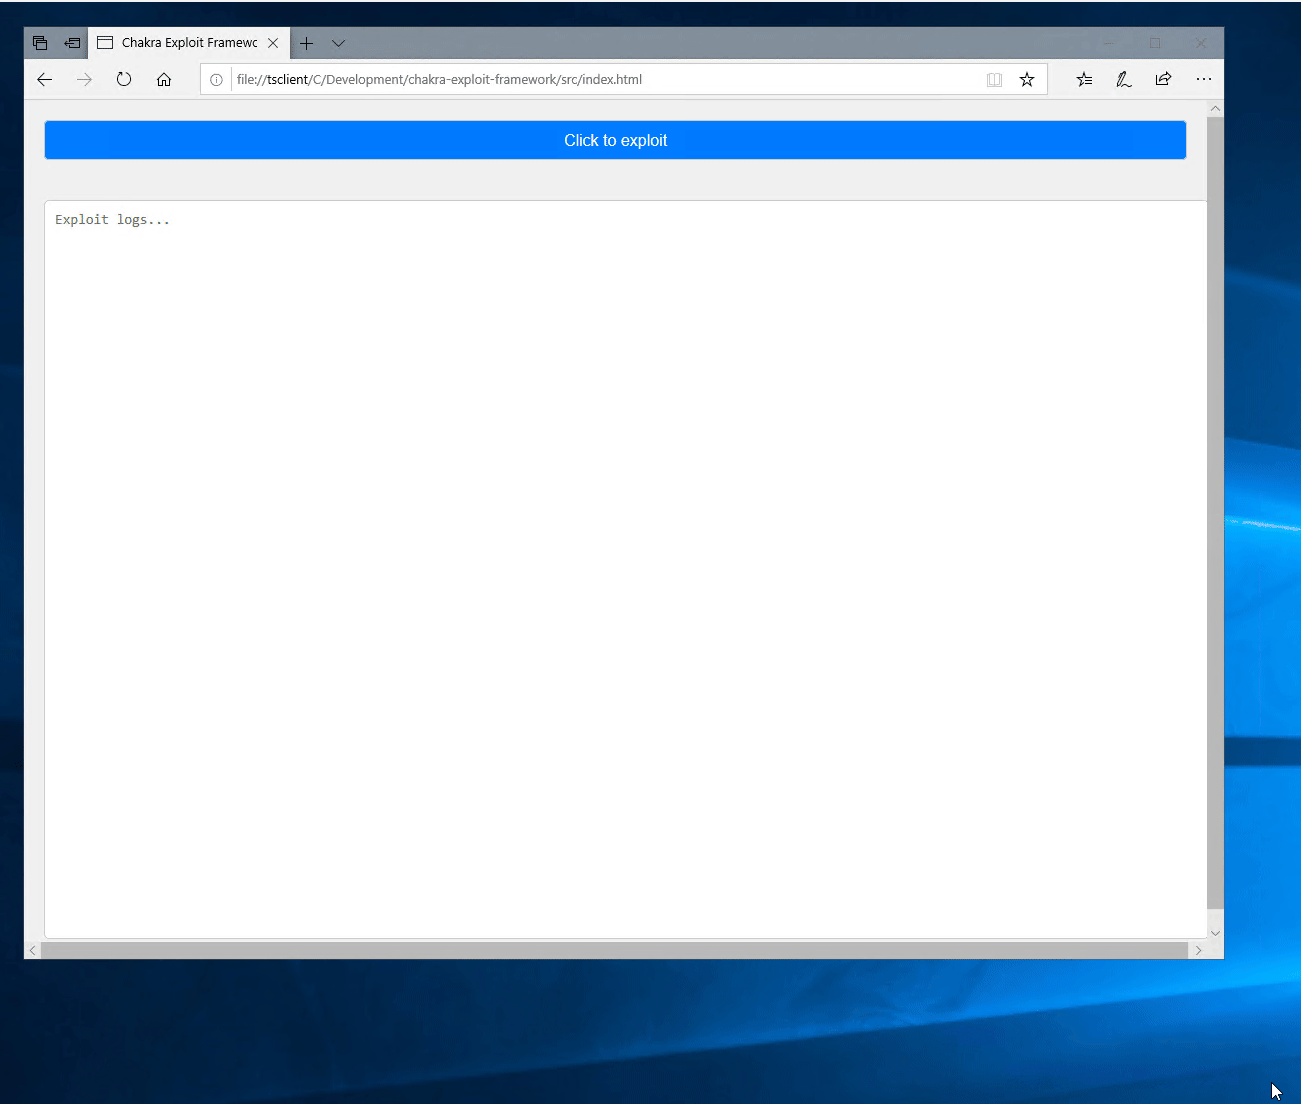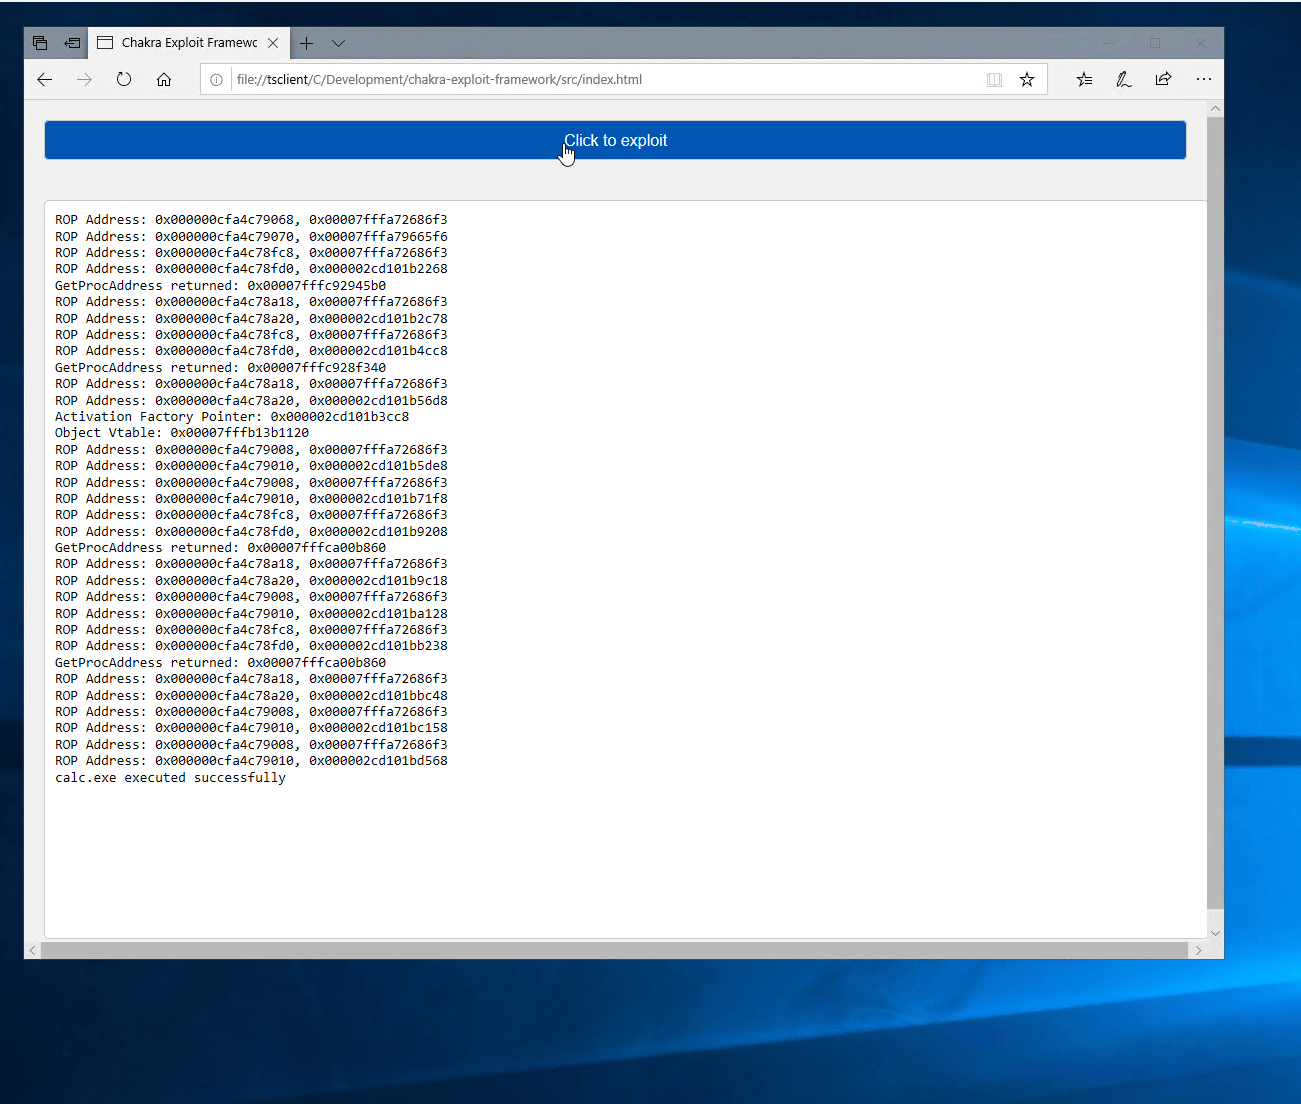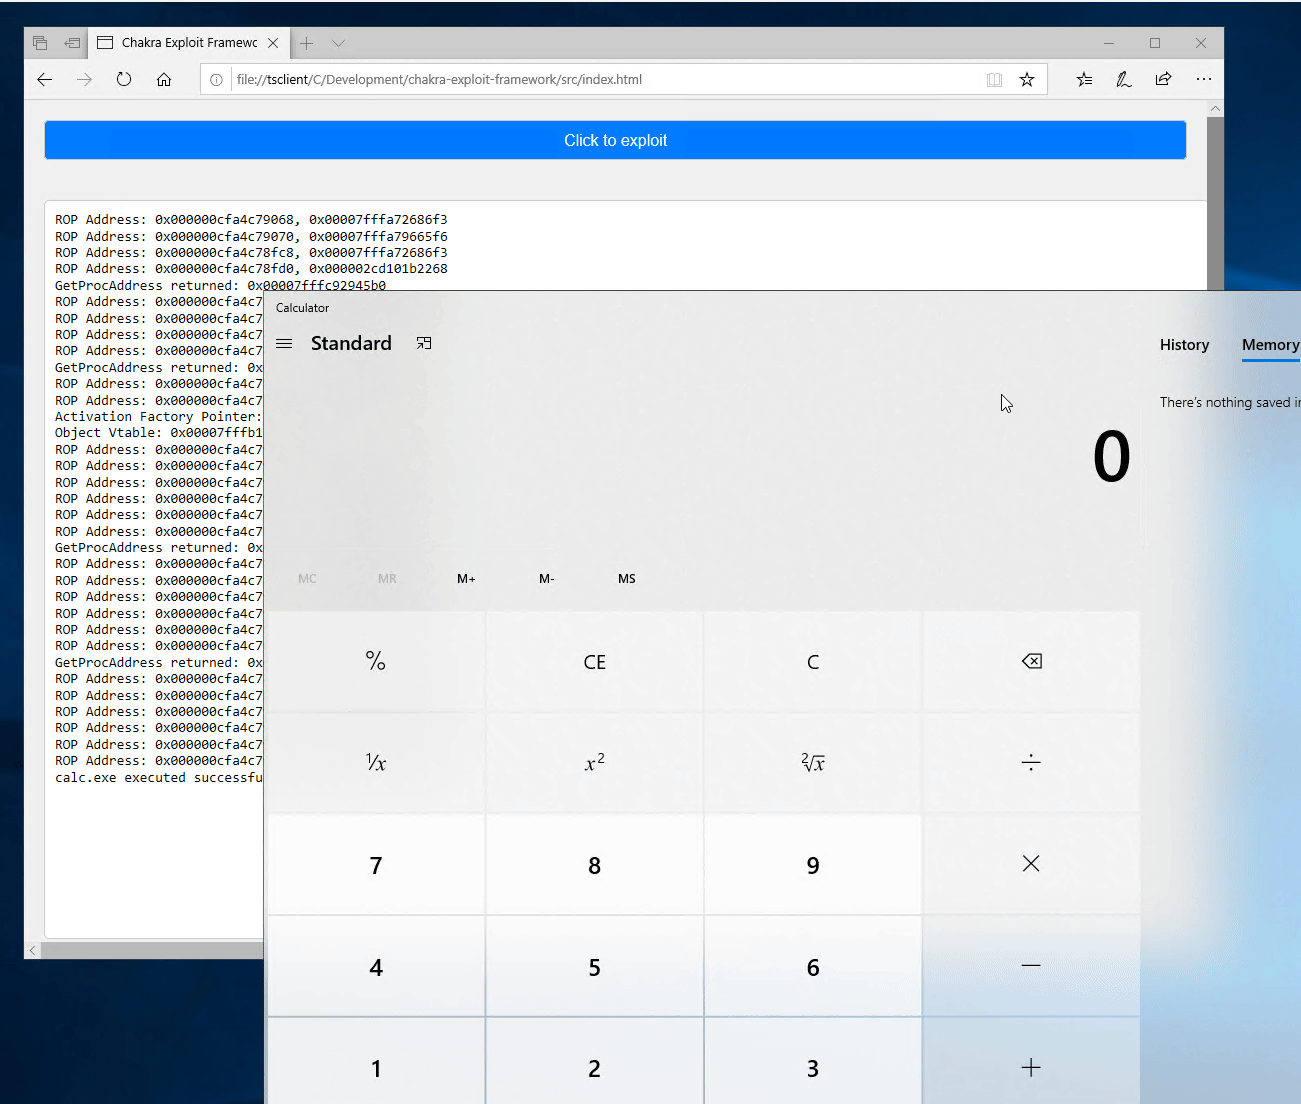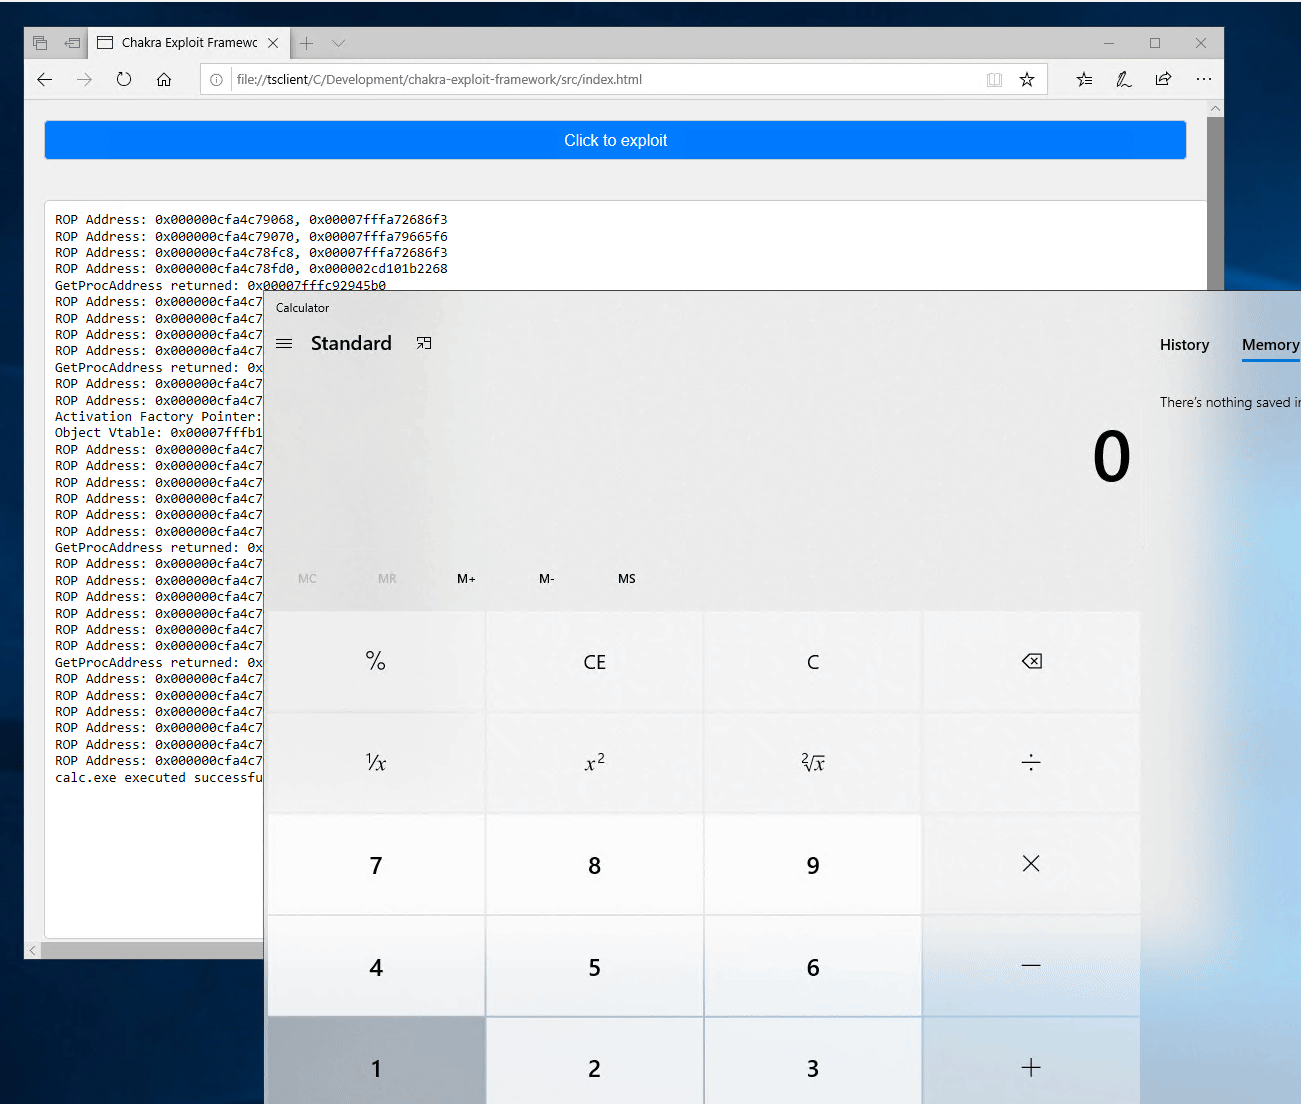 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 gallopsled/pwntools
CTF framework and exploit development library
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 c0rel0ader/east
Exploits and Security Tools Framework 2.0.1
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…