
LibAFL
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
binary-analysisdynamic-analysis-sandboxingeducation+5
2.6k
aflplusplus/libaflAdvanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
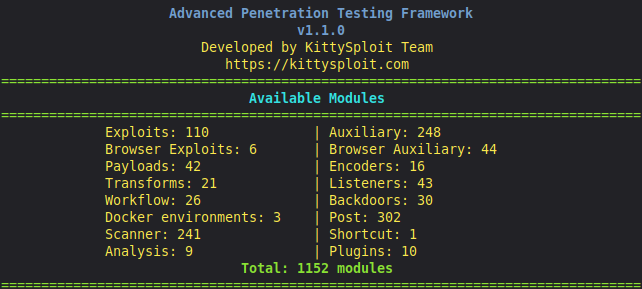 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework