
C3
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
command-and-controlexploit-frameworksids-ips-evasion+6
1.8k
reverseclabs/c3Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 bishopfox/sliver
Adversary Emulation Framework
 smythtech/sdnpwn
An SDN penetration testing toolkit
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
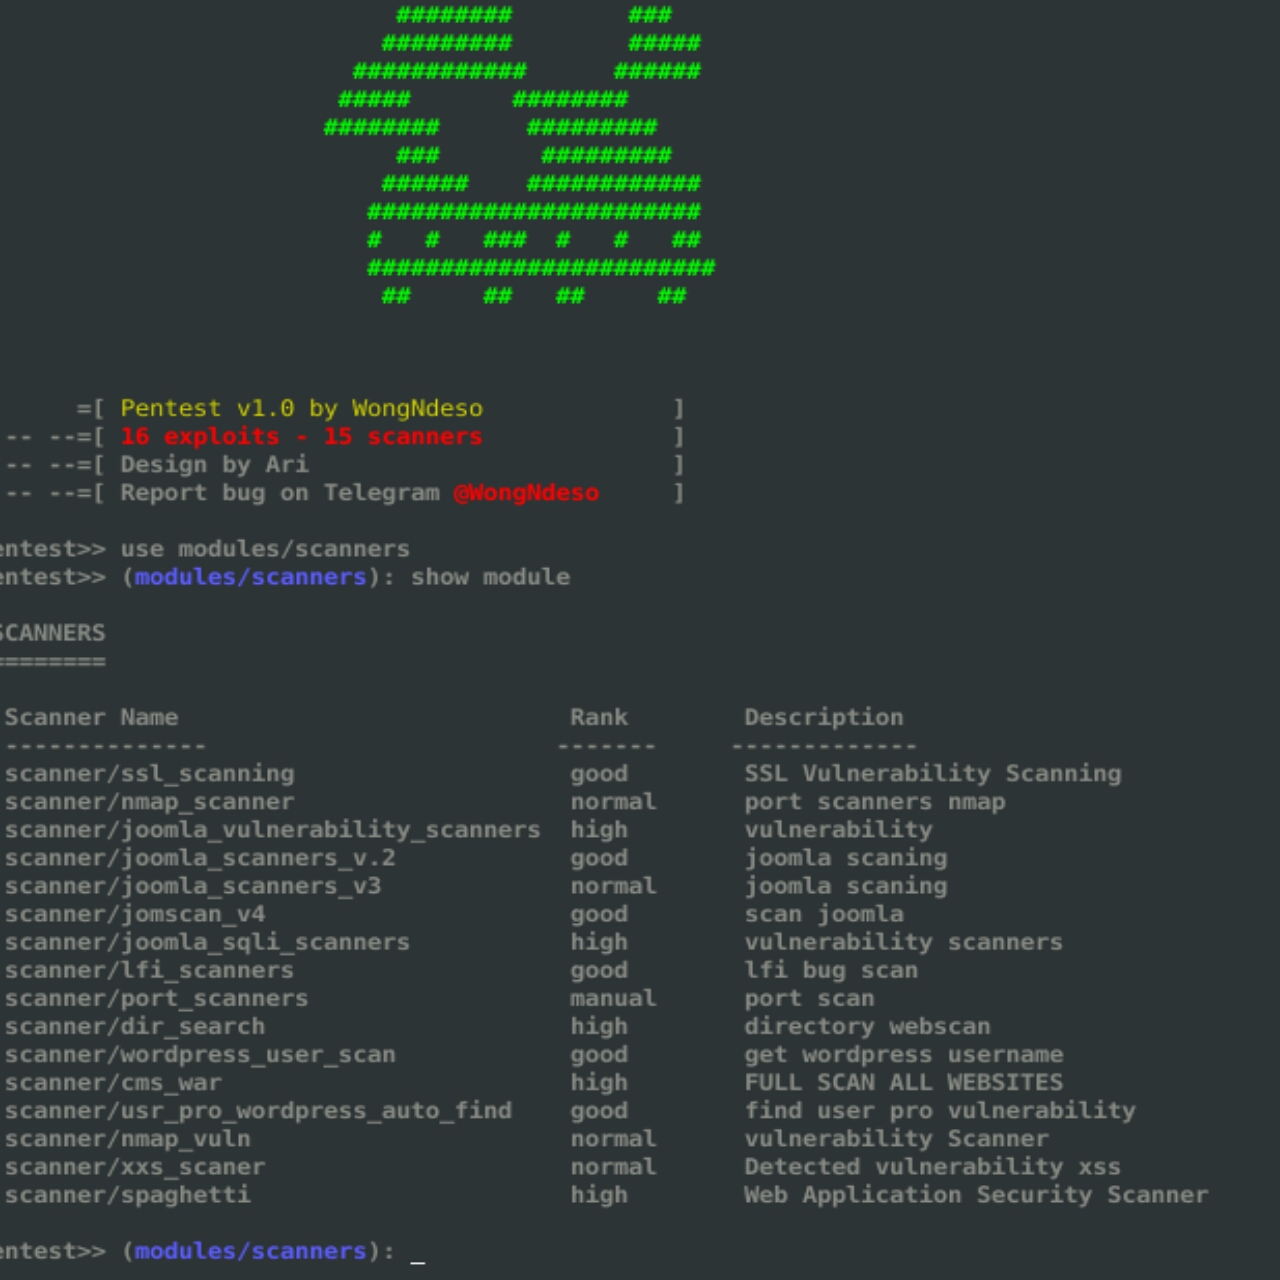 pikpikcu/pentest-tools-framework
Pentest Tools Framework is a database of exploits, Scanners and tools for penetration testing. Pentest is a powerful framework includes a lot of…
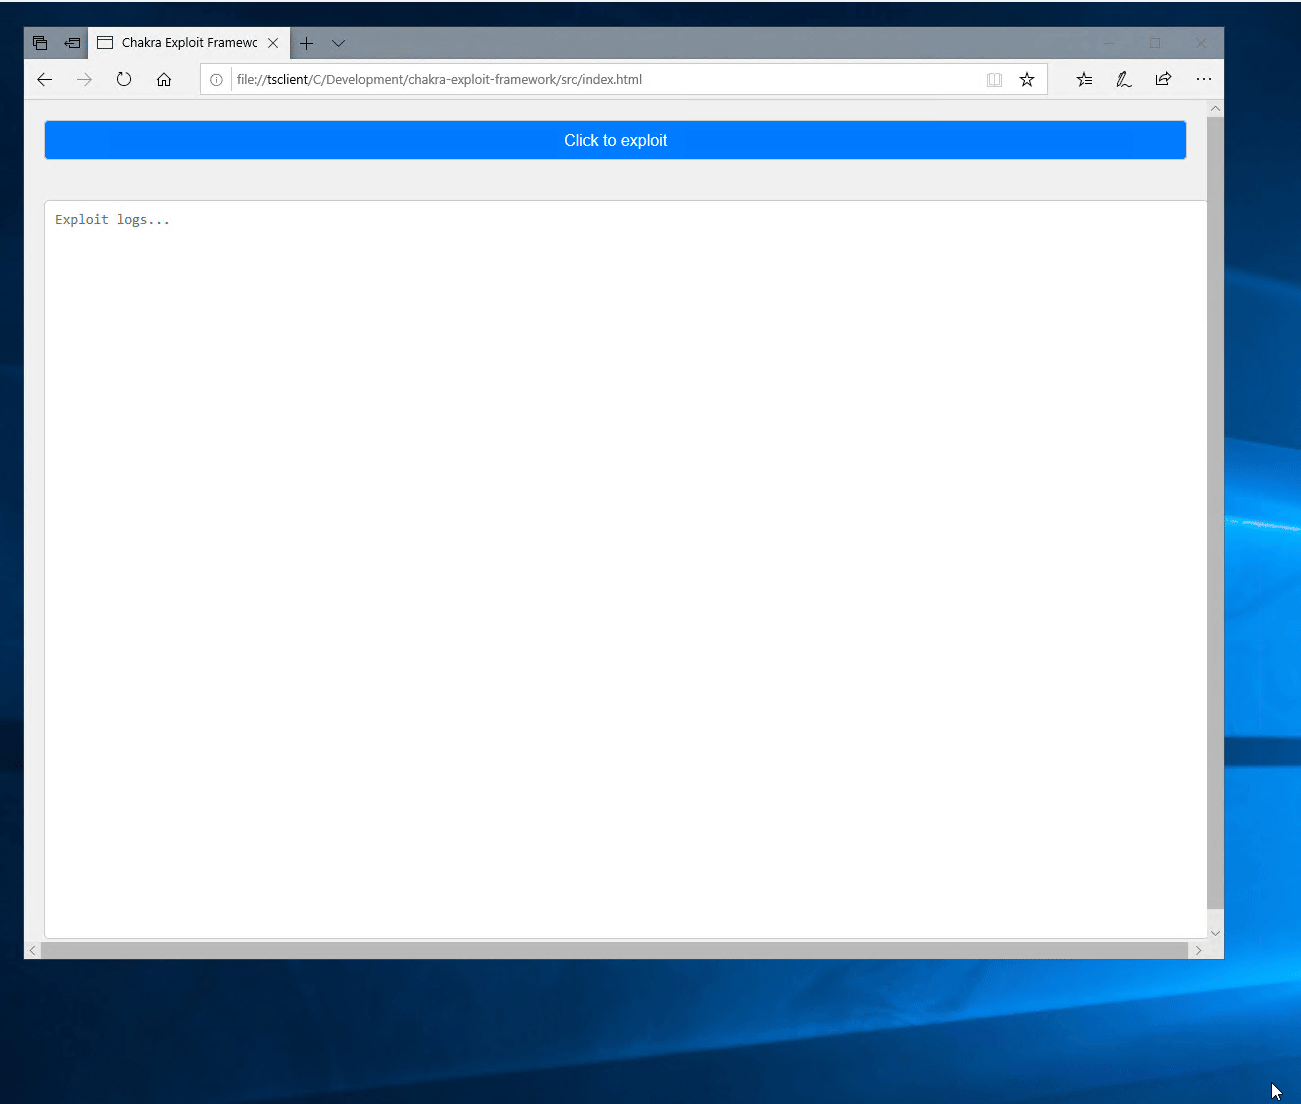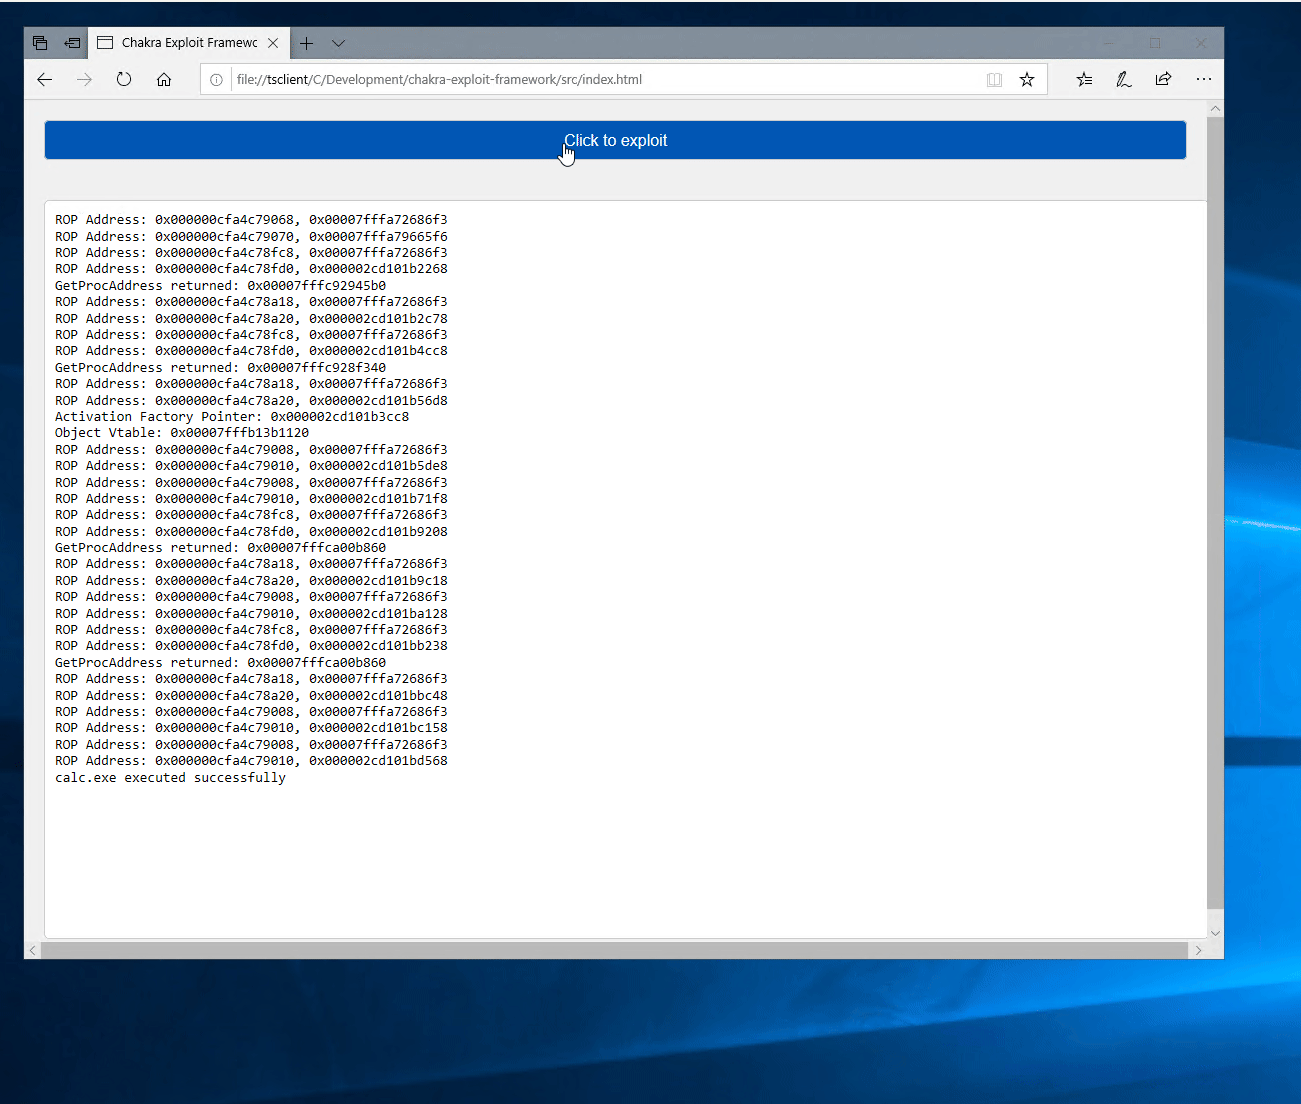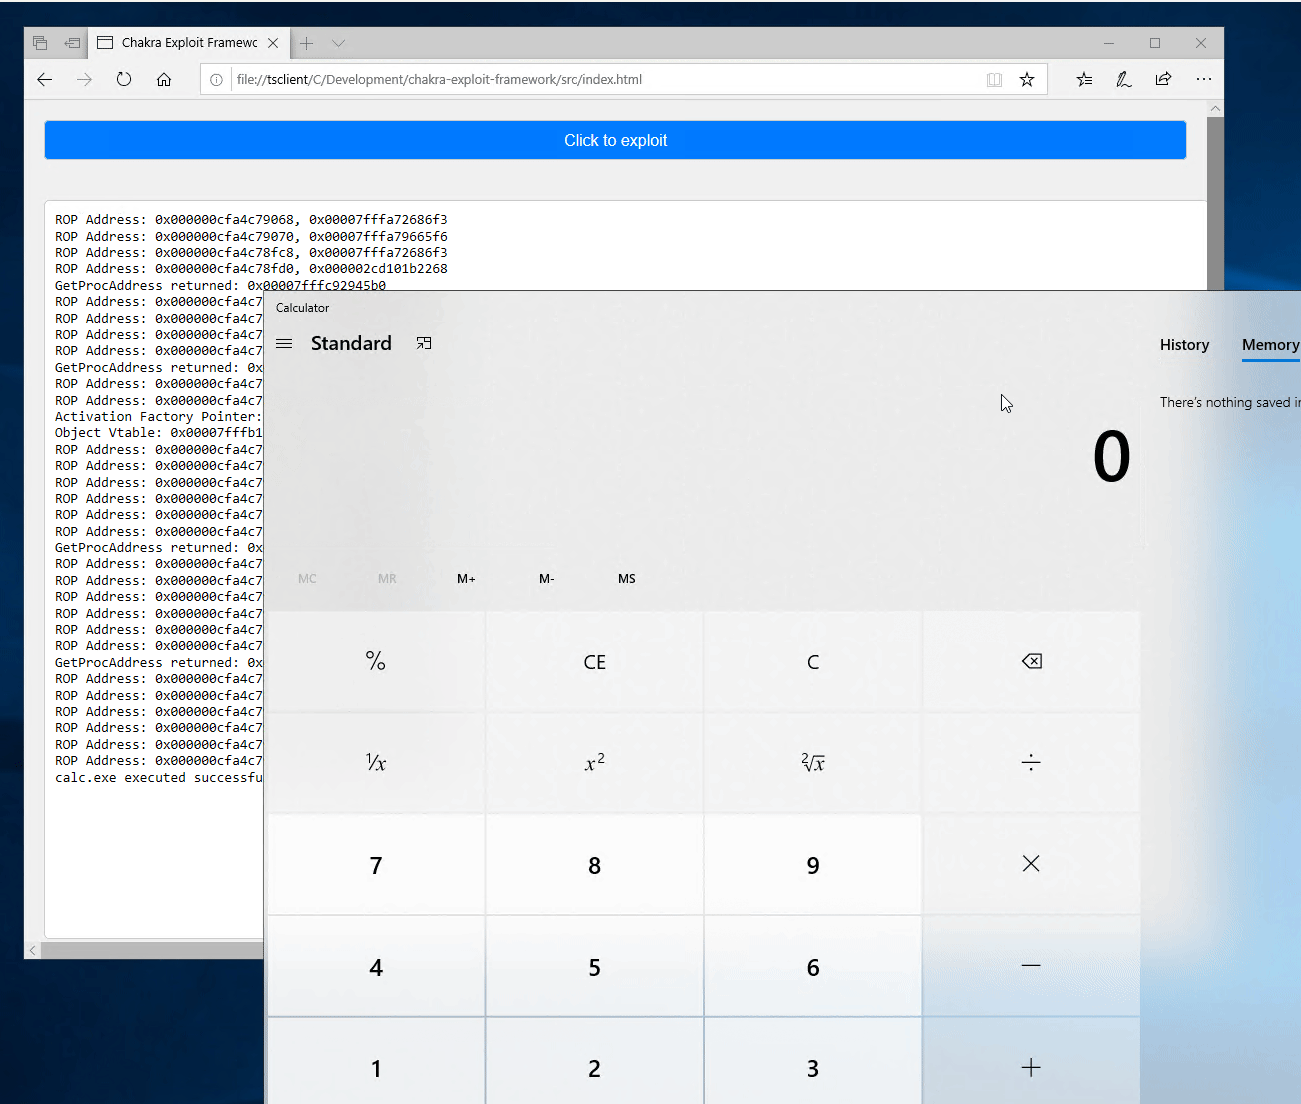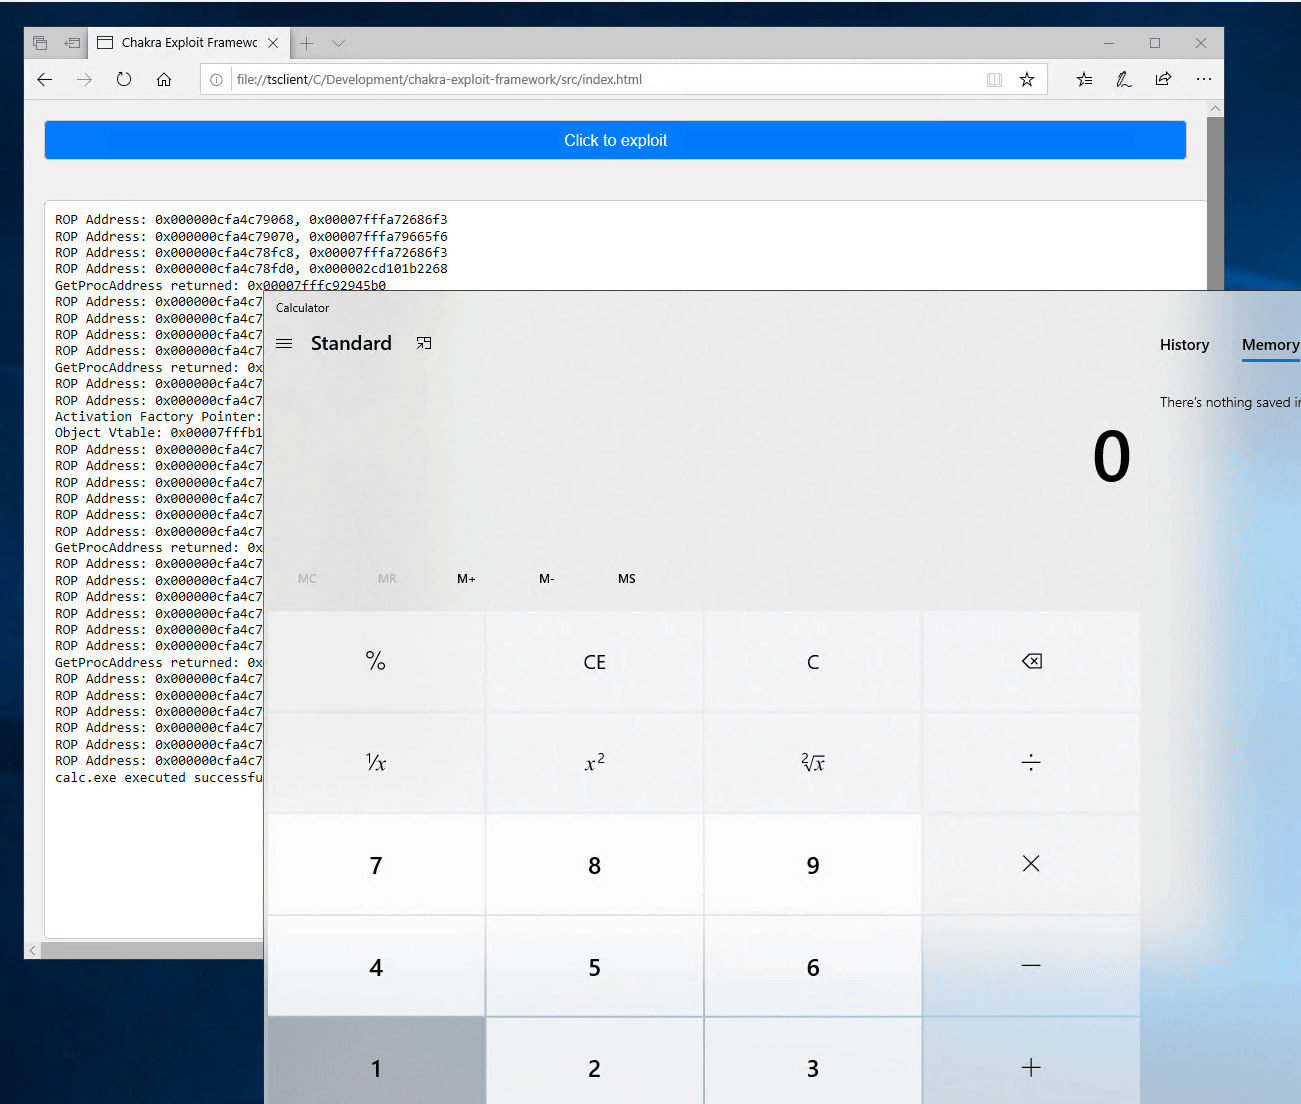 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 cchio/deep-pwning
Metasploit for machine learning.
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
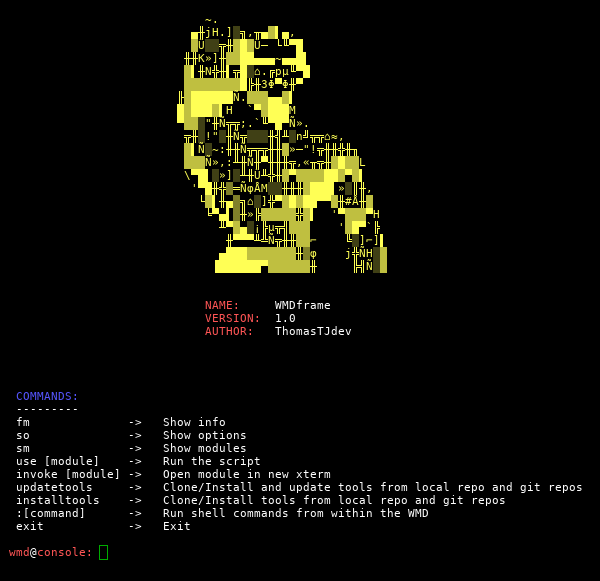 thomastjdev/wmd
Python framework for IT security tools
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
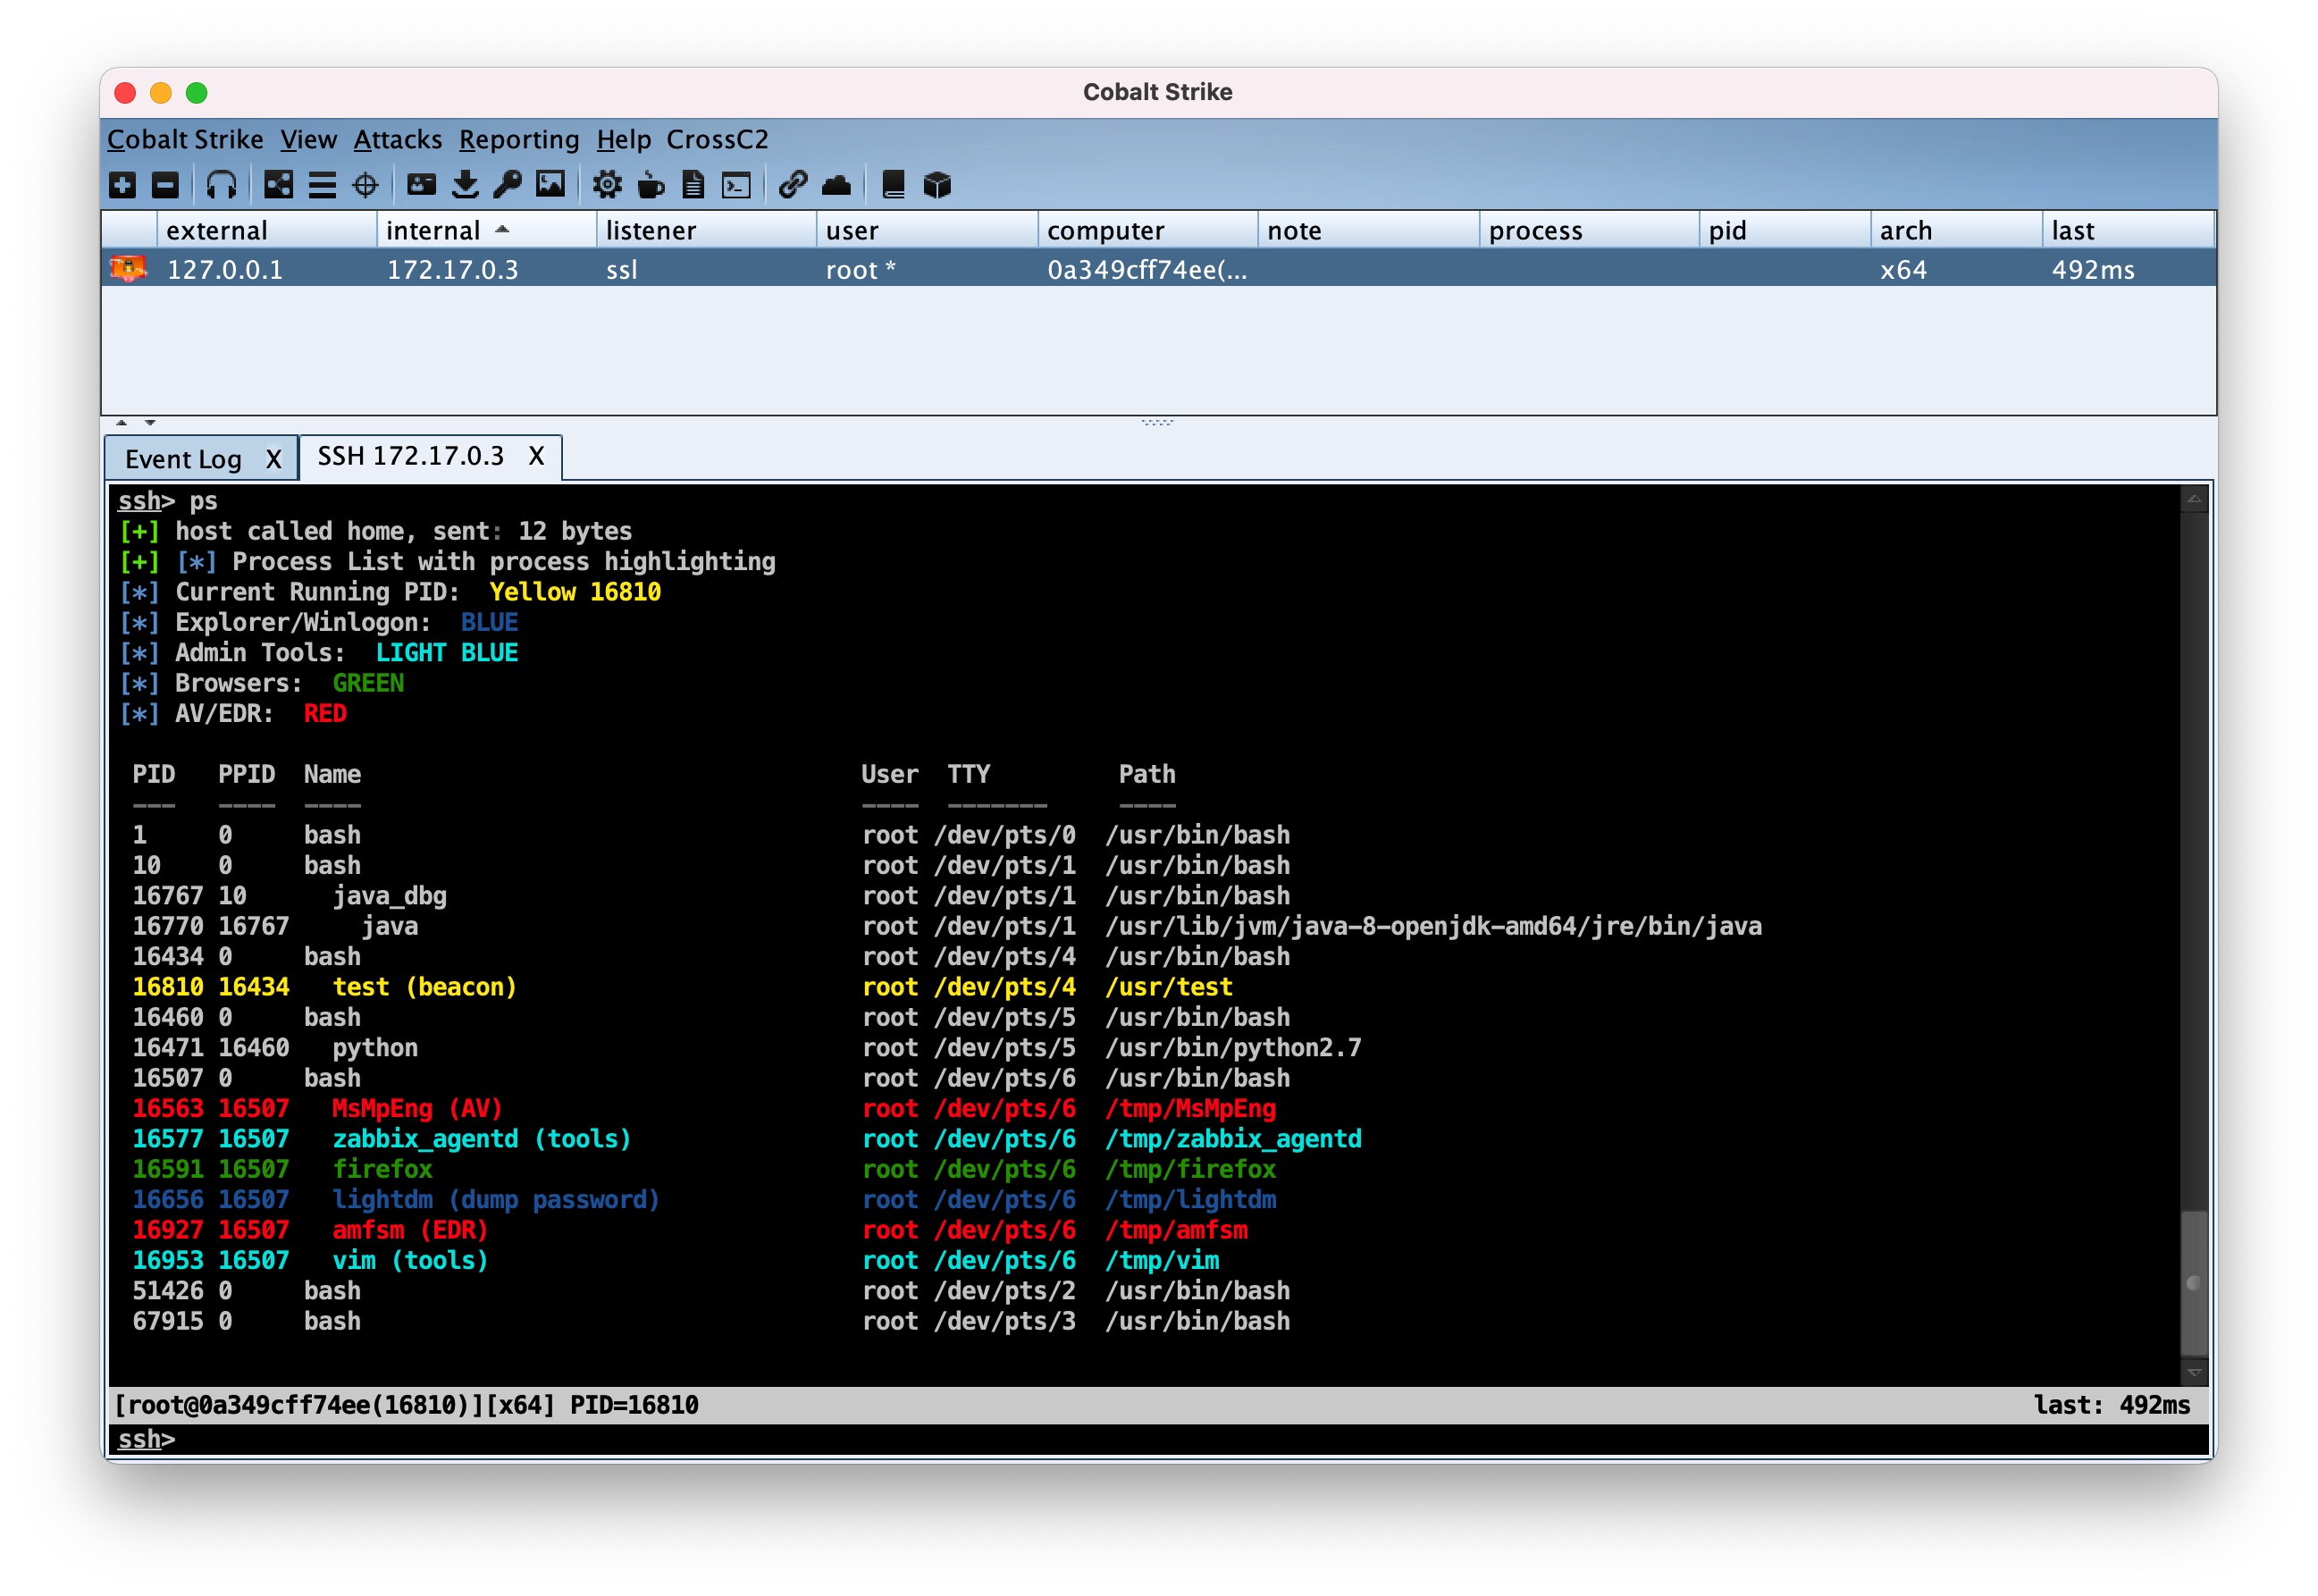 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's