
Archived
purpleteam-orchestrator
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
cloud-securitydevsecopspenetration-testing-frameworks+2
purpleteam-labs/purpleteam-orchestratorOrchestration component of purpleteam
 salesforce/vulnreport
Open-source pentesting management and automation platform by Salesforce Product Security
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
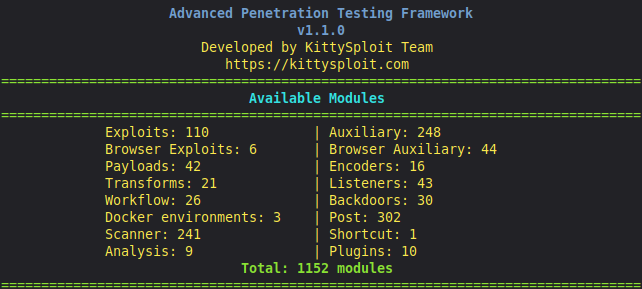 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 gallopsled/pwntools
CTF framework and exploit development library
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 koutto/jok3r
Jok3r v3 BETA 2 - Network and Web Pentest Automation Framework
 psmths/reave
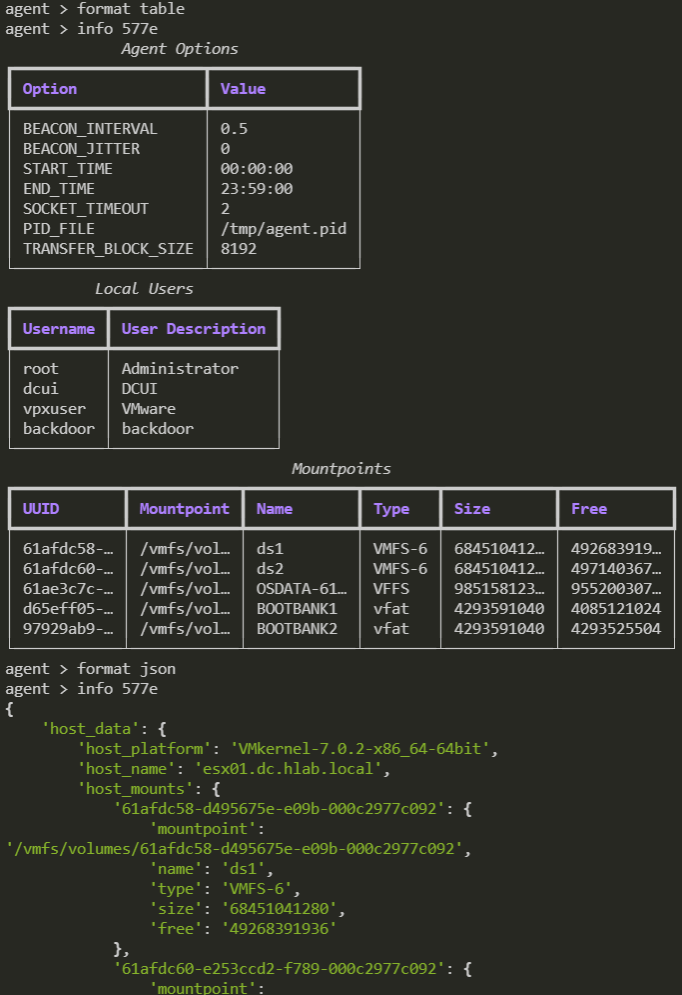
WIP Post-exploitation framework tailored for hypervisors.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 beefproject/beef
The Browser Exploitation Framework Project