
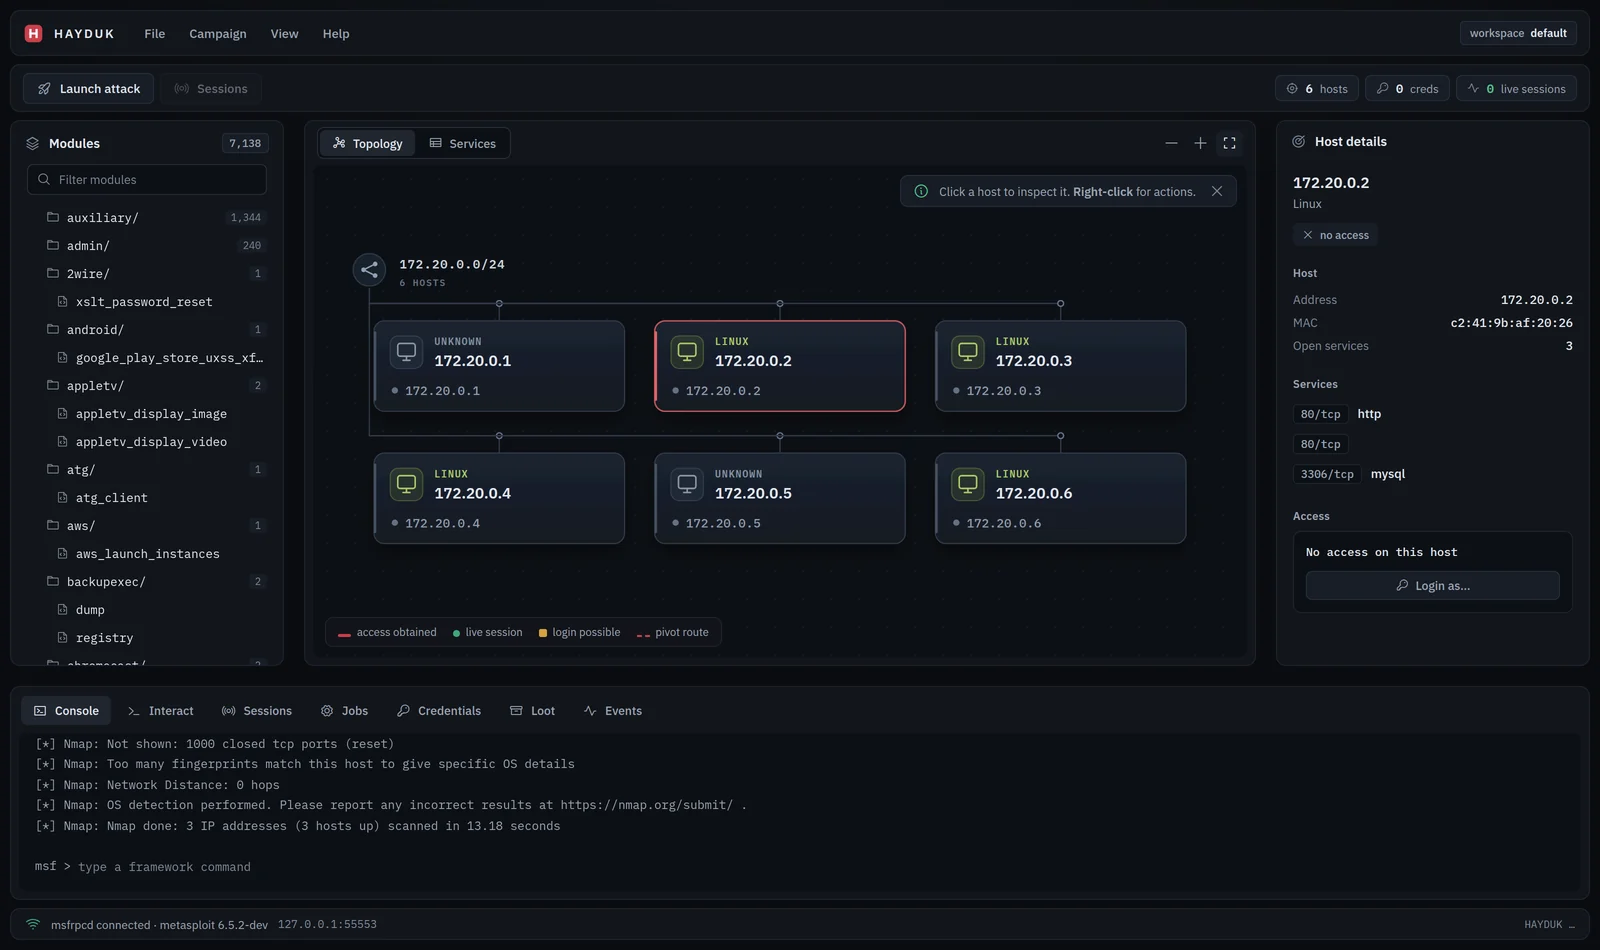
hayduk
 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
exploit-frameworksnetwork-mappingpenetration-testing-frameworks+3
6
jolovicdev/haydukGraphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 infobyte/faraday_templates
Template repository for Faraday security platform, providing reusable vulnerability scanning and exploitation templates for automated penetration…
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878
 0xjessie21/wp2shell-checker
WordPress Core Unauthenticated RCE (CVE-2026-63030, CVE-2026-60137)
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 d3vpp/metasploit-modules
Collection of proof-of-concept Metasploit modules for exploitation and post-exploitation testing, providing custom payloads and auxiliary functions…
 gmh5225/aggressor-aggregator
A helper script for consolidating Aggressor and BOF repositories into a single CNA for Cobalt Strike.
 0xmetr0/metasploit-ldapnightmare
SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit
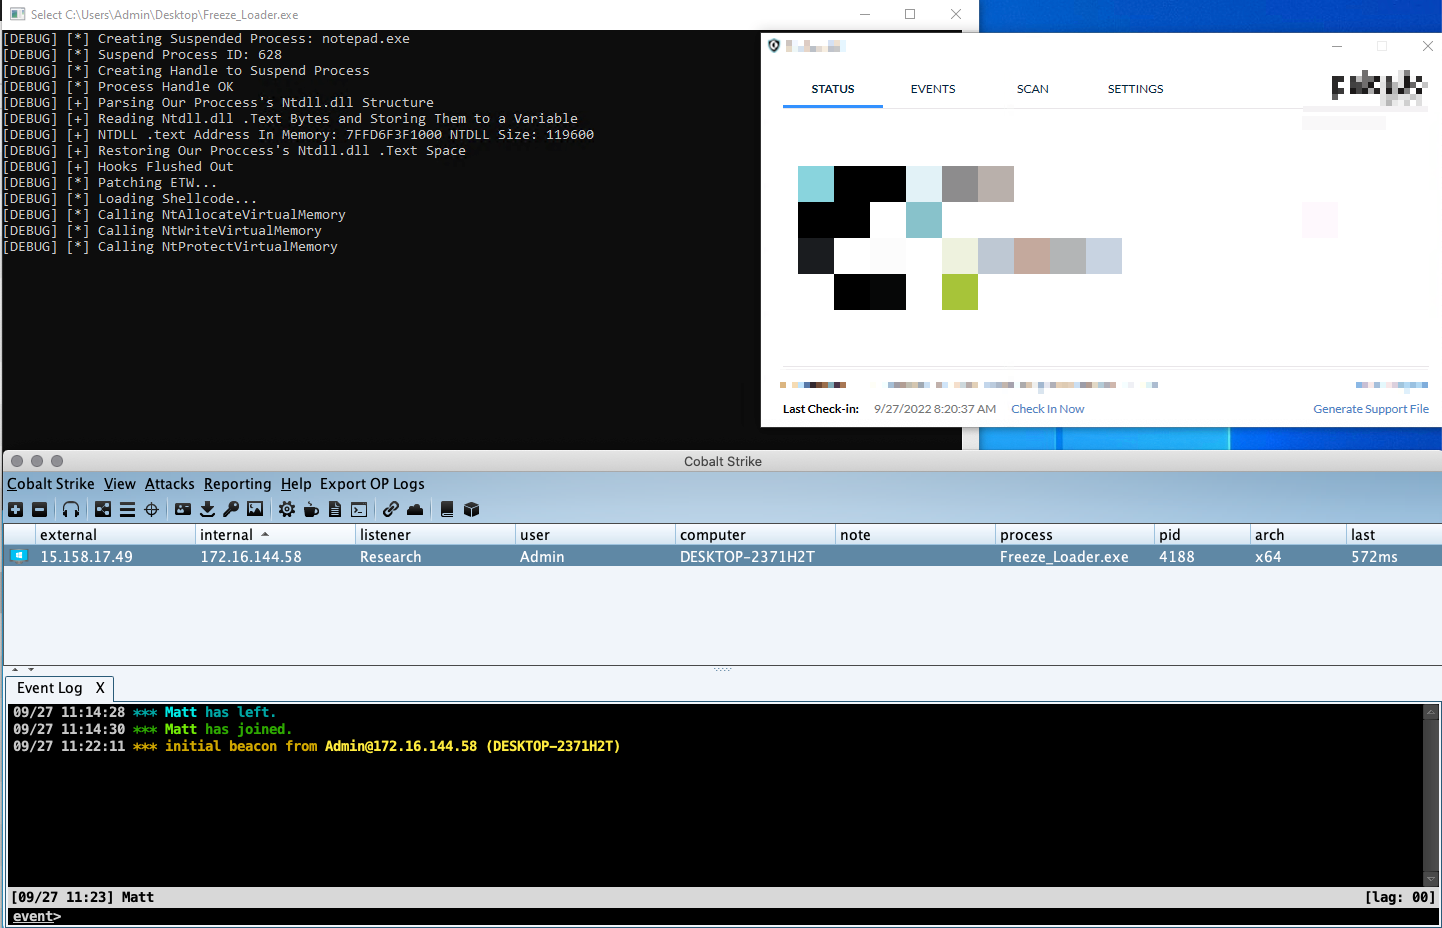 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 spiderlabs/msfrpc
Perl/Python modules for interfacing with Metasploit MSGRPC
 salesforce/vulnreport
Open-source pentesting management and automation platform by Salesforce Product Security
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
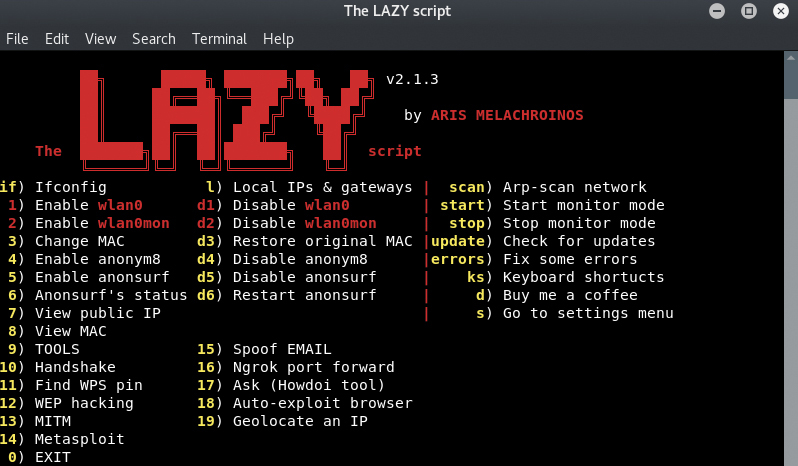 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
 gallopsled/pwntools
CTF framework and exploit development library