

Exploitivator
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
exploit-frameworkspayload-developmentpenetration-testing-frameworks+1
n1ckdunn/exploitivatorAutomate Metasploit scanning and exploitation
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 cobalt-strike/beacon_health_check
This aggressor script uses a beacon's note field to indicate the health status of a beacon.
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
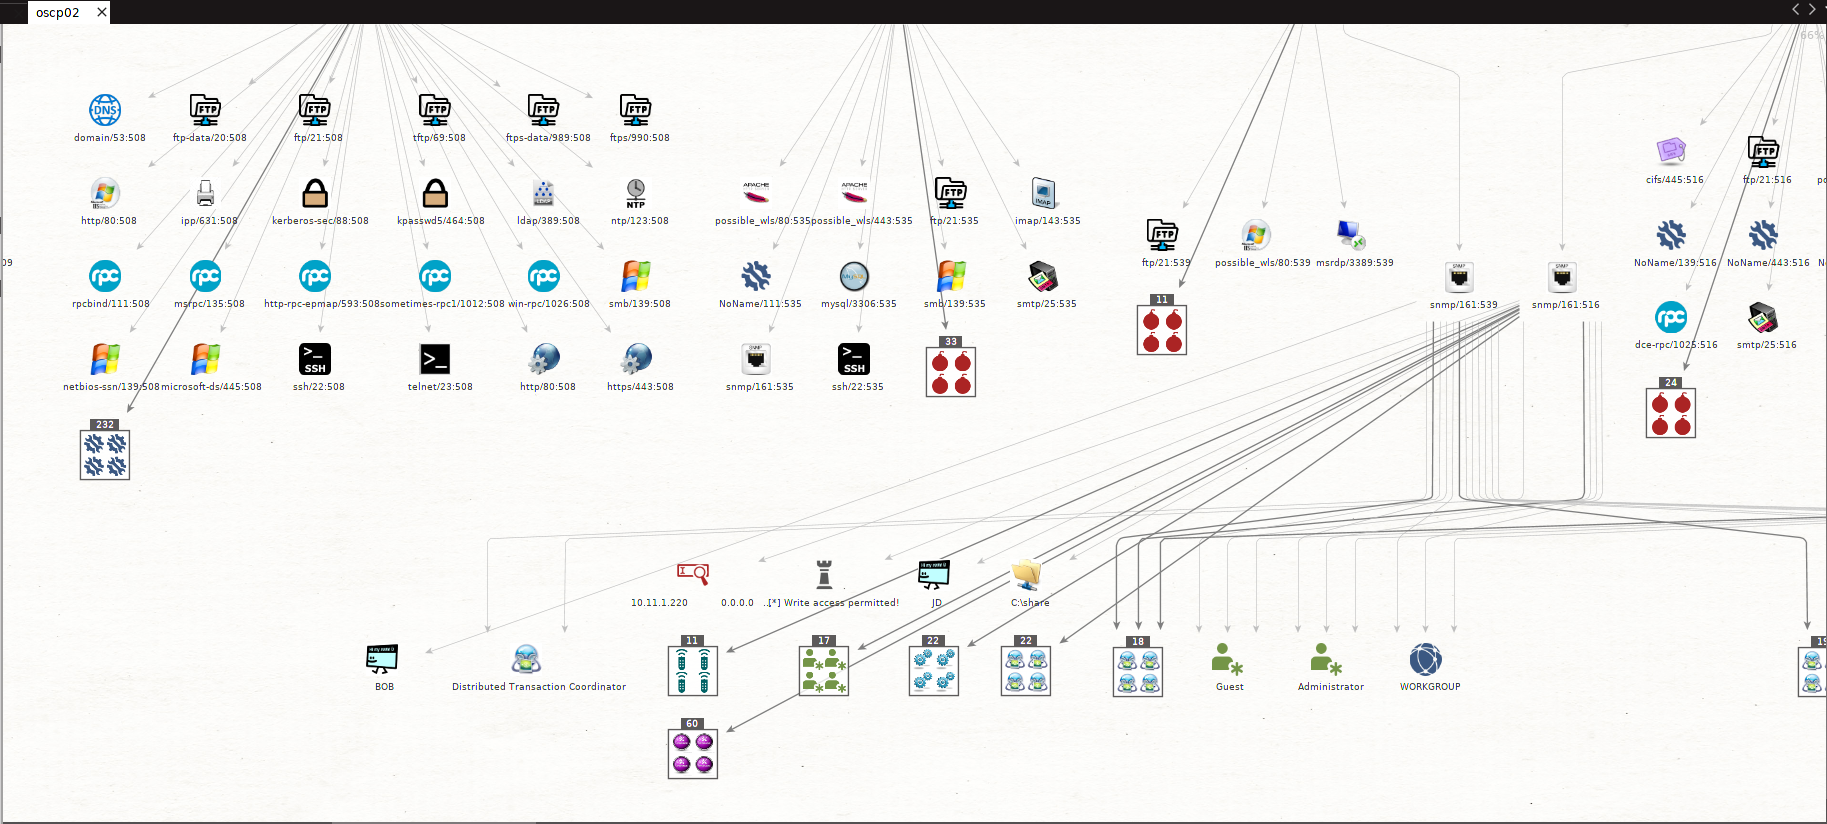 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 project-prismatica/prismatica
Responsive Command and Control System
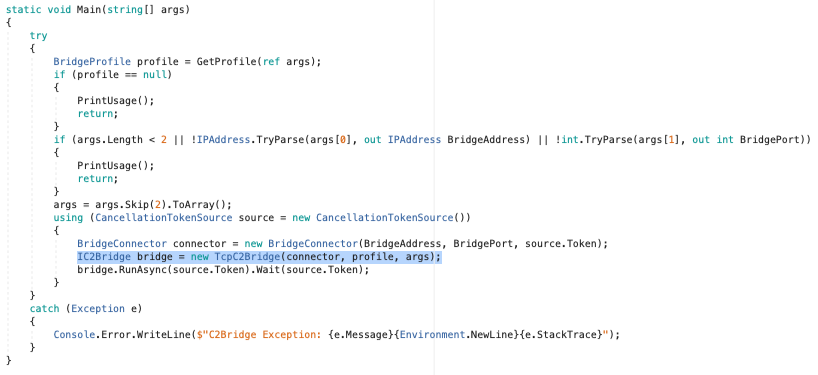 cobbr/c2bridge
C2Bridges allow developers to create new custom communication protocols and quickly utilize them within Covenant.
 mythicagents/apfell
JavaScript for Automation (JXA) macOS agent
 threatexpress/threatbox
Ansible-based attack platform for deploying and managing a standardized Linux penetration testing environment with automated tool installation,…
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing

 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 riswandans/litesploit
library and intepreter for penetration testing tools