

msf-auxiliarys
 r00t-3xp10it/msf-auxiliarys
My collection of metasploit auxiliary post-modules
exploit-frameworkspenetration-testingpenetration-testing-frameworks+2
191
r00t-3xp10it/msf-auxiliarysMy collection of metasploit auxiliary post-modules
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
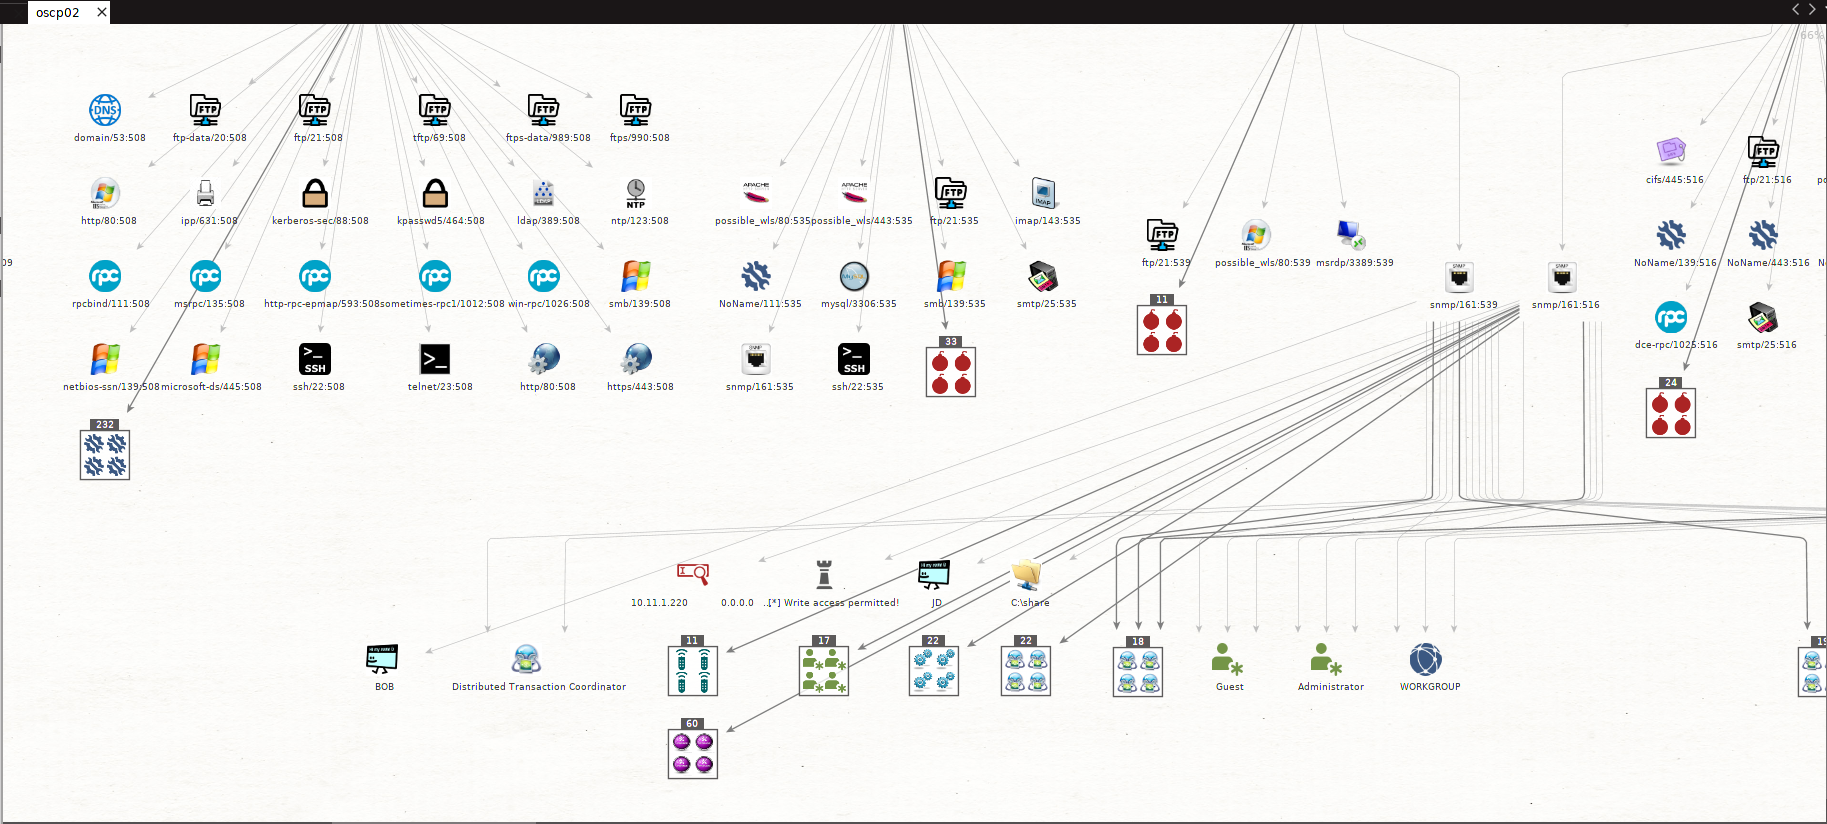 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
 mekhalleh/exchange_proxylogon
Module pack for #ProxyLogon (part. of my contribute for Metasploit-Framework) [CVE-2021-26855 && CVE-2021-27065]
 h3x0v3rl0rd/cve-2019-9053
Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…
 b0fh/cve-2018-4878
Metasploit module for CVE-2018-4878
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
 gmh5225/aggressor-aggregator
A helper script for consolidating Aggressor and BOF repositories into a single CNA for Cobalt Strike.